Key Takeaways
- What we are launching: OPSWAT is launching MetaDefender for Microsoft 365, formerly MetaDefender Cloud Email Security, to deliver Microsoft 365 file threat prevention across Microsoft email and Teams.
- Why it matters: Files now move through email and Teams conversations at speed, creating exposure paths for weaponized, suspicious, and password-protected content.
- Who it is for: Security, IT, SOC, compliance, and Microsoft 365 teams that need layered inspection, sanitization, and auditability beyond native controls without disrupting MX records.
A file arrives from a trusted sender, looking routine enough that nobody thinks twice. It moves from an inbox into a Teams chat, where more people can open it, forward it, and act on it. That workflow is everyday business, and everyday is exactly what attackers count on.
On September 29, 2026, OPSWAT is launching MetaDefender™ for Microsoft 365, formerly known as MetaDefender™ Cloud Email Security. This launch extends OPSWAT threat prevention from emails to files shared through Microsoft Teams.
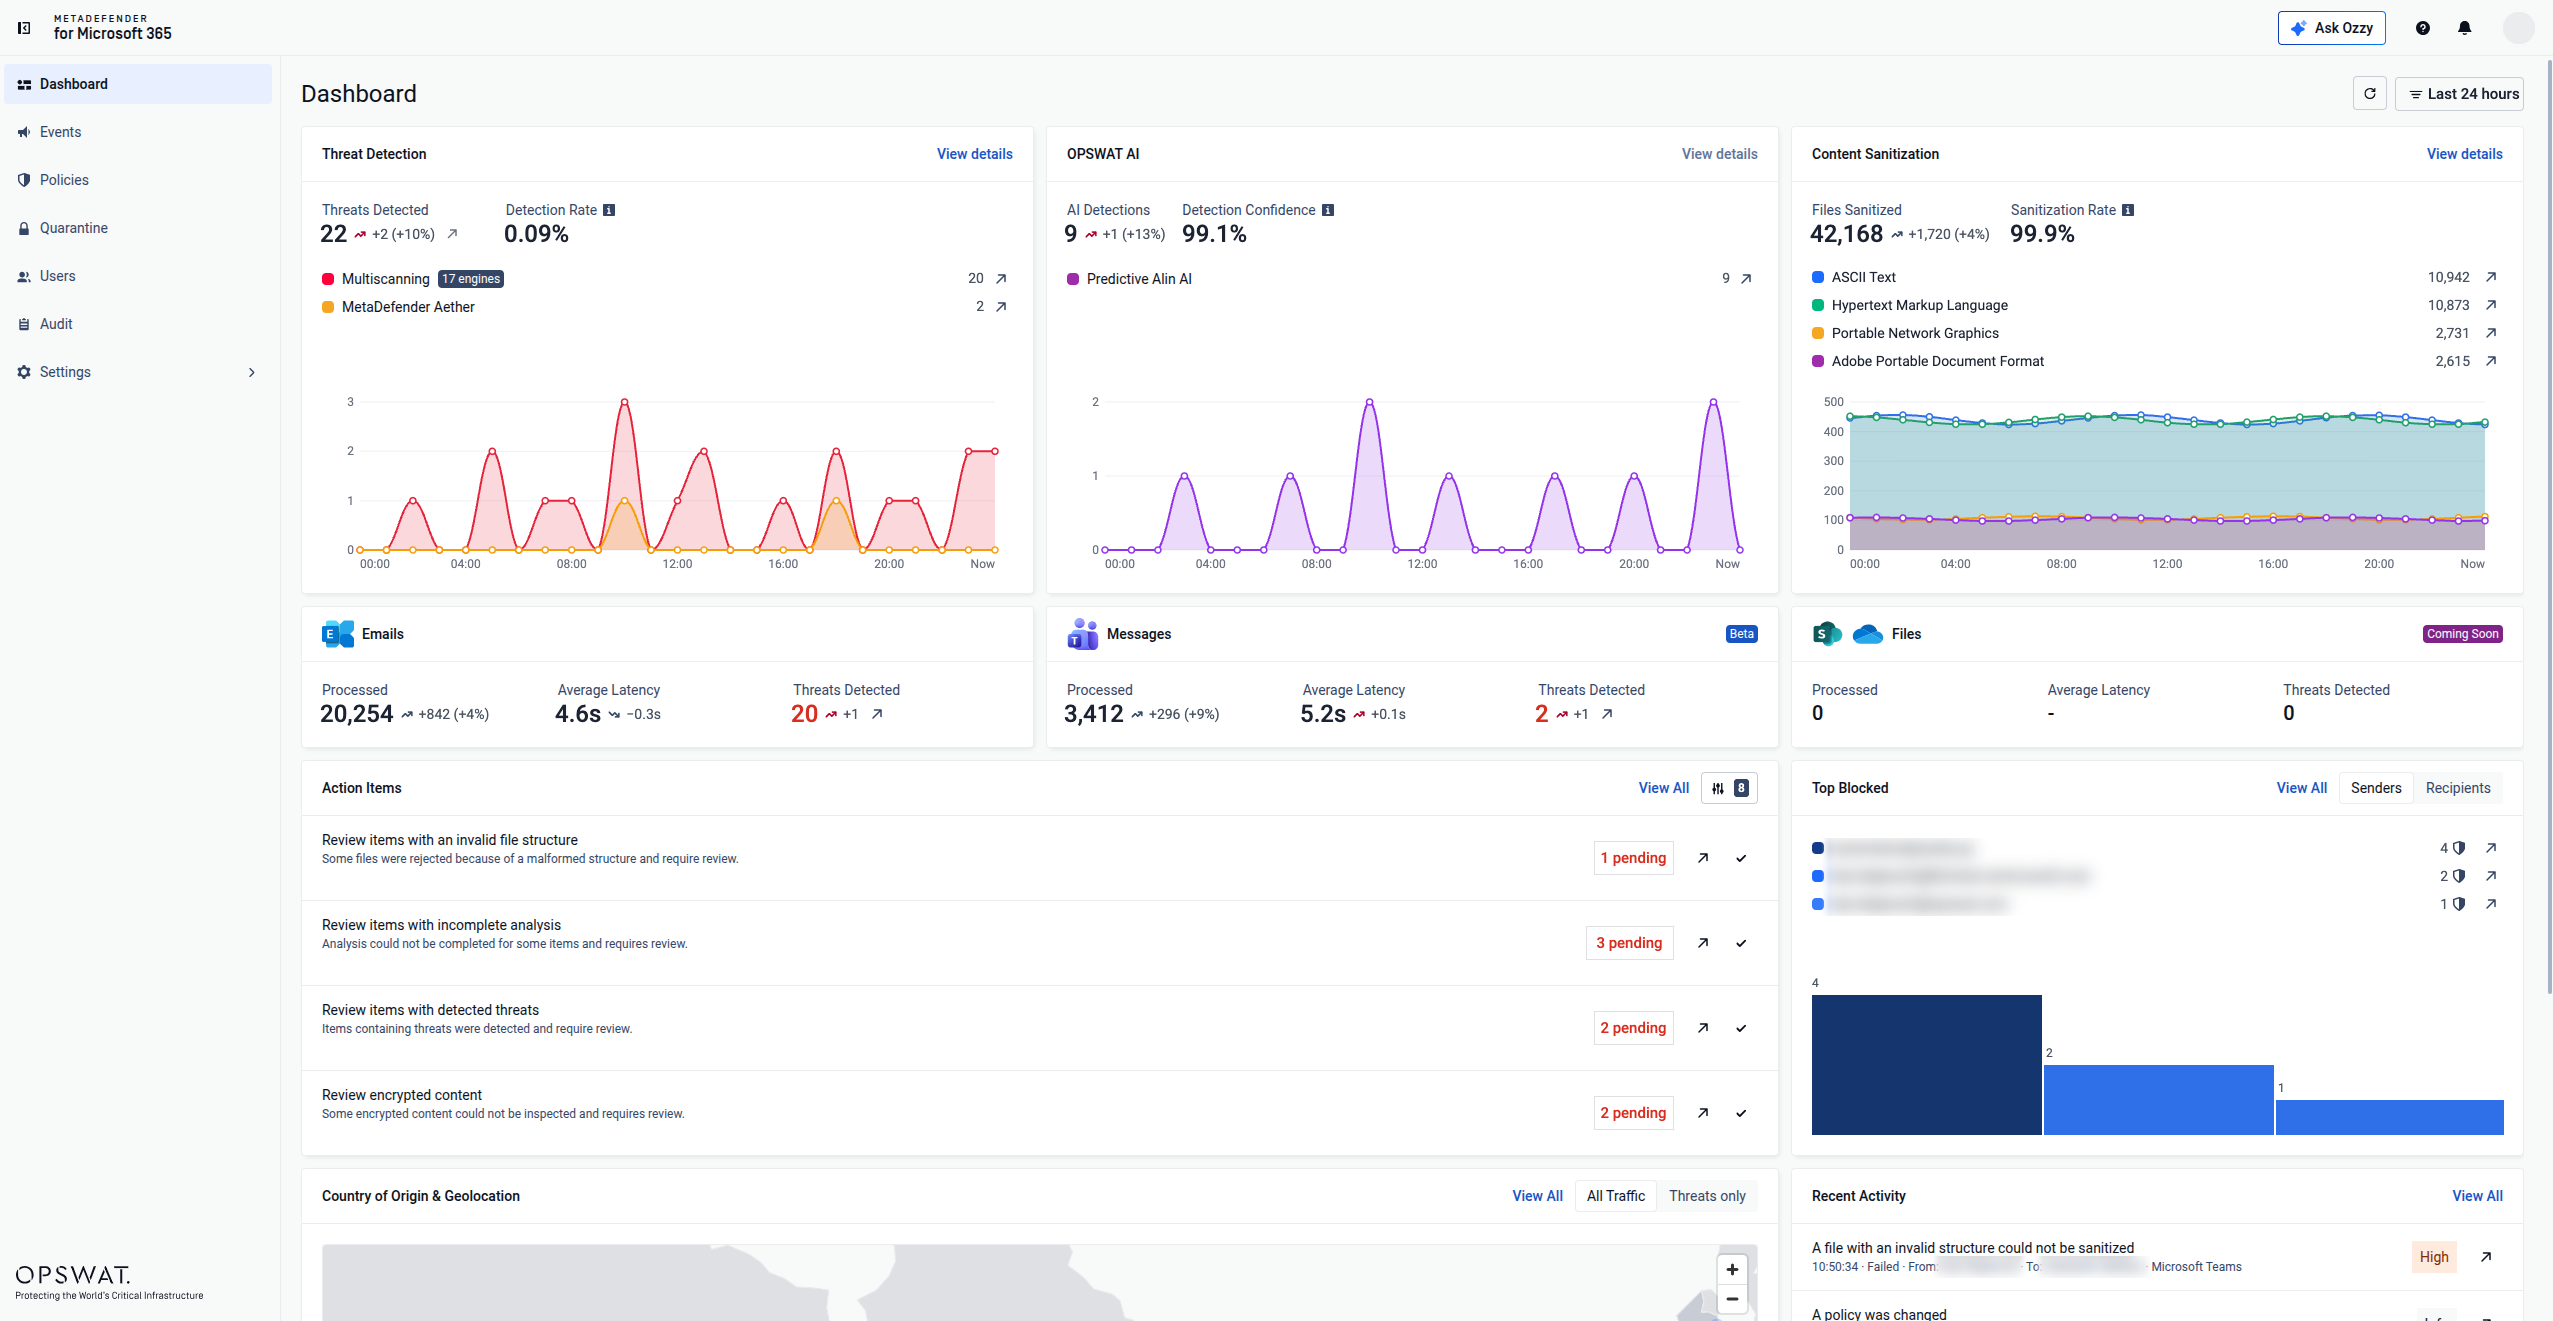
MetaDefender for Microsoft 365 is OPSWAT’s file threat prevention solution for inspecting and sanitizing files across Exchange Online and Microsoft Teams. It adds Metascan™ Multiscanning, Deep CDR™ Technology, MetaDefender Aether™, and Predictive Alin AI, an AI-powered malware analysis engine, beyond native Microsoft controls to help minimize exposure and post-delivery remediation.
Why This Launch Matters
Earlier this year, MetaDefender Cloud Email Security was launched with a focused purpose: help organizations strengthen protection for Exchange Online. That foundation remains in place. The way people work is what changed: the average employee now receives 117 emails and 153 Teams messages daily, according to Microsoft 2025 Work Trend Index Annual Report. That stat reflects how deeply chat-based collaboration has become embedded in daily work. As files move between inboxes, Teams chats, and channels, security must extend to the collaboration tools employees use every day. This is why OPSWAT is expanding its security footprint from email to Microsoft Teams.
With MetaDefender for Microsoft 365, files moving through Exchange Online and Microsoft Teams are inspected, analyzed, and sanitized, adding a depth of file-level scrutiny that complements native Microsoft controls and gives security and IT teams practical control over Microsoft 365 malware protection.
How MetaDefender for Microsoft 365 Helps
- Exchange Online: inline email protection without MX record changes; before emails reach inboxes, they are screened and automatically sent to quarantine if deemed malicious.
- Microsoft Teams: inspection and sanitization for files shared in chats and channels.
MetaDefender for Microsoft 365 combines four OPSWAT technologies to support Microsoft 365 file threat prevention across email and Teams:
| Technology | What it does |
| Metascan™ Multiscanning | Runs emails and files through up to 17 anti-malware engines in parallel to help close detection gaps. |
| Deep CDR™ Technology | Provides prevention-first CDR security across 200+ file types by treating every file or attachment as potentially harmful, removing active content such as scripts, macros, embedded objects, QR-code risks, and out-of-policy elements, then delivering a clean, usable version. |
| MetaDefender Aether™ | Uses emulation-based dynamic malware analysis to expose zero-day, evasive, and multi-stage threats at the perimeter. Its Adaptive Sandbox can analyze 50,000+ files or attachments per day per server, return fast-pass verdicts with threat intelligence in about 10 seconds, and map behaviors to MITRE ATT&CK for analyst-ready evidence. |
| Predictive Alin AI | Delivers pre-execution malware verdicts by analyzing structural and behavior-linked file and email characteristics before signatures or sandbox detonation are required. Predictive Alin AI returns an average verdict in 6.67 milliseconds, with a 0.03% false-positive rate and 93% detection efficacy. |
Together, these layers help reduce the exposure window and post-delivery remediation while strengthening file threat prevention against known, evasive, and AI-assisted threats across supported Microsoft 365 workflows.
Why Choose OPSWAT?
Many Microsoft 365 security tools provide important baseline protection. OPSWAT adds a different level of file scrutiny for organizations whose emails and files carry regulated data, supplier content, customer records, or operational dependencies.
Password-protected files create a familiar dilemma. Block them, and legitimate work slows down. Let them through unopened, and they can become a blind spot. MetaDefender for Microsoft 365 gives users a self-serve workflow to provide the password. Deep CDR™ Technology then automatically deconstructs the file, removes potentially malicious content, reconstructs it, and delivers a sanitized, functional version to the recipient.
MetaDefender for Microsoft 365 is new, but the OPSWAT technologies which it is built upon carry 20+ years of critical infrastructure know-how. Emails and files are inspected with the level of scrutiny required as the average cost of a data breach has increased by 12%, up to USD 4.99 million, according to IBM Cost of a Data Breach Report 2026.
Built to Fit Existing Workflows
MetaDefender for Microsoft 365 brings file threat prevention to the Microsoft 365 tools employees already use, without MX record changes, hardware, or unnecessary mail-flow disruption. With inline protection for Exchange Online and API-based protection for Microsoft Teams, organizations can strengthen security while keeping everyday communication and collaboration moving.
| Benefits for CISOs | Reduce Microsoft 365 content risk and show layered control beyond native Microsoft protection. |
| Benefits for SOC teams | Improve visibility into suspicious files across Exchange Online and Microsoft Teams in a single platform while reducing manual triage. |
| Benefits for compliance and risk teams | Support inspection, sanitization, reporting, and auditability for files moving through covered Microsoft 365 workflows. |
| Benefits for Microsoft 365 administrators | Add protection for email and Teams without unnecessary deployment friction. |
See What MetaDefender for Microsoft 365 Can Do for Your Organization
Visit the product page to explore how OPSWAT brings file threat prevention to Exchange Online and Microsoft Teams.
Frequently Asked Questions (FAQ)
What happened to MetaDefender Cloud Email Security?
MetaDefender Cloud Email Security has evolved into MetaDefender for Microsoft 365. The cloud email security capabilities remain, and the protected surface now extends to Microsoft Teams, covering files shared in chats and channels as well as email.
What does Microsoft 365 file threat prevention mean?
It means inspecting, analyzing, and sanitizing files as they move through Exchange Online and Microsoft Teams, rather than limiting protection to email alone.
Is Microsoft Defender for Office 365 enough on its own?
Native Microsoft controls provide a baseline. MetaDefender for Microsoft 365 adds prevention layers beyond native controls, including Metascan Multiscanning, Deep CDR™ Technology, MetaDefender Aether, and Predictive Alin AI. This gives organizations several independent checks: multi-engine inspection, sanitization, and behavioral analysis.
Can files shared in Microsoft Teams be scanned for malware?
Yes, MetaDefender for Microsoft 365 applies multi-engine scanning, Deep CDR™ Technology sanitization and emulation-based sandbox analysis to files shared through Teams chats and channels.
Does deployment require MX record changes?
No, MetaDefender for Microsoft 365 adds email security to Microsoft 365 without changing MX records, hardware, or mail flow.
How does it handle password-protected files?
Users provide the password through a self-serve portal. Our product applies it automatically, inspects, deconstructs the file, removes potentially malicious content, reconstructs it, and delivers a sanitized, functional version without routine admin validation. If a threat has been detected, the file will be sent to quarantine where the security teams can investigate it further.