Secure Access to Every App and Network
My OPSWAT™ Central Management continuously verifies user identity and device security posture to enforce compliant, seamless access across enterprise applications and networks.
- Zero-Trust Access
- Continuous Posture Checks
- Centralized Visibility
OPSWAT is Trusted by
The Access Gaps Weakening Your Security Posture
VPNs Are Now a Breach Vector, Not a Security Layer
Legacy VPNs were designed for a different threat model. Once connected, users get broad network access with no ongoing compliance checks, making them one of the most exploited enterprise attack vectors for lateral movement, credential theft, and ransomware.
Authenticated Users, Unverified Devices
Identity providers confirm who's logging in but say nothing about the endpoint. Unpatched, non-compliant, or compromised devices bypass identity checks entirely, turning trusted users into unintentional threats.
No Unified Visibility Across Your Access Controls
Cloud apps, on-prem networks, VDI, BYOD, contractors, each secured by a different tool with its own policies. Without centralized control, security gaps grow with every new environment you add.
One Platform for Complete Zero-Trust Access Orchestration
My OPSWAT Central Management bridges the gap between user authentication and real-time device health, enforcing continuous, least-privilege access from a single console.
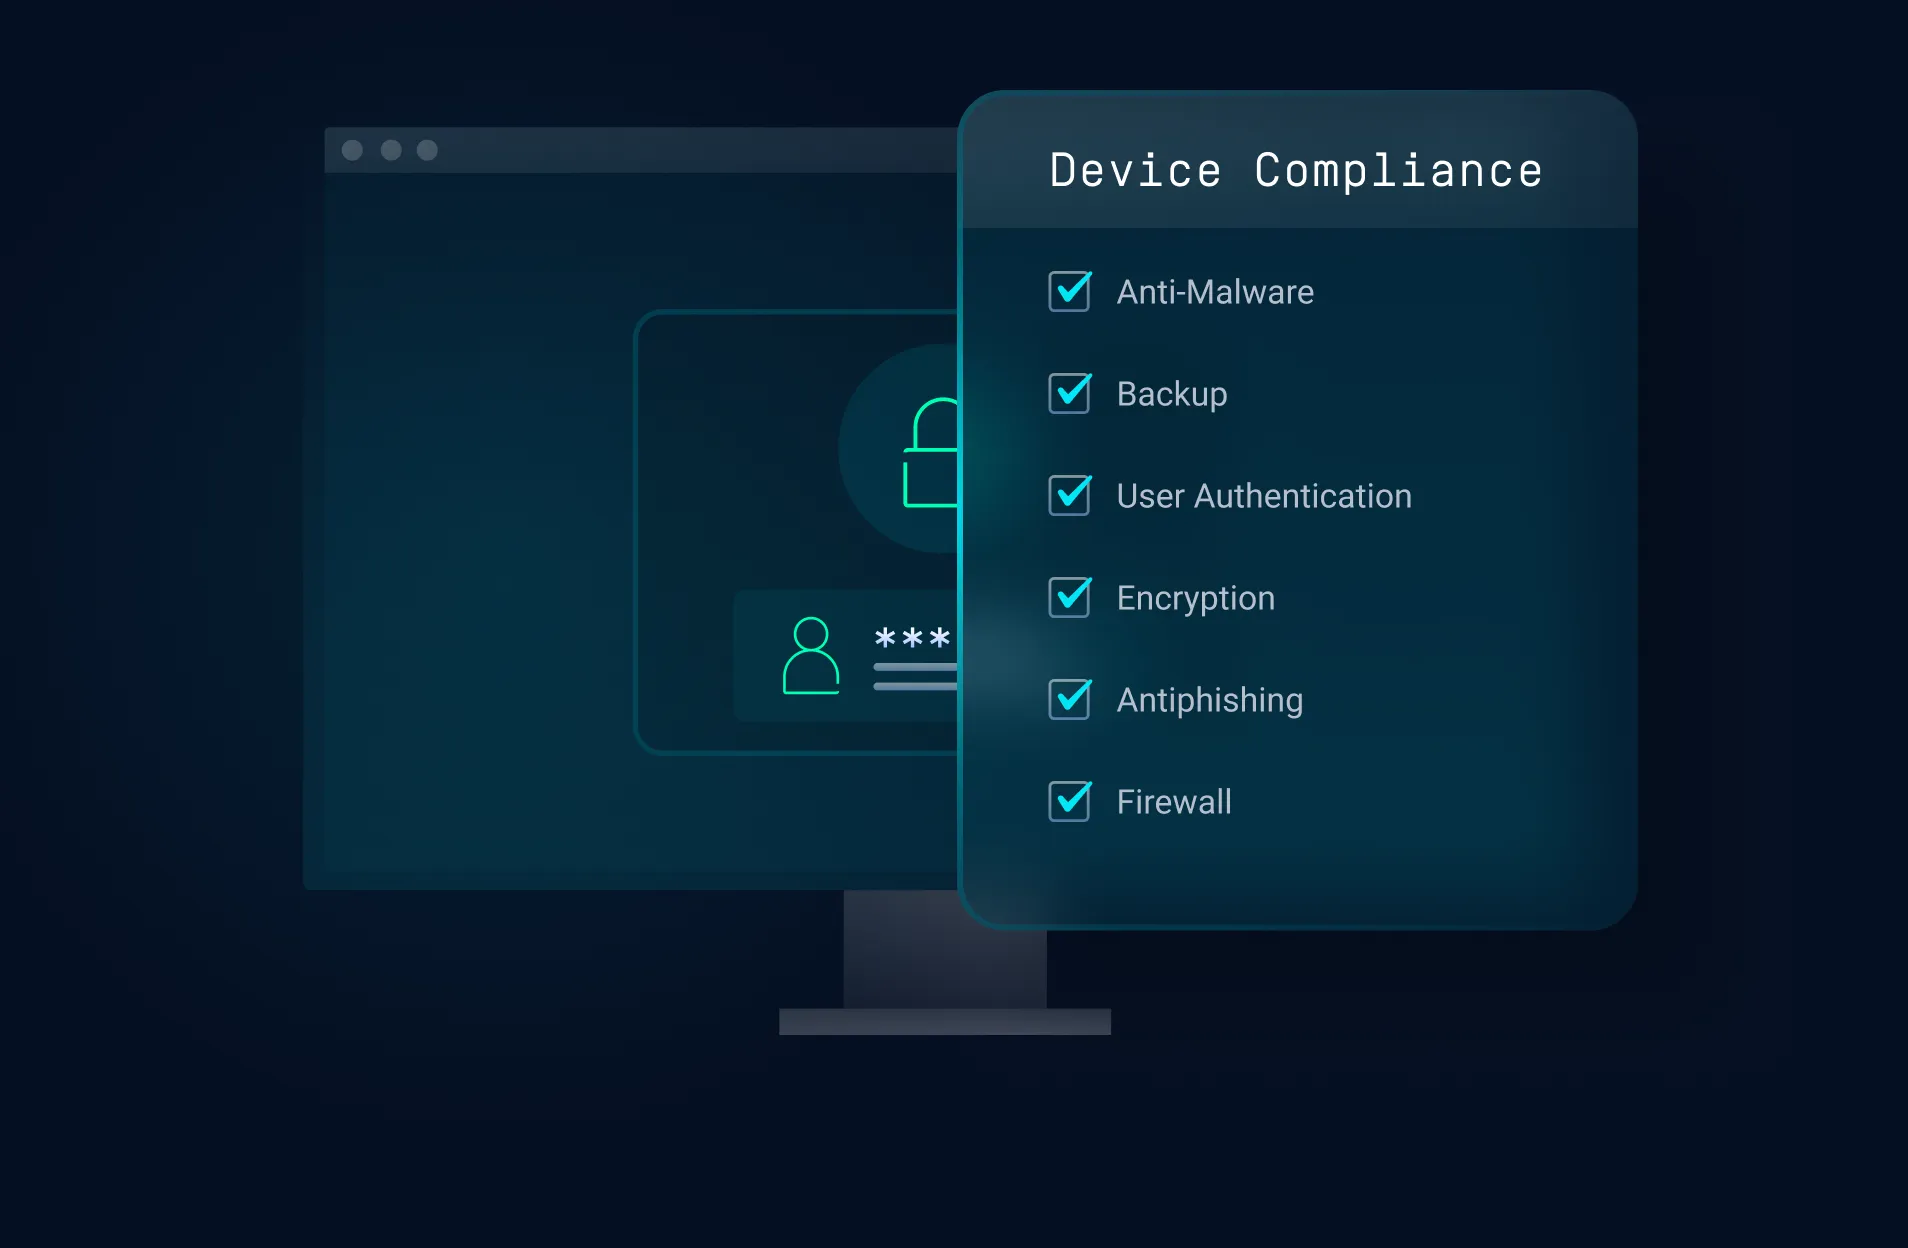
Replace VPNs With Zero-Trust, Application-Level Access
Eliminate broad network exposure with access methods that continuously verify identity and device compliance before granting least-privilege, per-application access.
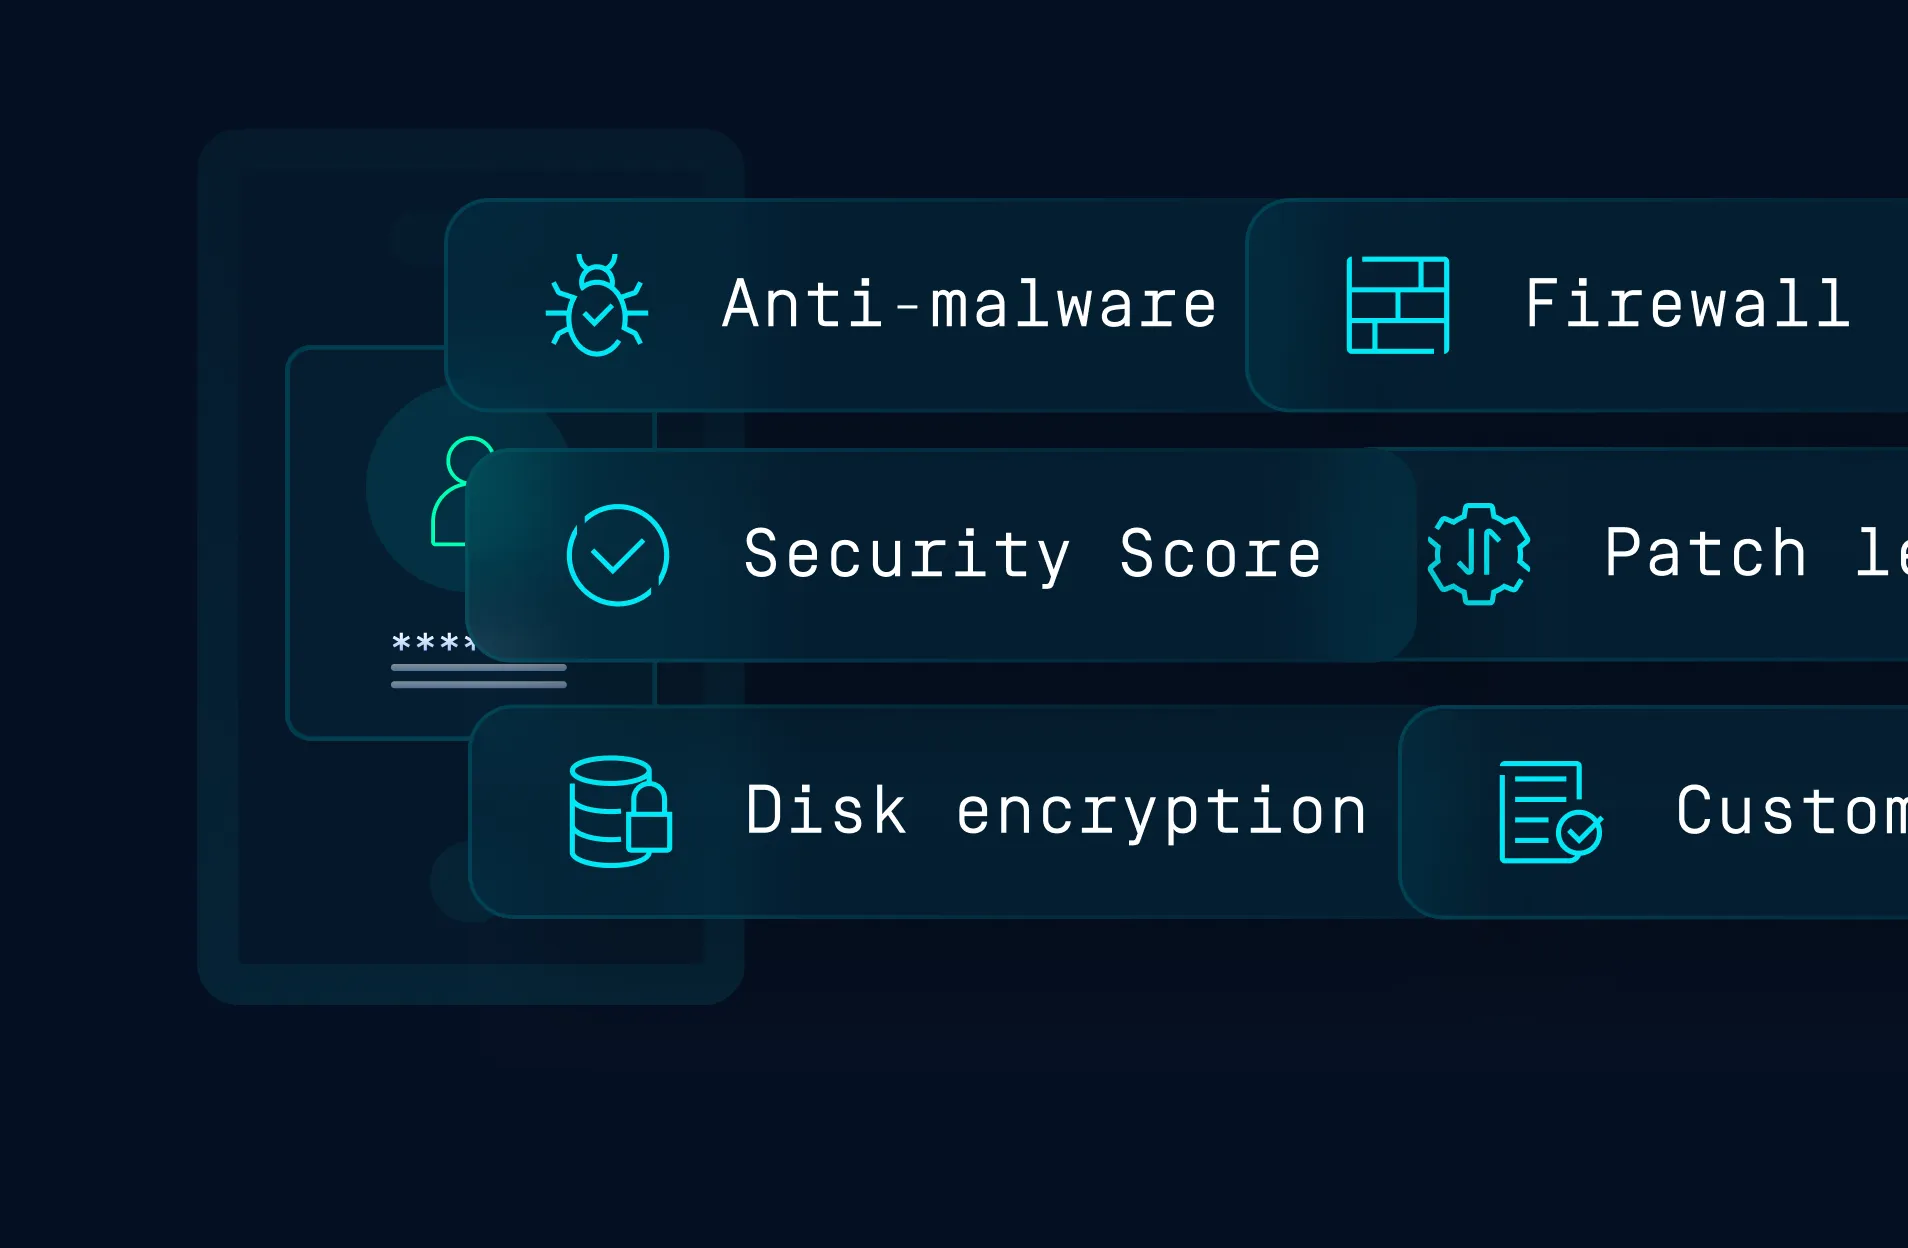
Add Device Verification to Every Access Decision
Layer real-time device compliance on top of your existing IdP and MFA. Access depends on both who the user is and whether their device is healthy and compliant at that moment.
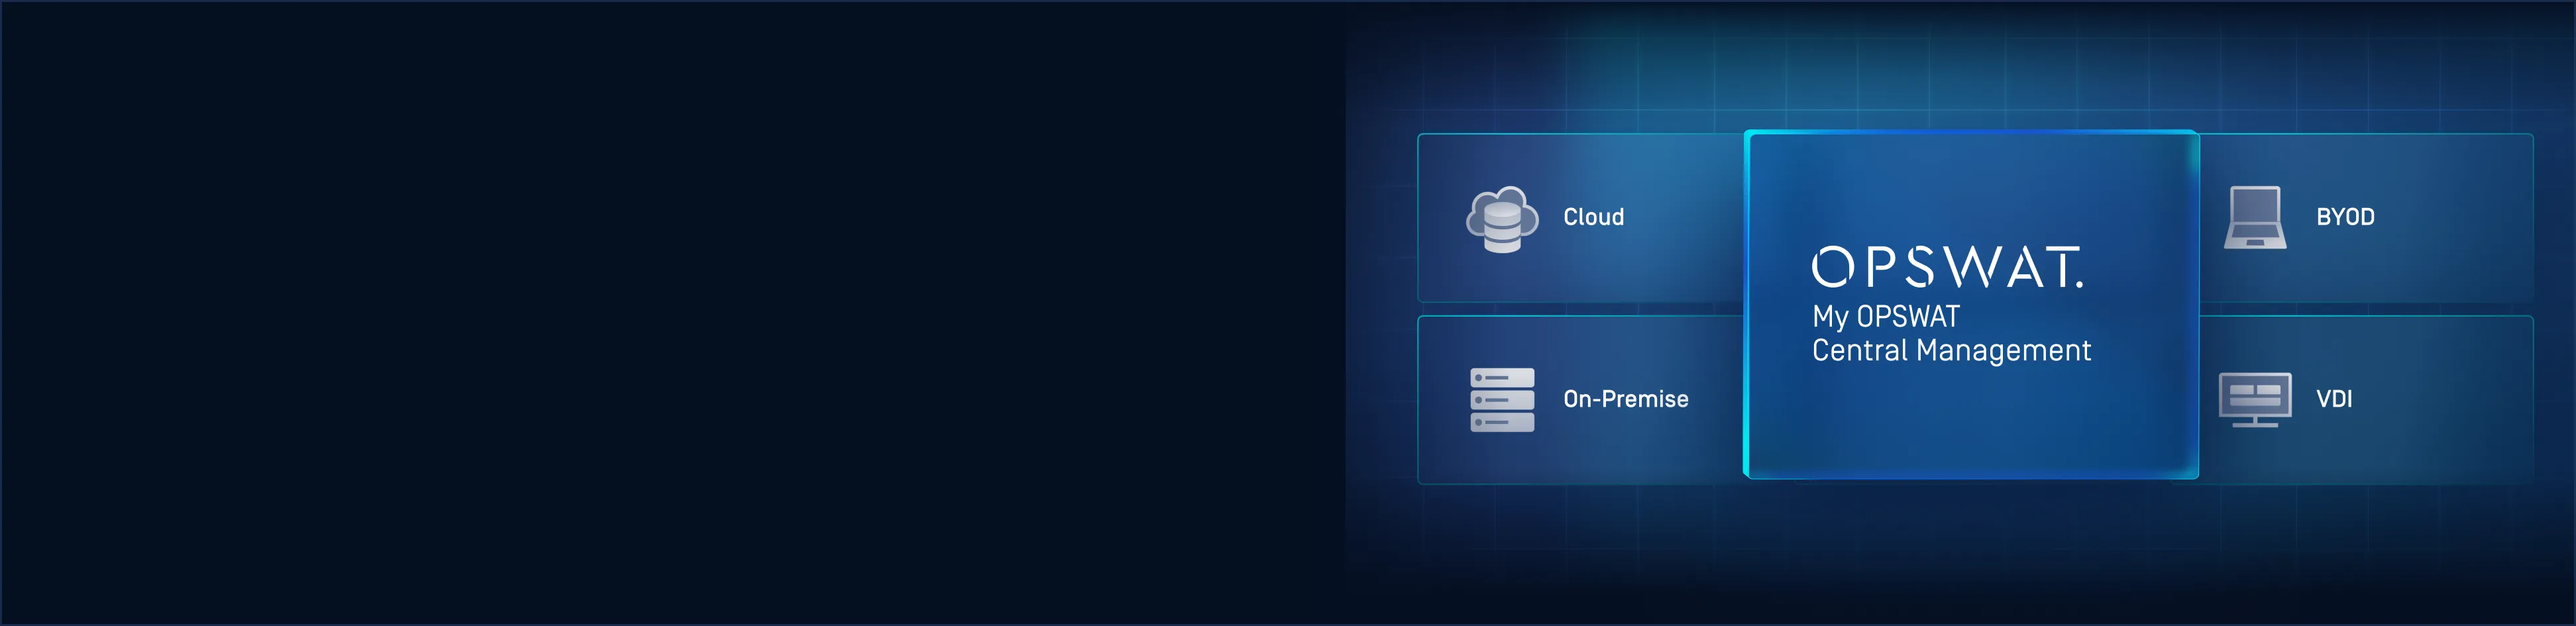
One Console for Every Access Method and Environment
Define, deploy, and monitor secure access rules globally from My OPSWAT Central Management. One policy engine, one dashboard, one audit trail, across cloud, on-prem, VDI, and BYOD.
Zero-Trust Access Enforcement Across Every Environment
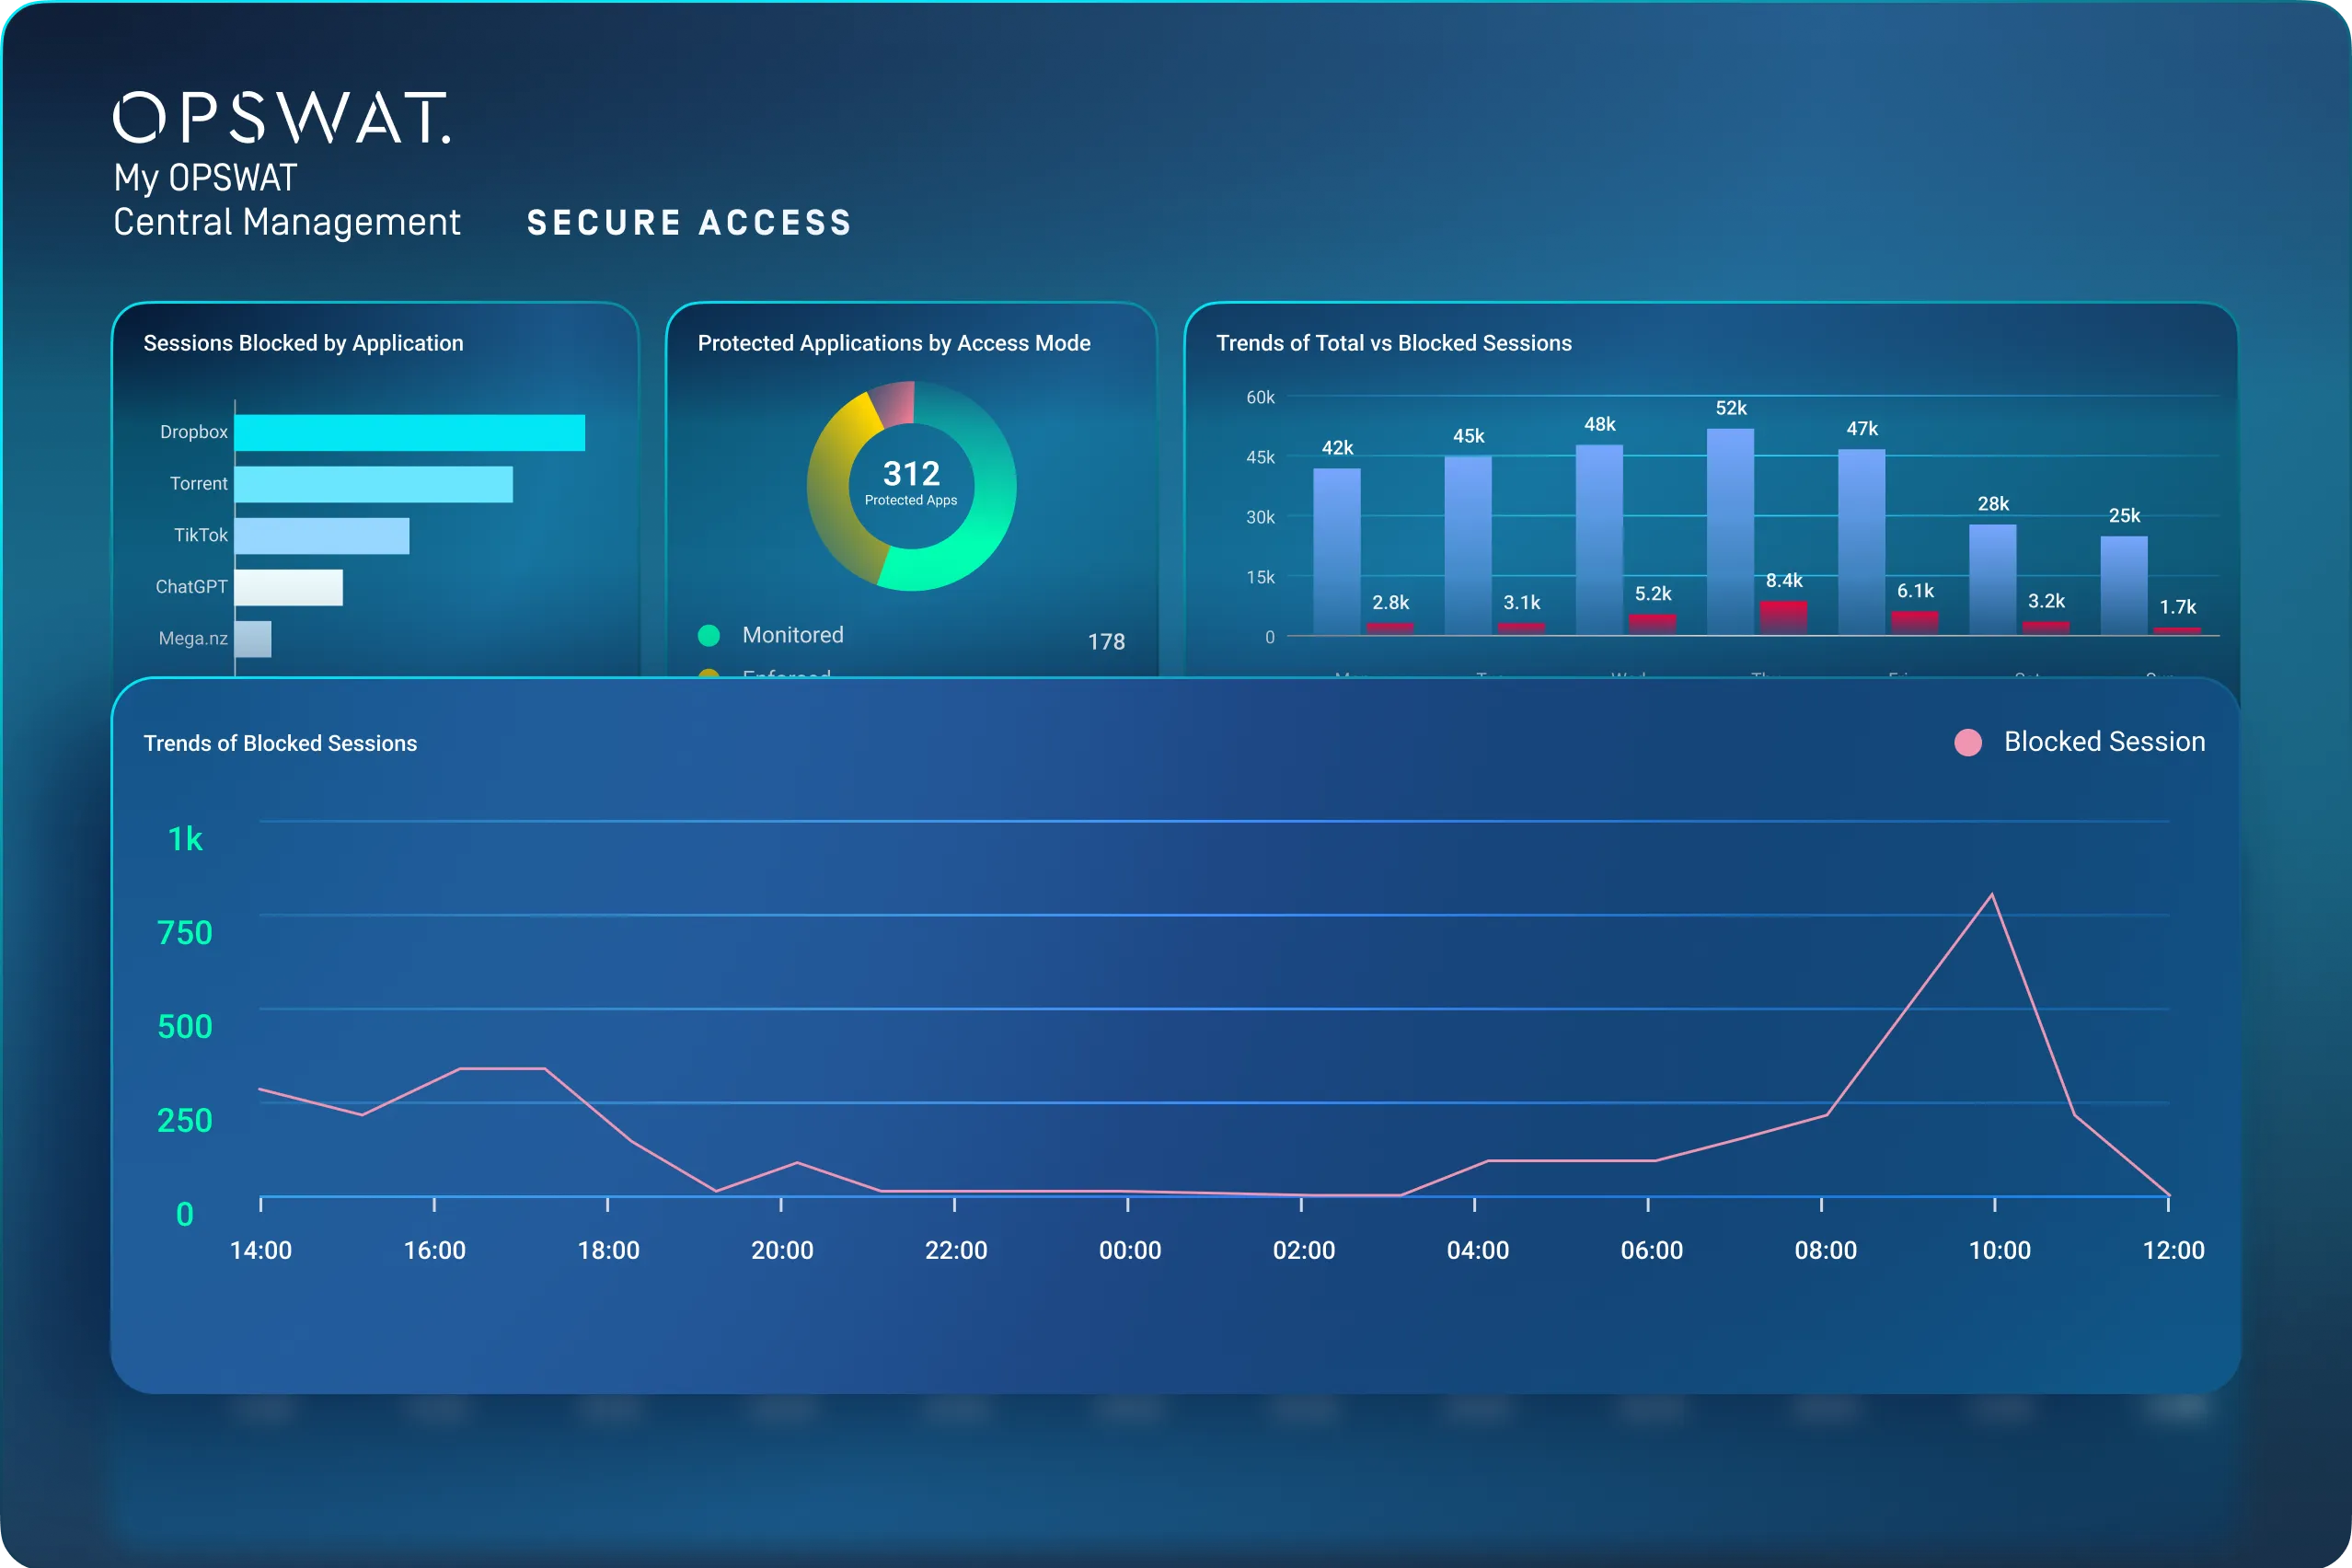
My OPSWAT Central Management gives security teams a single console to inspect devices, enforce compliance, and act on risk, before and after access is granted.
Centralized Visibility & Policy Control
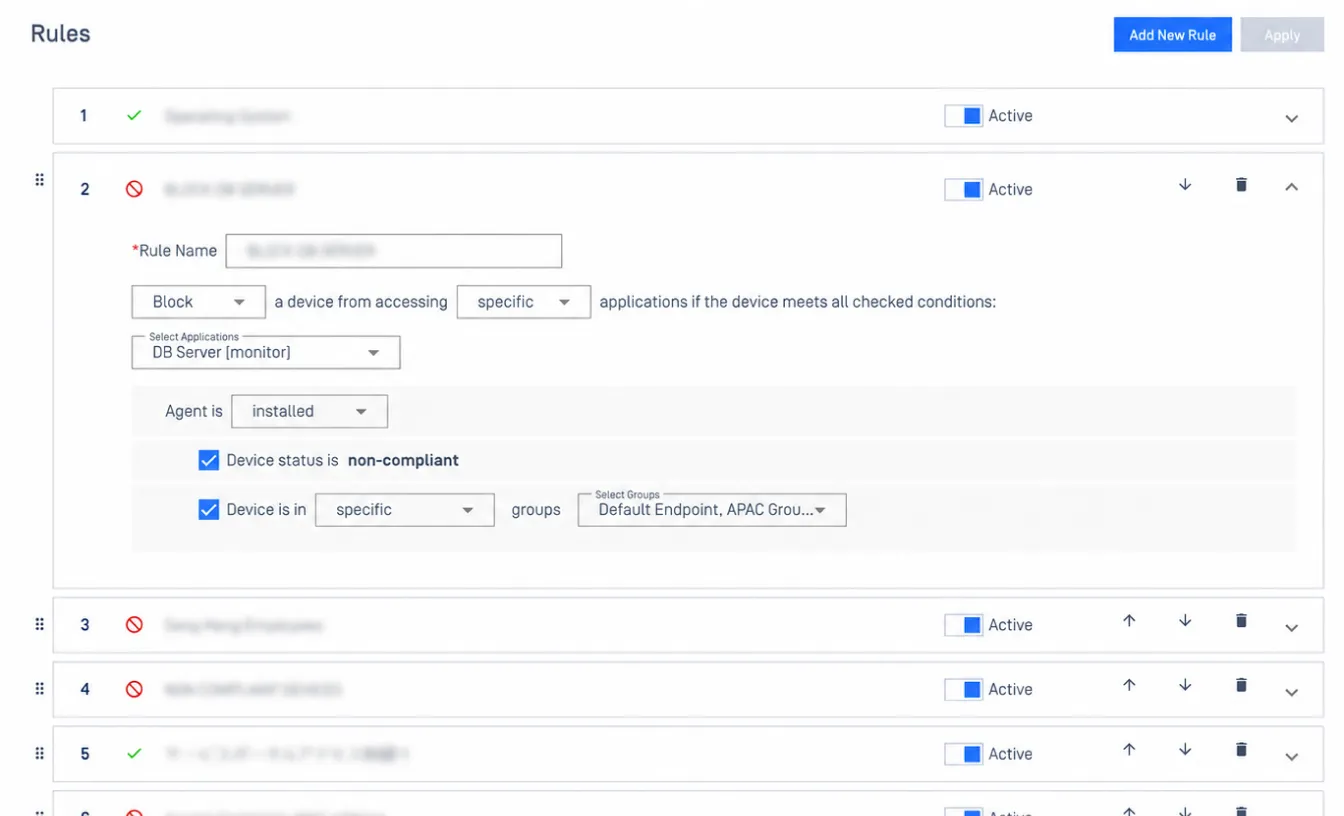
A single view of all devices and their access methods keeps IT teams informed as the workforce scales. Easily allow or block any device and enforce rules from one console.
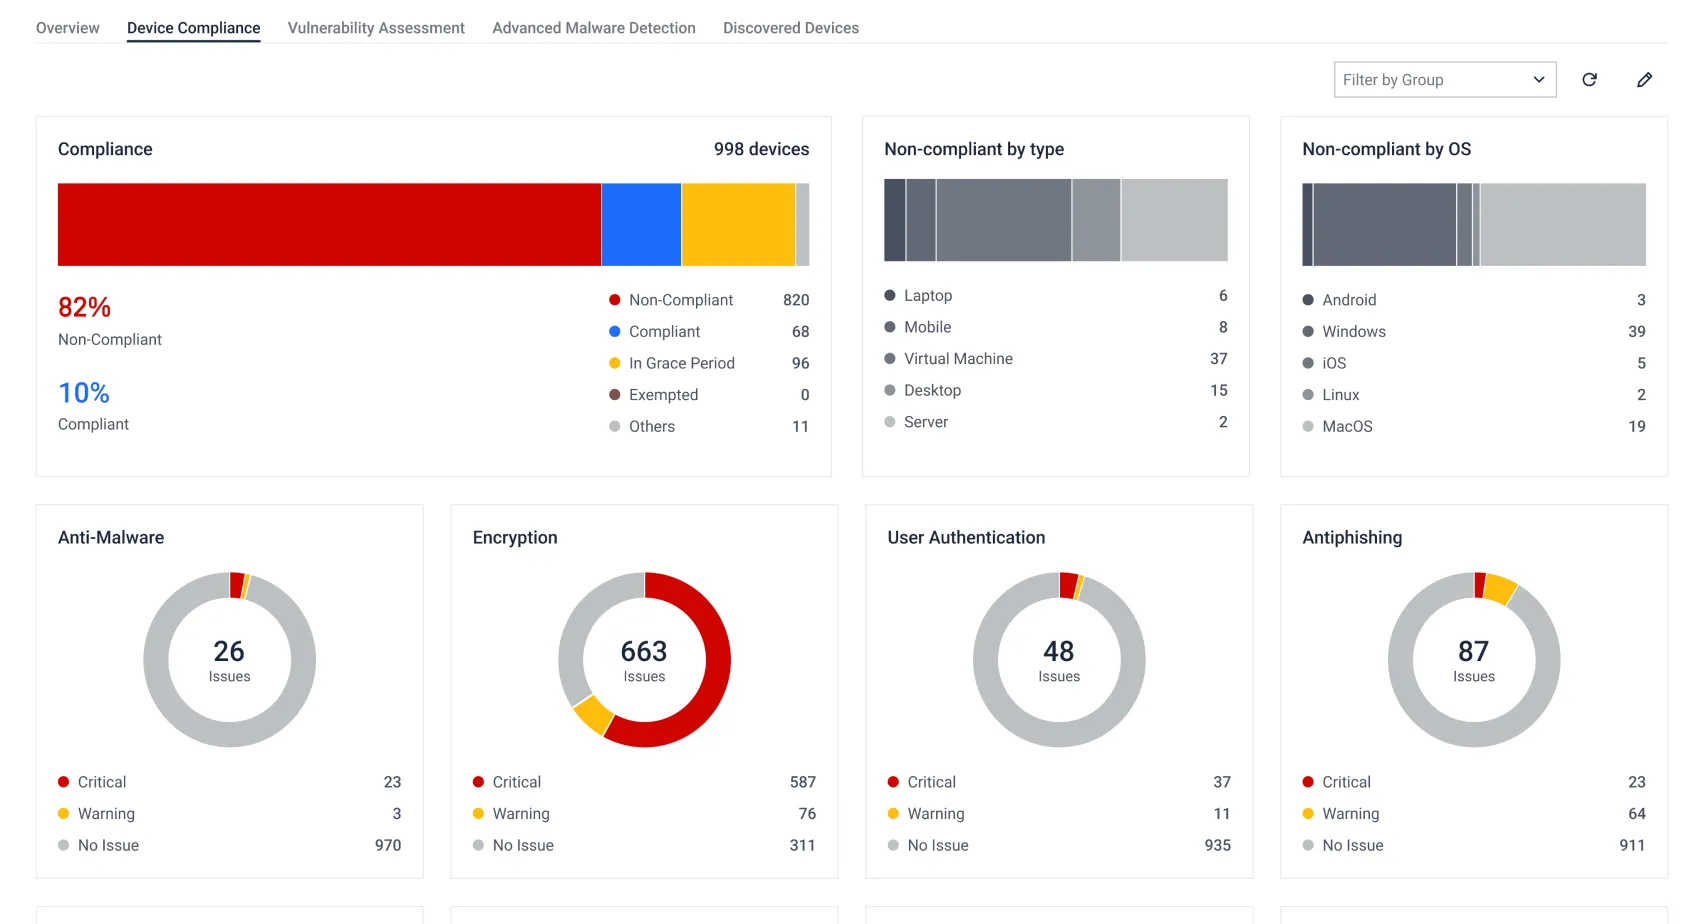
Real-Time Device Posture Checks
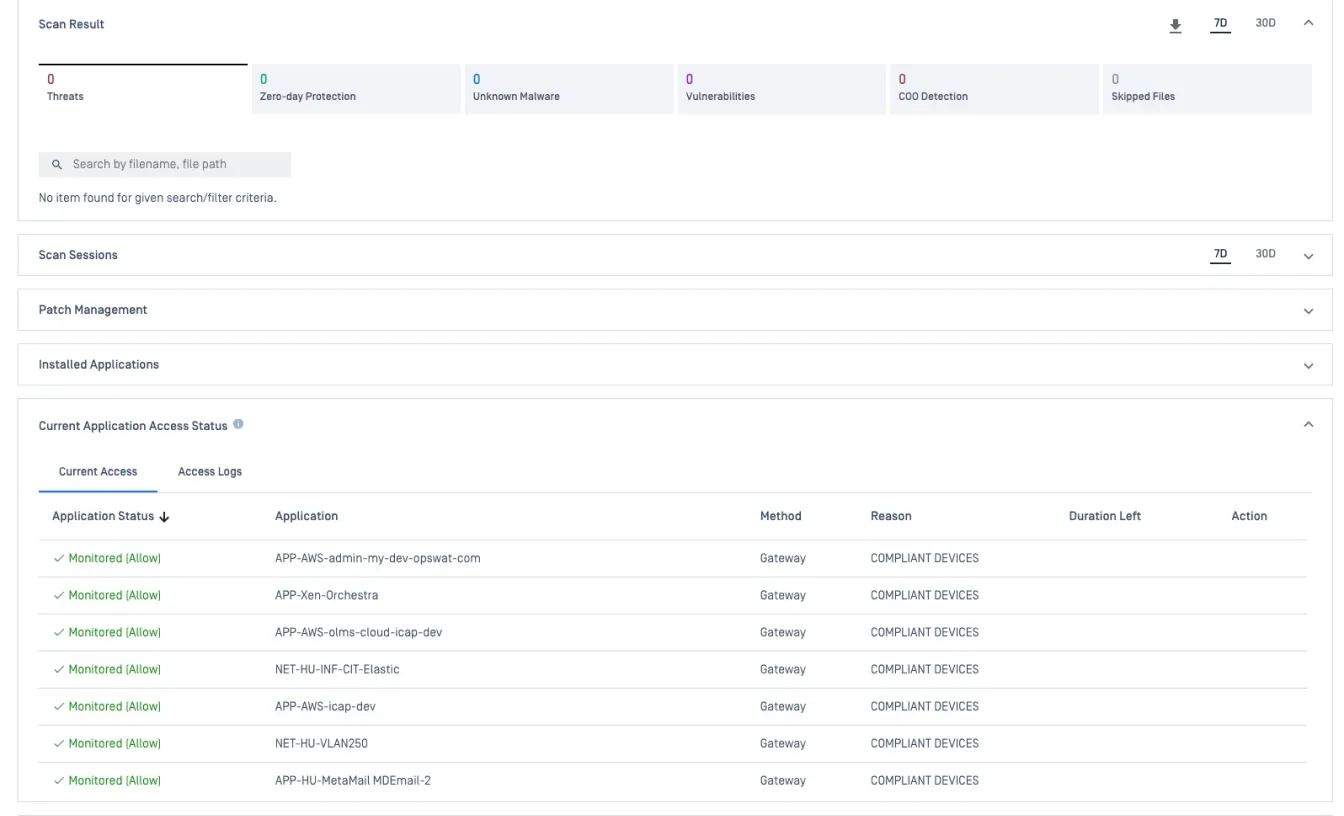
Get a complete, real-time view of endpoint health across the entire environment. Review detailed security data for any device, monitor which devices are accessing which applications, and track risk trends from one interface.
In-Depth Compliance & Control
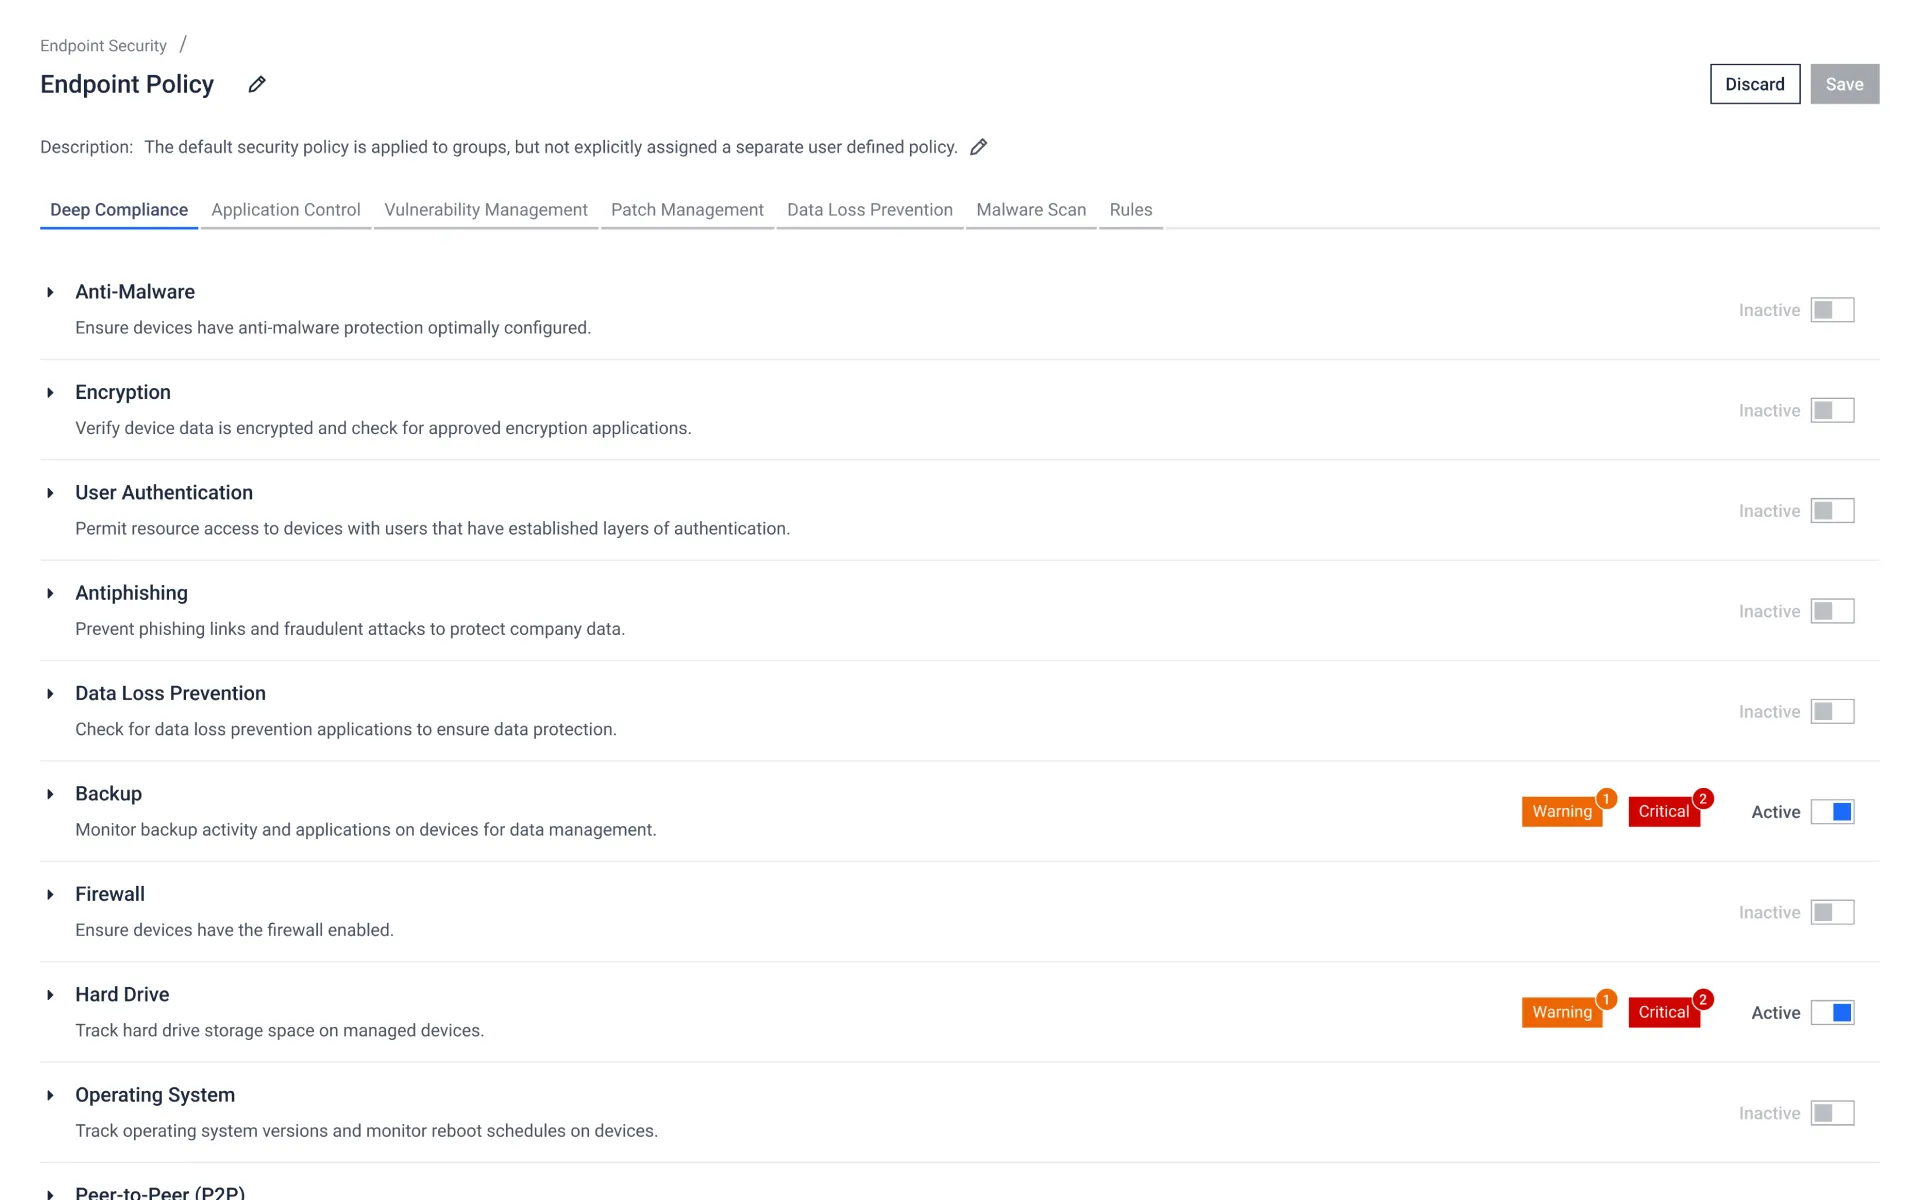
Perform deep device inspections across 5,000+ third-party applications covering controls such as disk encryption, anti-malware, backup, firewall status, and vulnerability scanning, going well beyond standard OS and antivirus checks.
- My OPSWAT Central Management


- My OPSWAT Central Management
- My OPSWAT Central Management
 MetaDefender Endpoint

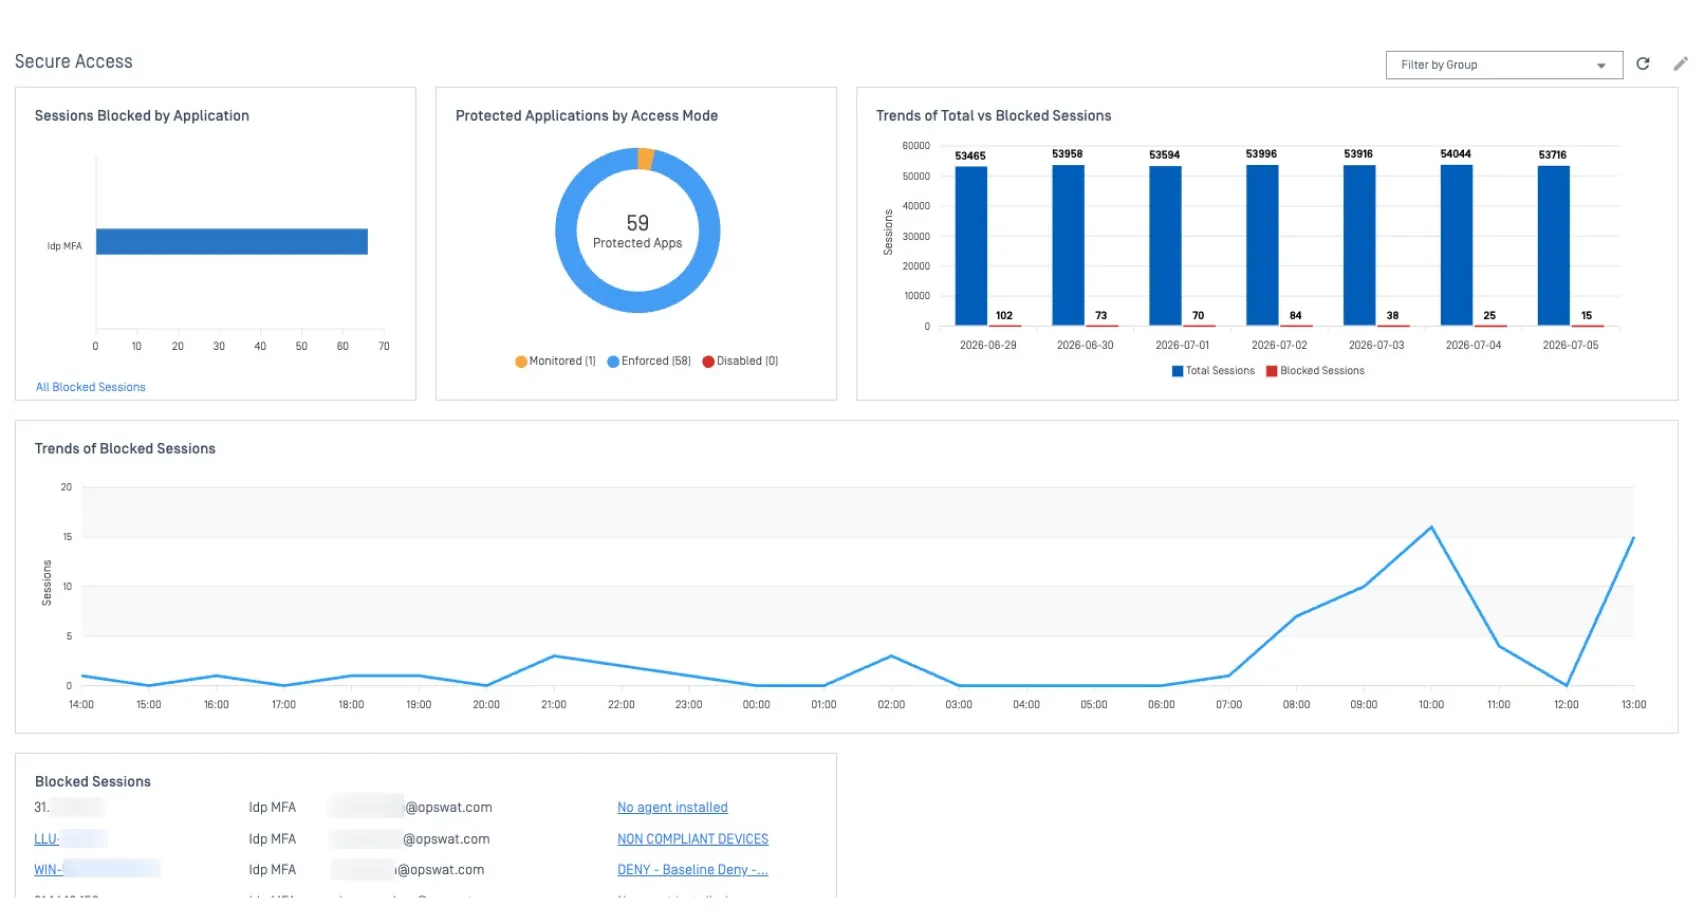
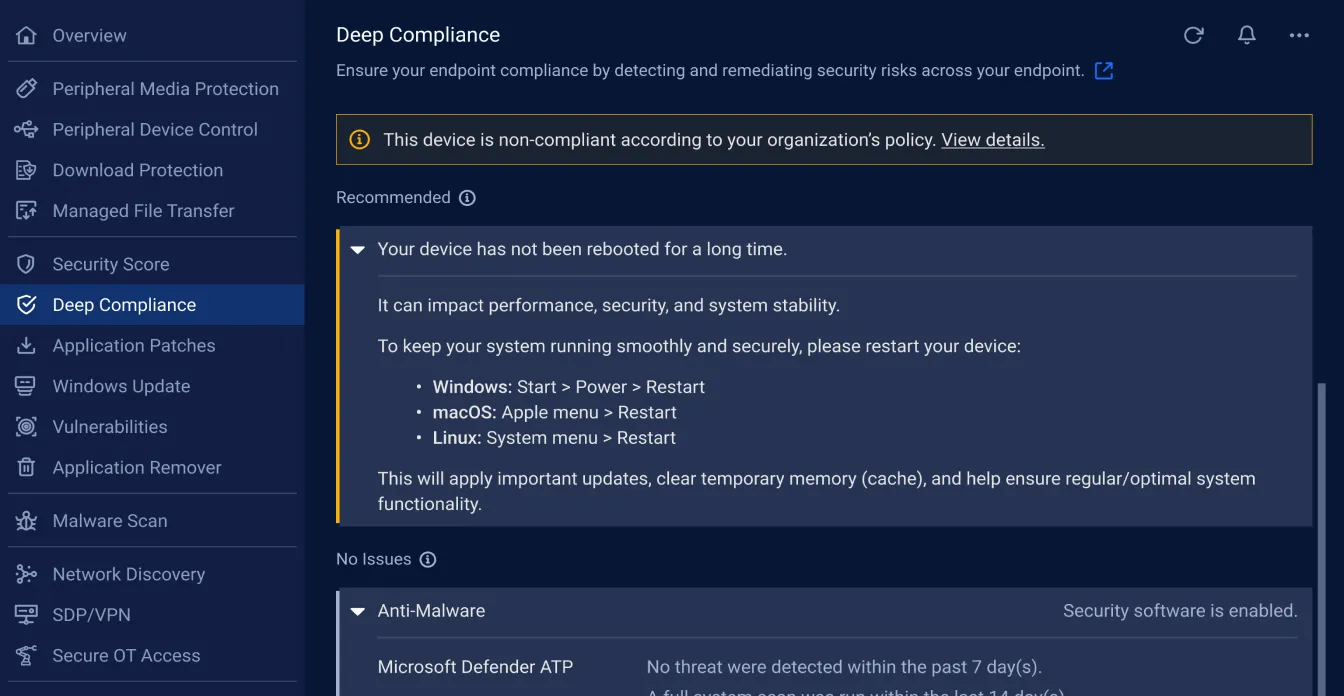
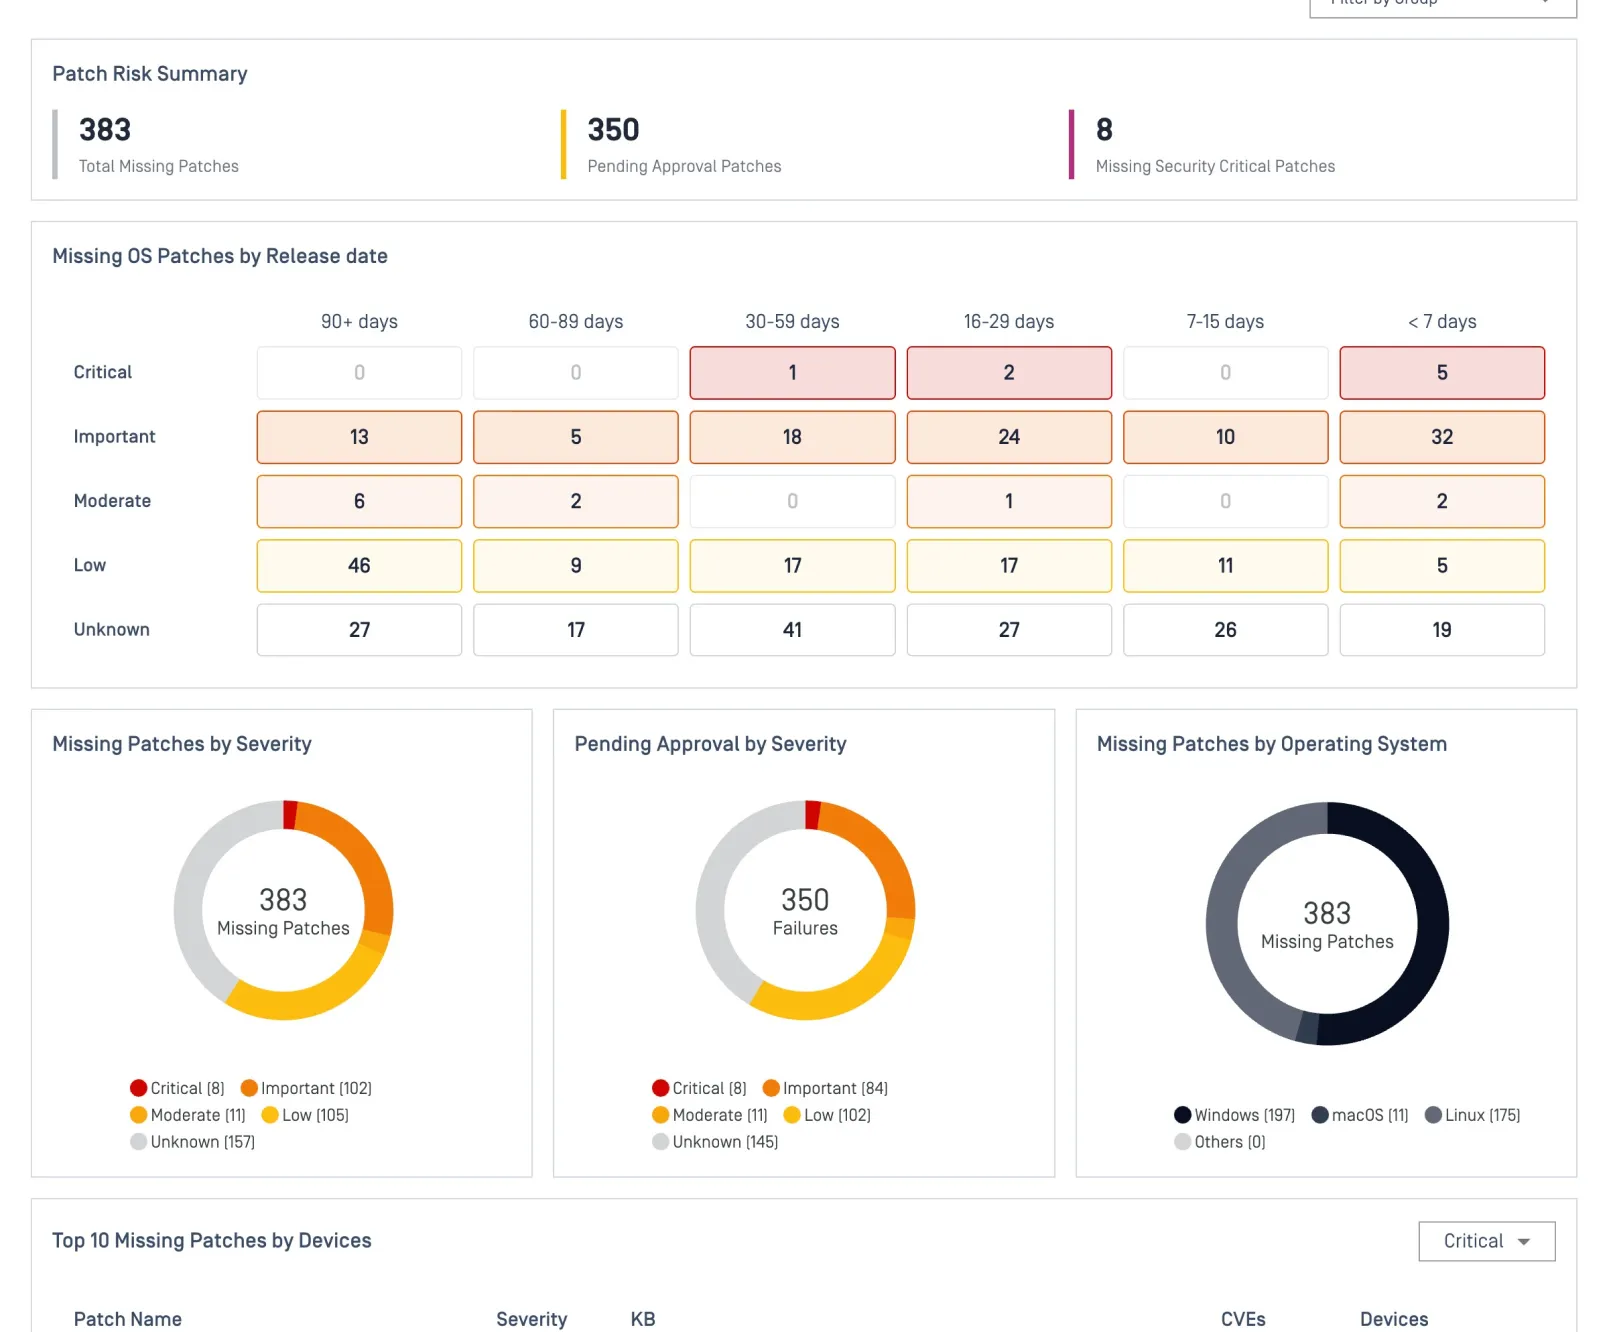
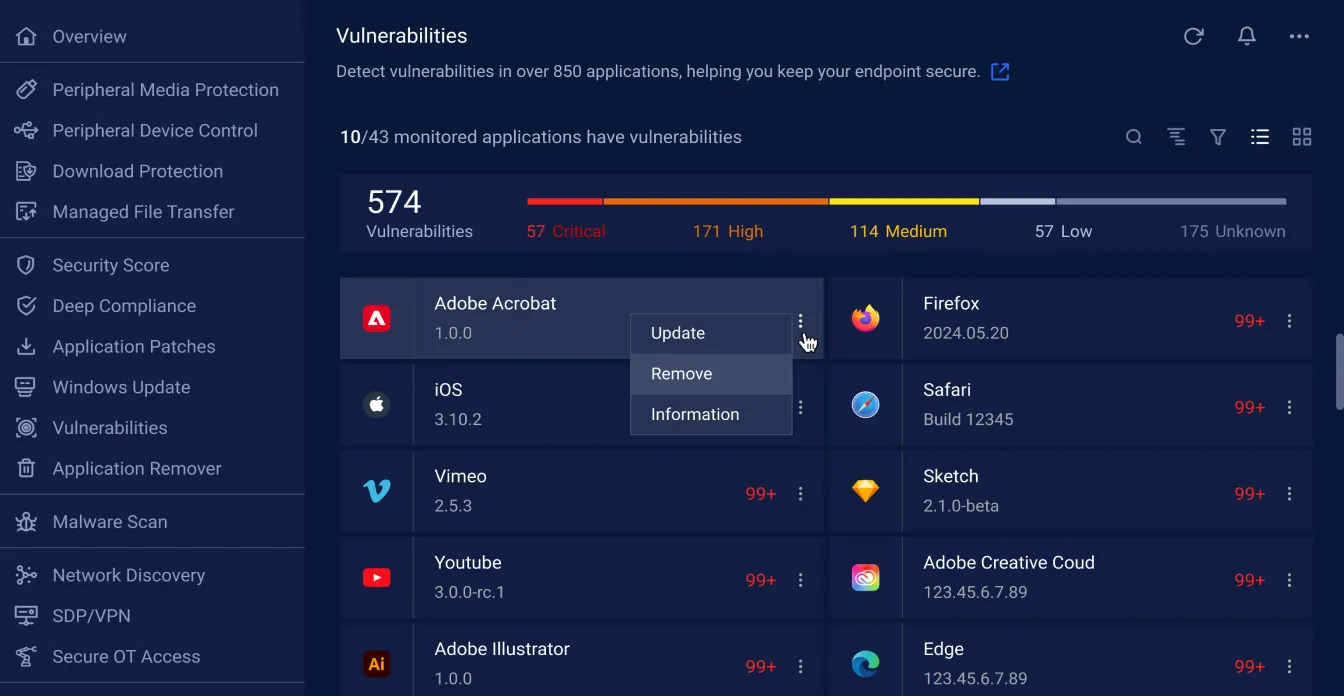
Up-to-Date Vulnerability and Patch Management
Detect known vulnerabilities from the CVE database and prioritize remediation using OPSWAT's proprietary scoring system, built from protecting over 100 million endpoints. Optimize patch management before vulnerabilities become exploits.
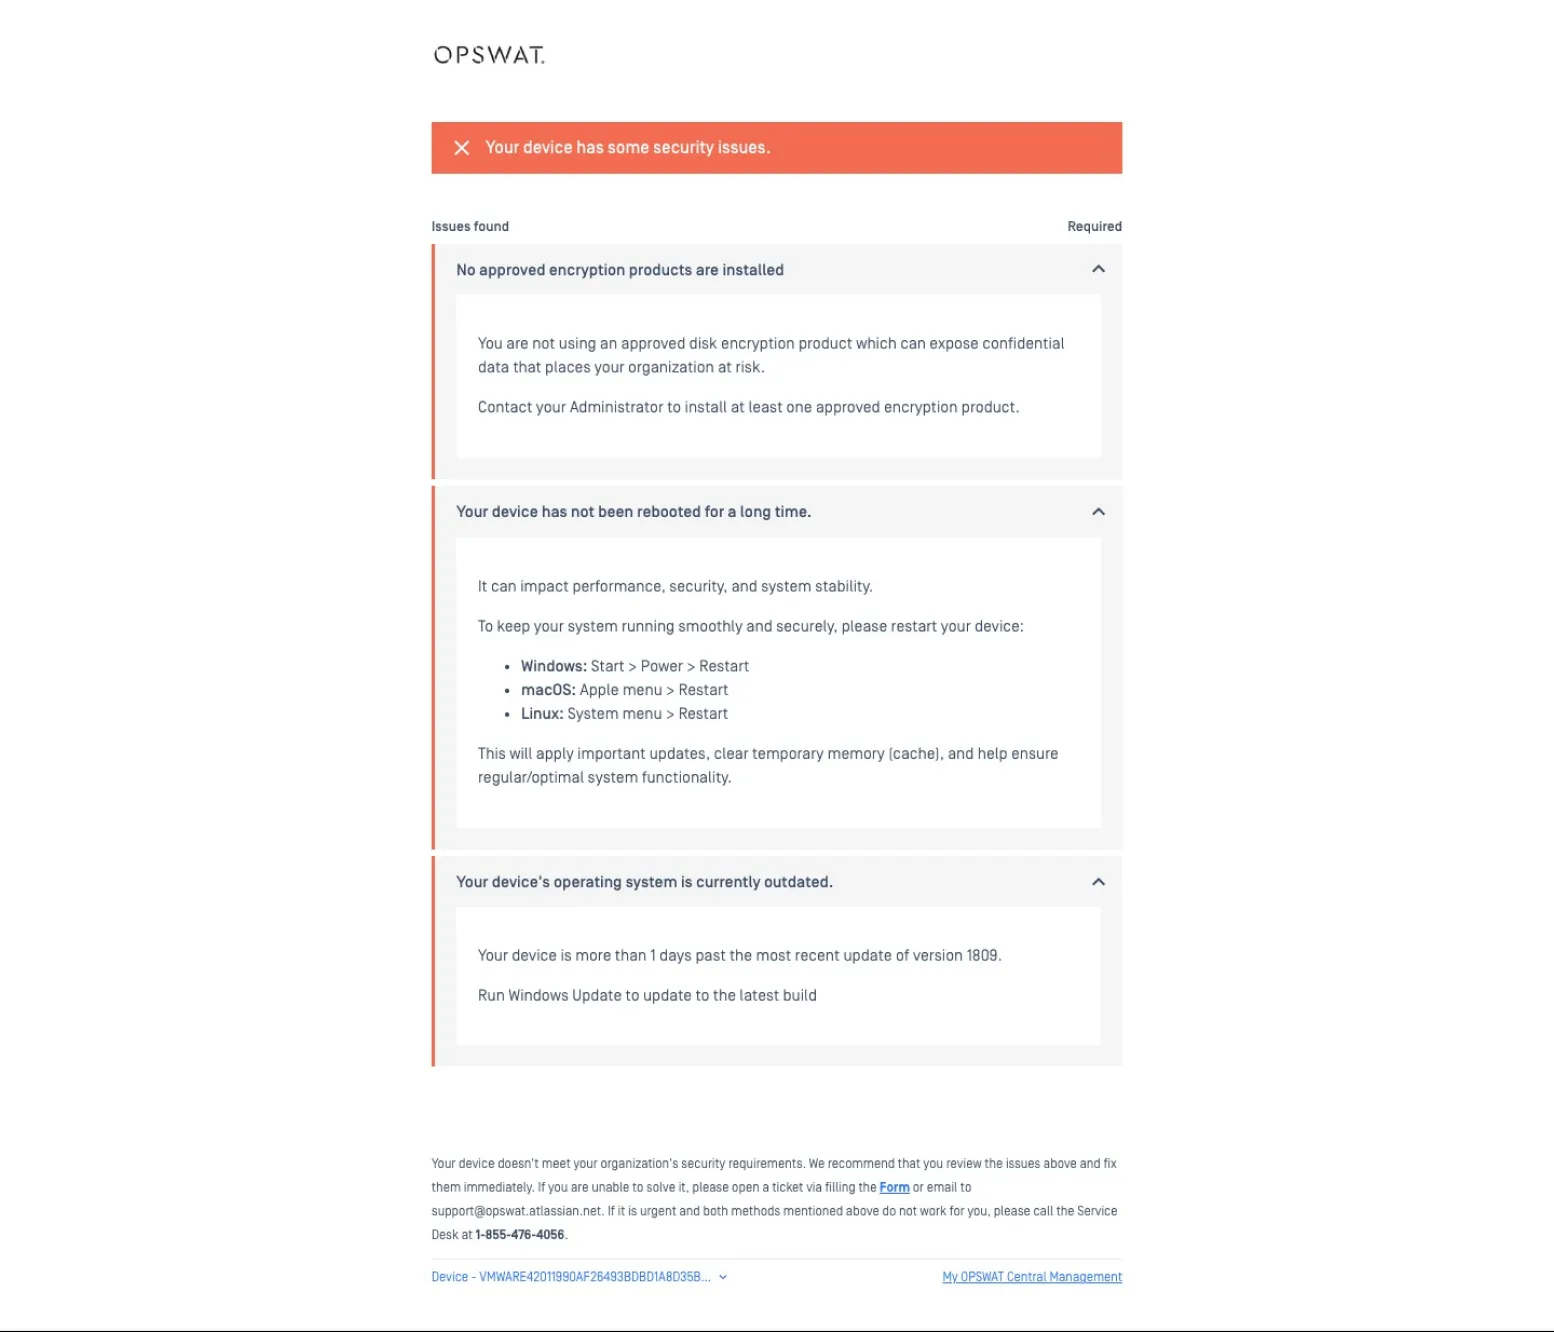
Automated and Self-Service Remediation
Users on non-compliant devices are redirected to a self-service page with specific instructions on exactly what to fix. Common remediations, such as updating antivirus definitions, activating firewalls, and removing unwanted apps, can be fully automated.
Device-Aware Network Access Control
Get precise device identification and real-time compliance enforcement across your network. Block unauthorized connection attempts and enforce segmentation to place IoT devices in the appropriate group.
- My OPSWAT Central Management
 MetaDefender Endpoint
- My OPSWAT Central Management


- My OPSWAT Central Management


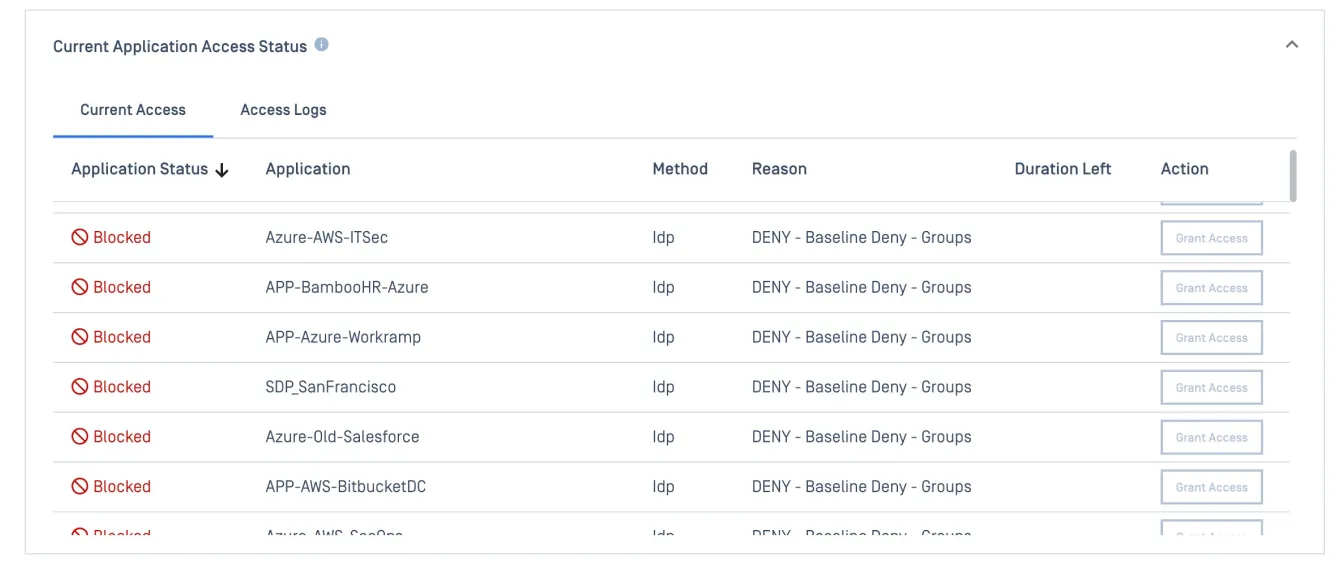
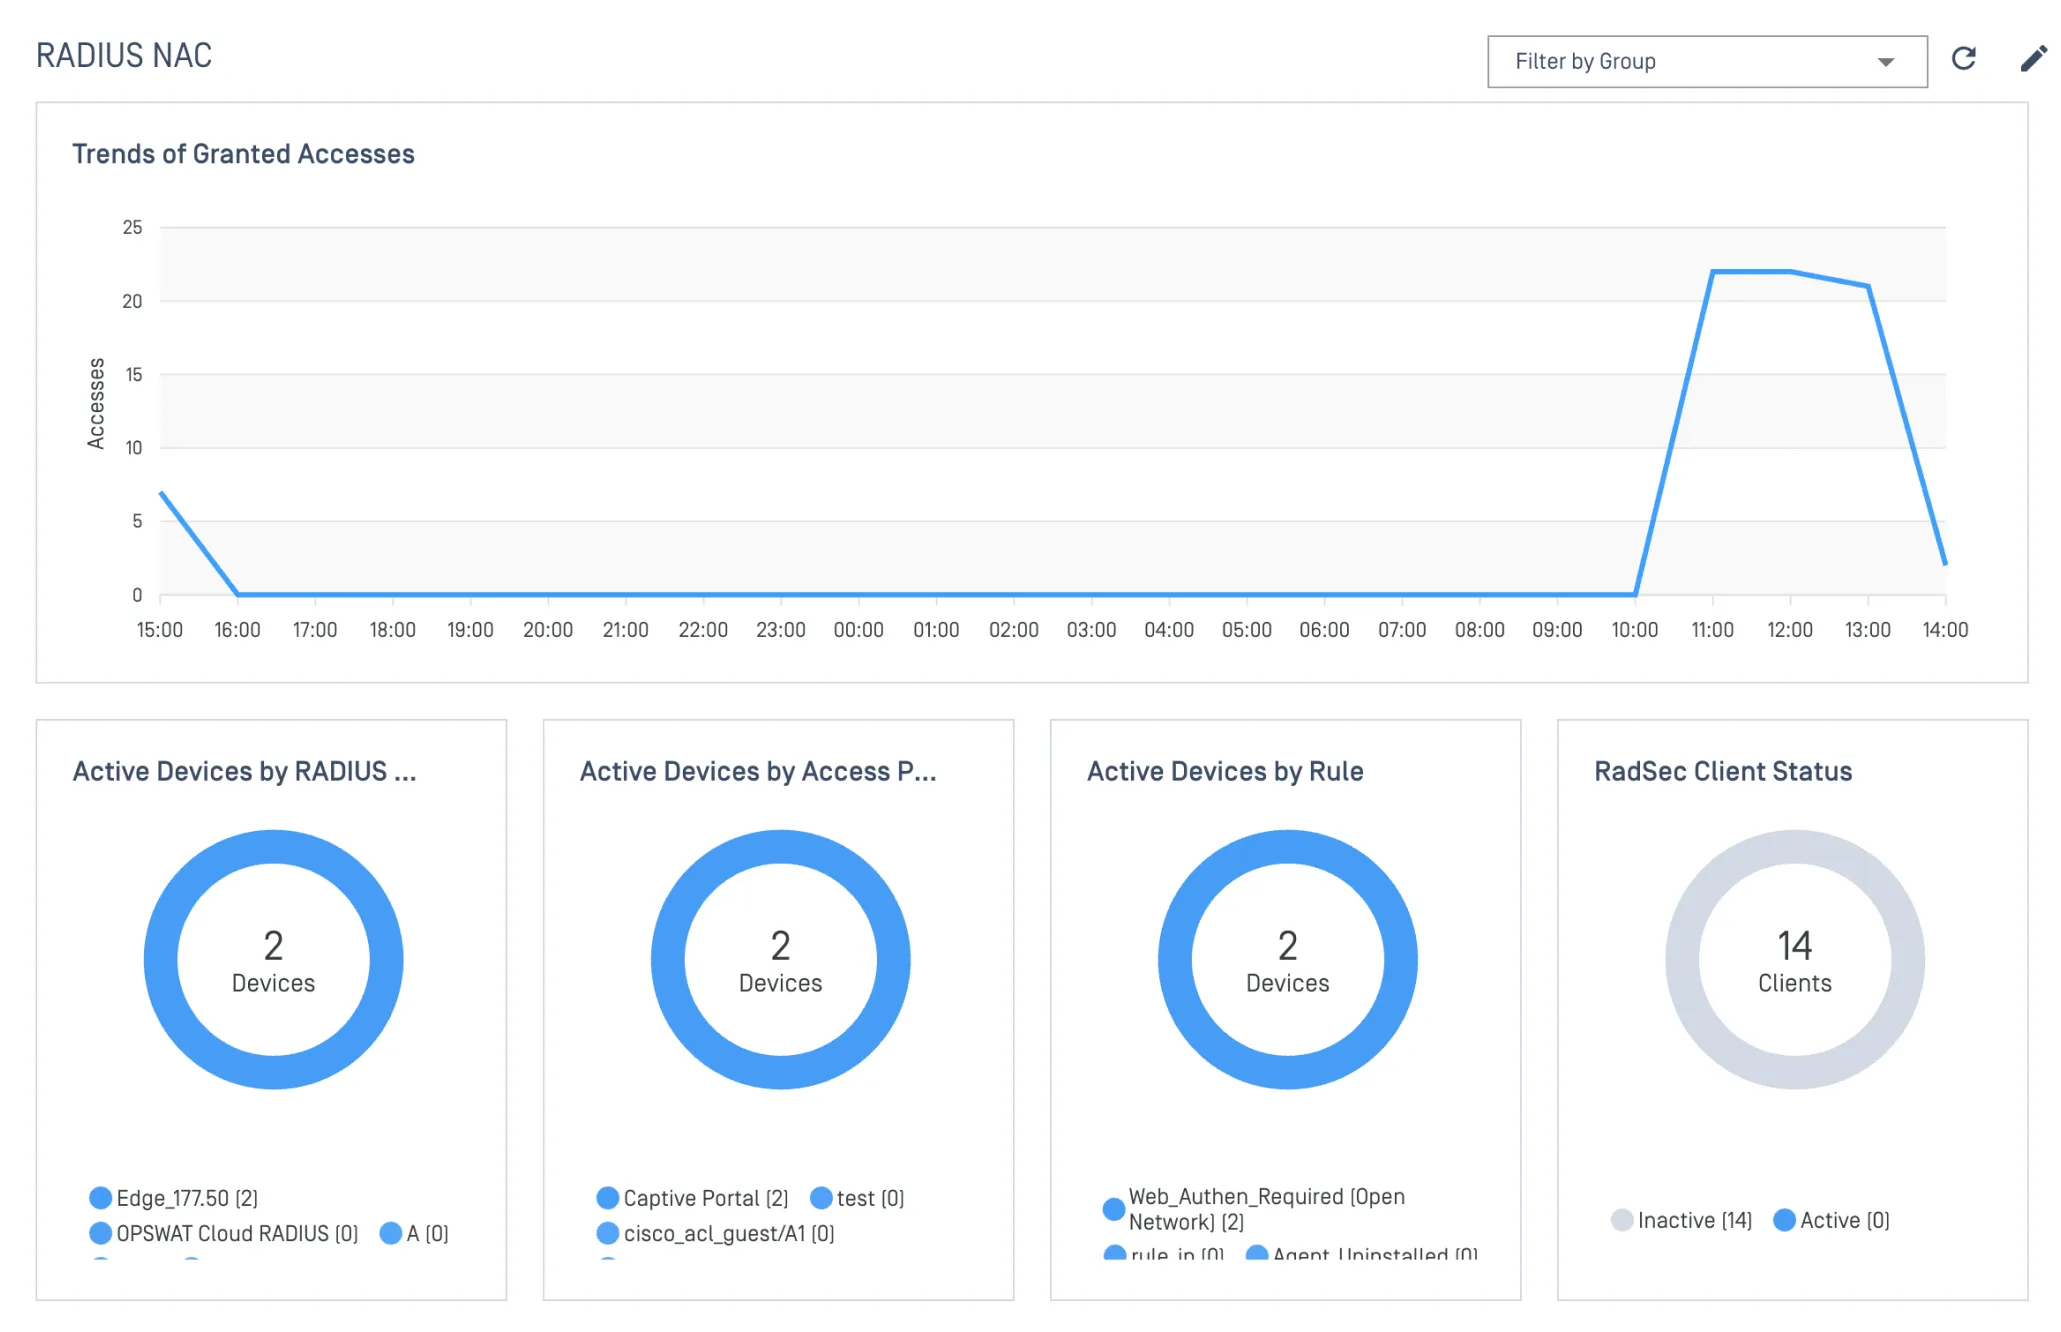
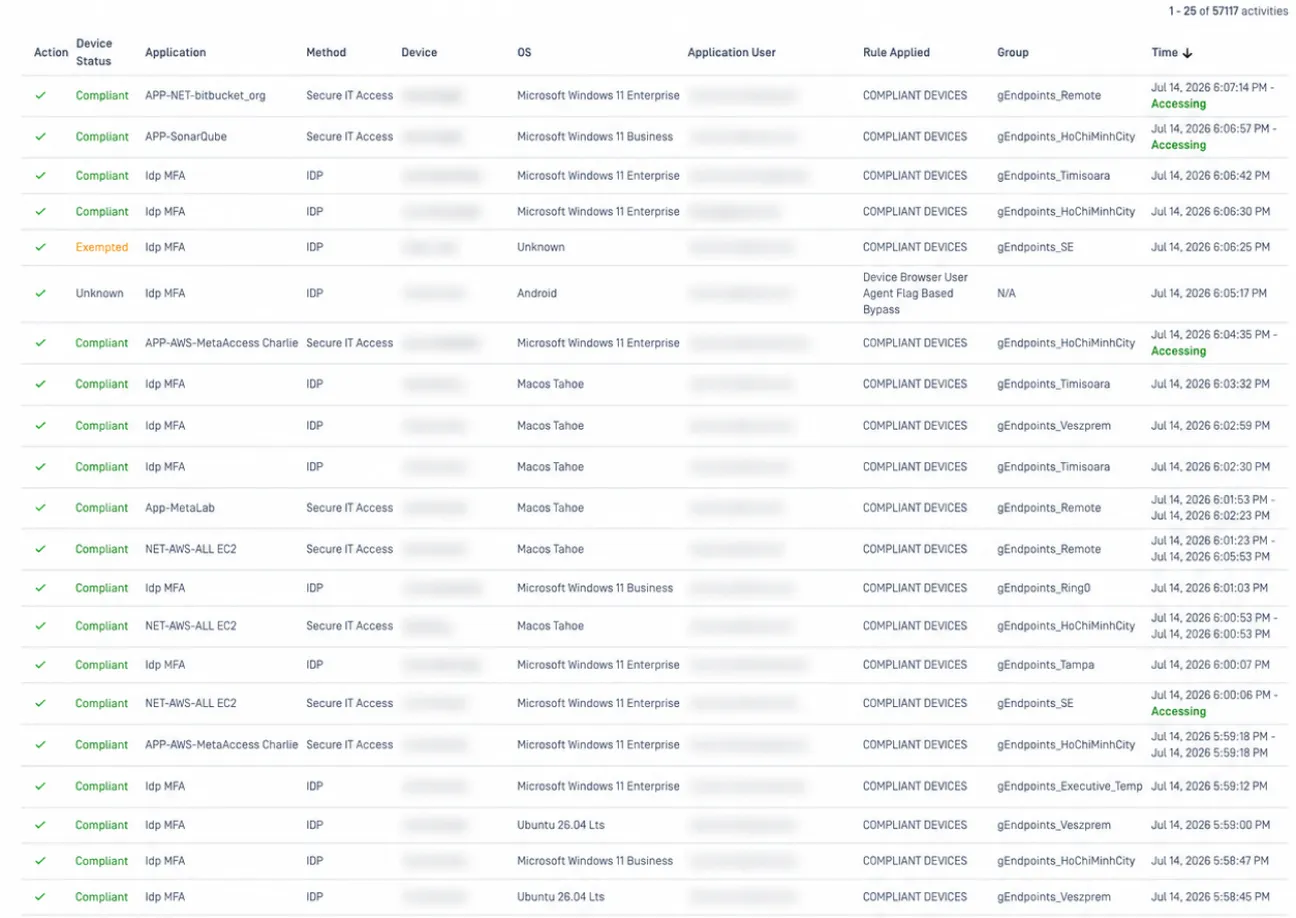
Choose the Access Method That Fits
Your Architecture
My OPSWAT Central Management ensures only authorized, compliant devices can access your applications and networks, regardless of environment or access method.
Application-Level Zero-Trust Access
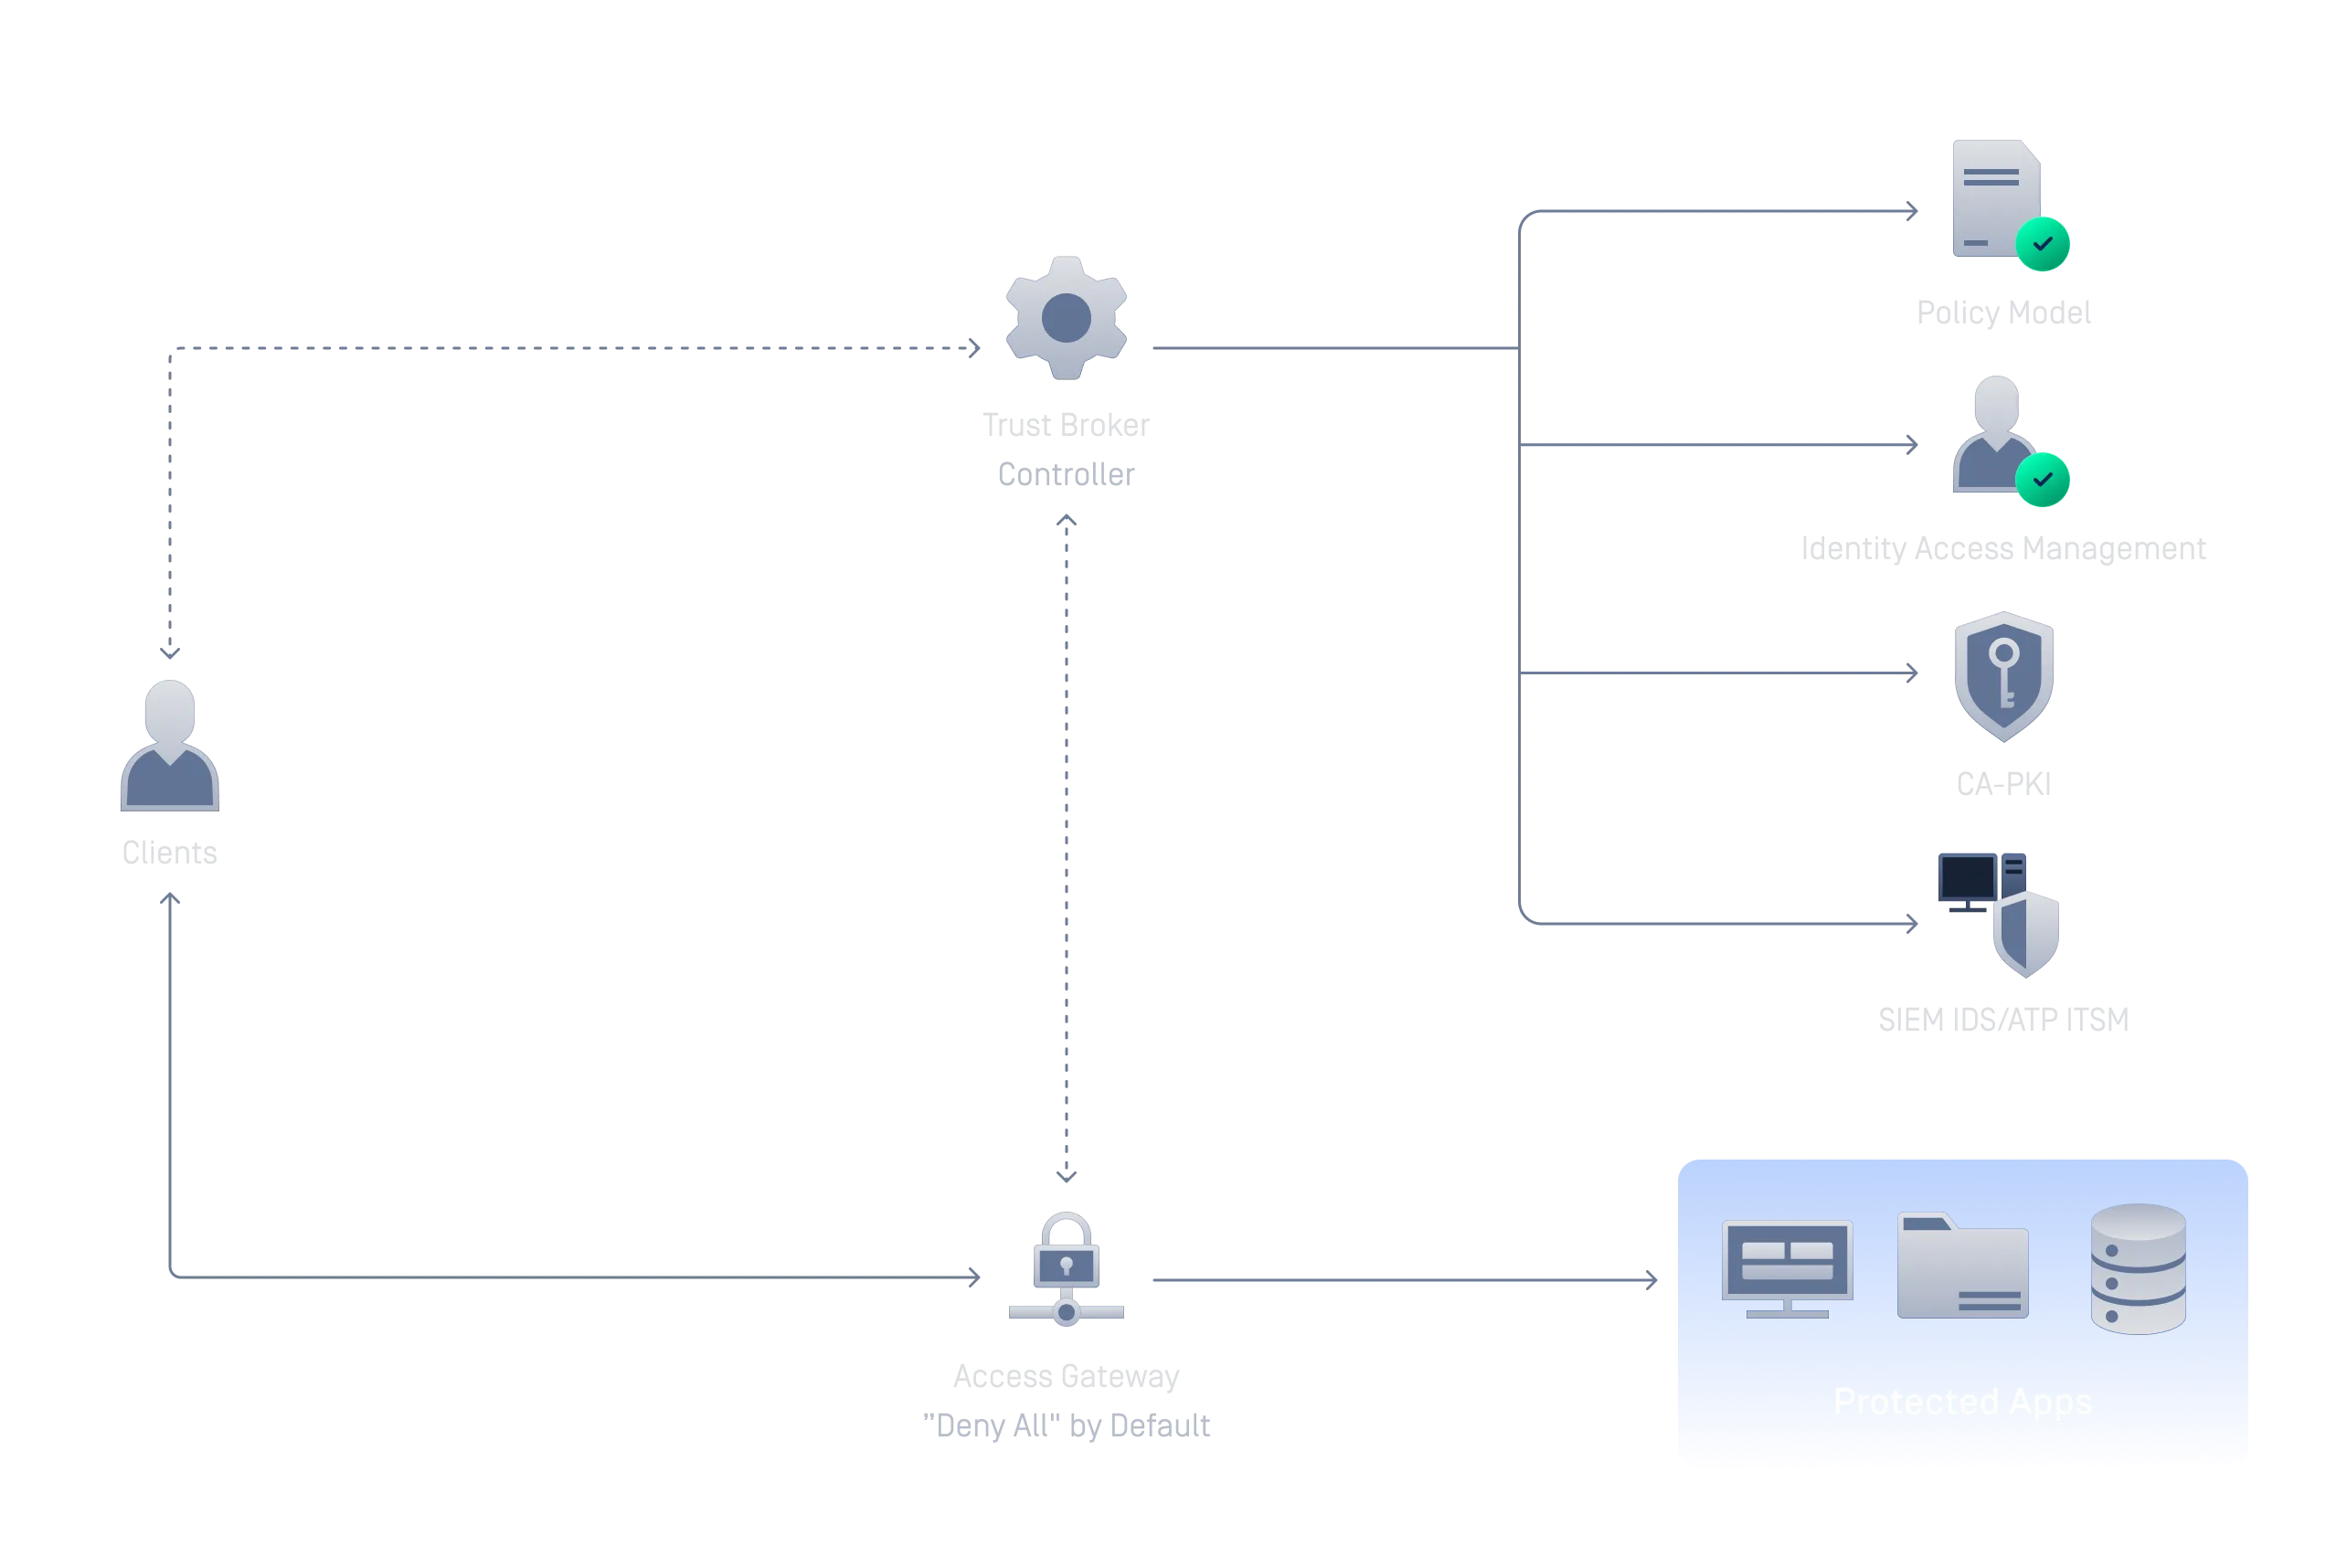
Protected Resources Stay Hidden Until Identity and Device Compliance Checks Pass
Replace broad, legacy VPN access with application-level zero trust. Protected apps stay invisible to unauthorized devices; access is granted only after identity and compliance are verified.
Single Sign-On With Verified Device Access
Connect your existing Identity Provider to enforce SSO across corporate applications, with device compliance checked at every login, not just credentials.
MFA That Checks the Device, Not Just the User
Standard MFA verifies two layers: your credentials and a second factor. OPSWAT's IdP MFA adds a third layer by verifying the device's health and compliance. Non-compliant devices are blocked even with valid credentials, and users are guided to fix issues themselves.
Secure Access for Virtual Desktops
Device Compliance Enforcement for Omnissa Horizon Environments
Enforce device compliance before virtual desktop and published app sessions launch. Only endpoints that pass posture checks can access your Omnissa Horizon environment.
Automated Network Access Control for Every Device
Automatically verify every device trying to access your network and enforce access policies in real time. Profile devices with or without an agent, control access by identity, device type, location, and posture, and deploy as cloud-native SaaS, hybrid, or fully on-premises for air-gapped environments.
Learn More About MetaDefender NAC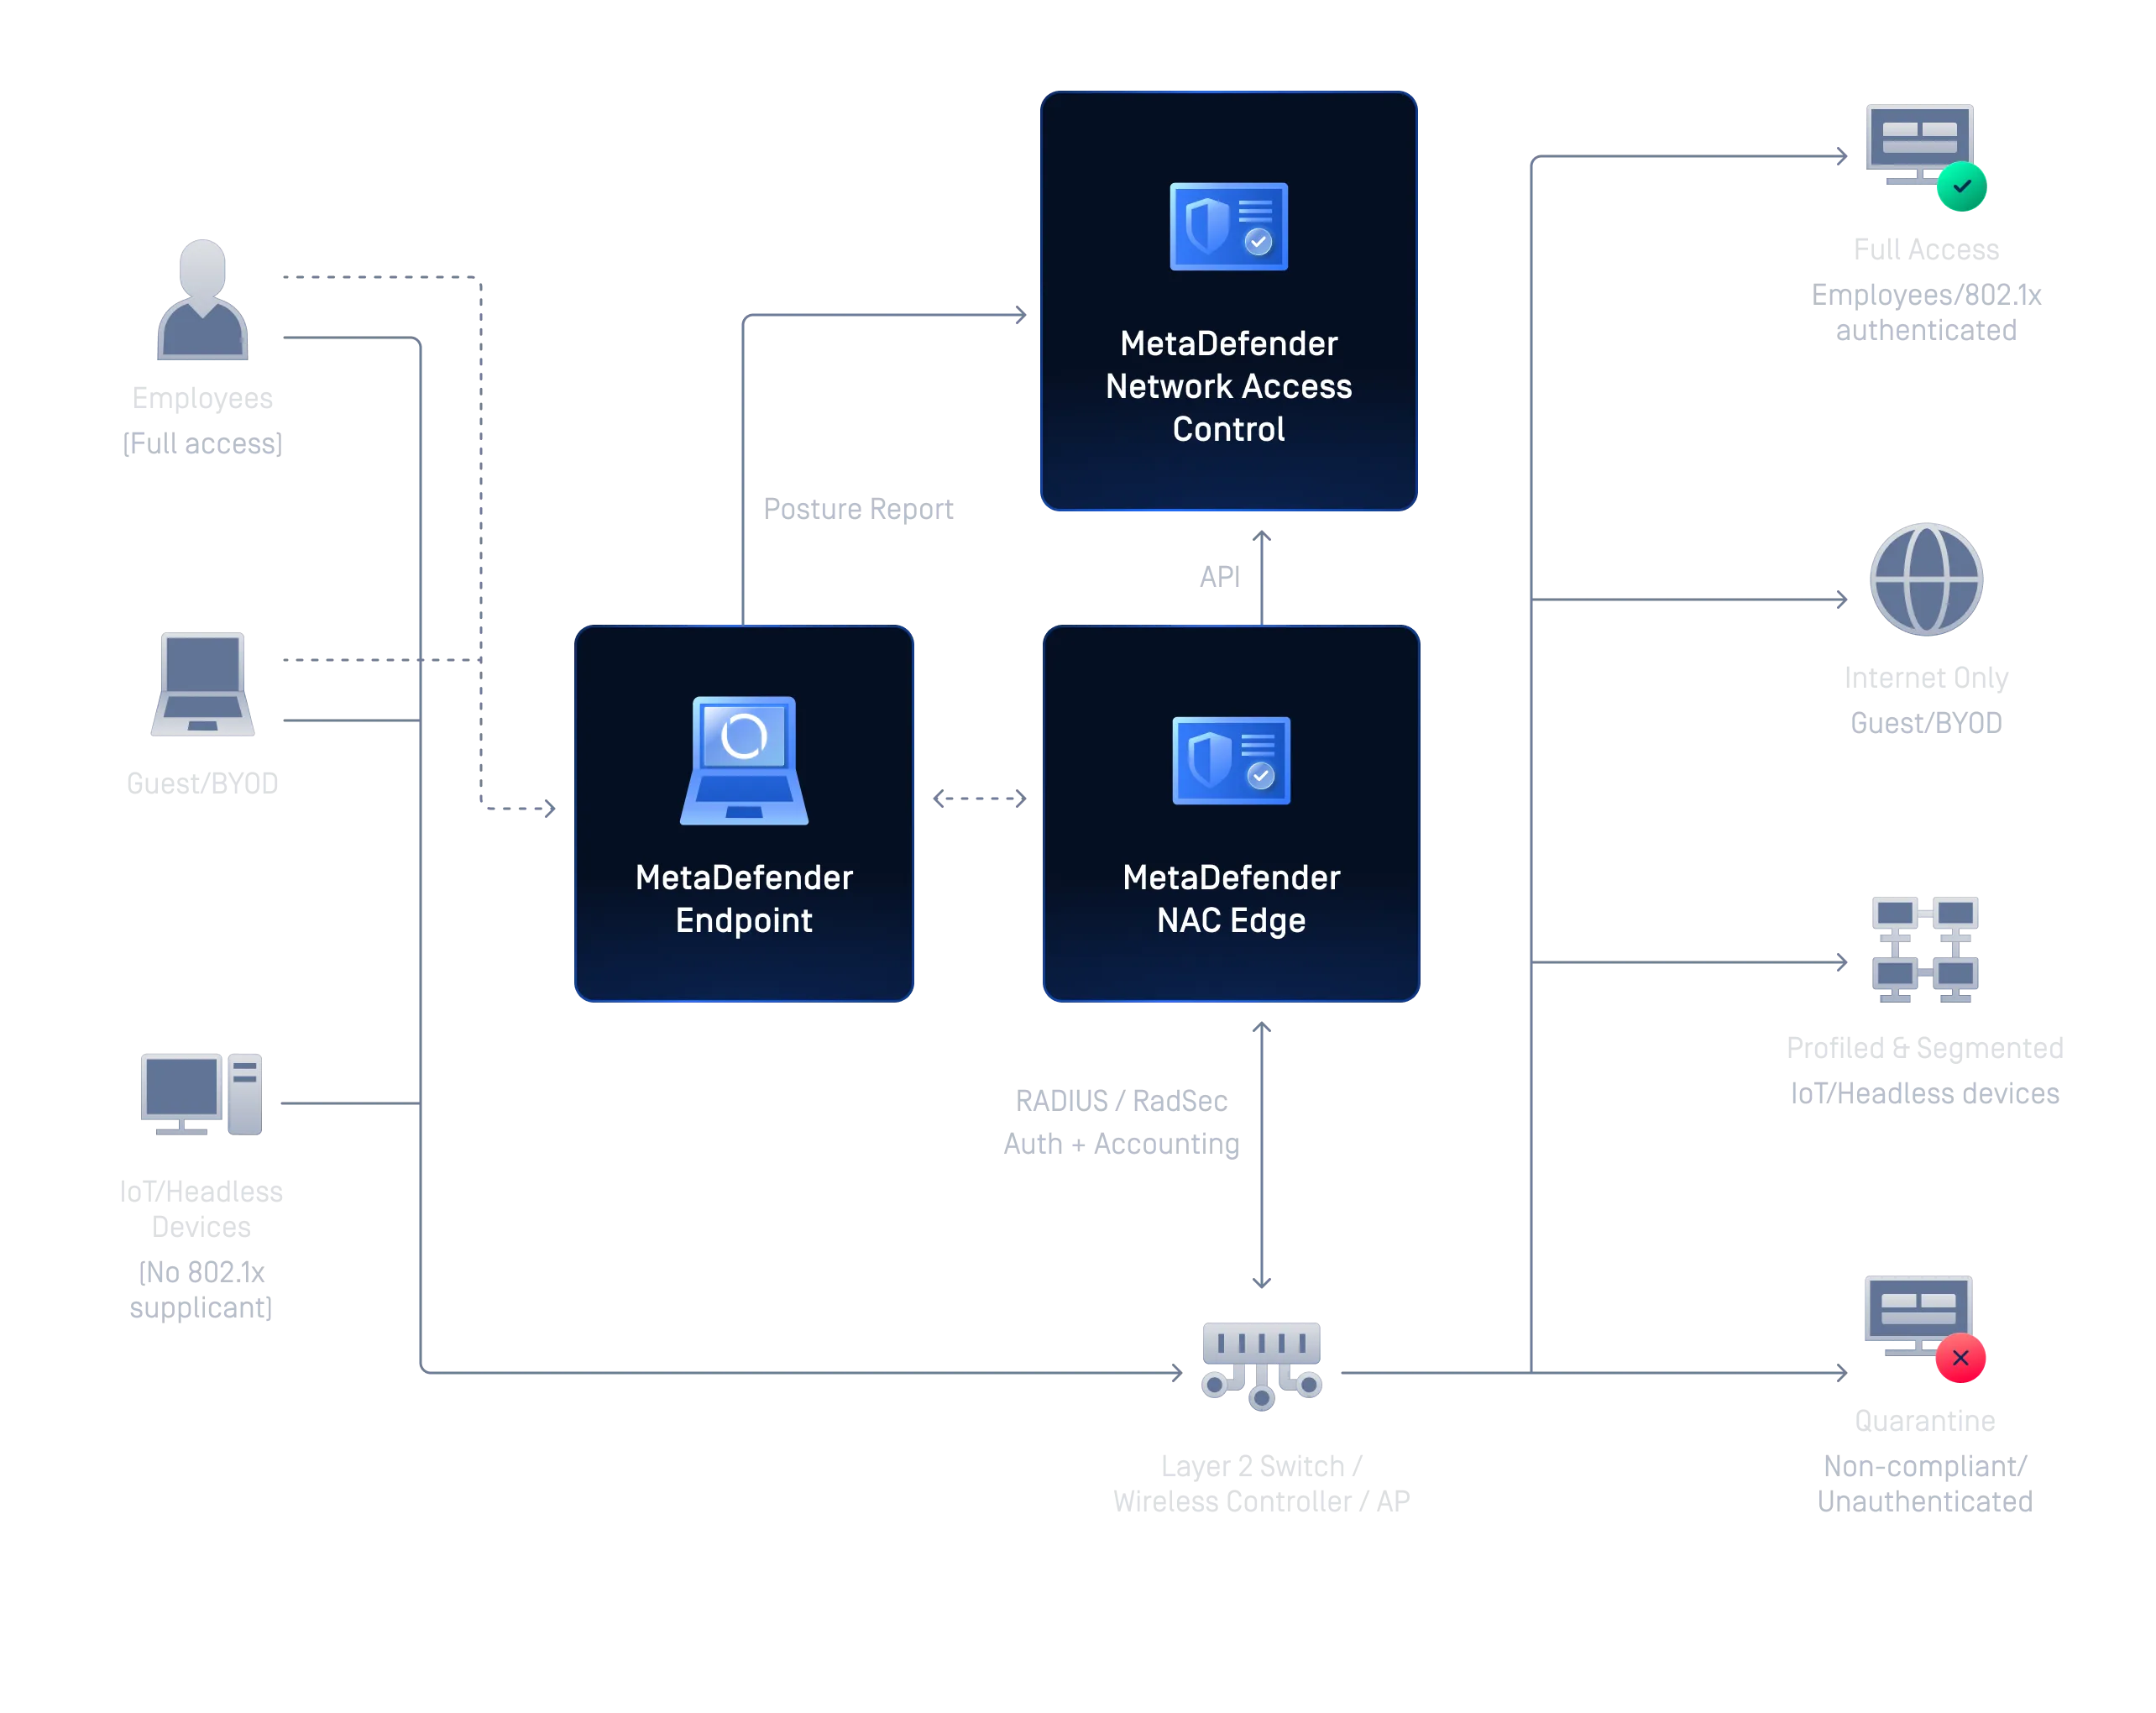
Works With the Stack You Already Run
Connect your existing identity providers, MFA, and virtual desktop infrastructure without changing your
infrastructure or replacing what works.
Trusted by Security Teams in
Regulated Industries
OPSWAT is trusted by over 2,100 organizations worldwide to protect their critical data, assets, and networks from
device and file-borne threats.
- “Once the agents were deployed, we were quickly able to validate more than 70,000 remote user devices' security before accessing our network, with no impact to productivity.”Miroslav SklanskyHead of Information Security Technology, EPAM
- “Excellent product. Great support. We have a safer and clearer understanding of our security posture and potential risks we might have.”Stephen WaltersInfrastructure Manager, Genesis Investment Management
- “With third-party vendors accessing our systems daily, enforcing a consistent, zero exceptions authentication system was a necessity, not an option. OPSWAT’s technology ensures that only compliant devices can connect to our cloud resources.”Senior Security Engineer
Secure Access Across Every Digital Edge
Tailor your zero-trust architecture to fit the practical demands of distributed corporate teams and sensitive industrial environments.
Empower a Secure Remote Workforce
Validate the real-time health of employee devices before granting access to any application or network resource. Devices that fail compliance checks are blocked or redirected to self-remediation automatically.
Protect Your Critical Infrastructure from Untrusted Devices
Profile every device entering your industrial and critical infrastructure sites, such as contractor laptops, BYOD, and IoT equipment, and assign it to the appropriate network zone before access is granted. On-premises deployment is fully supported for air-gapped sites.
Secure Every Device Before It Joins Your Network
Validate device identity, security posture, and compliance before granting network access. Unauthorized or non-compliant devices are automatically blocked, quarantined, or redirected to self-remediation, helping prevent threats from entering the network.
Regulatory Audit Readiness
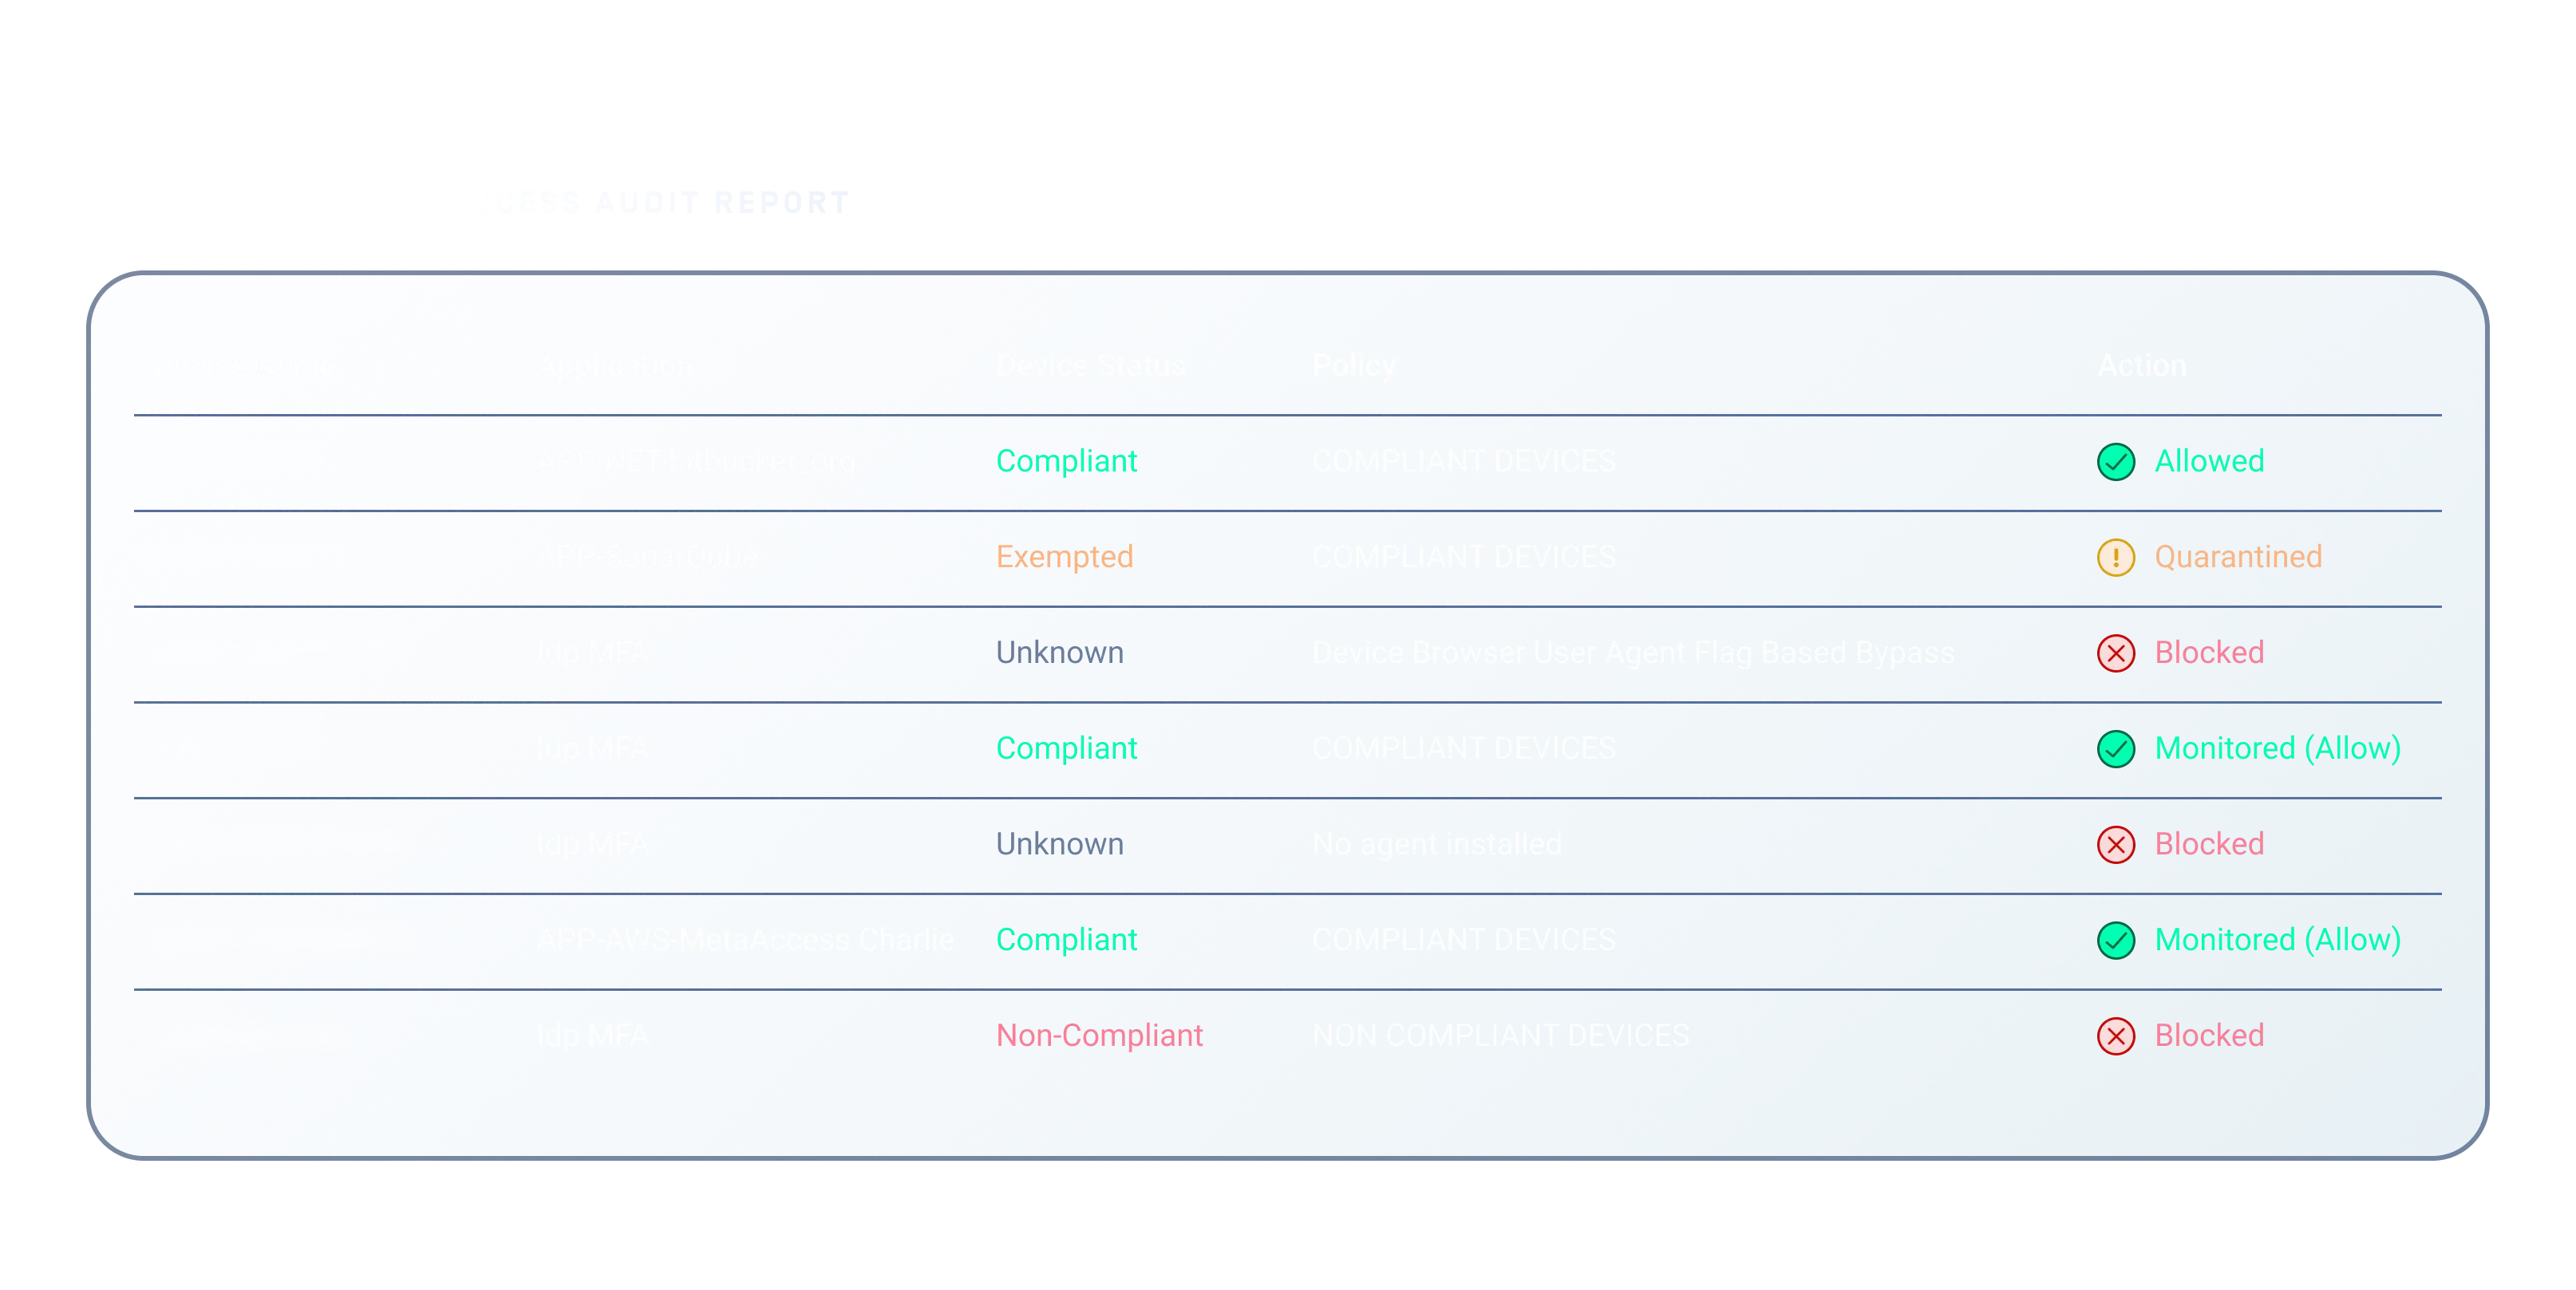
Maintain detailed audit trails, posture reports, and policy enforcement records across every access event, giving auditors exactly what they need to verify compliance with frameworks such as PCI DSS, HIPAA, NIST 800-53, ISO 27001, FISMA, FedRAMP, FINRA, HITECH, SOX, CIS Controls, COBIT, and SANS.
Recommended Resources
My OPSWAT Central Management Datasheet

My OPSWAT Central Management Documentation

Unifying Device Monitoring in Smart Manufacturing with My OPSWAT Central Management

European Renewable Energy Producer Upgrades Cybersecurity with OPSWAT

Securing Access to Proprietary Code with My OPSWAT Central Management: A Leading Game Developer’s Story

EPAM Ensures Secure Remote Access and File Security with My OPSWAT Central Management and MetaDefender Cloud

Ping Identity and OPSWAT Revolutionize Access Security with DaVinci and My OPSWAT Central Management

Omnissa Strengthens Security and Compliance in Accessing Horizon VDI with My OPSWAT Central Management
0 results. Please try again.
FAQs
SDP grants per-application, least-privilege access only after identity and compliance checks pass. Unlike traditional VPNs, which provide broad network access once connected, SDP isolates users to only the resources they need, dramatically reducing the attack surface and lateral movement risk.
A VPN grants connectivity once a user logs in; standard ZTNA adds a basic posture check. OPSWAT verifies deep device compliance before access and continuously after, so a valid login on a compromised device will still be blocked.
My OPSWAT Central Management detects the shift in real time. Depending on policy configuration, it will either immediately isolate the session or guide the user through automated, self-service remediation steps. Once the device meets policy requirements, access is restored automatically, reducing helpdesk load and keeping users productive.
No. You have two options: replace your legacy VPN with our next-generation SDP access or keep your current solution with an extra layer onto the IdP and MFA you already run.
Yes, through agent and agentless methods. On-prem network access control (MetaDefender NAC) is agentless, discovering and profiling devices on the wire; deeper endpoint and remote checks use a lightweight, easily removed agent for managed and BYOD devices, with a fast compliance check before access.
