


Azure DevOps
Category:Source Code
Learn More about Benny Czarny's Book Cybersecurity Upside Down
Identify software packages and known vulnerabilities, assess cryptographic risk, and review AI model provenance and declared licenses.
CycloneDX & SPDX For SBOM
Third-Party Open-Source
Software Components
CI/CD Pipeline
Integration
Software & AI License Information
Known Vulnerability & Cryptographic Risk Visibility
Incomplete inventories leave teams reconstructing evidence for vulnerability response, cryptographic migration, and AI model reviews.
Supplier software and AI model files can arrive without usable inventories, leaving teams to establish package versions, cryptographic dependencies, model provenance, and declared licenses before review.
The EU CRA sets SBOM obligations, EO 14412 directs CBOM guidance, and the EU AI Act requires documentation for covered general-purpose AI models. Separate inventories make supporting evidence harder to assemble.
When a new CVE is disclosed, missing package names and versions delay the initial task: identifying which software artifacts need investigation.
Supplier software and AI model files can arrive without usable inventories, leaving teams to establish package versions, cryptographic dependencies, model provenance, and declared licenses before review.
The EU CRA sets SBOM obligations, EO 14412 directs CBOM guidance, and the EU AI Act requires documentation for covered general-purpose AI models. Separate inventories make supporting evidence harder to assemble.
When a new CVE is disclosed, missing package names and versions delay the initial task: identifying which software artifacts need investigation.
List package names, versions, license information, critical software updates and known vulnerabilities from 8.7 million third-party libraries.
Inspect algorithms, libraries, certificates, protocols, and related cryptographic material. Review classical and quantum risks, with recommended replacements where available, to inform migration decisions.
Match model files to repositories known to publish the same bytes and report available declared licenses, giving reviewers concrete references for provenance and licensing checks.
Analyze supported files inside isolated networks. With the required databases installed locally, teams can perform BOM reviews without cloud connectivity during scanning.
Generate software, cryptographic, and AI inventories through one engine, reducing the need to configure separate scanning workflows for each inventory type.
Set software vulnerability thresholds and package license restrictions. Separately enable blocking for cryptographic risk and selected AI model licenses, according to your workflow requirements.
Inspect the scan summary, switch between SBOM, CBOM, and AIBOM findings, and export the report you need.
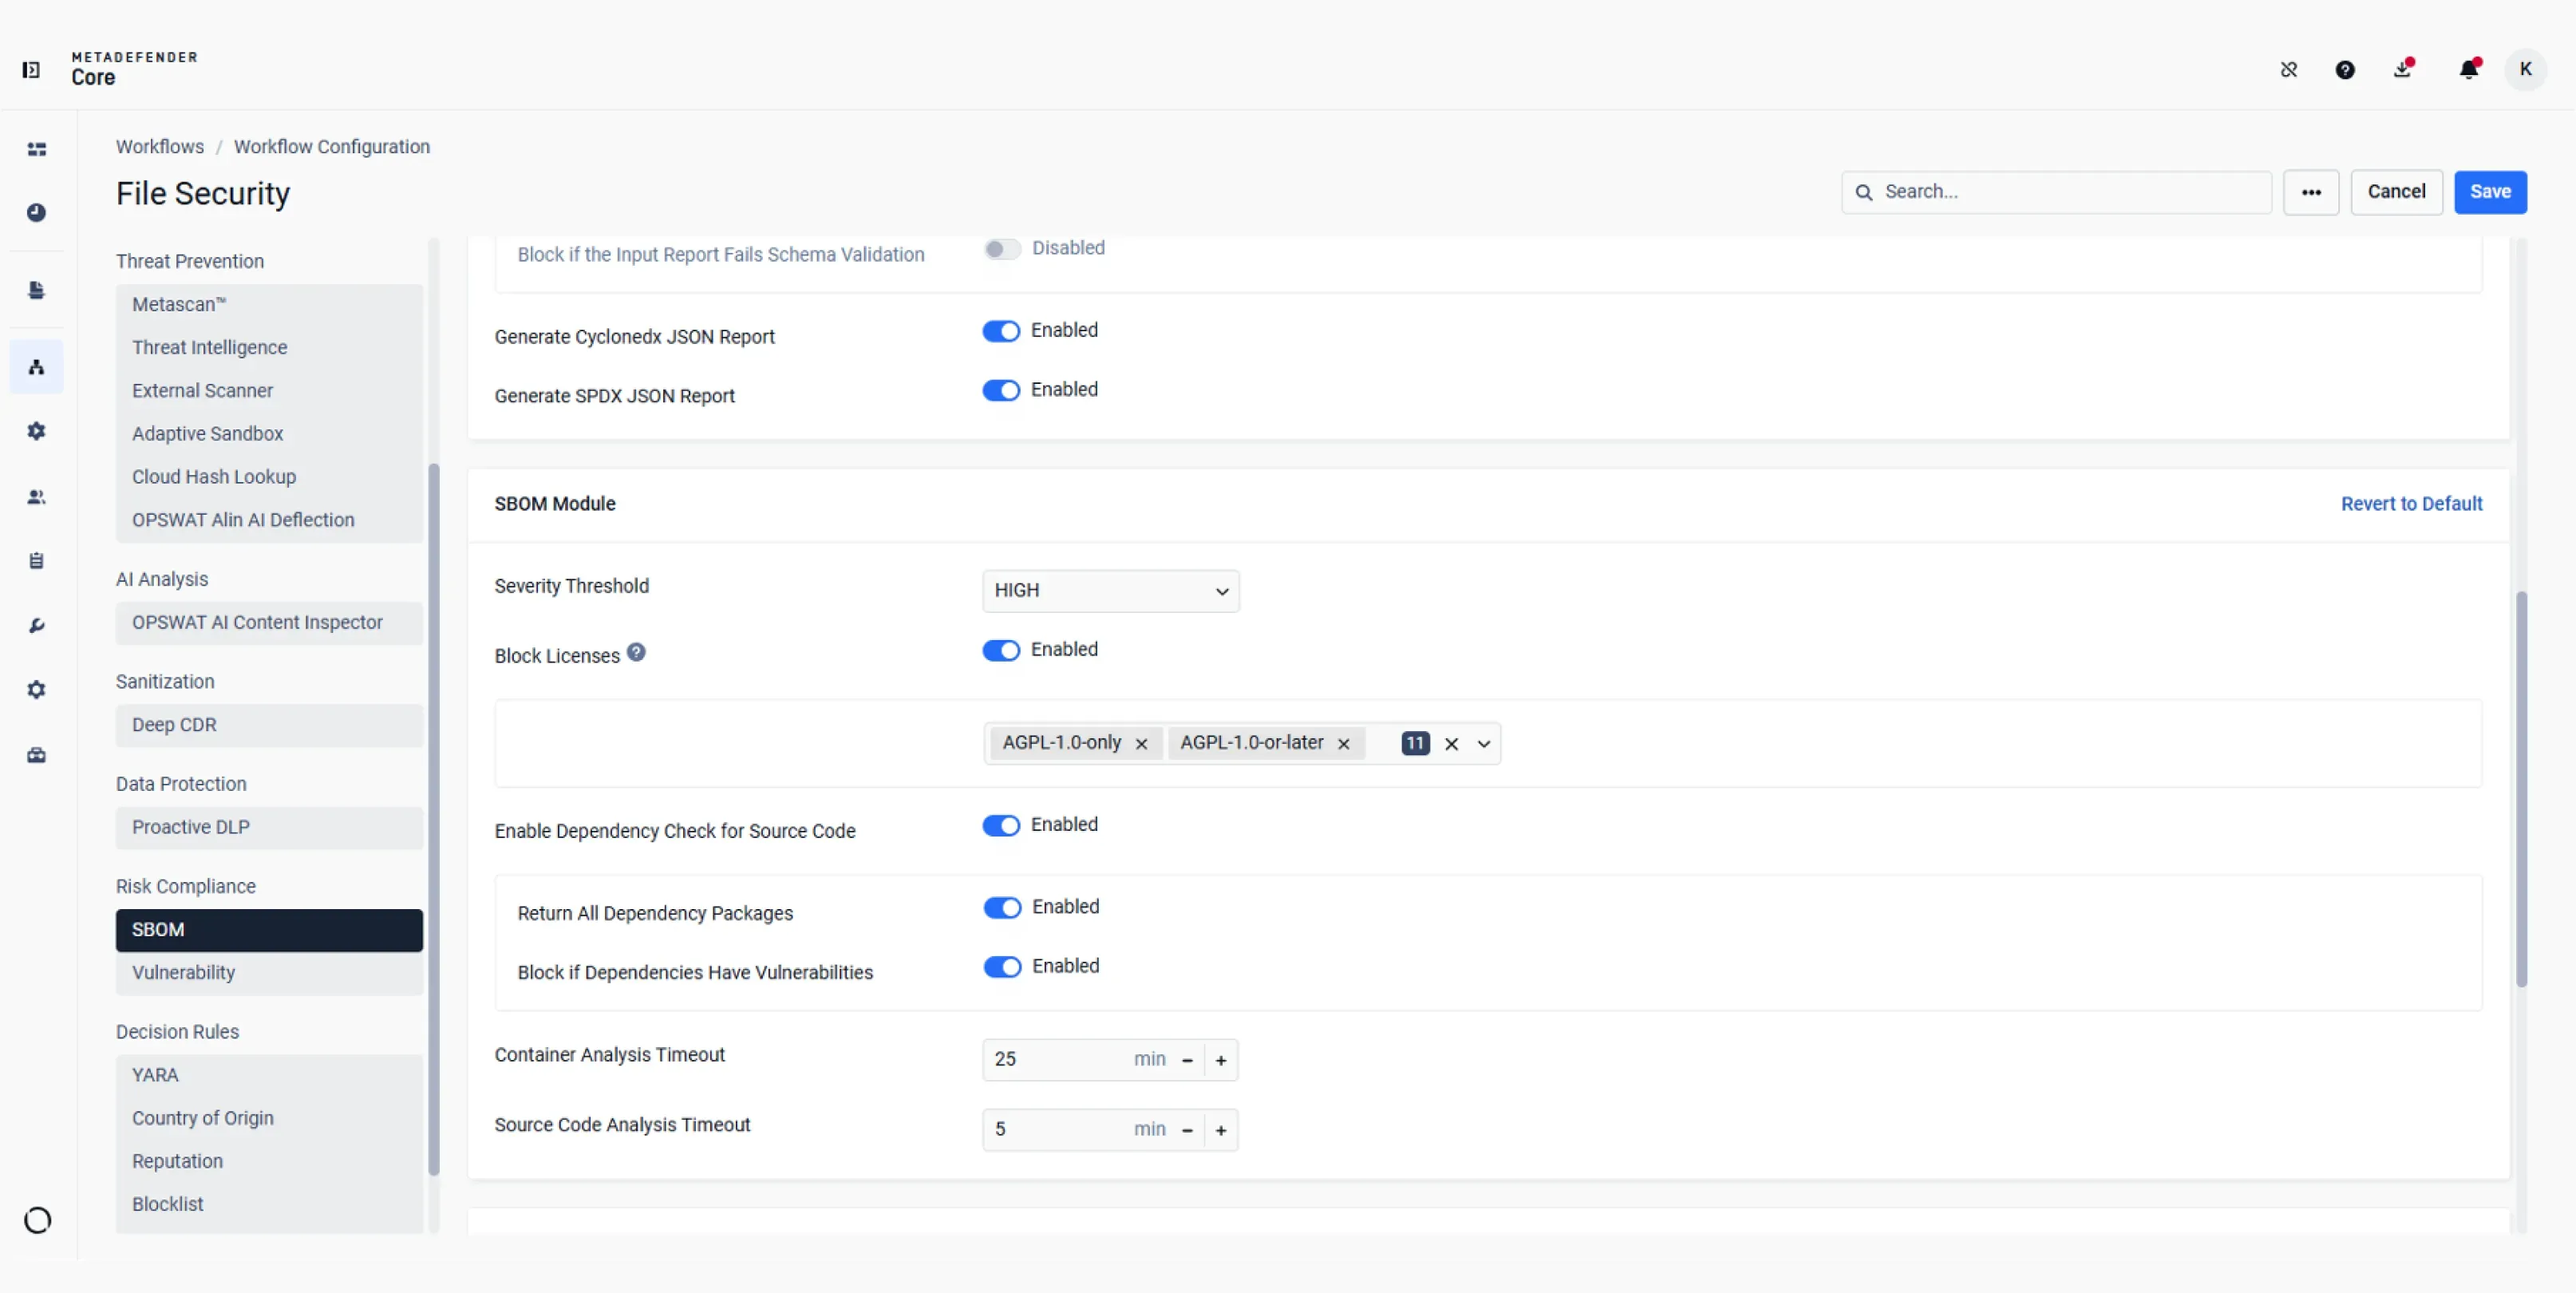
Set vulnerability severity thresholds, select package licenses to block, and enable dependency checks for source code.
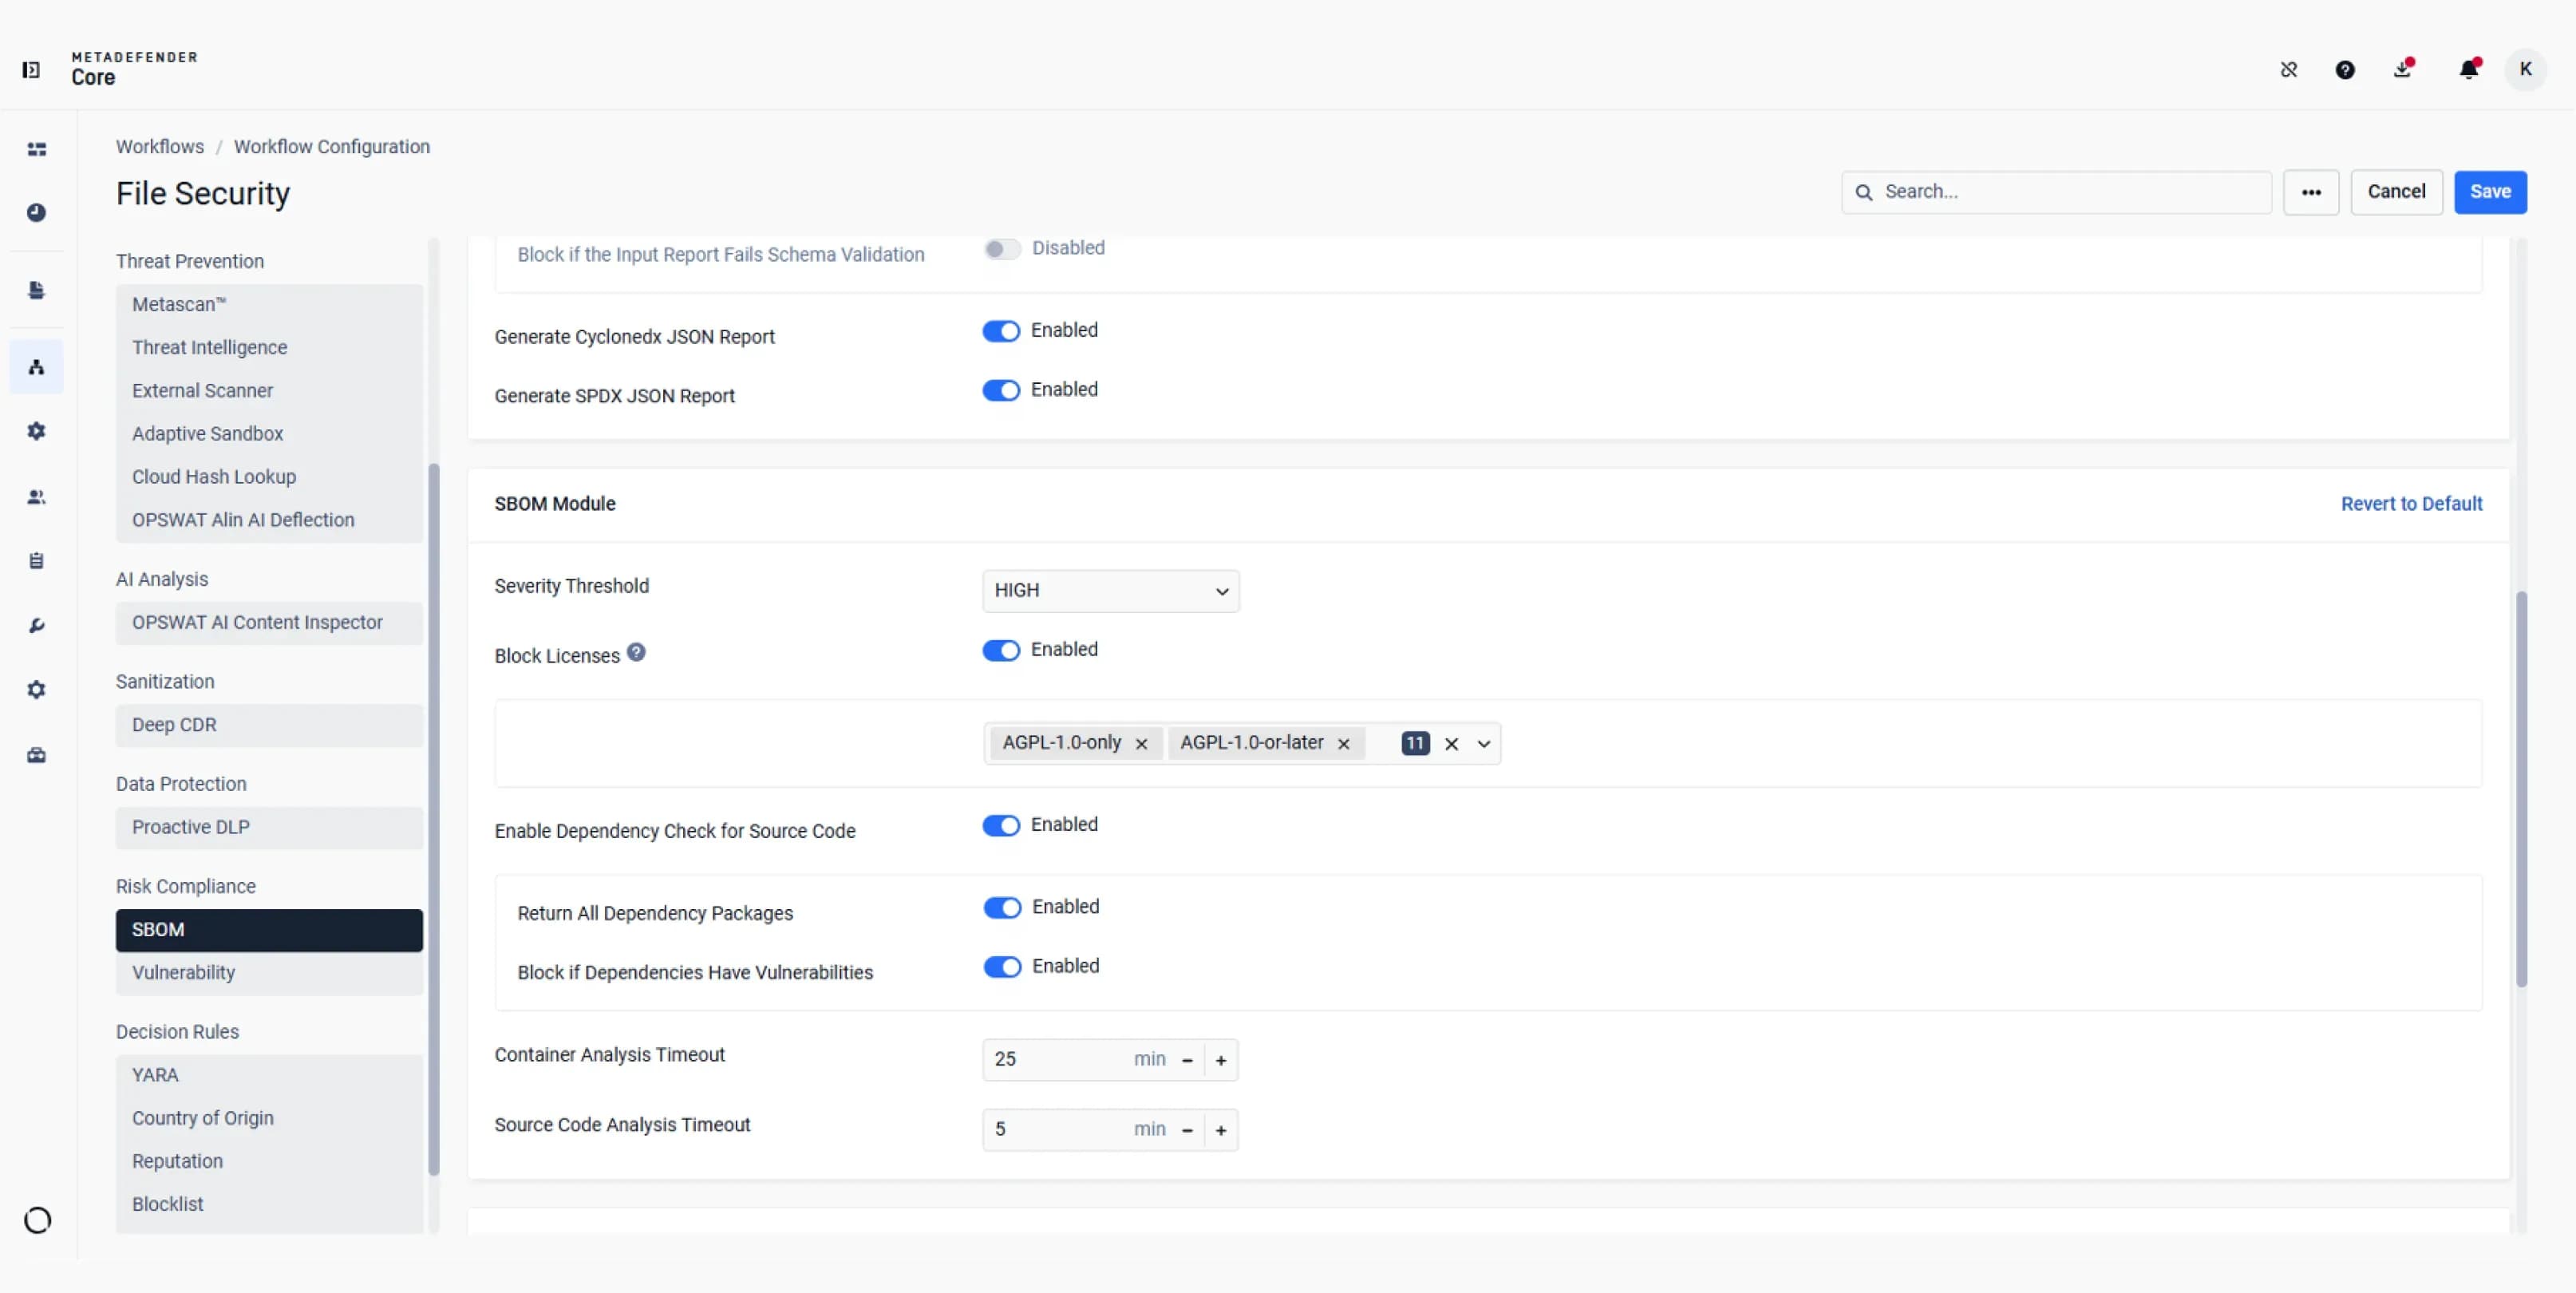
Set vulnerability severity thresholds, select package licenses to block, and enable dependency checks for source code.
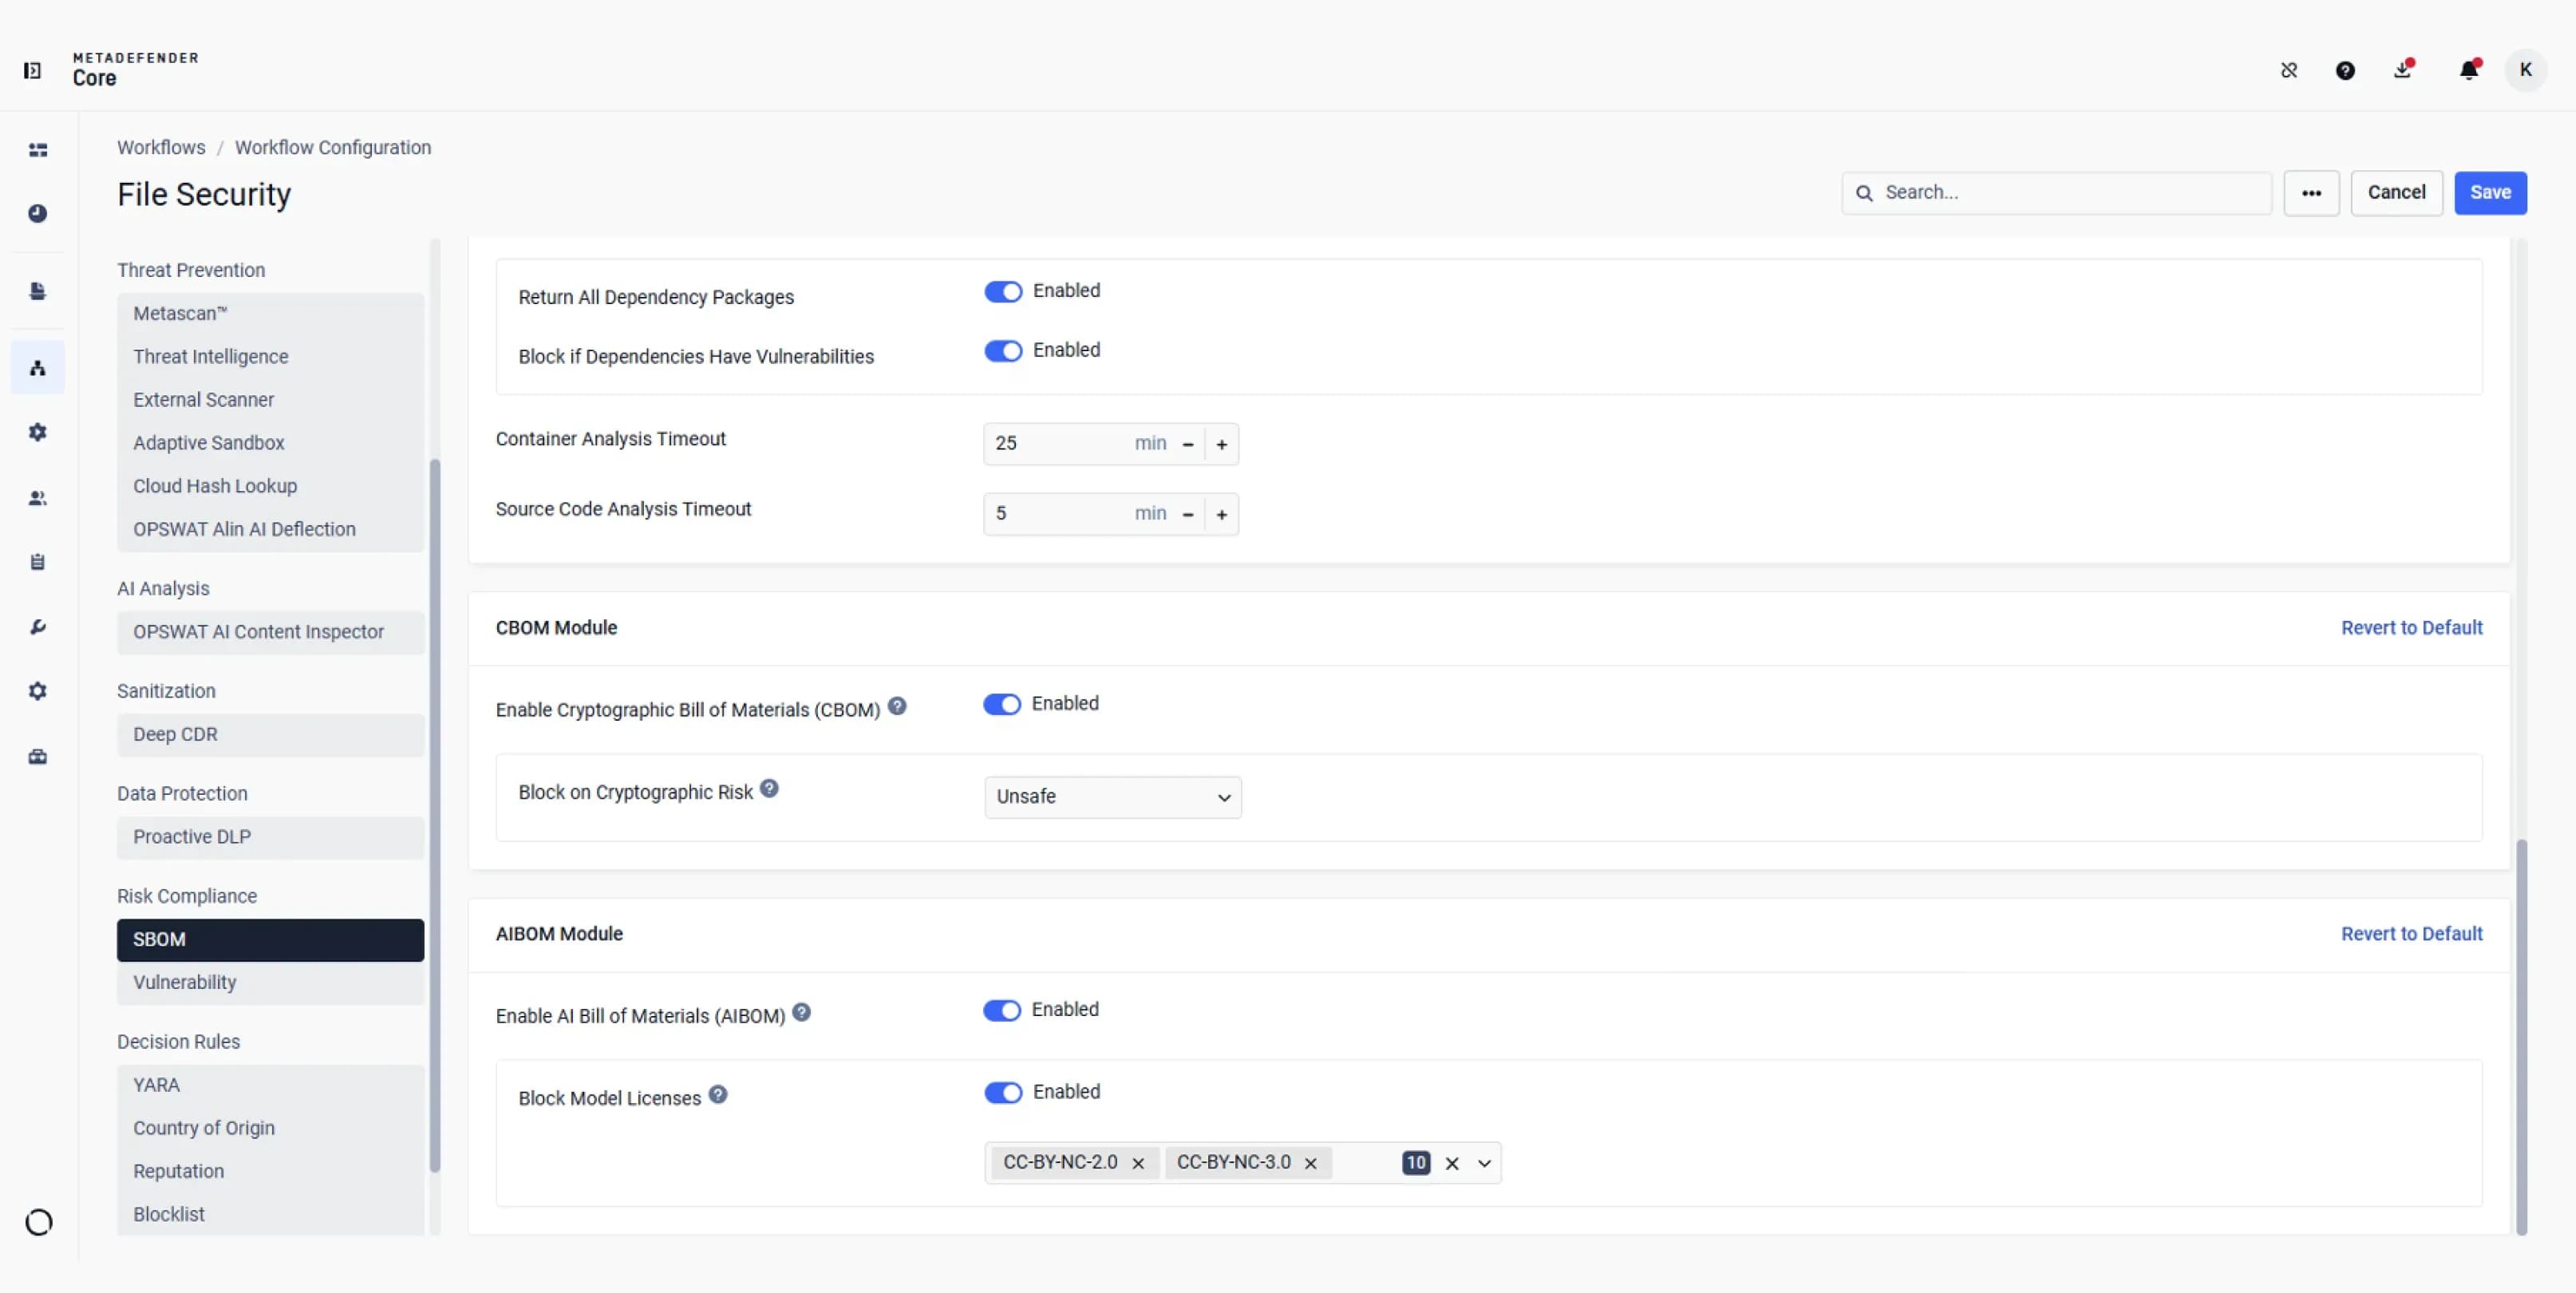
Choose whether to block on cryptographic risk or which AI model licenses to restrict.
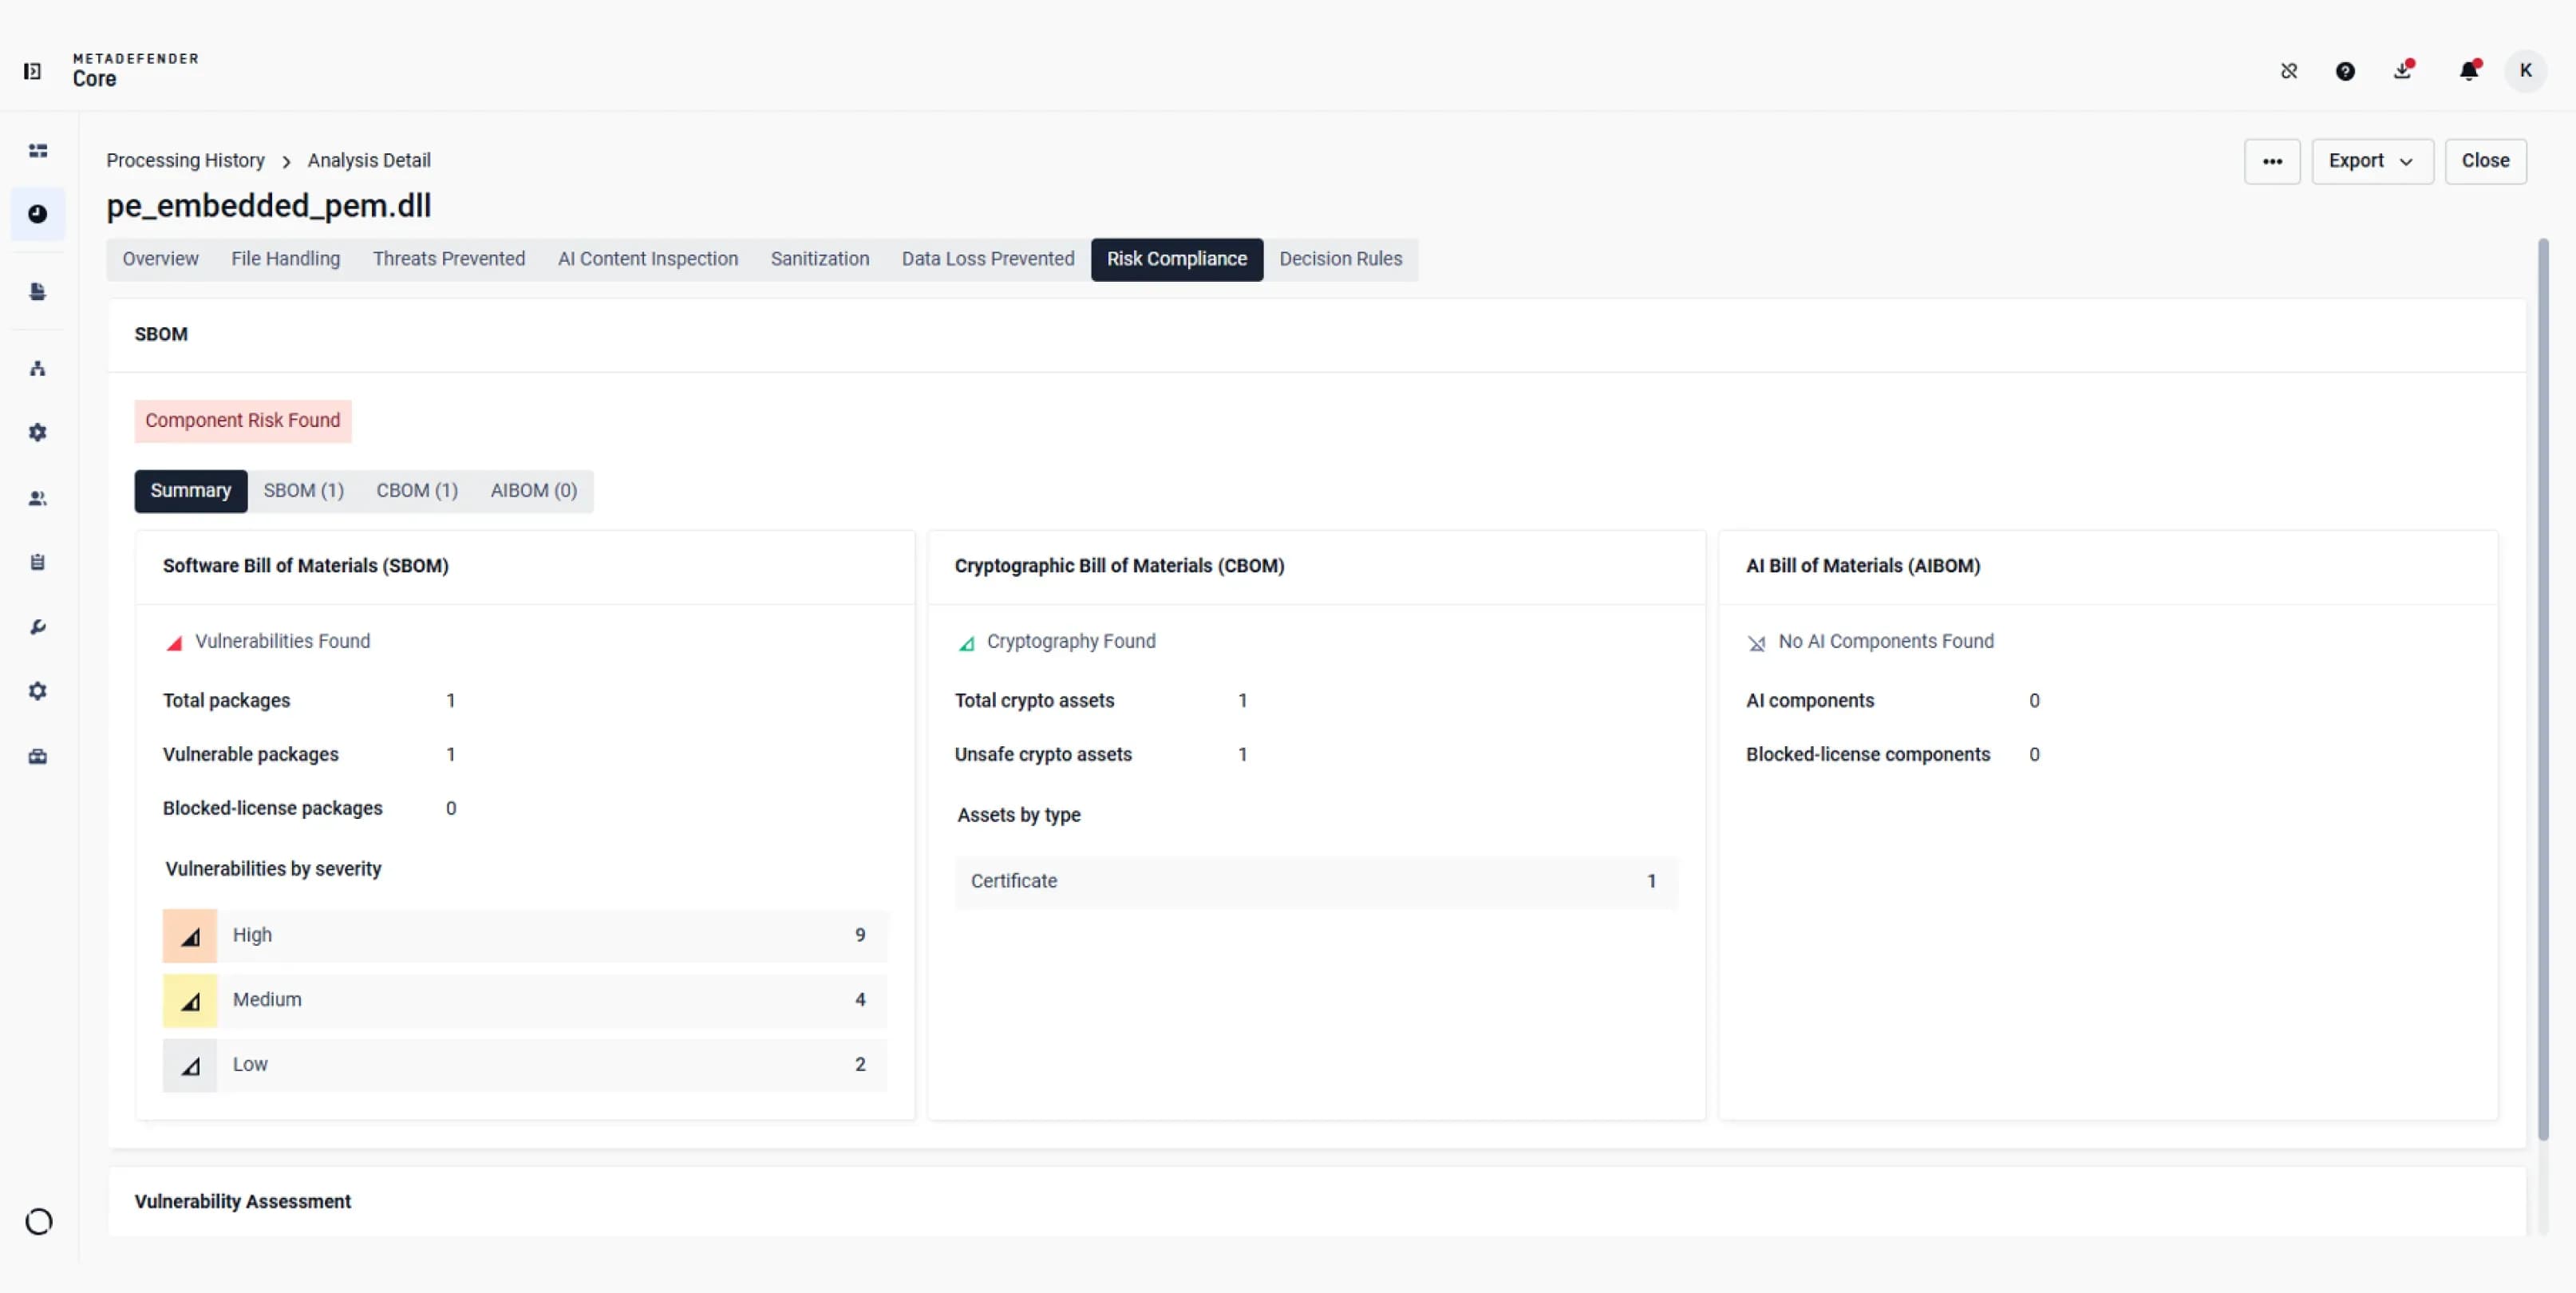
Compare software, cryptographic, or AI findings for the scanned file, then open each module for details.
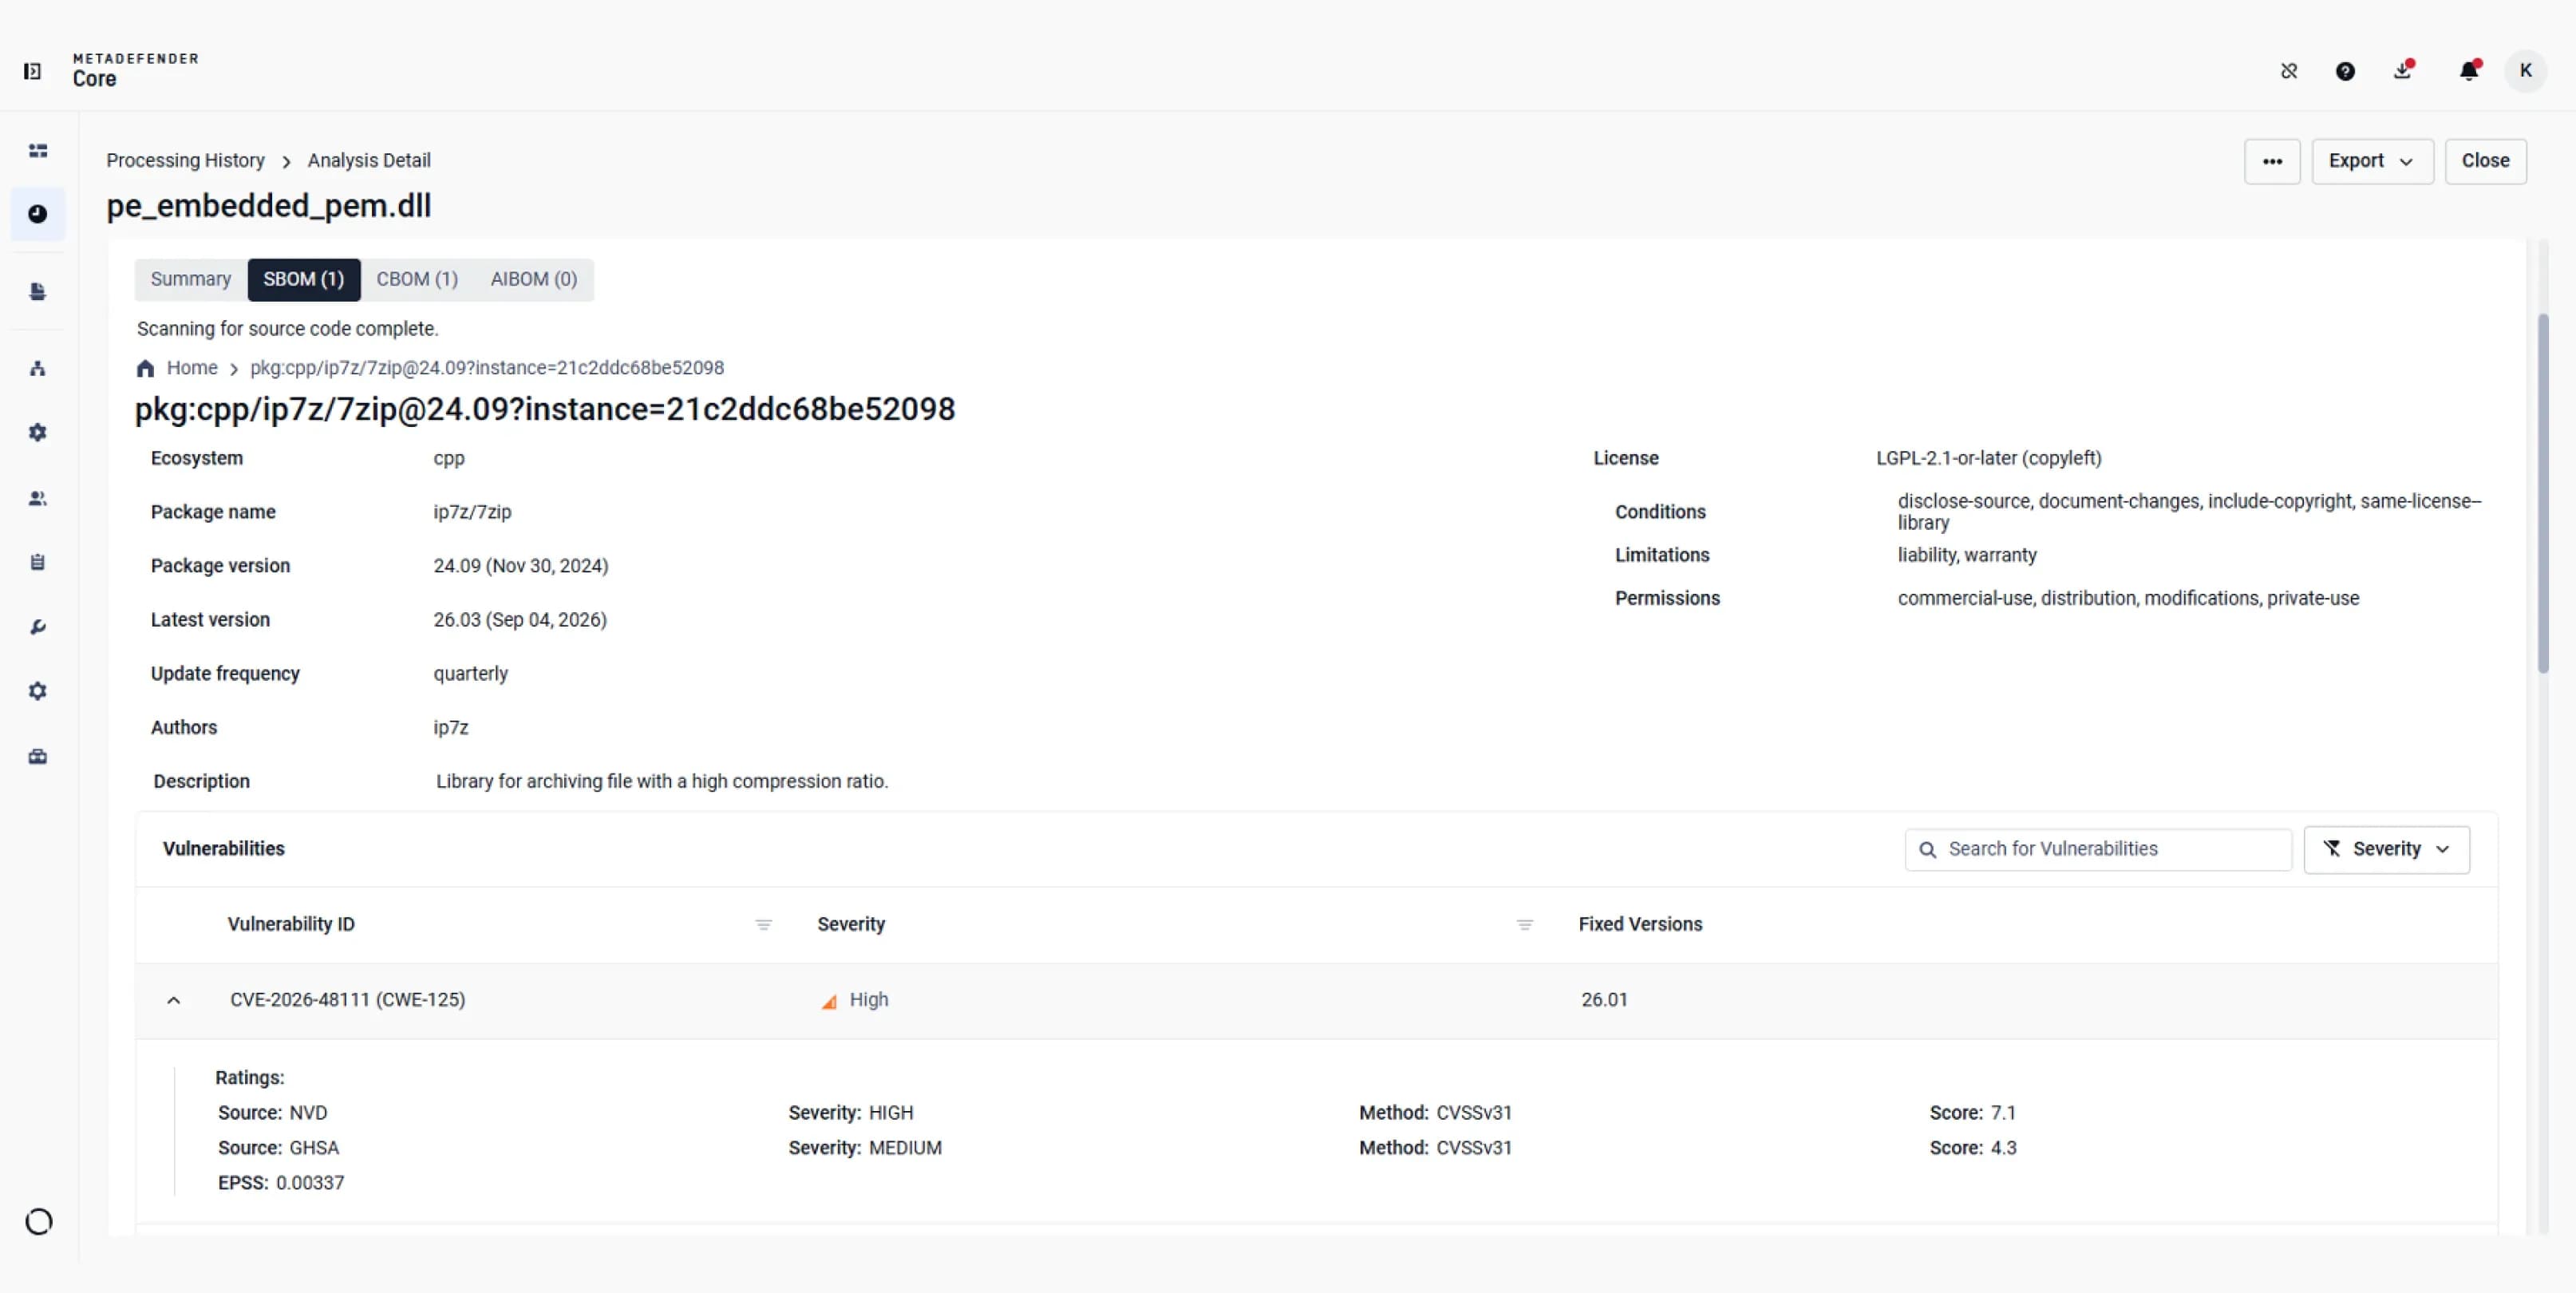
Review package version, reported license, associated CVEs, and severity ratings.
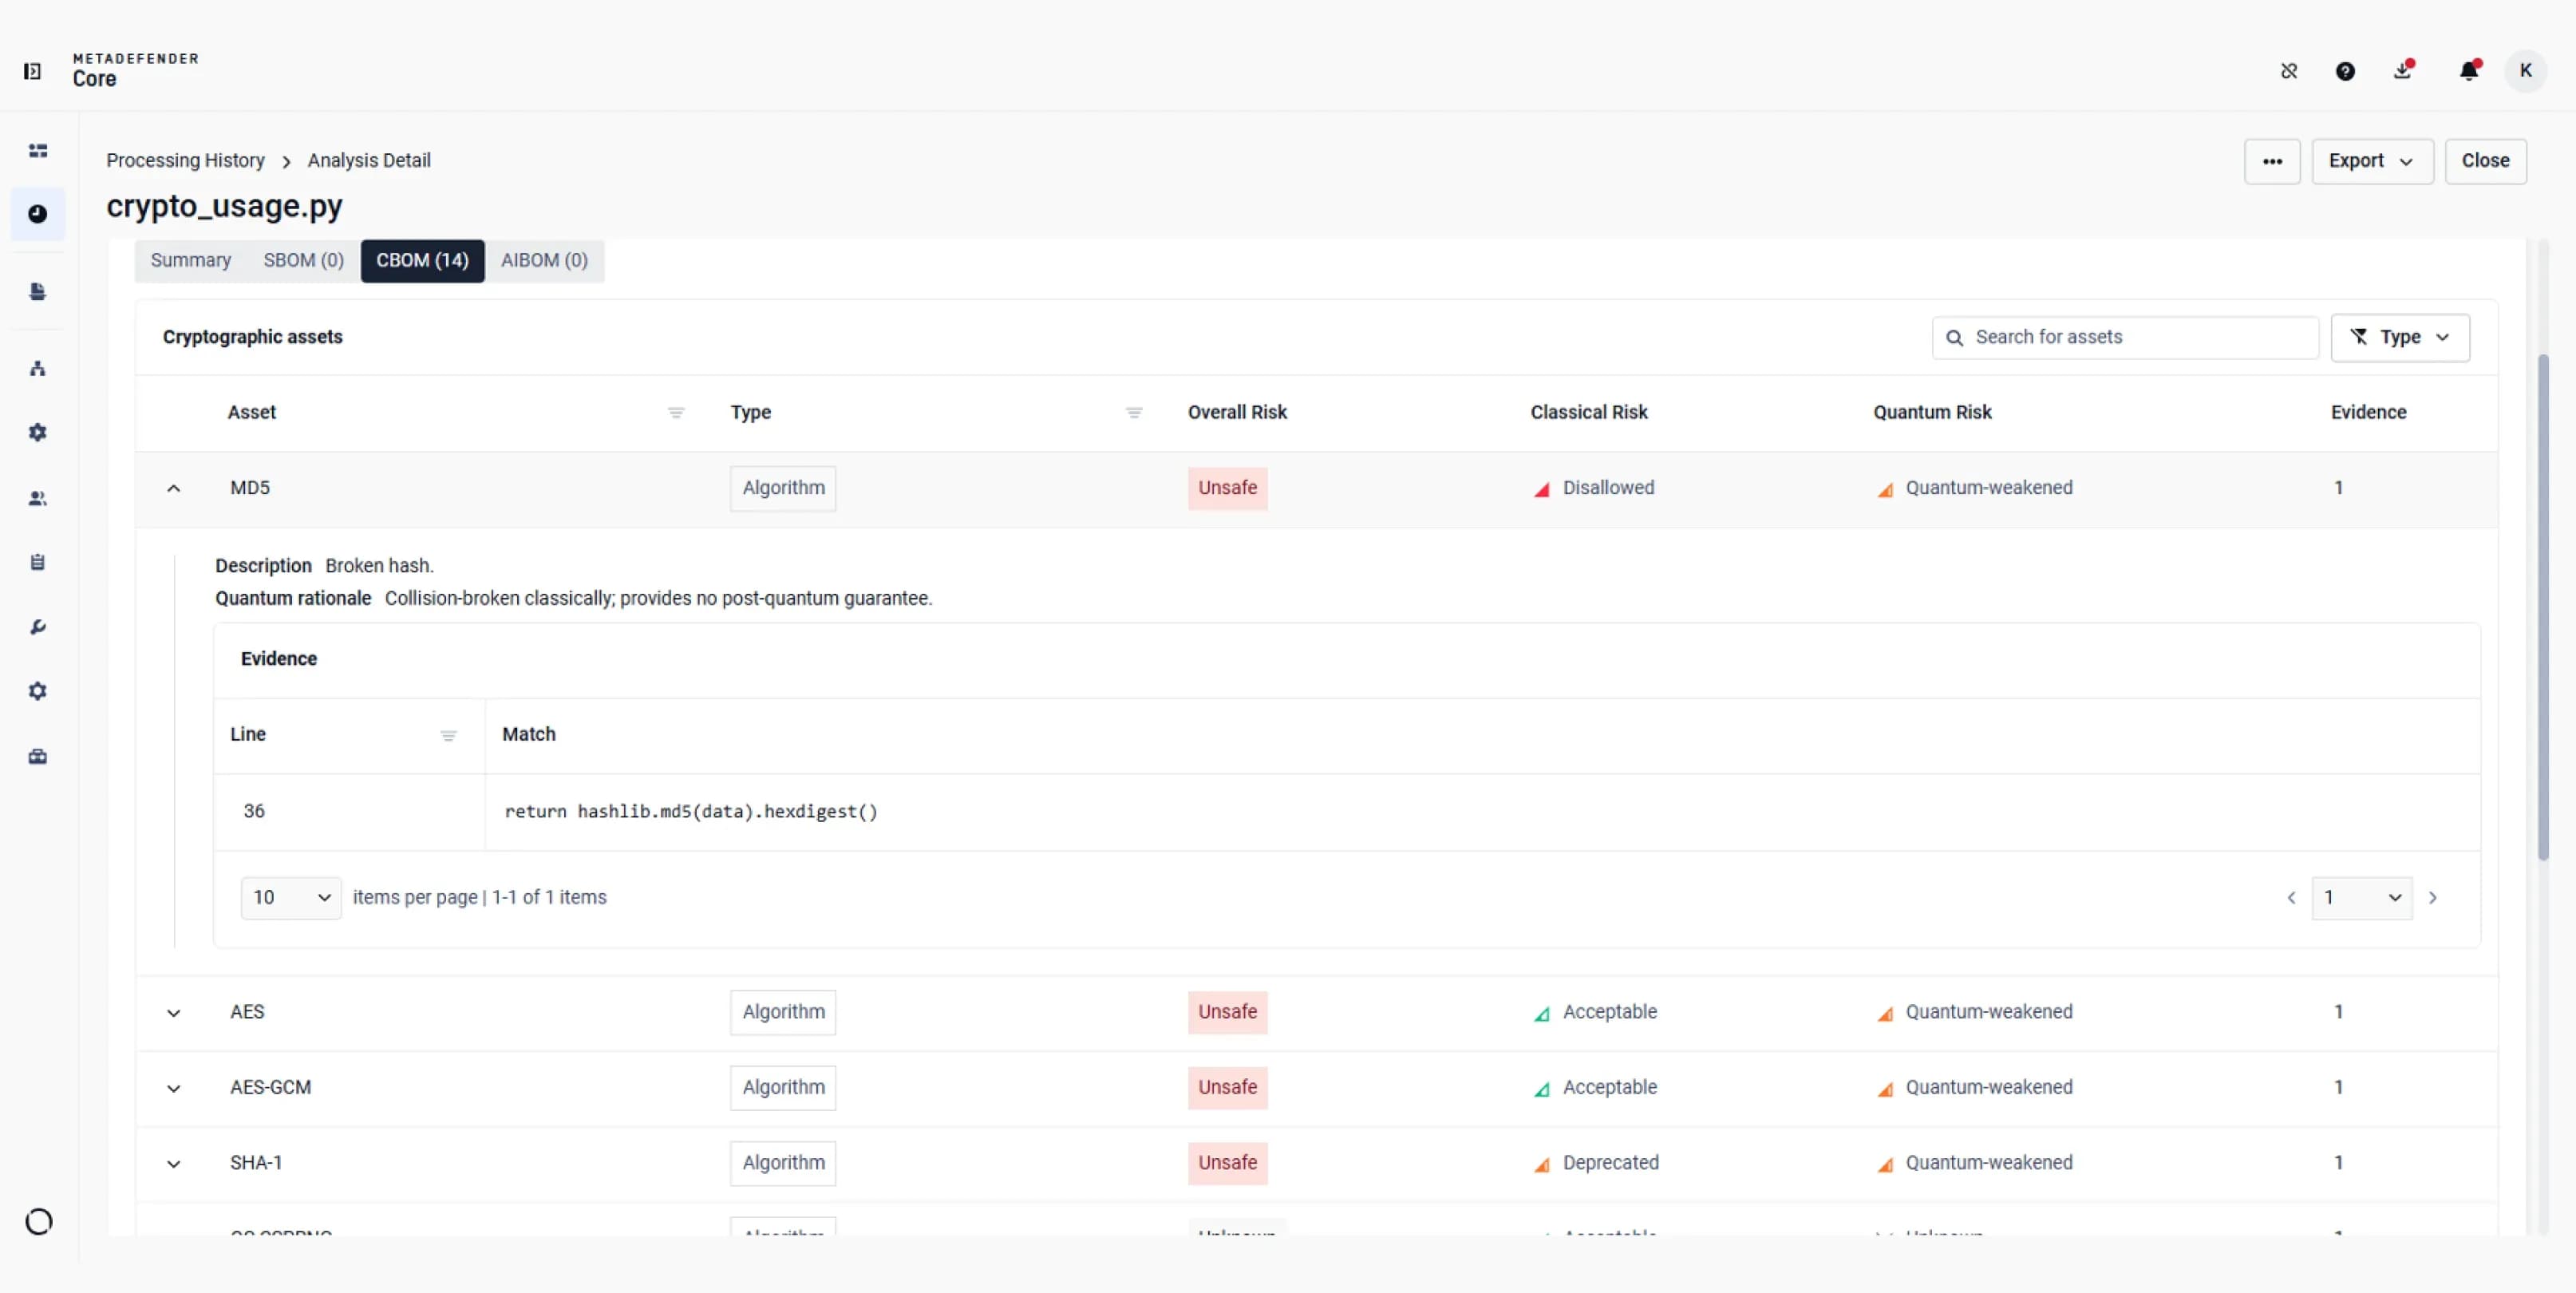
Review classical and quantum risk classifications alongside source evidence showing where cryptographic assets were found.
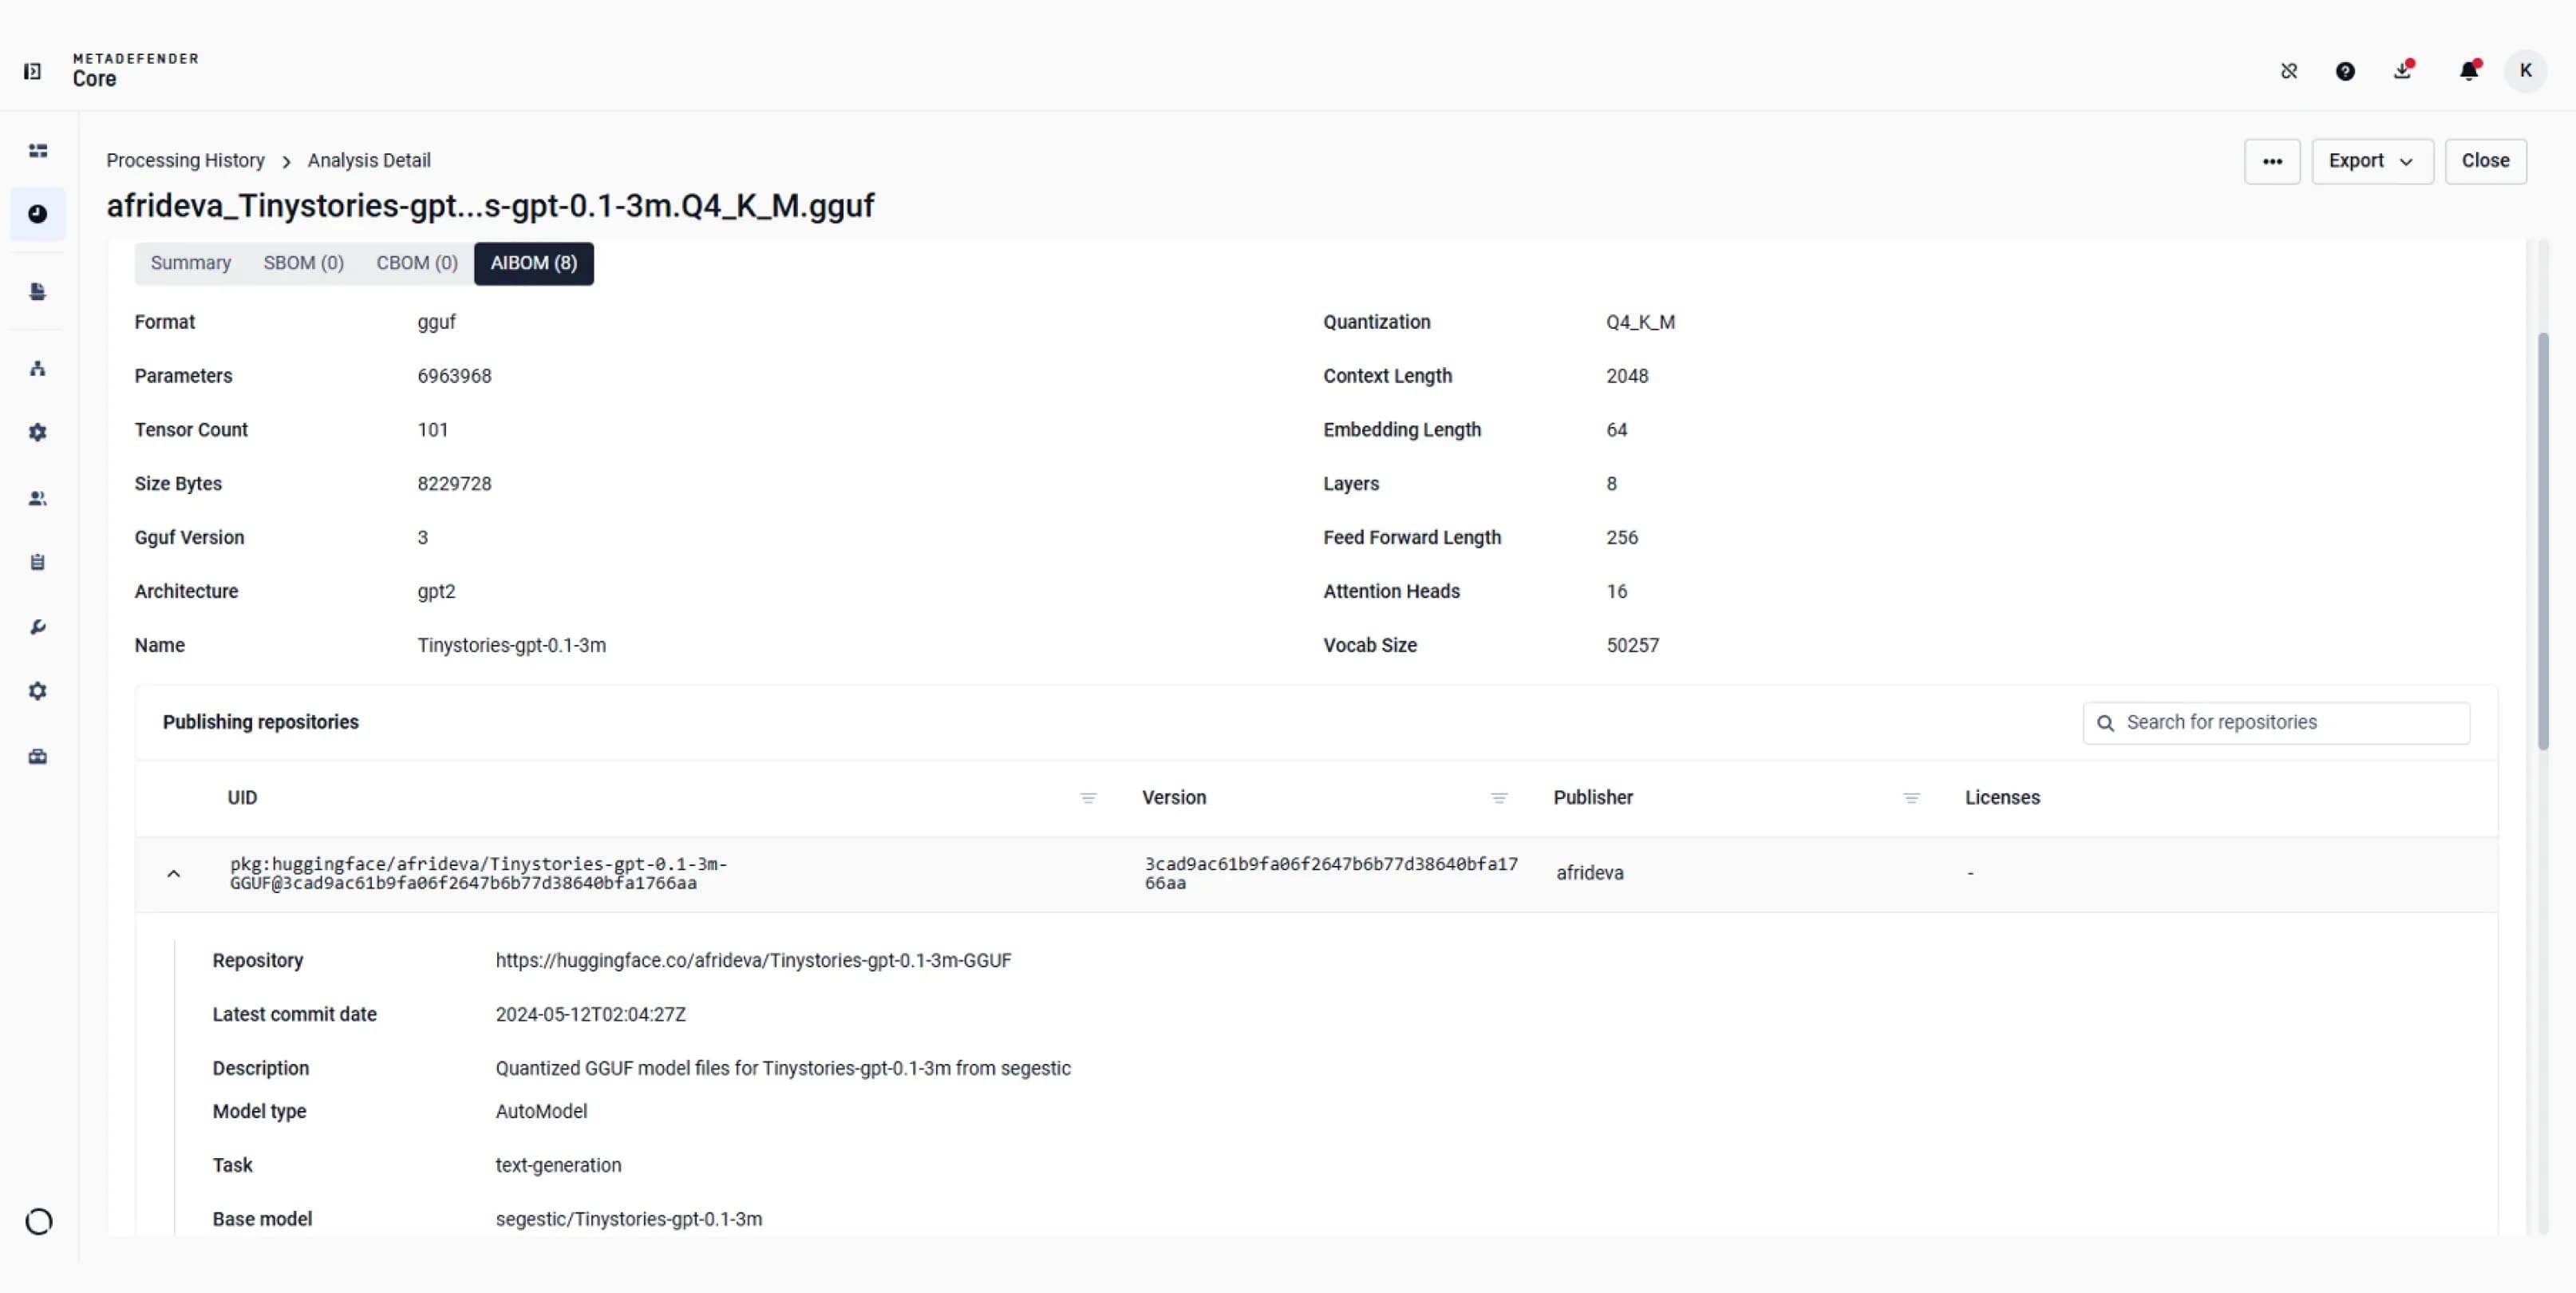
Inspect the model format and architecture, then review repositories known to publish the same file.
Azure DevOps
Bitbucket
GitHub
GitLab
AmazonECR
Azure ACR
DockerHub
JFrog Container
Quay
JFrog Binary
Ruby
Python
PHP
Node.js
Java
Go
Rust
Dart
.NET
C/C++
Check scanned artifacts for the affected package and version to scope the team's remediation work.
Use cryptographic findings and recommended replacements to identify assets needing specialist review before migration planning.
Review known publishing repositories and available declared licenses before approving a model for application use.
Scan source files, binaries, certificates, container content, and AI model files. Analysis coverage depends on the file type and enabled BOM modules.
Enabled modules generate up to three inventories within one scan result, depending on the submitted file and supported analysis.
Generate separate SBOMs in SPDX or CycloneDX, or together with CBOM and AIBOM in JSON or PDF, giving AppSec, PQC, AI governance, Legal, and GRC teams the formats relevant to their work.