Advanced Threat Detection And
Prevention For Trusted File Workflows
MetaDefender Core is OPSWAT’s advanced threat detection and prevention platform for identifying file-borne threats before execution. It combines Deep CDR™ Technology, Metascan™ Multiscanning, adaptive sandboxing, Proactive DLP, and AI-powered malware detection to secure file workflows across critical infrastructure while supporting compliance and zero trust at the file level.
- Turn Every File into a Trusted Asset
- Neutralize Threats Before They Proliferate
- Secure Anywhere, Scale Everywhere
OPSWAT is Trusted by
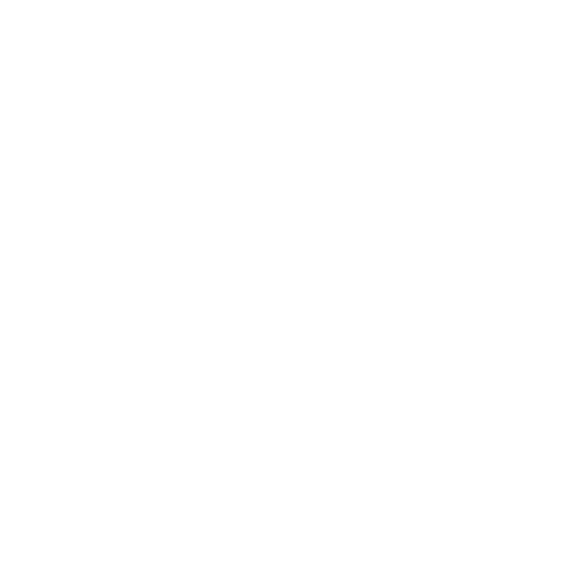
A Platform for Complete File Trust
MetaDefender Core delivers advanced threat detection and prevention for regulated environments. Using Predictive Alin AI, Deep CDR™ Technology, Metascan™ Multiscanning, AI Content Inspector, Proactive DLP™, Adaptive Sandbox, Threat Intelligence, File-based Vulnerability Assessment and SBOM, it stops zero-day attacks, aids compliance, and secures every file across security workflows without slowing your business.
Detect, Analyze, and Eliminate Malware and Zero-Day Attacks
Advanced Threat Prevention
Combining industry-leading technologies like Metascan Multiscanning and Deep CDR™ Technology, MetaDefender Core detects and neutralizes embedded malware and zero-day threats.
Multi-Layered Security Architecture
A modular, policy-driven design that orchestrates scanning, sanitization, vulnerability assessment, and threat intelligence for consistent, high-volume protection across environments.
AI-Powered Threat Defense
Leveraging AI and machine learning to optimize every threat detection and prevention engine for faster, smarter, and more adaptive protection.
Centralized Policy Enforcement
Administrators can define and automate file handling policies to ensure consistent security standards across the entire organization, simplifying compliance and governance
Seamless Integration and Scalability
Integrates easily with existing IT and OT systems through APIs, ICAP, and SDKs, adapting to complex infrastructures without disrupting operations.
Proven Protection for Regulated Environments
Trusted by governments, critical infrastructure operators, and over 2,100 global organizations, MetaDefender Core provides full control over data security while helping organizations meet regulatory requirements.
Stopping Threats Starts with Market-Leading Technology
OPSWAT’s proven, globally trusted, award-winning, and market-leading technology prevents file-borne malware from entering and propagating into your critical environments.
AI-Powered Zero-Day Prediction at the Perimeter
- Pre-Execution Detection & Deflection
- ML-Model trained on Enterprise File Workflows
More Engines Are Better Than One
- Detect nearly 100% of malware
- Scan simultaneously with 30+ leading AV engines
Stop Threats That Others Miss
- Supports 200+ file formats
- Recursively sanitize multi-level nested archives
- Regenerate safe and usable files
AI-Driven Content Authenticity & Document Fraud Detection
- Deduplicate, validate, and canonicalize image metadata
- Evaluate visual forensic signals, text-stylometry features, and document structure cues
- Use separate gates for AI-generated text, AI-generated images, and document-fraud classifiers
Prevent Sensitive Data Loss
- Utilize AI-powered models to locate and classify unstructured text into predefined categories
- Automatically redact identified sensitive information like PII, PHI, PCI in 125+ file types
- Support for Optical Character Recognition (OCR) in images
Detect Evasive Malware with Advanced Emulation-Based Sandboxing
- Analyze files in a high-speed
- Anti-evasion sandbox engine extracts IOCs
- Identify zero-day threats
- Enable deep malware classification via API or local integration
Block Malformed Files Before Inspection Begins
- Validate 160+ file types, including AI model formats
- Block invalid structure and suspicious content
- Extract and send risk objects to other engines
Enhance Detection with Real-Time Threat Intelligence
- Correlate global IOCs, IPs, URLs, & file reputation across 50B+ artifacts
- Stop emerging threats faster
- Enrich downstream analysis
Secure Your Software Supply Chain
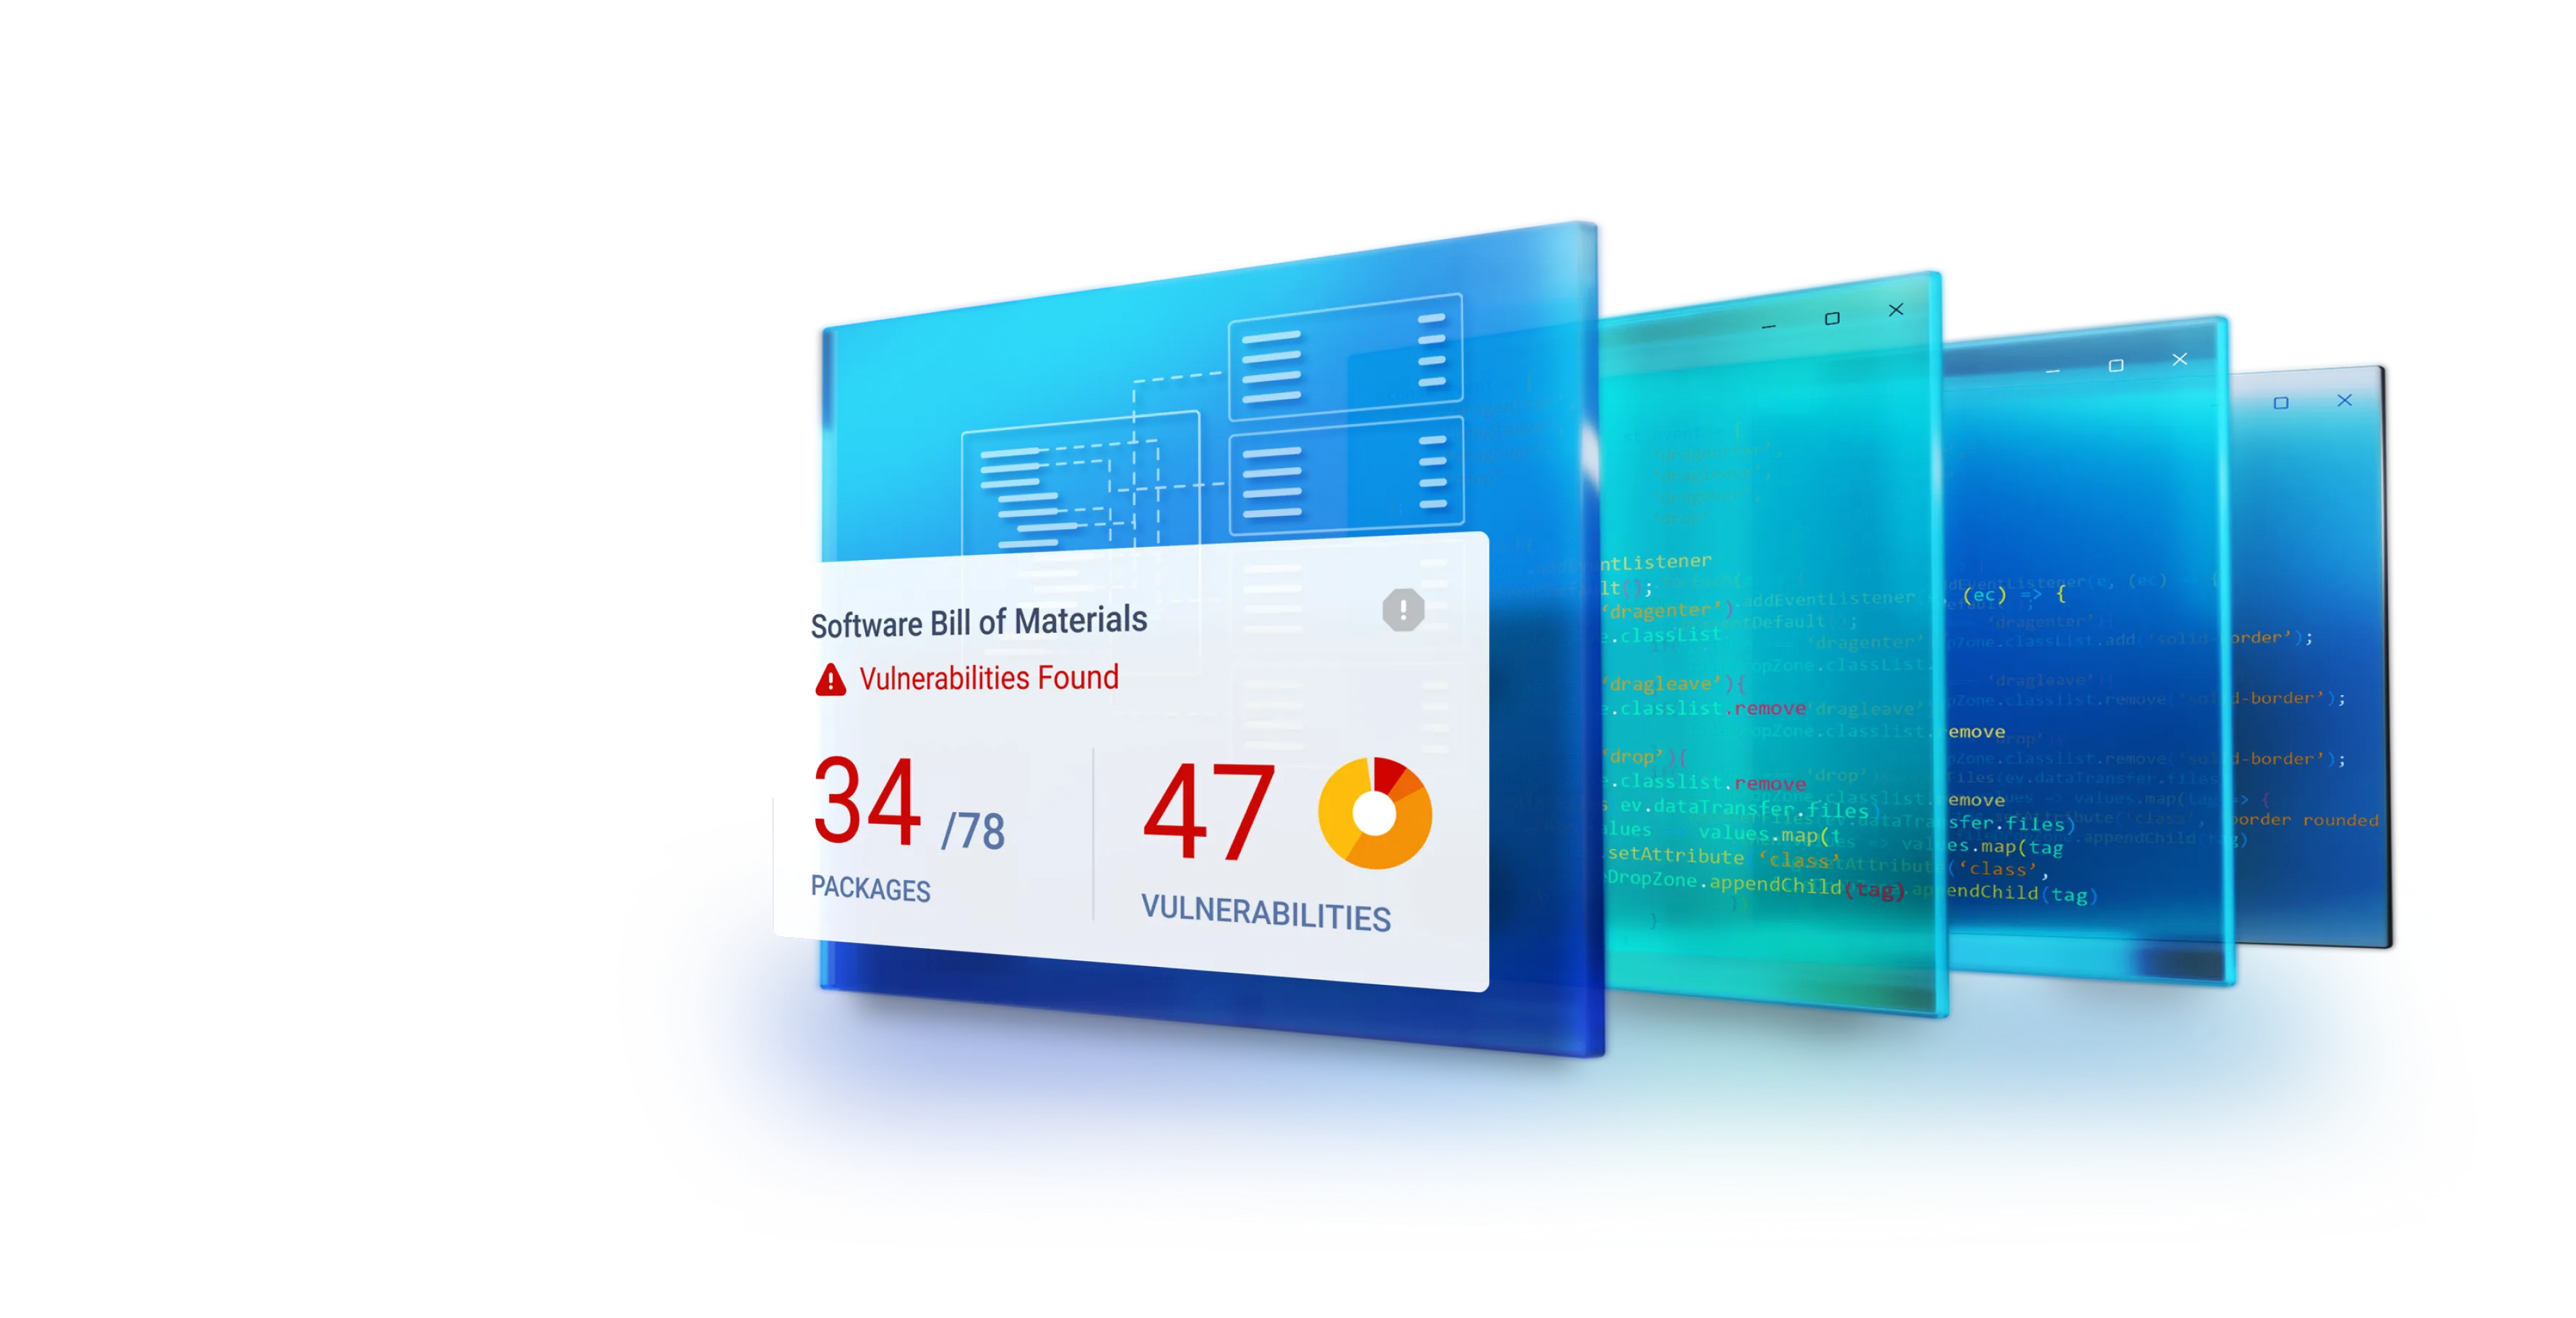
- Manage risks associated with open-source software (OSS), 3rd party components and dependencies
- Ensure codebase transparency, security, and compliance
Detect Application Vulnerabilities Before They Are Installed
- Check software for known vulnerabilities before installation
- Scan systems for known vulnerabilities when devices are at rest
- Quickly examine running applications and their libraries for vulnerabilities
![OPSWAT Technologies Image]() AI Content Inspector
AI-Driven Content Authenticity & Document Fraud Detection
- Deduplicate, validate, and canonicalize image metadata
- Evaluate visual forensic signals, text-stylometry features, and document structure cues
- Use separate gates for AI-generated text, AI-generated images, and document-fraud classifiers
100+ Billion ImagesFrom Google SynthID Detection99% Accuracyfor Major Image Generators![OPSWAT Technologies Image]() File Structure Validation
Block Malformed Files Before Inspection Begins
- Validate 160+ file types, including AI model formats
- Block invalid structure and suspicious content
- Extract and send risk objects to other engines
Selective processingEarly blocking prevents resource consumption downstreamTraceabilityObject-level extraction and reporting![OPSWAT Technologies Image]() Threat Intelligence
Enhance Detection with Real-Time Threat Intelligence
- Correlate global IOCs, IPs, URLs, & file reputation across 50B+ artifacts
- Stop emerging threats faster
- Enrich downstream analysis
FasterSpeed up overall triage timeTransparentDefend critical environments with greater clarity![OPSWAT Technologies Image]() SBOM (Software Bill of Materials)
Secure Your Software Supply Chain
- Manage risks associated with open-source software (OSS), 3rd party components and dependencies
- Ensure codebase transparency, security, and compliance
18,400Vulnerabilities Found In Production Code In 202113.62%Vulnerabilities Are File Based
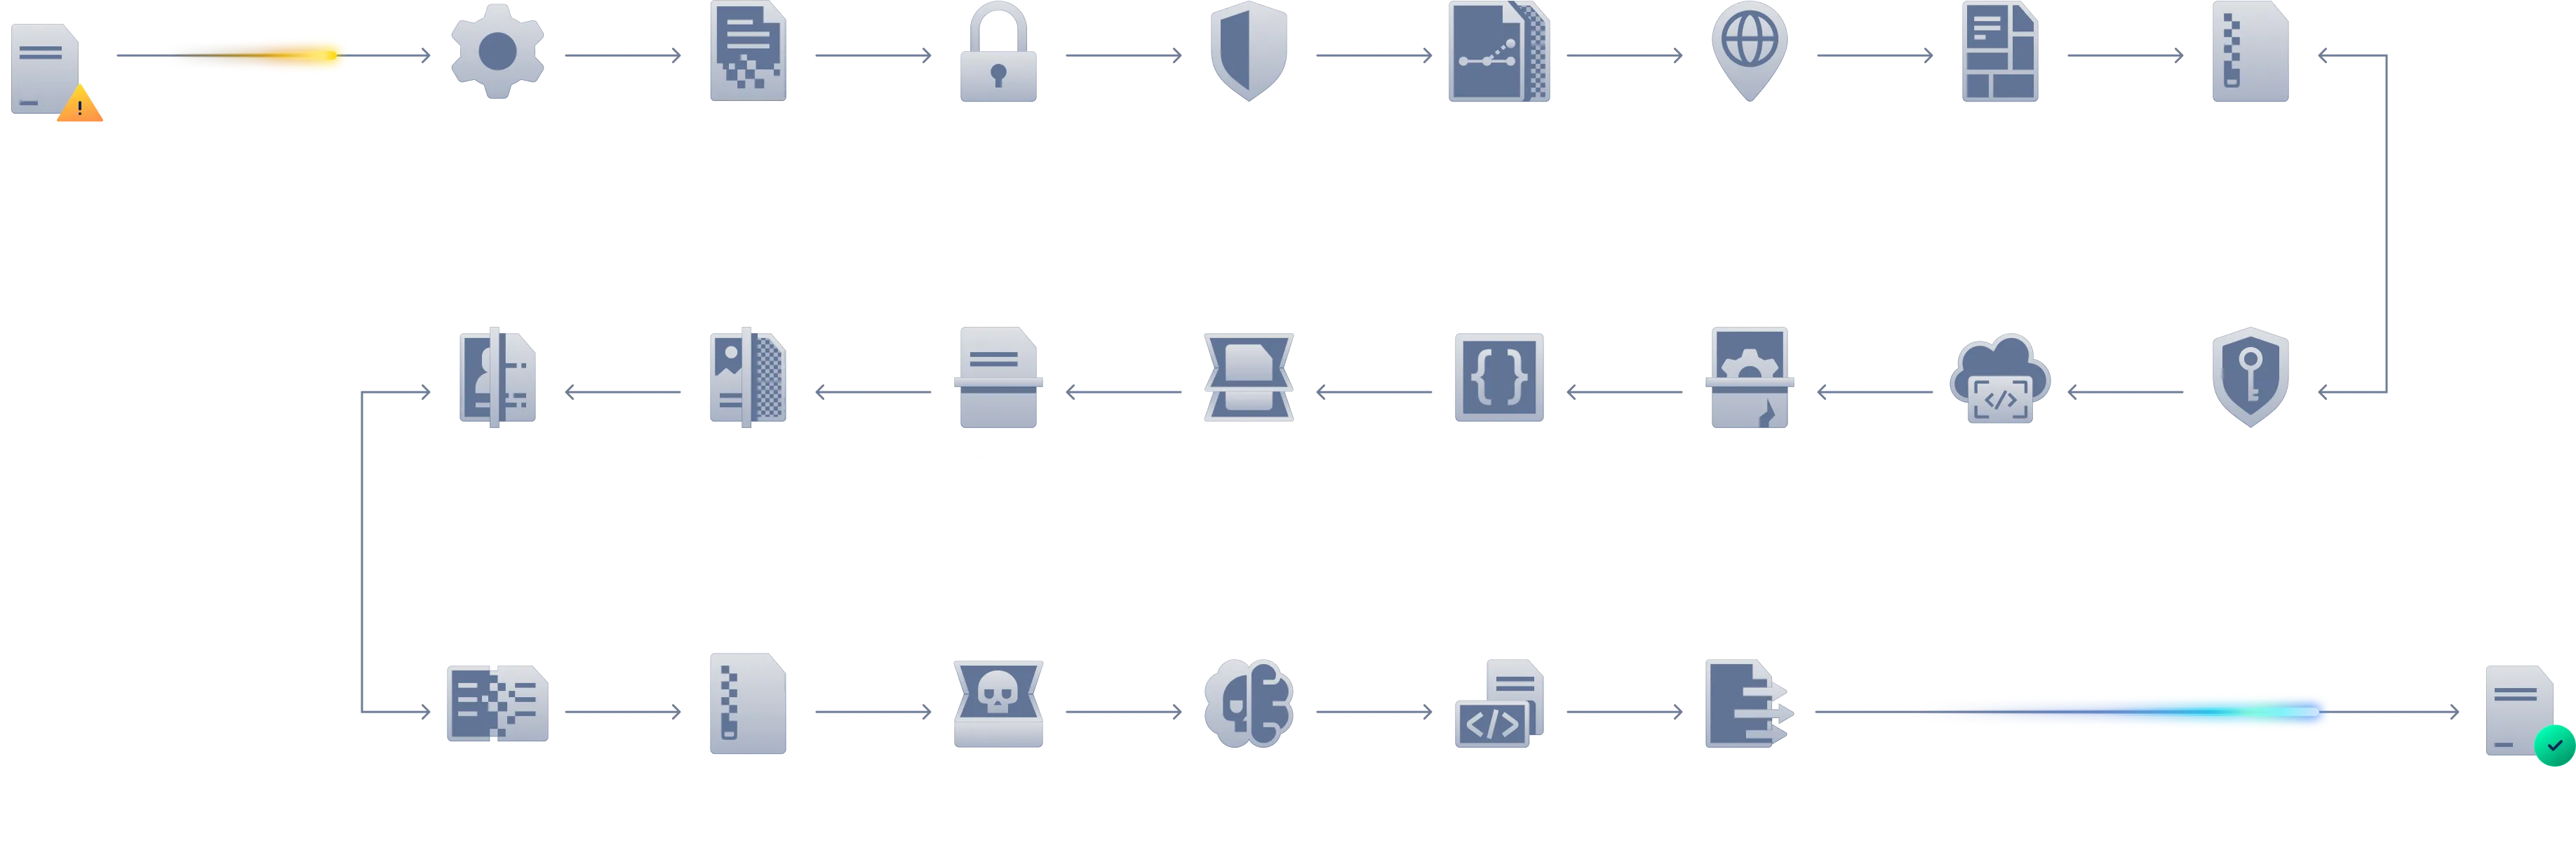
MetaDefender Core File Processing Workflow
Every step is designed to protect your data. Any file entering MetaDefender Core follows a controlled, multi-stage workflow designed to detect, sanitize, and verify content before it’s released into secure networks. This process ensures that even complex, nested files are fully analyzed and compliant with organizational security policies. Each stage is modular, policy-driven, and optimized for performance and accuracy across IT, OT, and air-gapped environments.
MetaDefender Core in Action
See how MetaDefender Core helps teams configure security workflows, apply layered file protection, process suspicious files, and monitor security outcomes across operational environments.
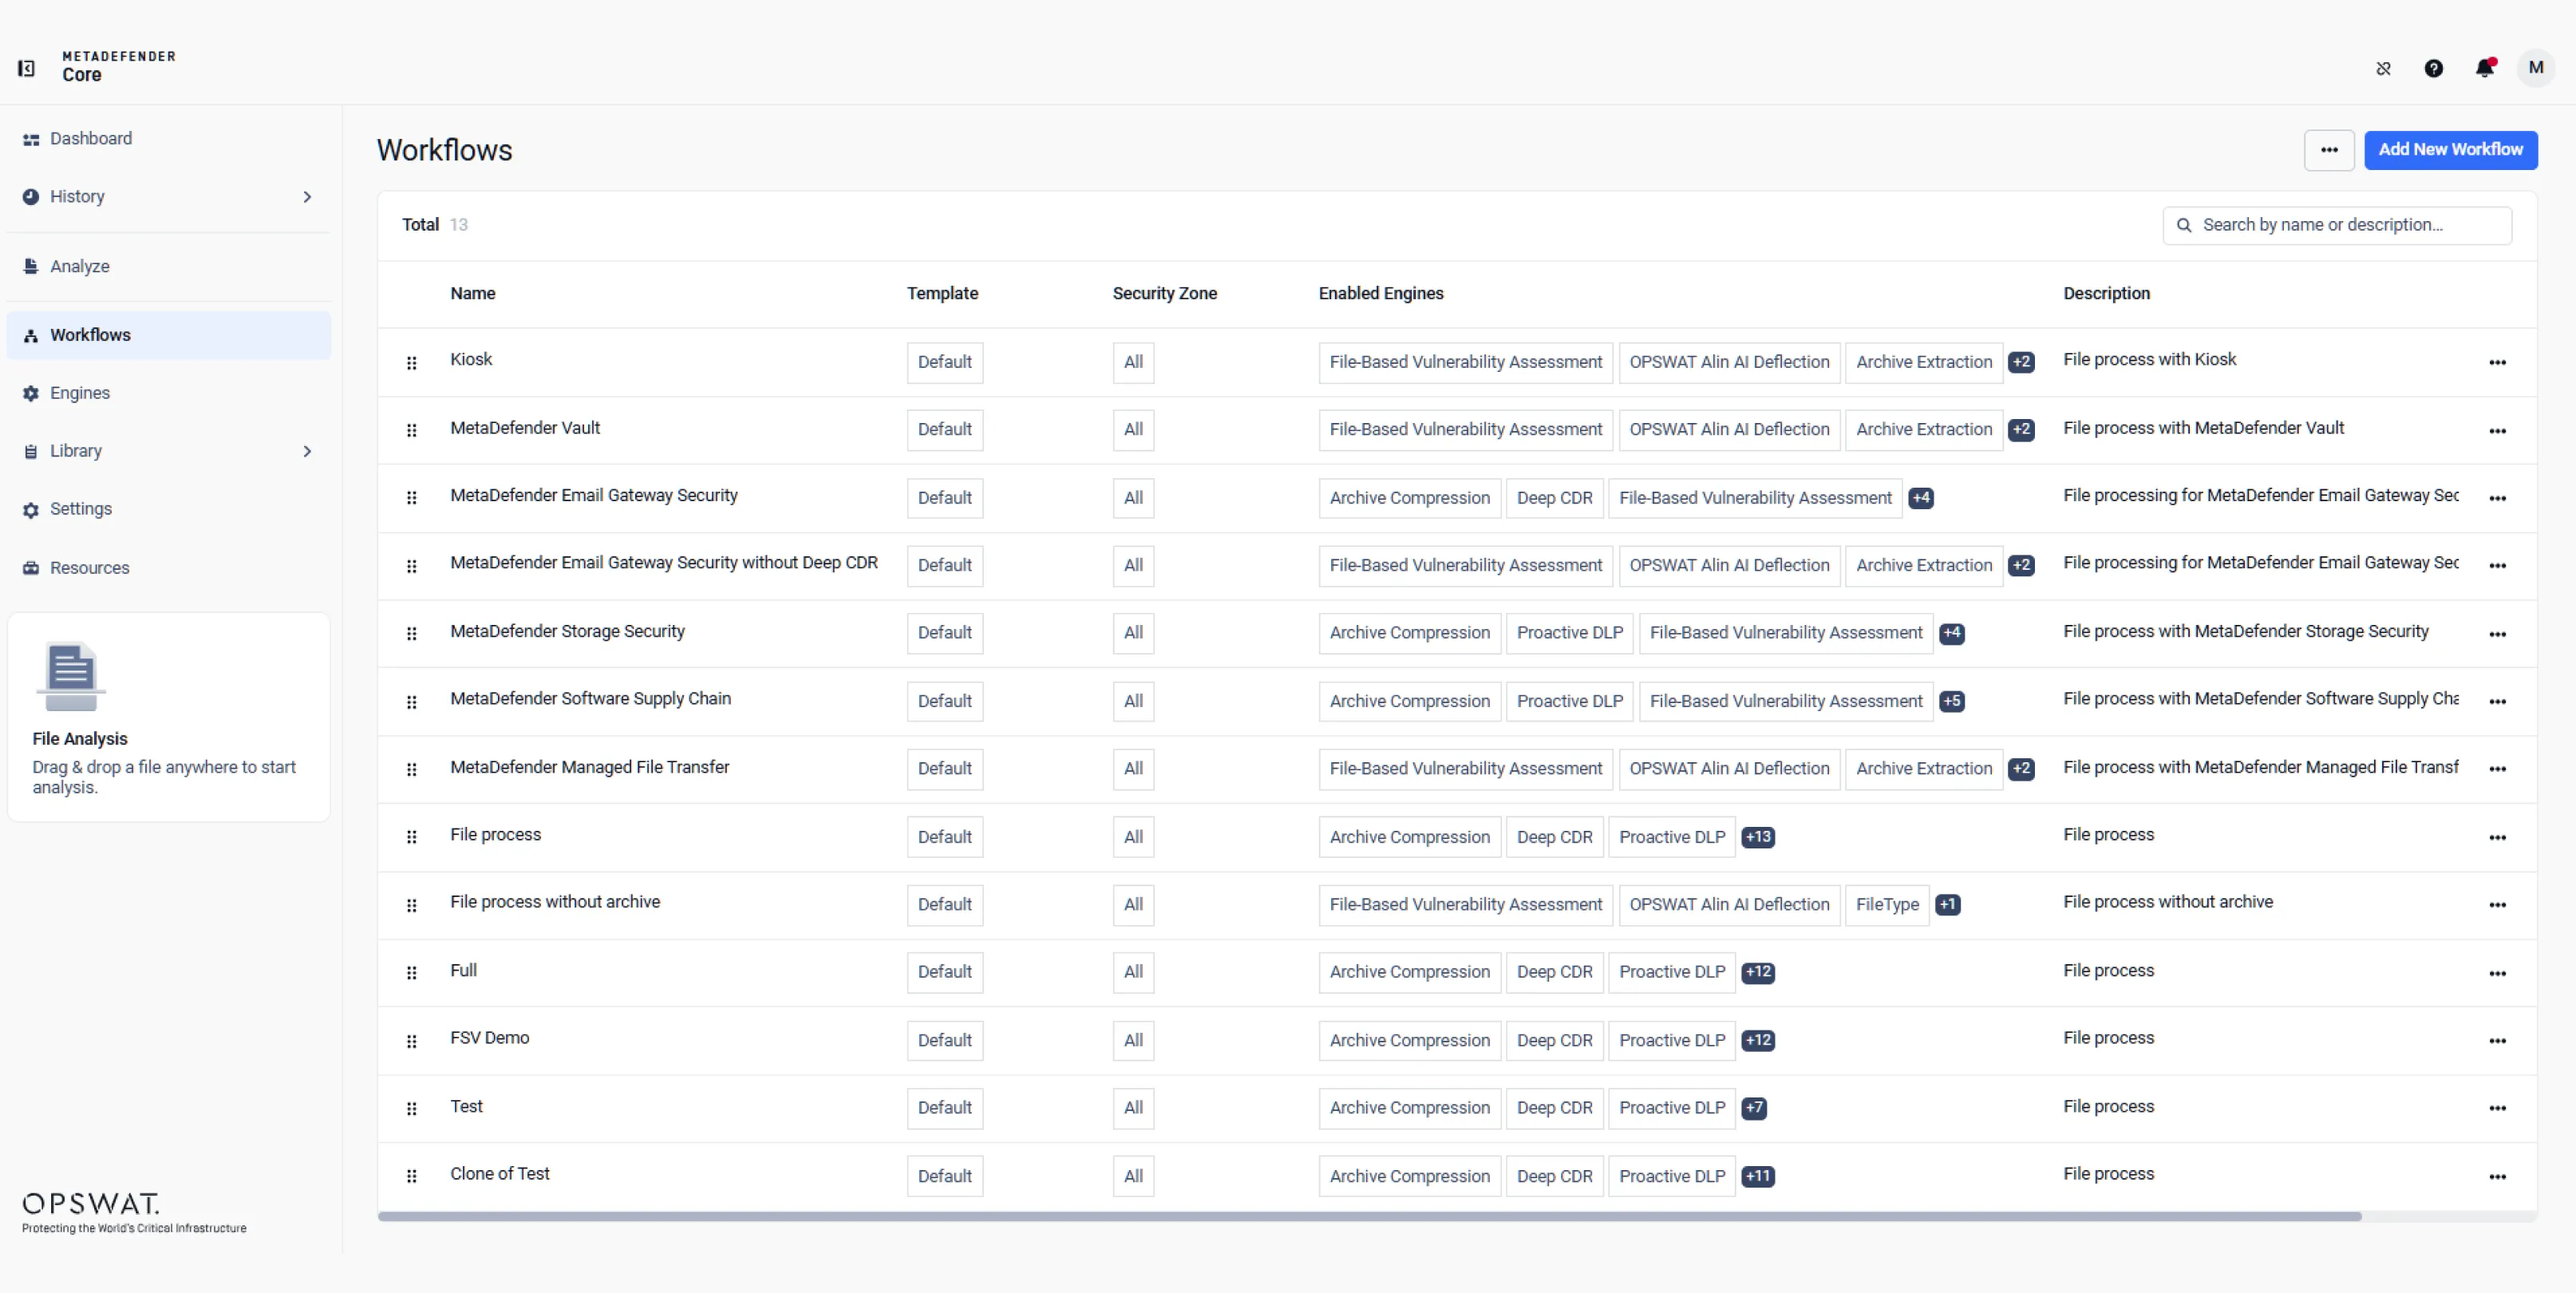
Configure security aligned workflows to match your operational policies across email, file transfer, storage, or custom environments. Establish how files enter the system and how they are processed.
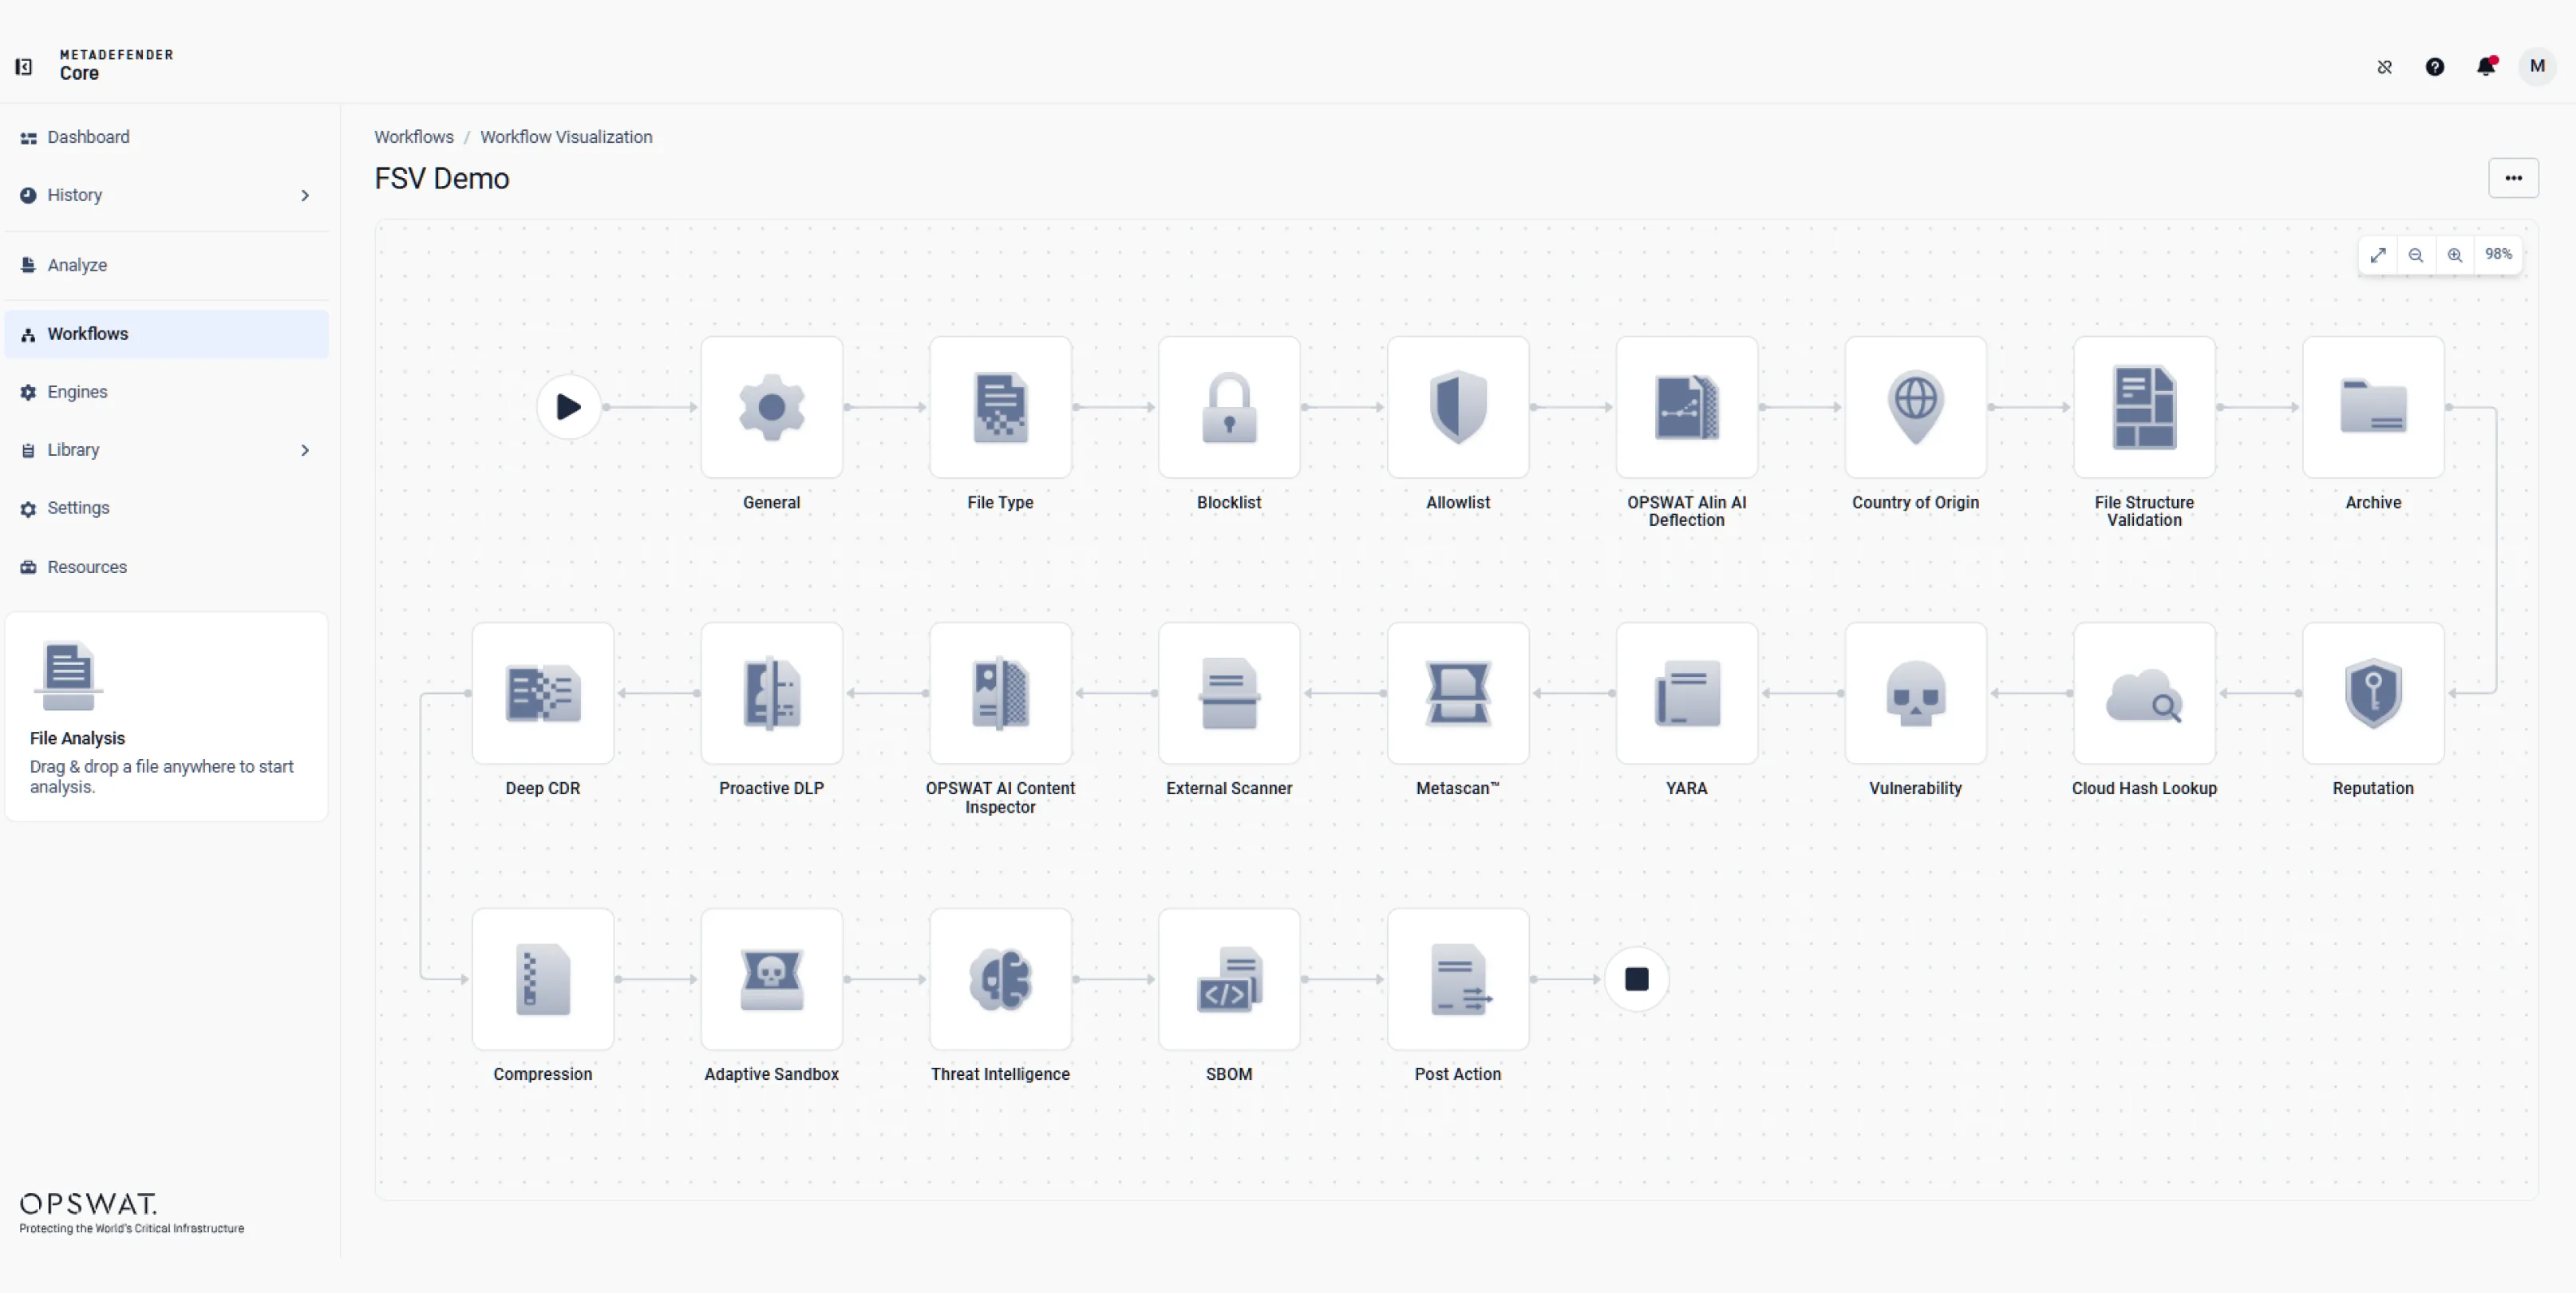
Use modular, layered detection and prevention engines, including Predictive Alin AI, Deep CDR™ Technology, Multiscanning, AI Content Inspector, Proactive DLP, Adaptive Sandbox and Threat Intelligence, to tailor file-processing flows to your operational needs and security requirements.
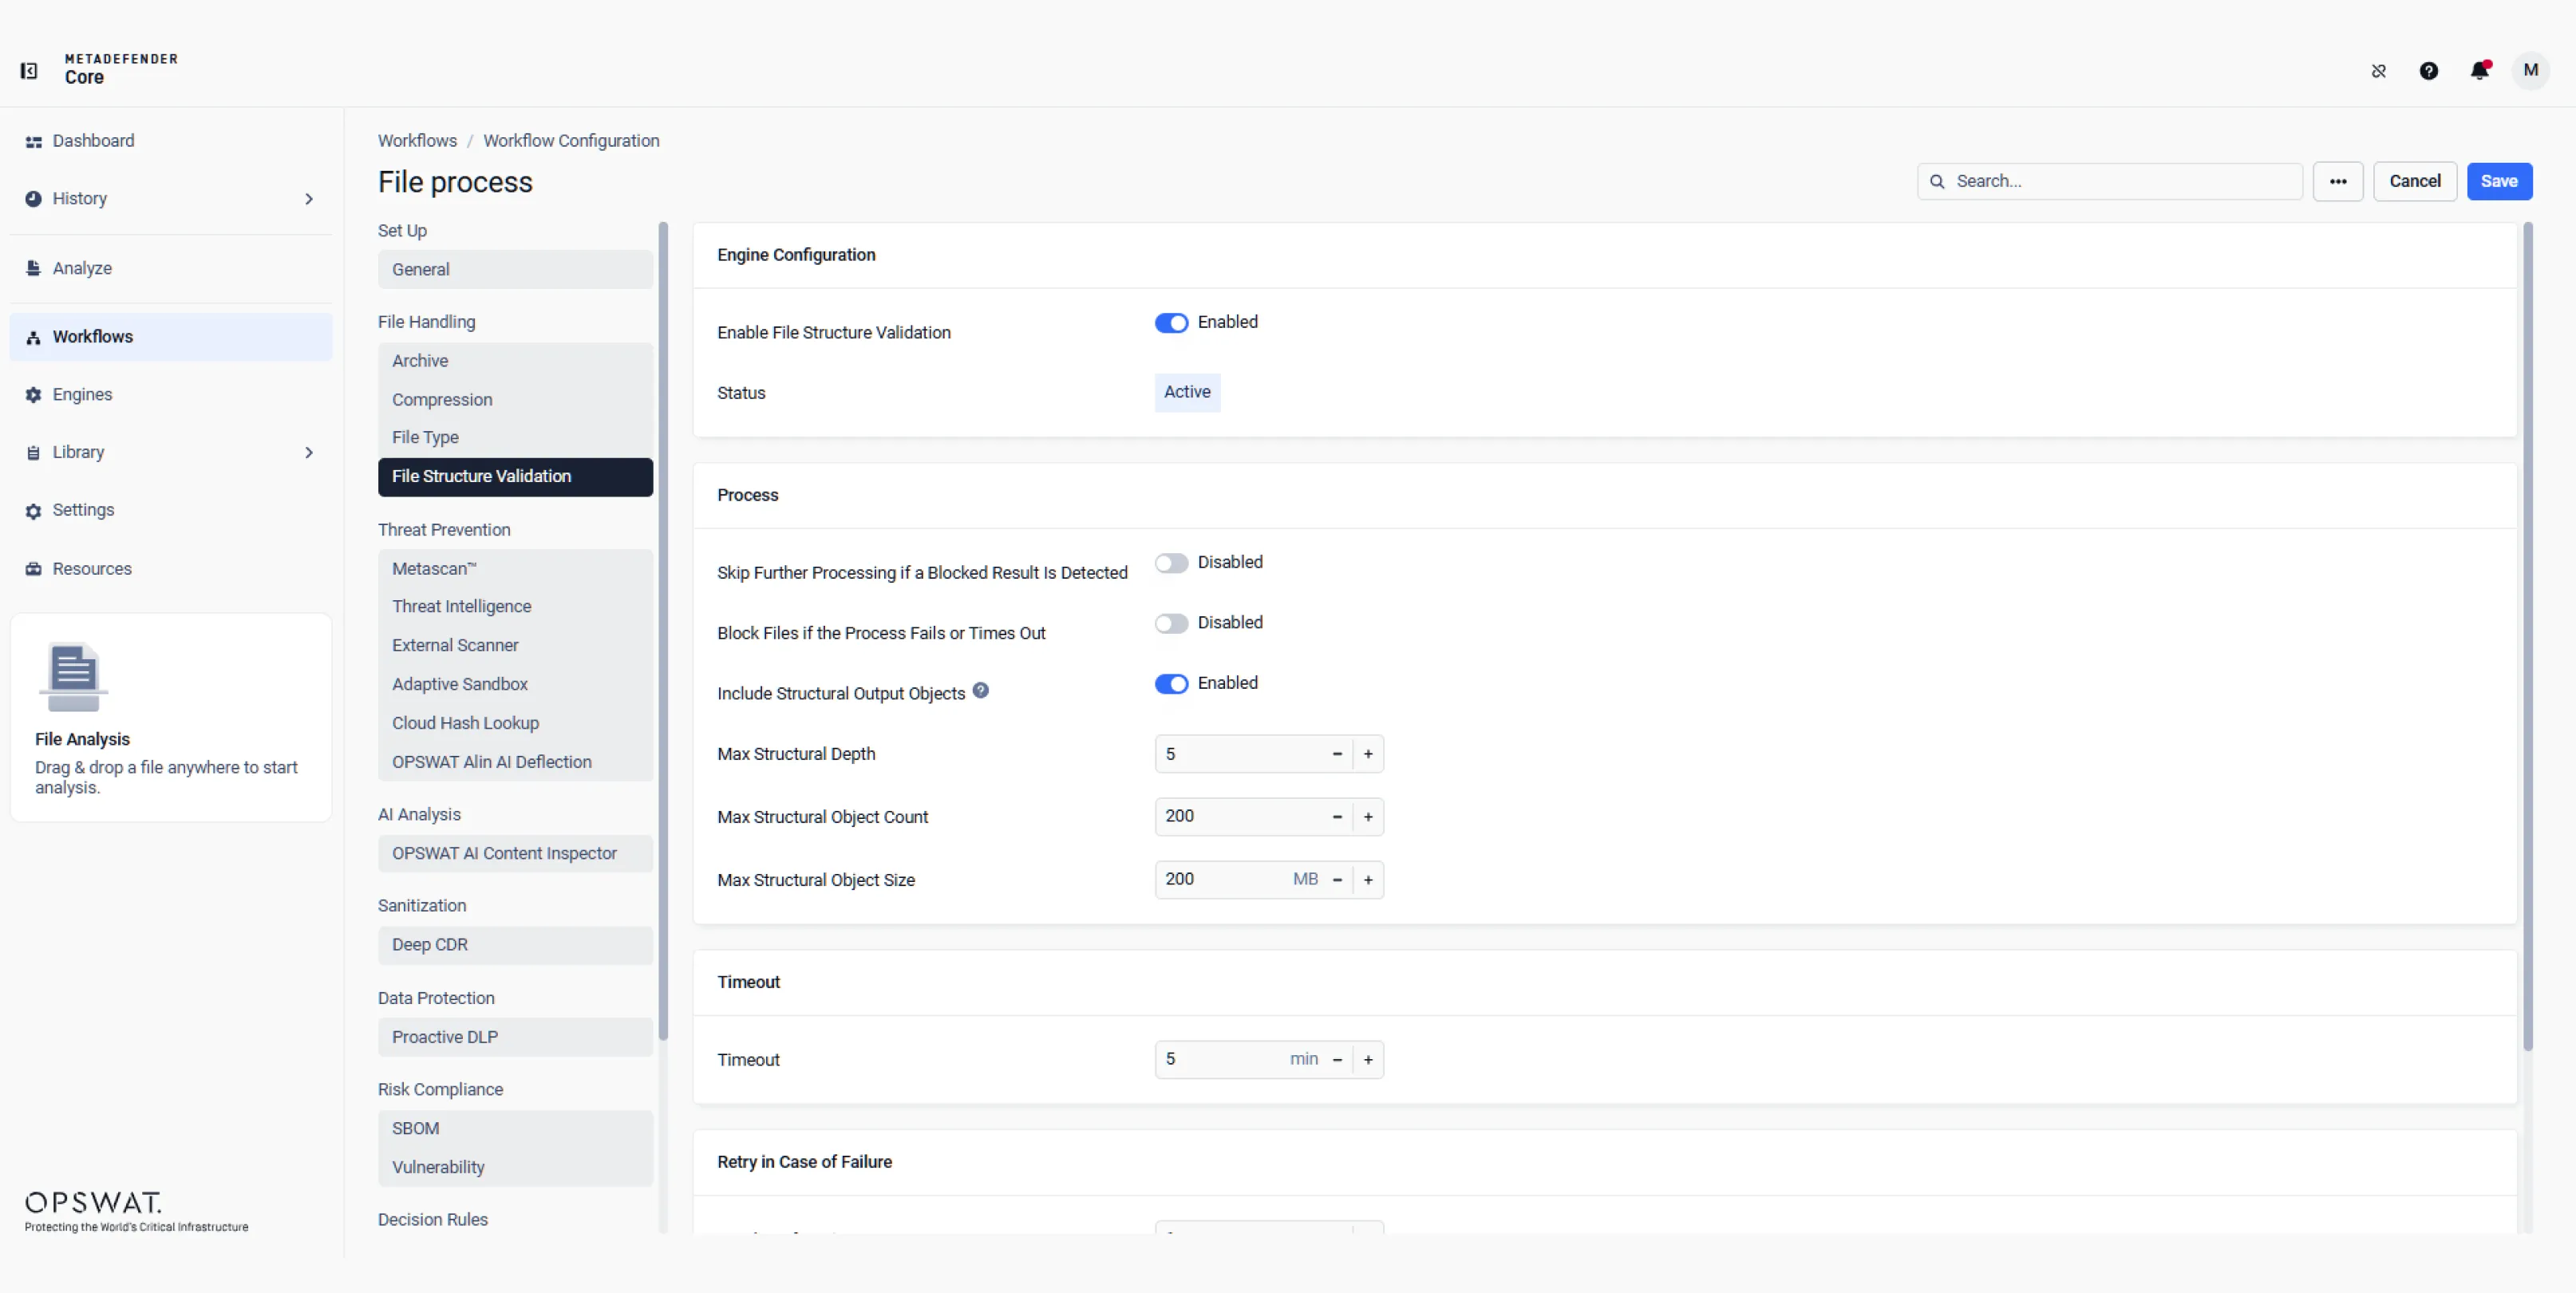
Configure Archive Extraction, Compression, True File Type Detection, and File Structure Validation to ensure files are correctly identified, unpacked, processed, and verified before downstream analysis.
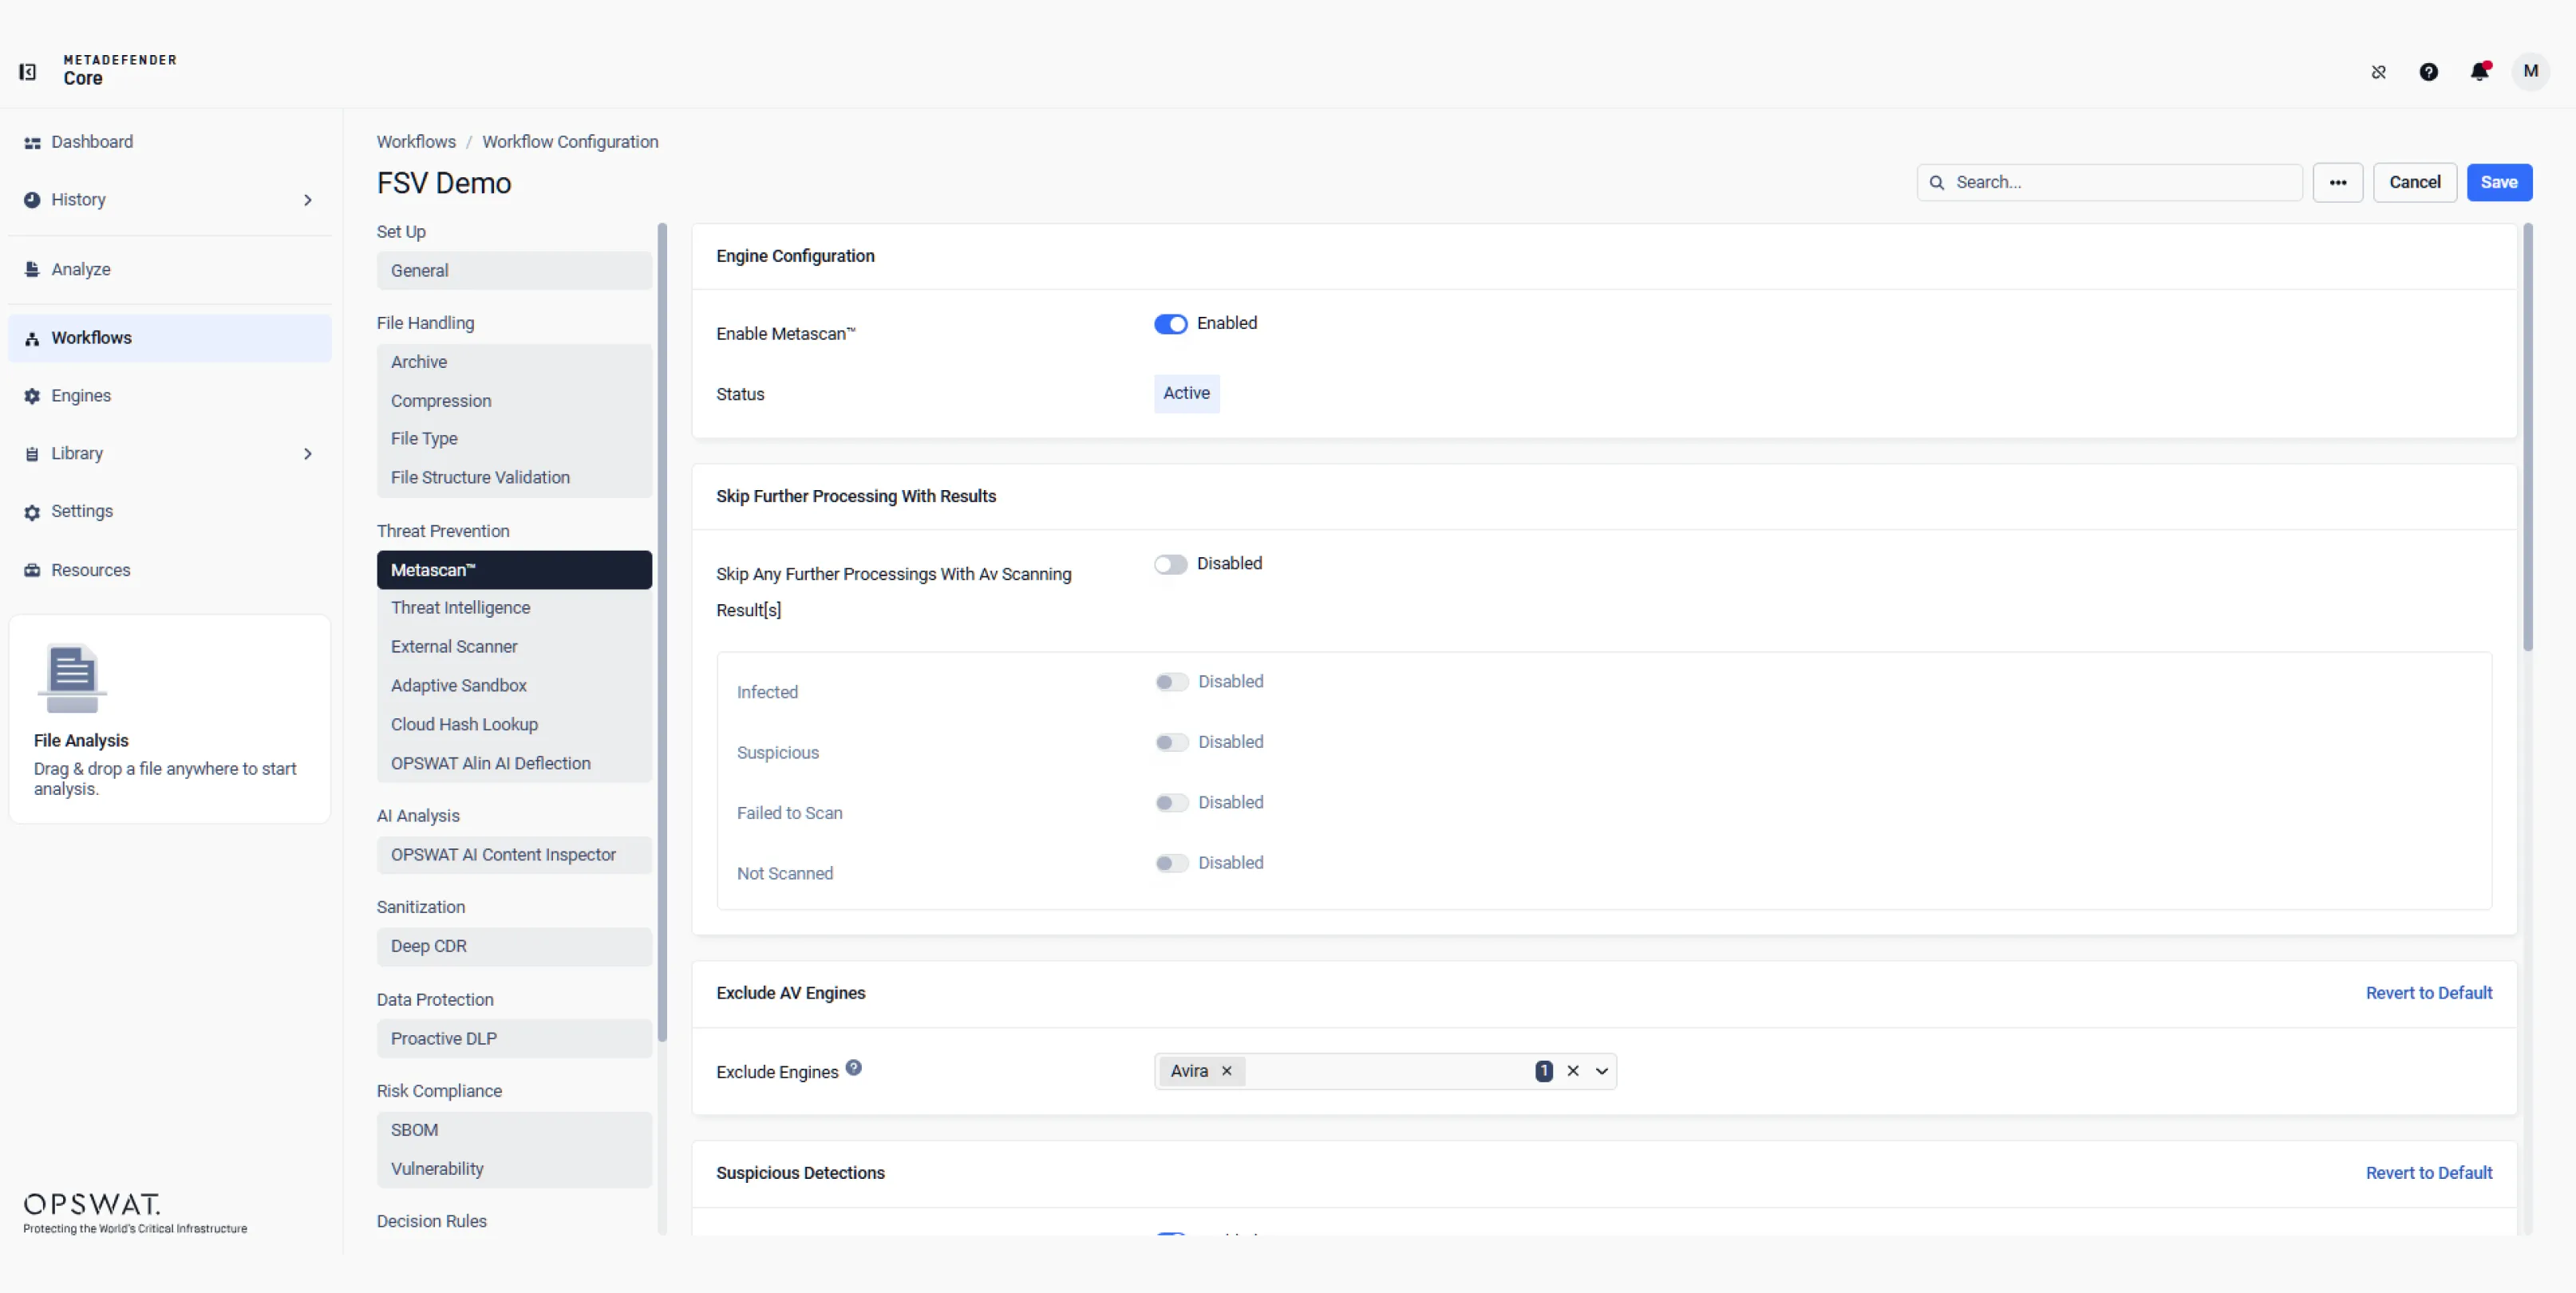
Combine Metascan, Predictive Alin AI, Threat Intelligence, Adaptive Sandbox, and Alin AI Deflection to identify known, unknown, and AI-generated threats through multi-engine scanning, reputation intelligence, behavioral analysis, and intelligent routing.
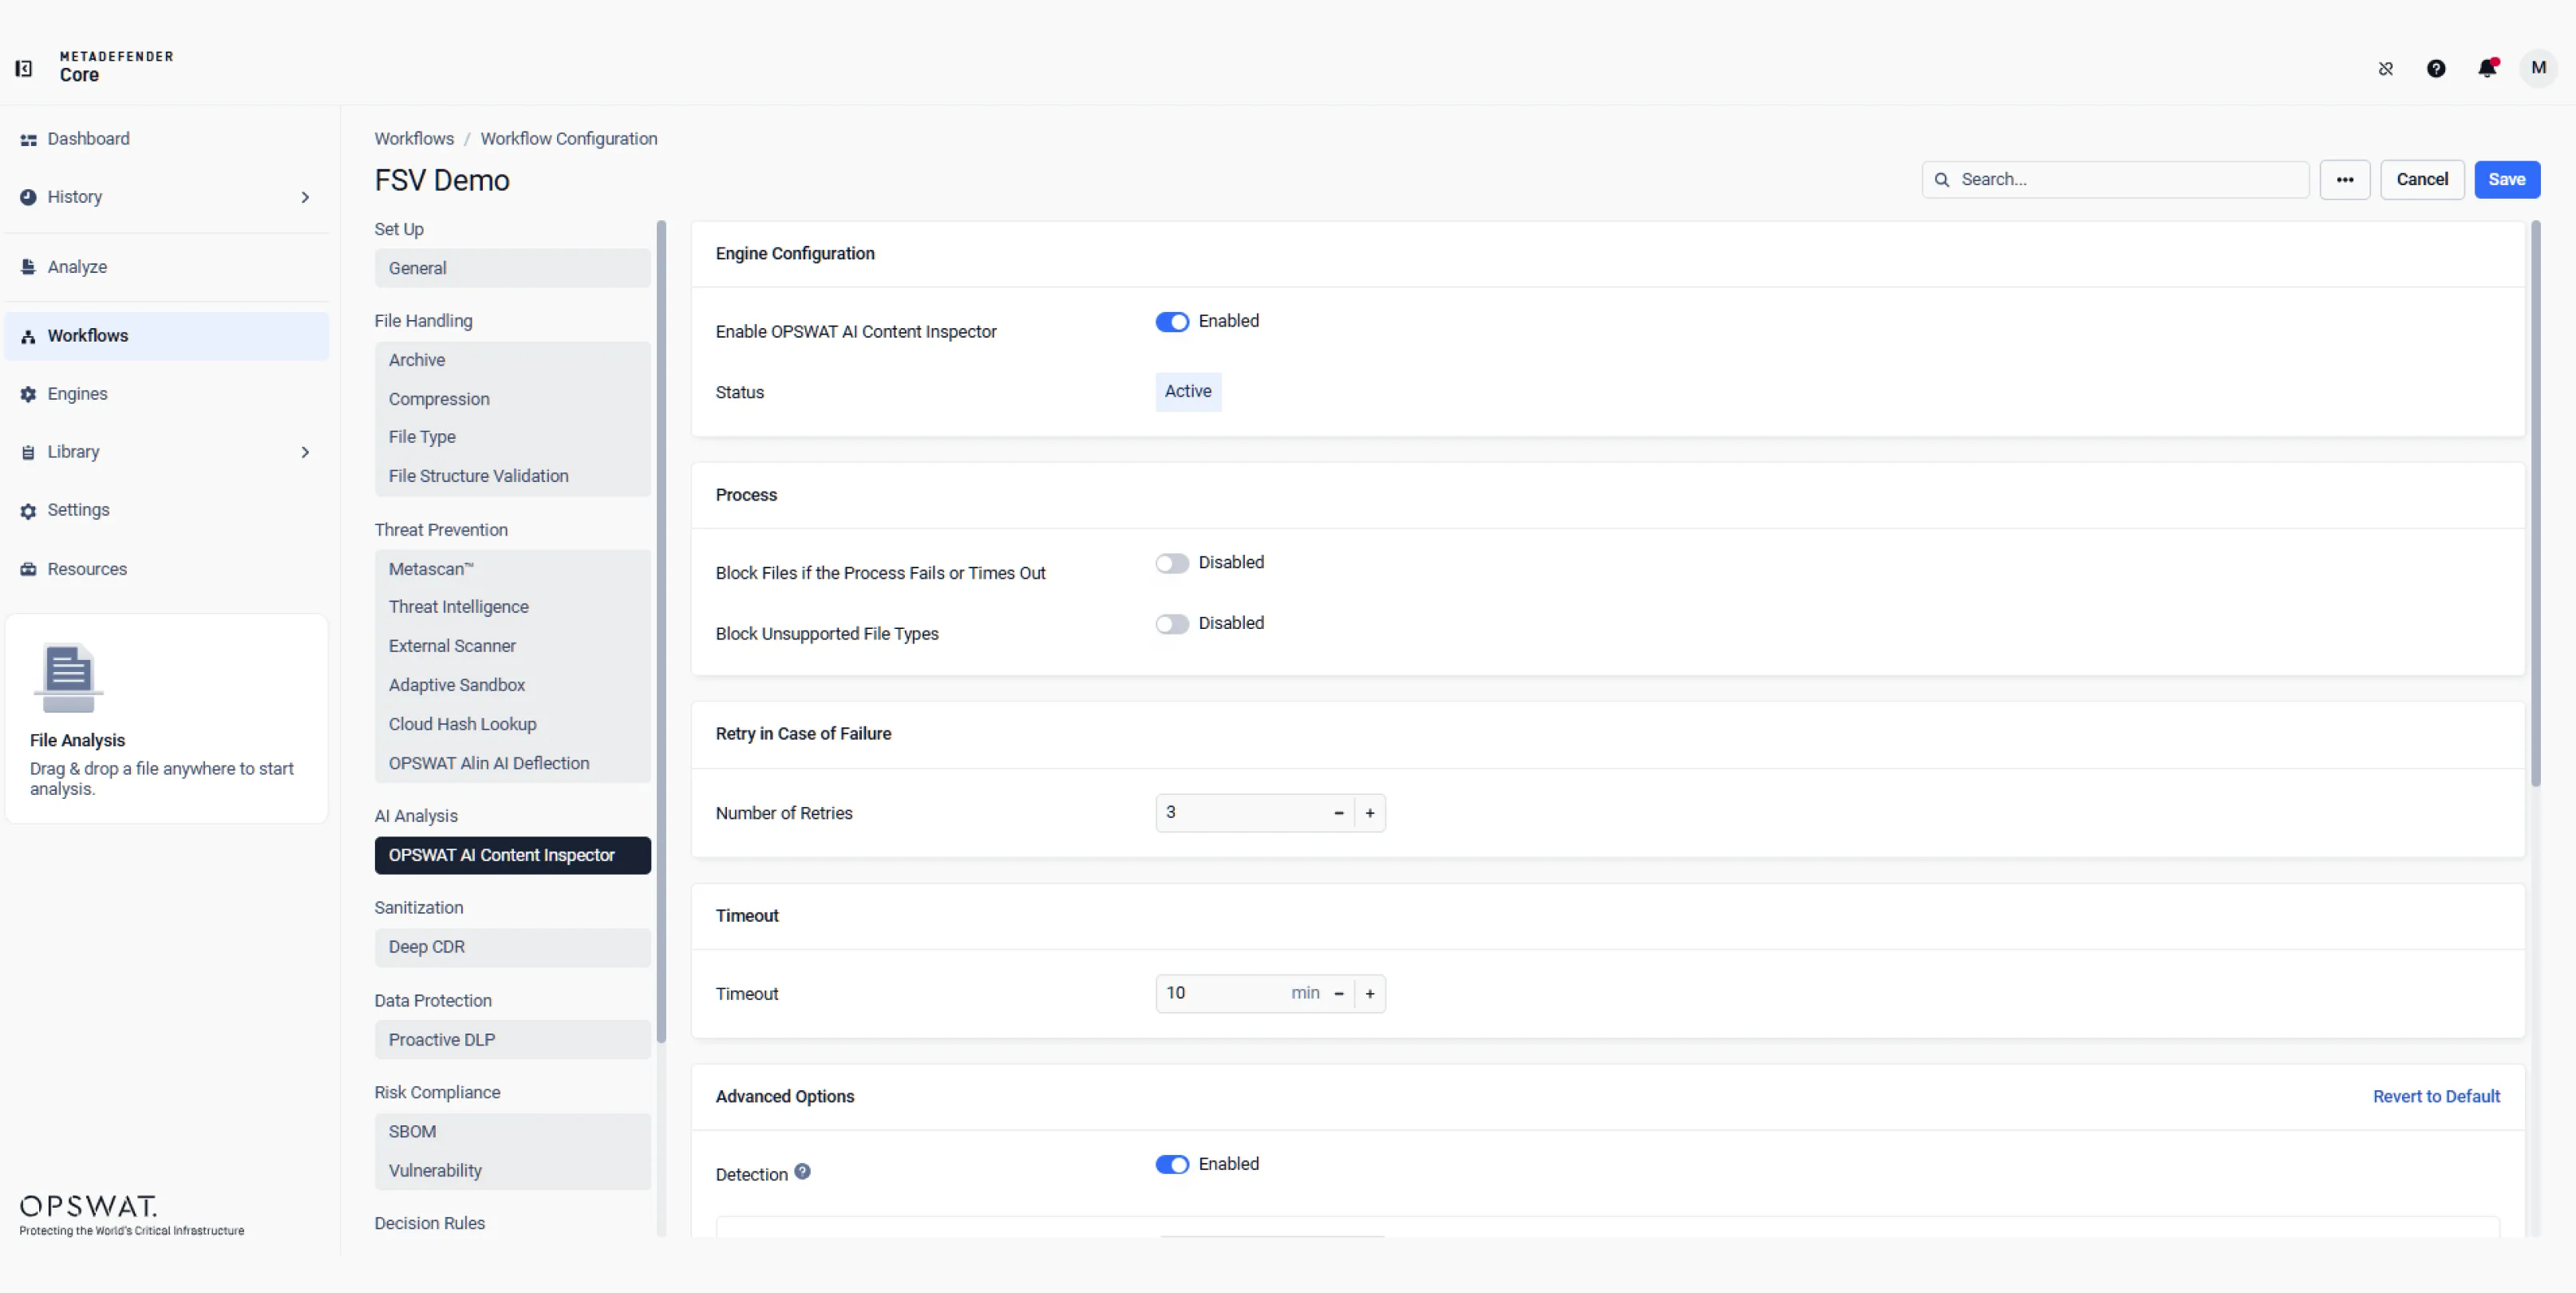
Configure AI Content Inspector to analyze text and images, identify AI-generated content, and detect potential fraud. Use its verdicts to assess risk before files enter critical workflows.
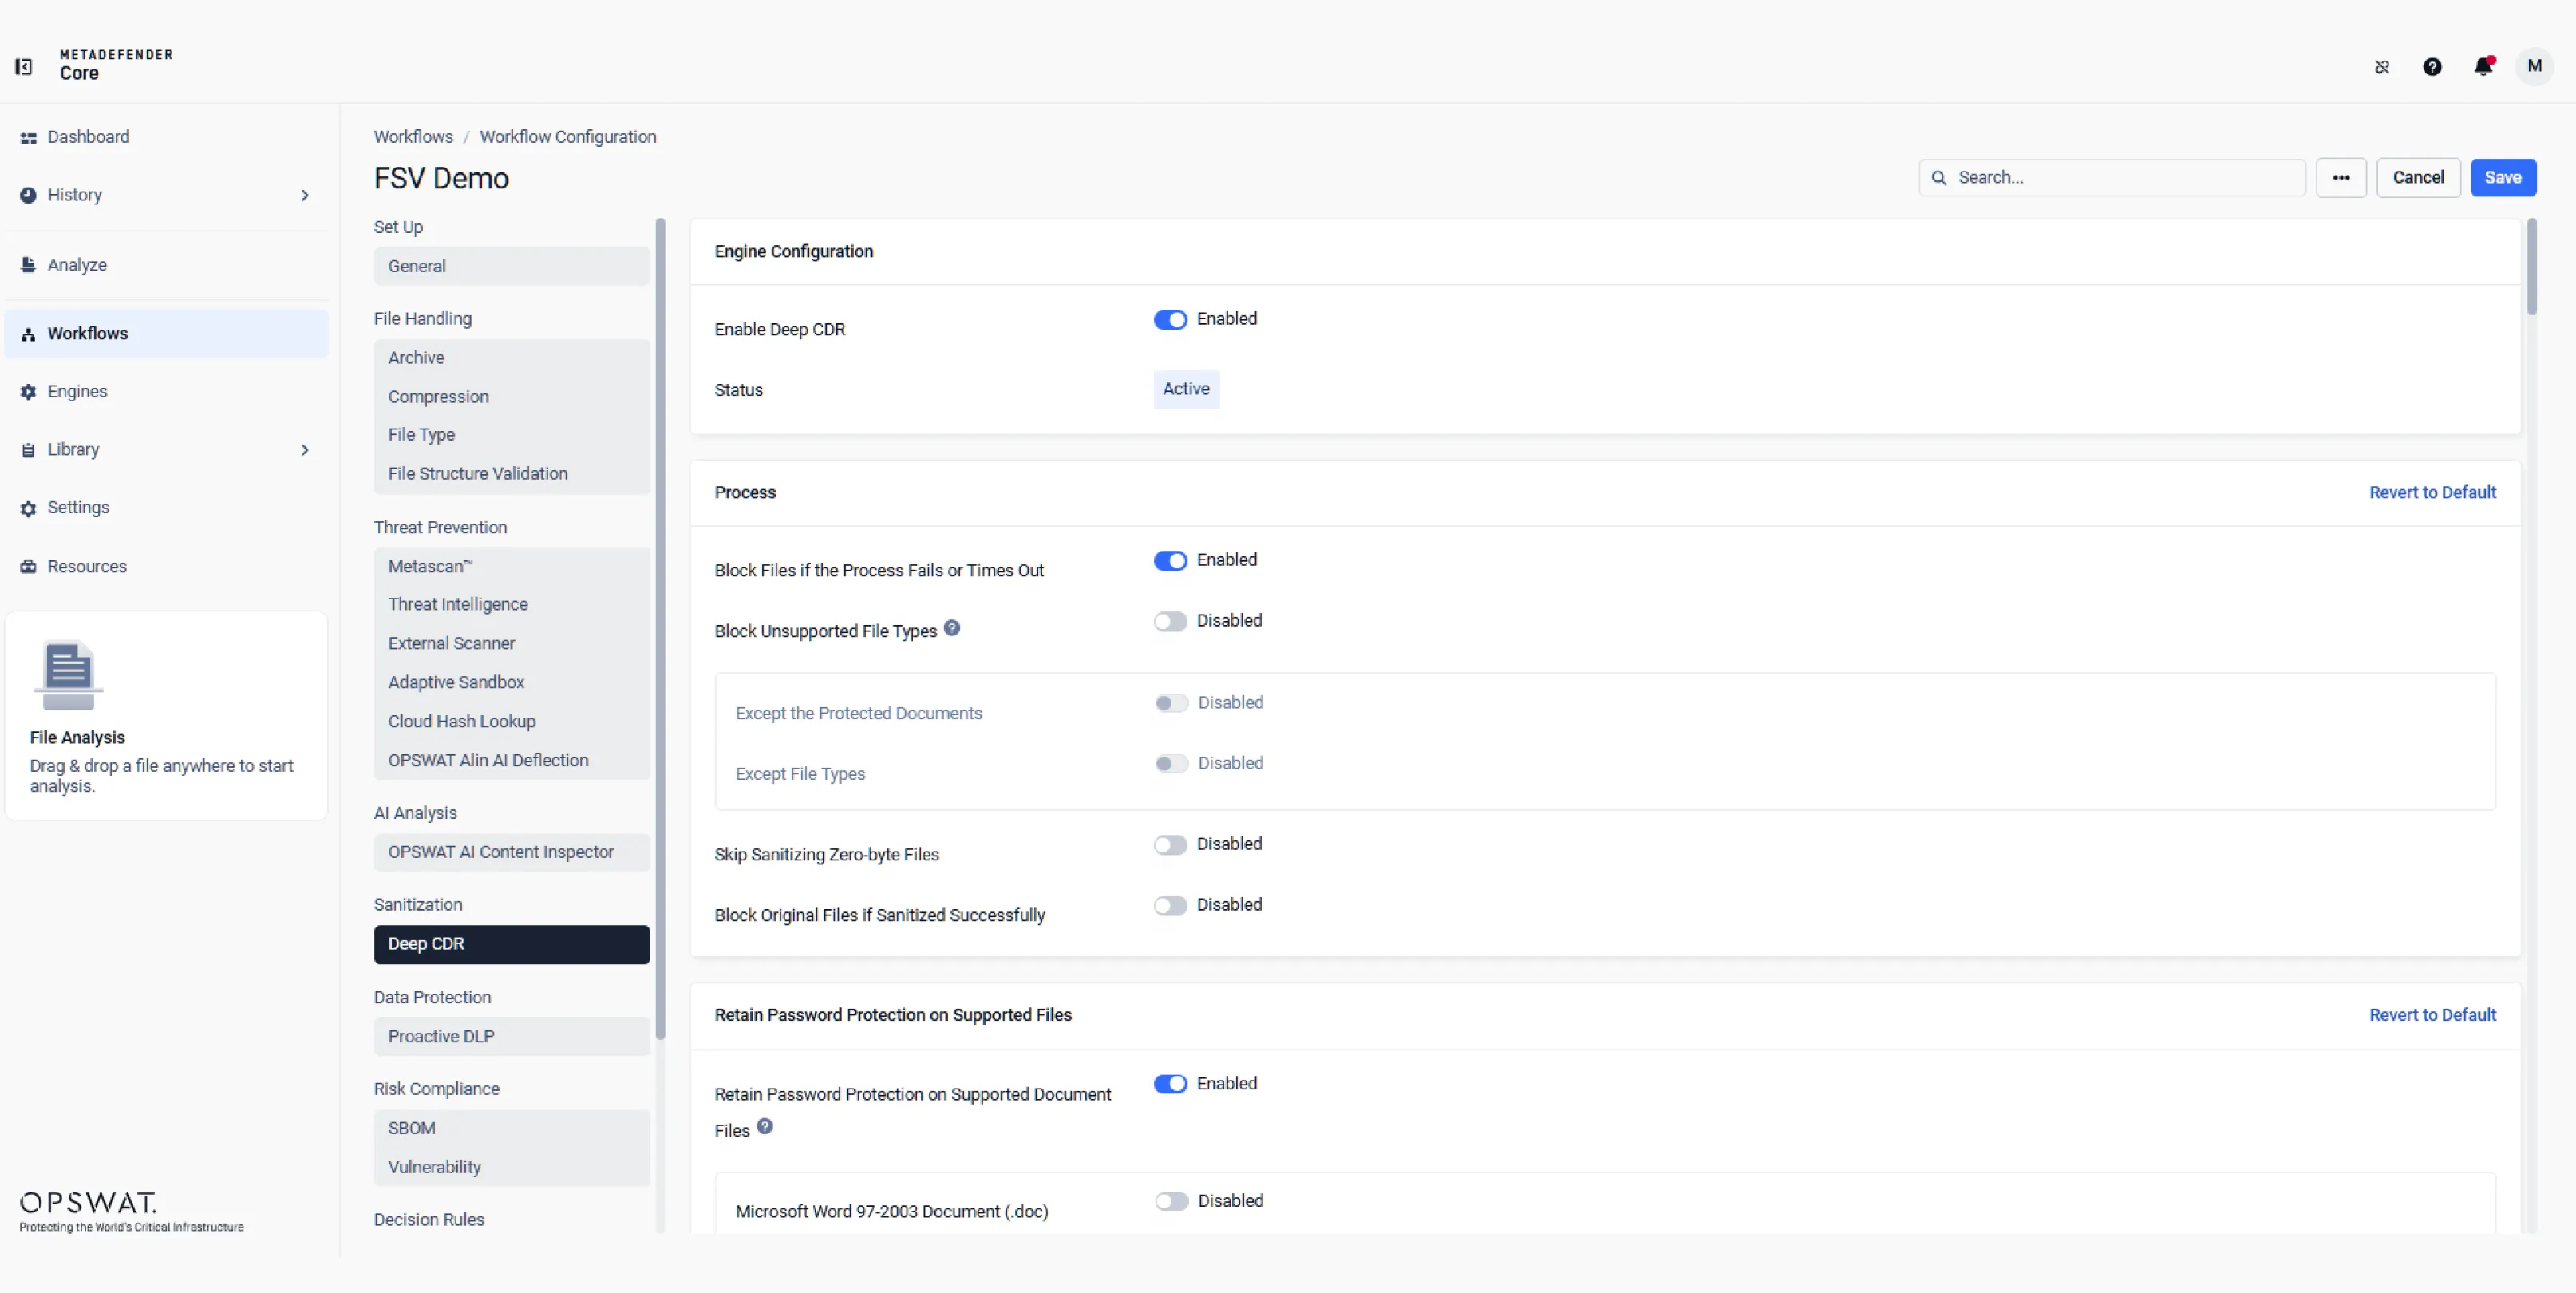
Configure Deep CDR™ Technology to sanitize files by removing potentially malicious content and reconstructing safe, usable versions while preserving business-critical functionality before files enter downstream workflows.
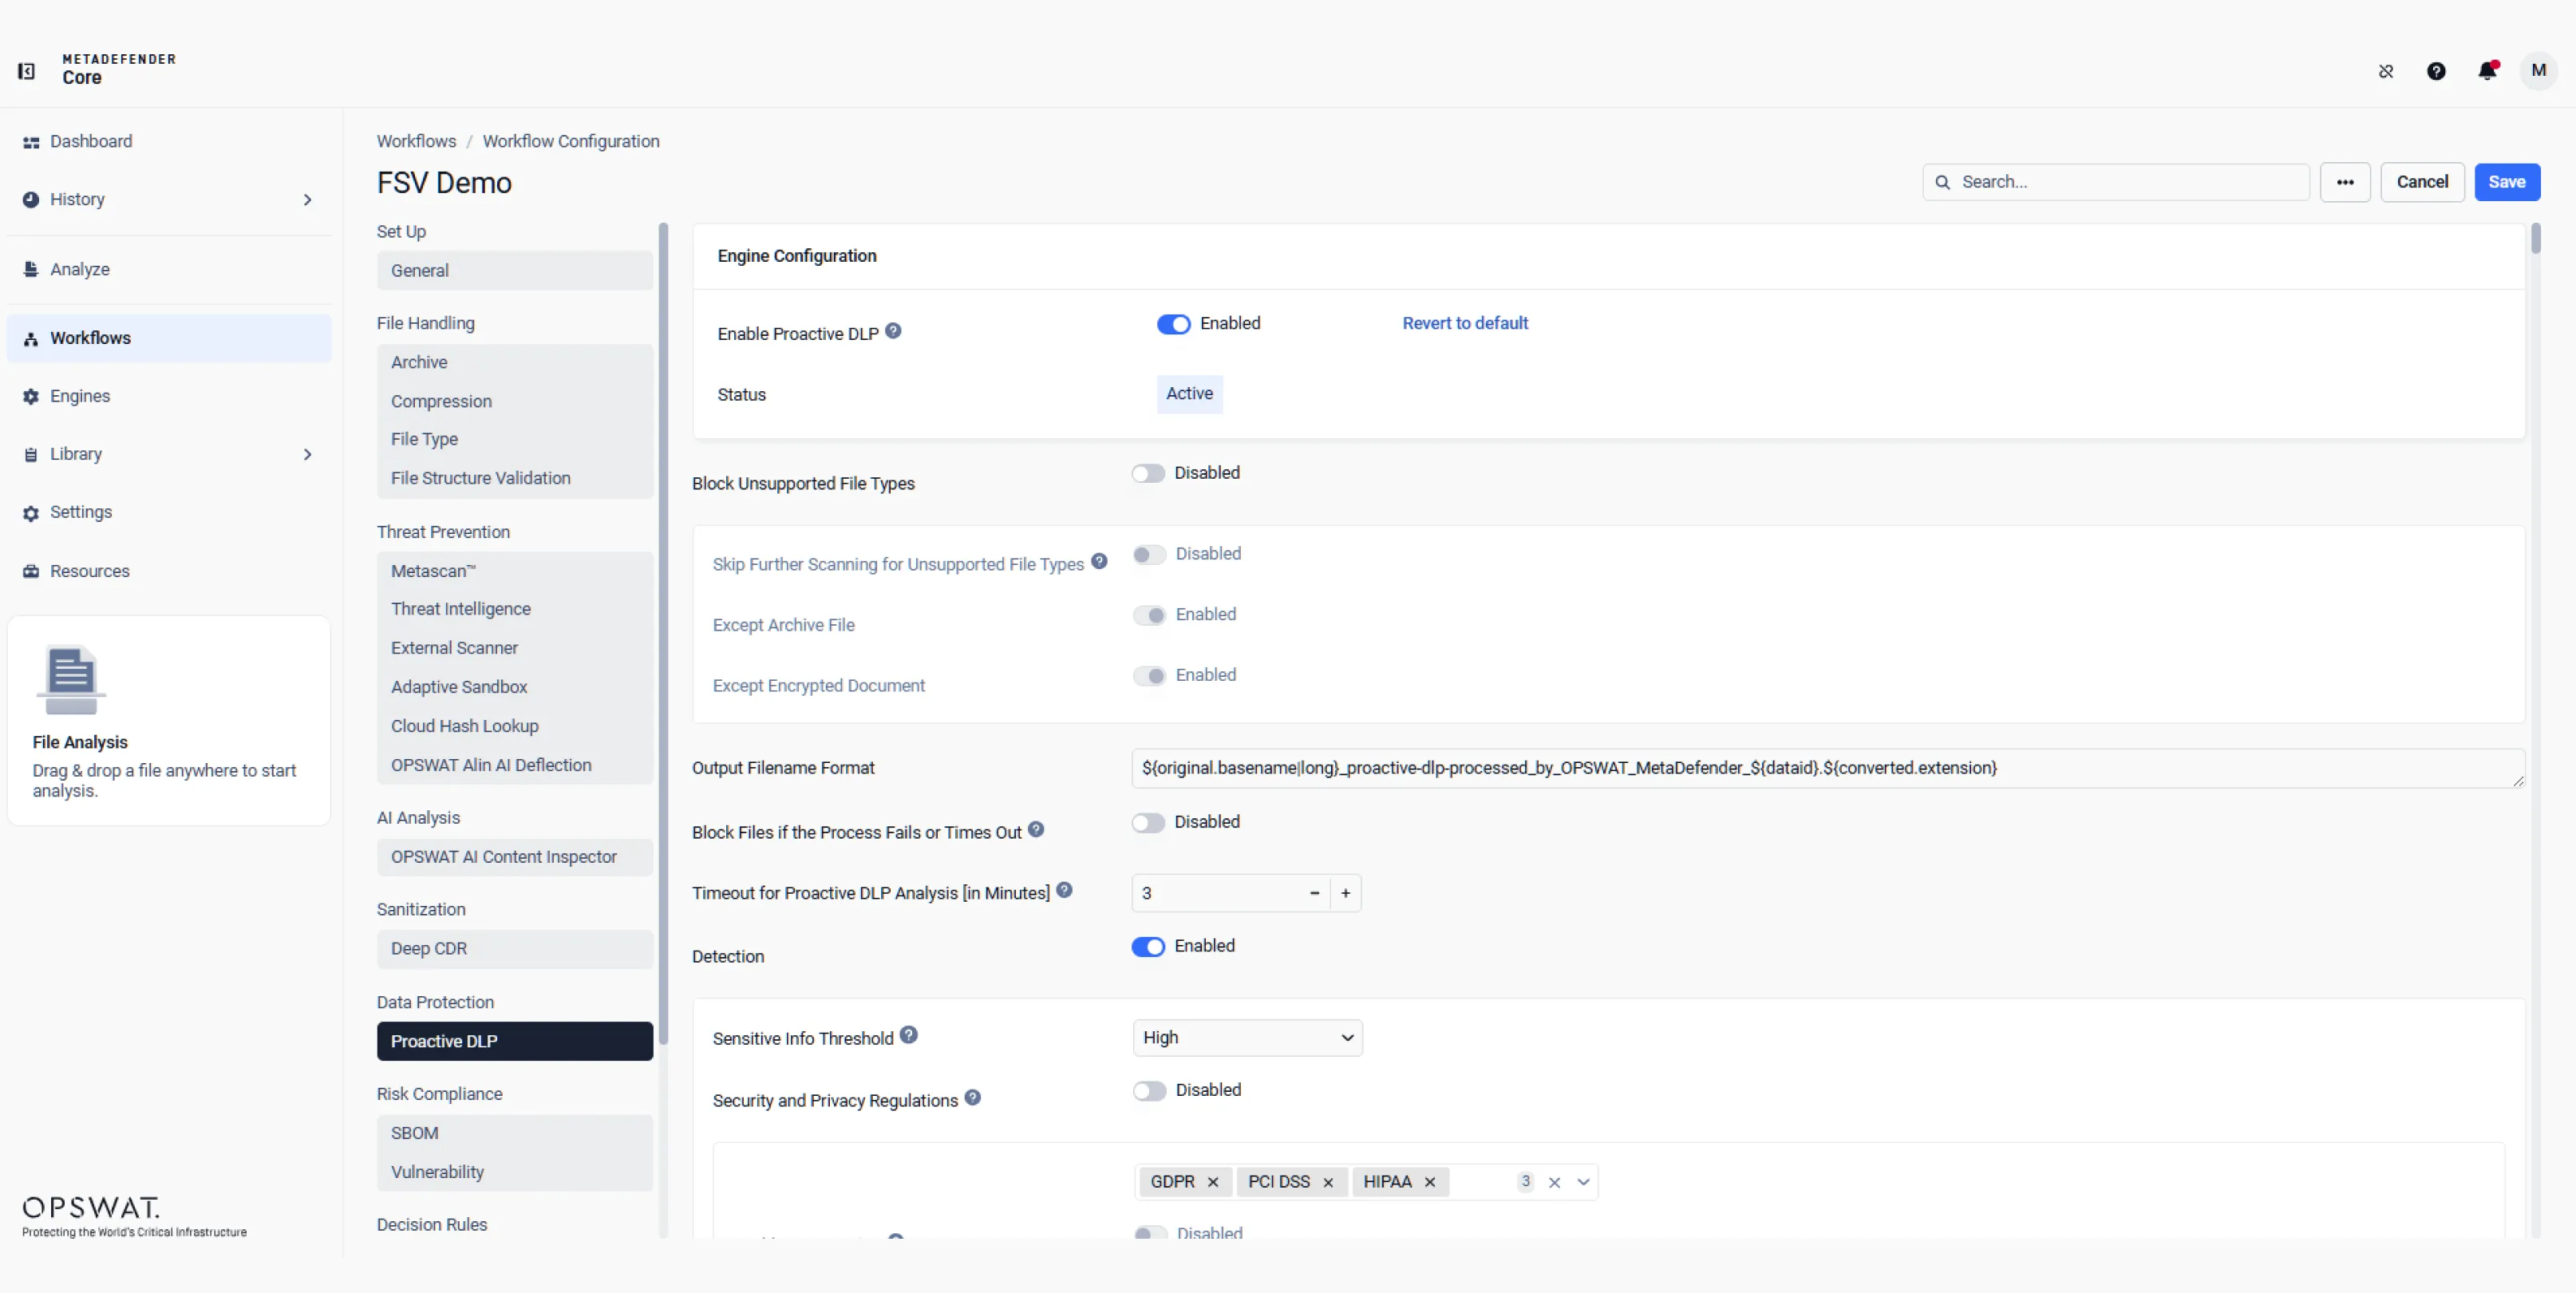
Use AI-powered classification and pattern detection to identify and protect sensitive data. Configure rules to monitor file movement, reduce insider risk, and redact, block, or alert based on policy.
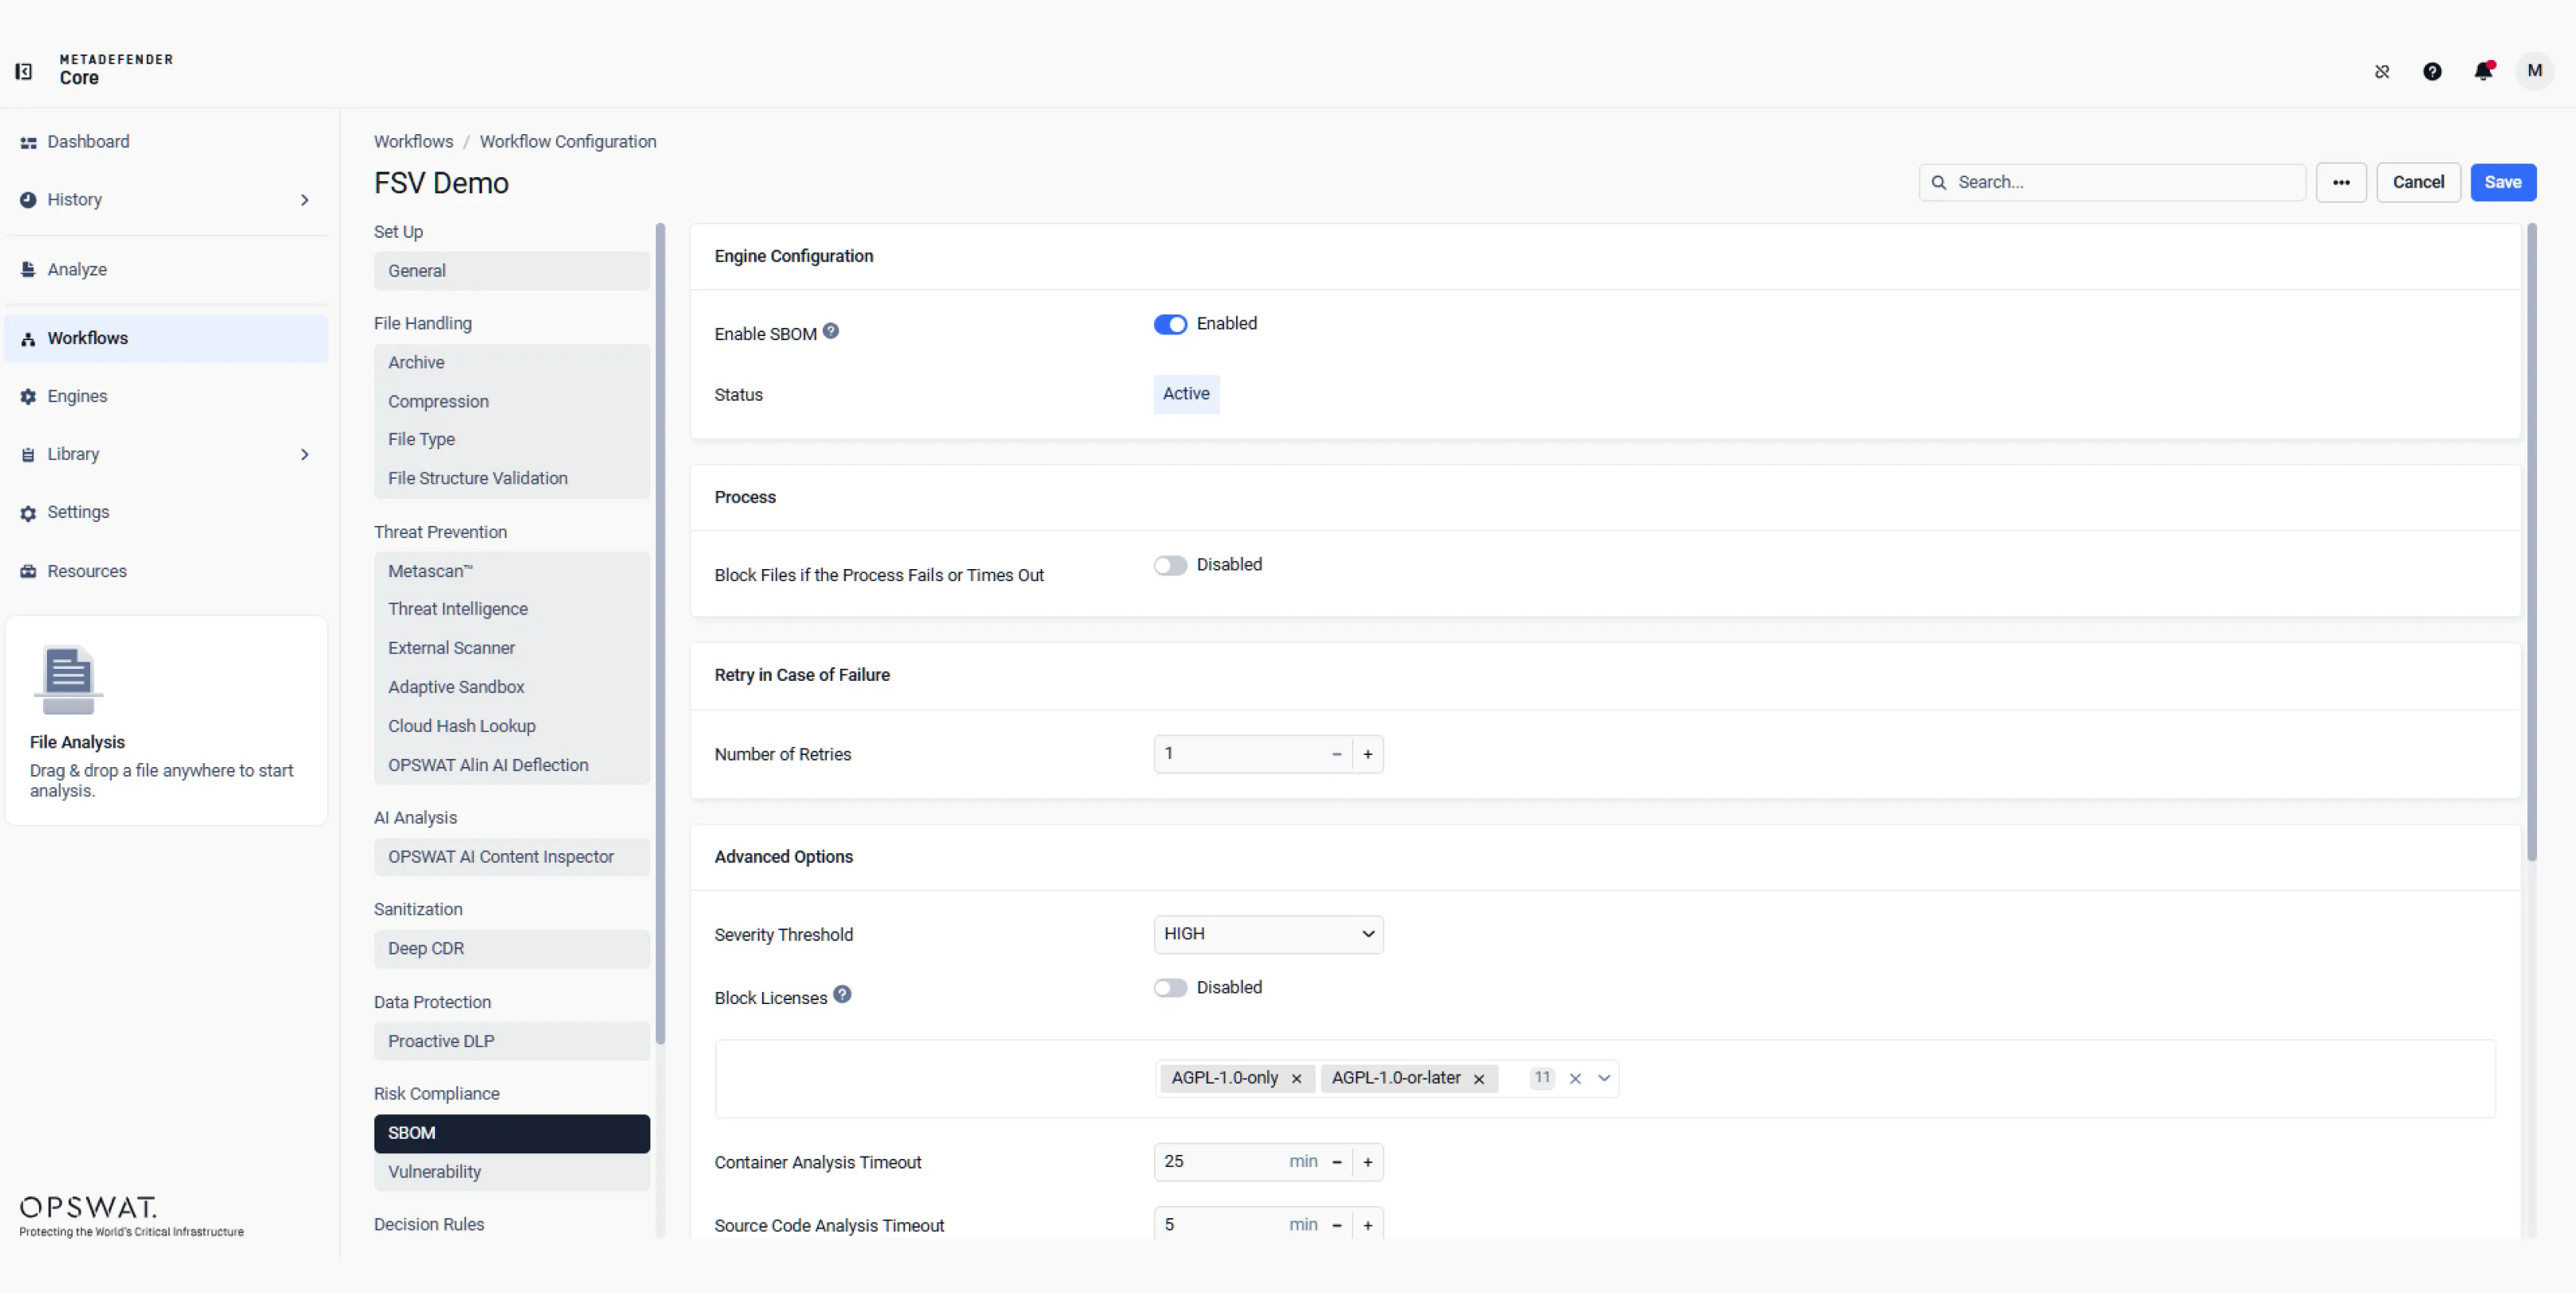
Analyze files, installers, and executables to generate an SBOM of components, versions, licenses, and dependencies. Identify known vulnerabilities and enforce risk-based policies before software enters critical environments.
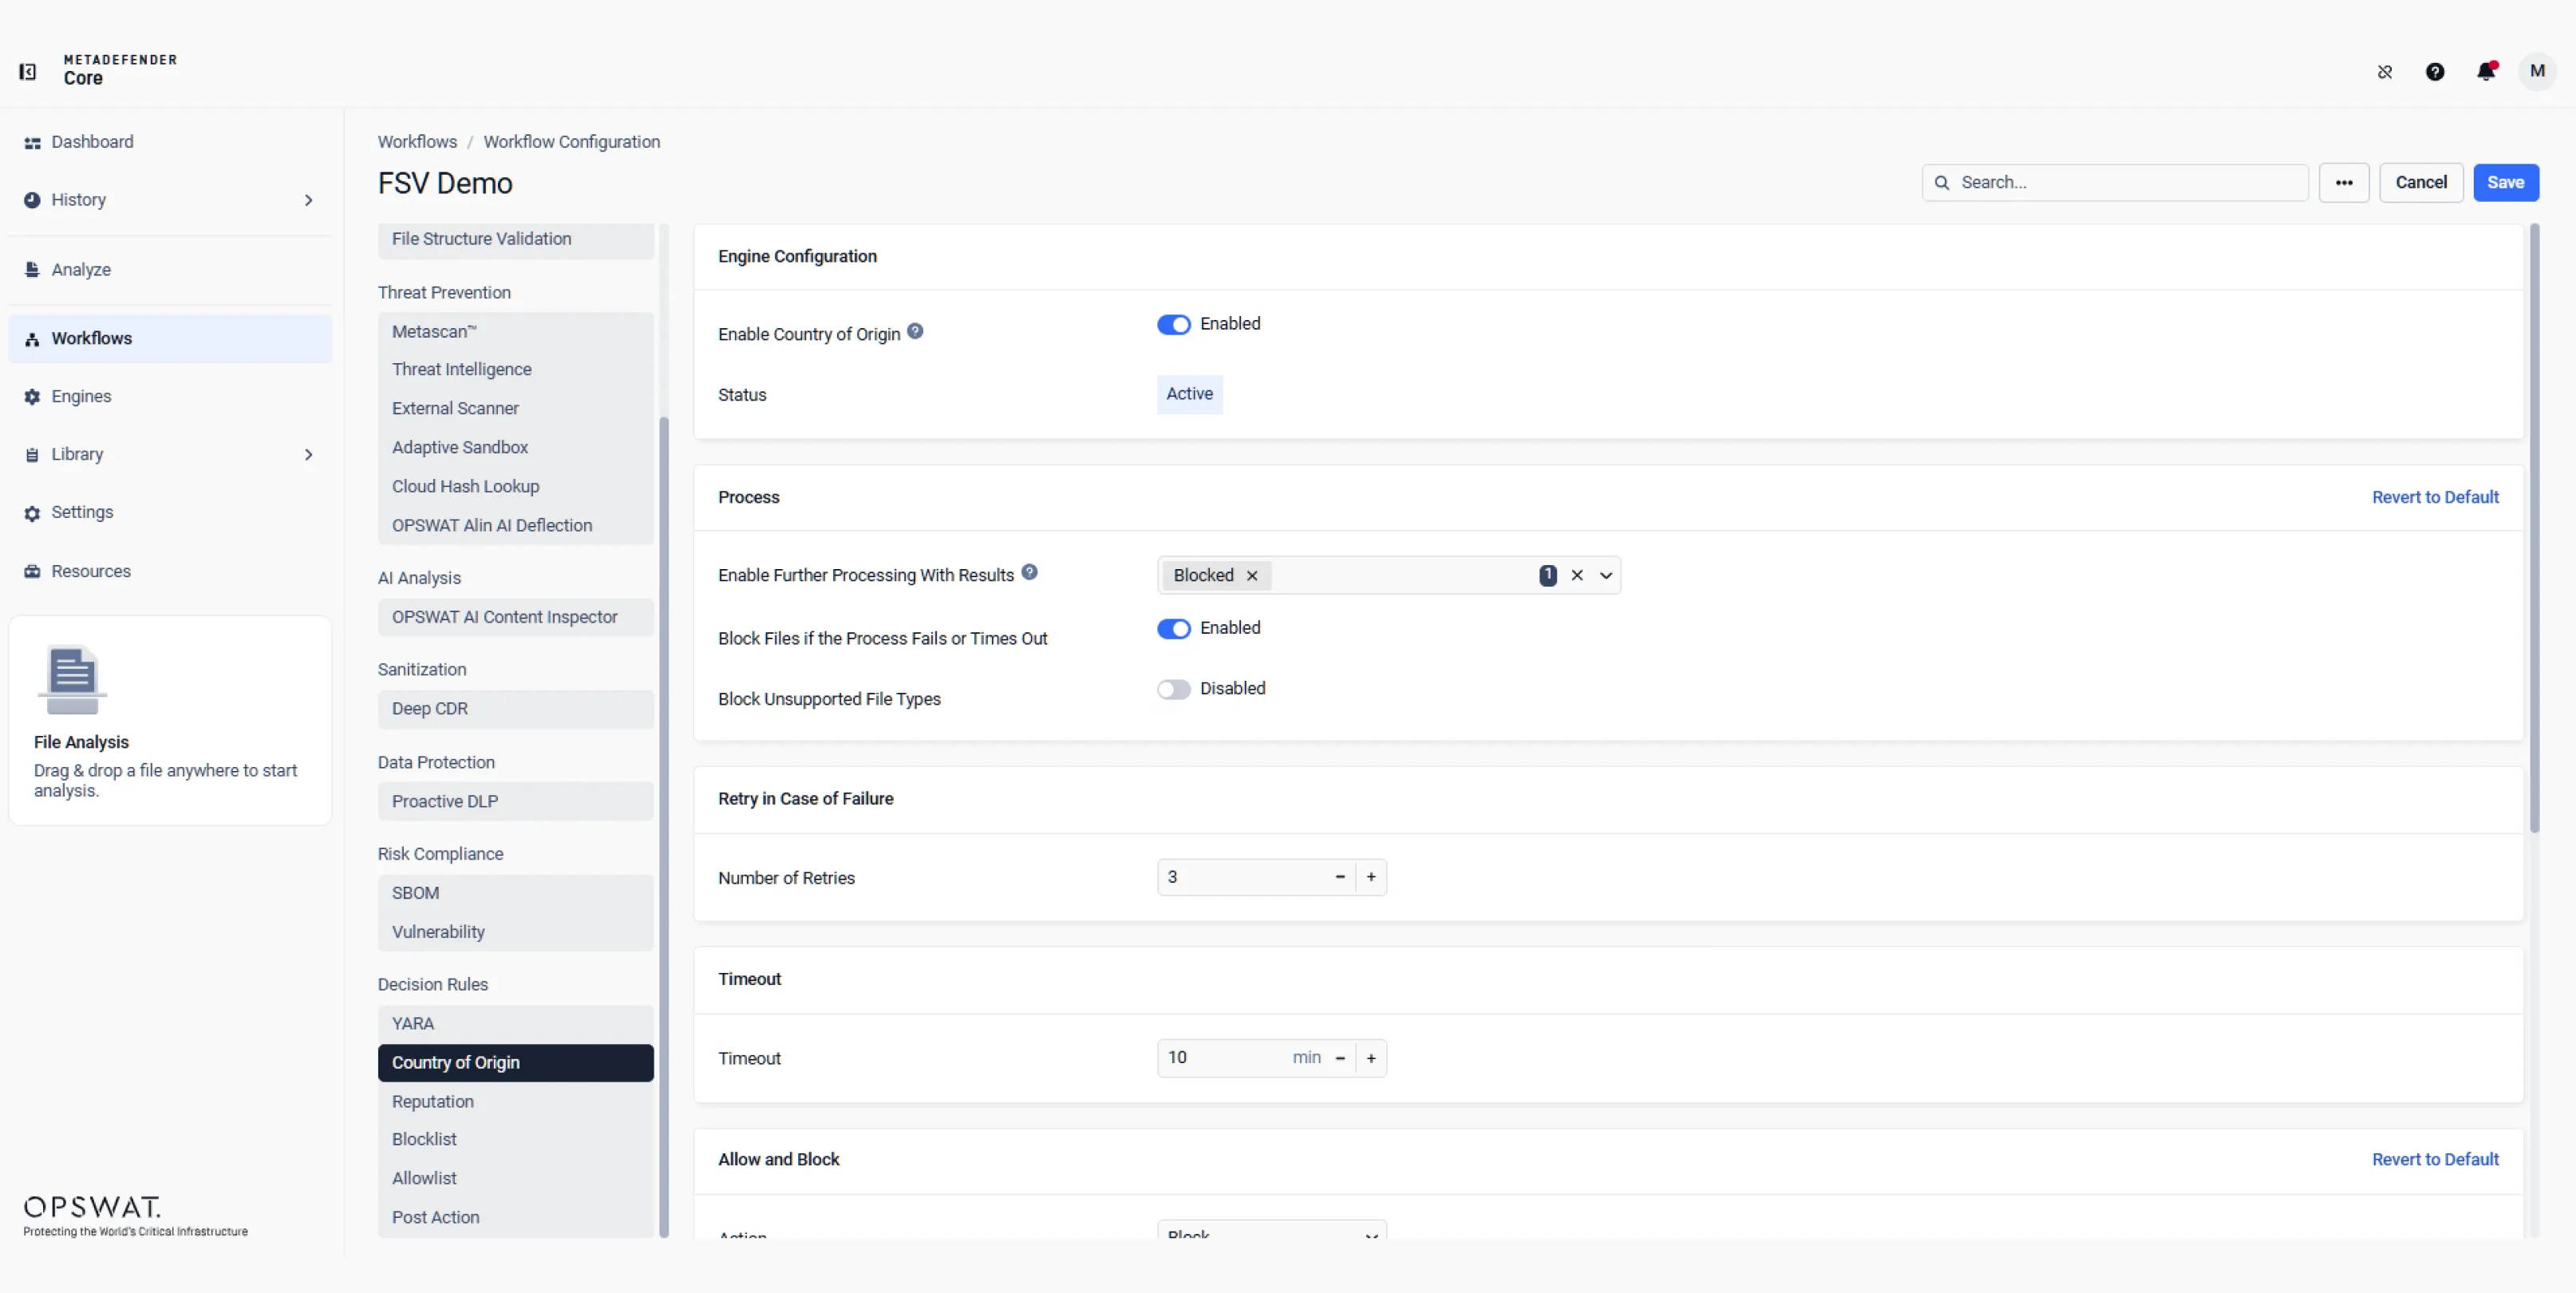
Configure YARA, Country of Origin, Reputation, Blocklist, Allowlist, and Post Action rules to evaluate file context and scan outcomes, then automatically allow, block, or route files according to policy.
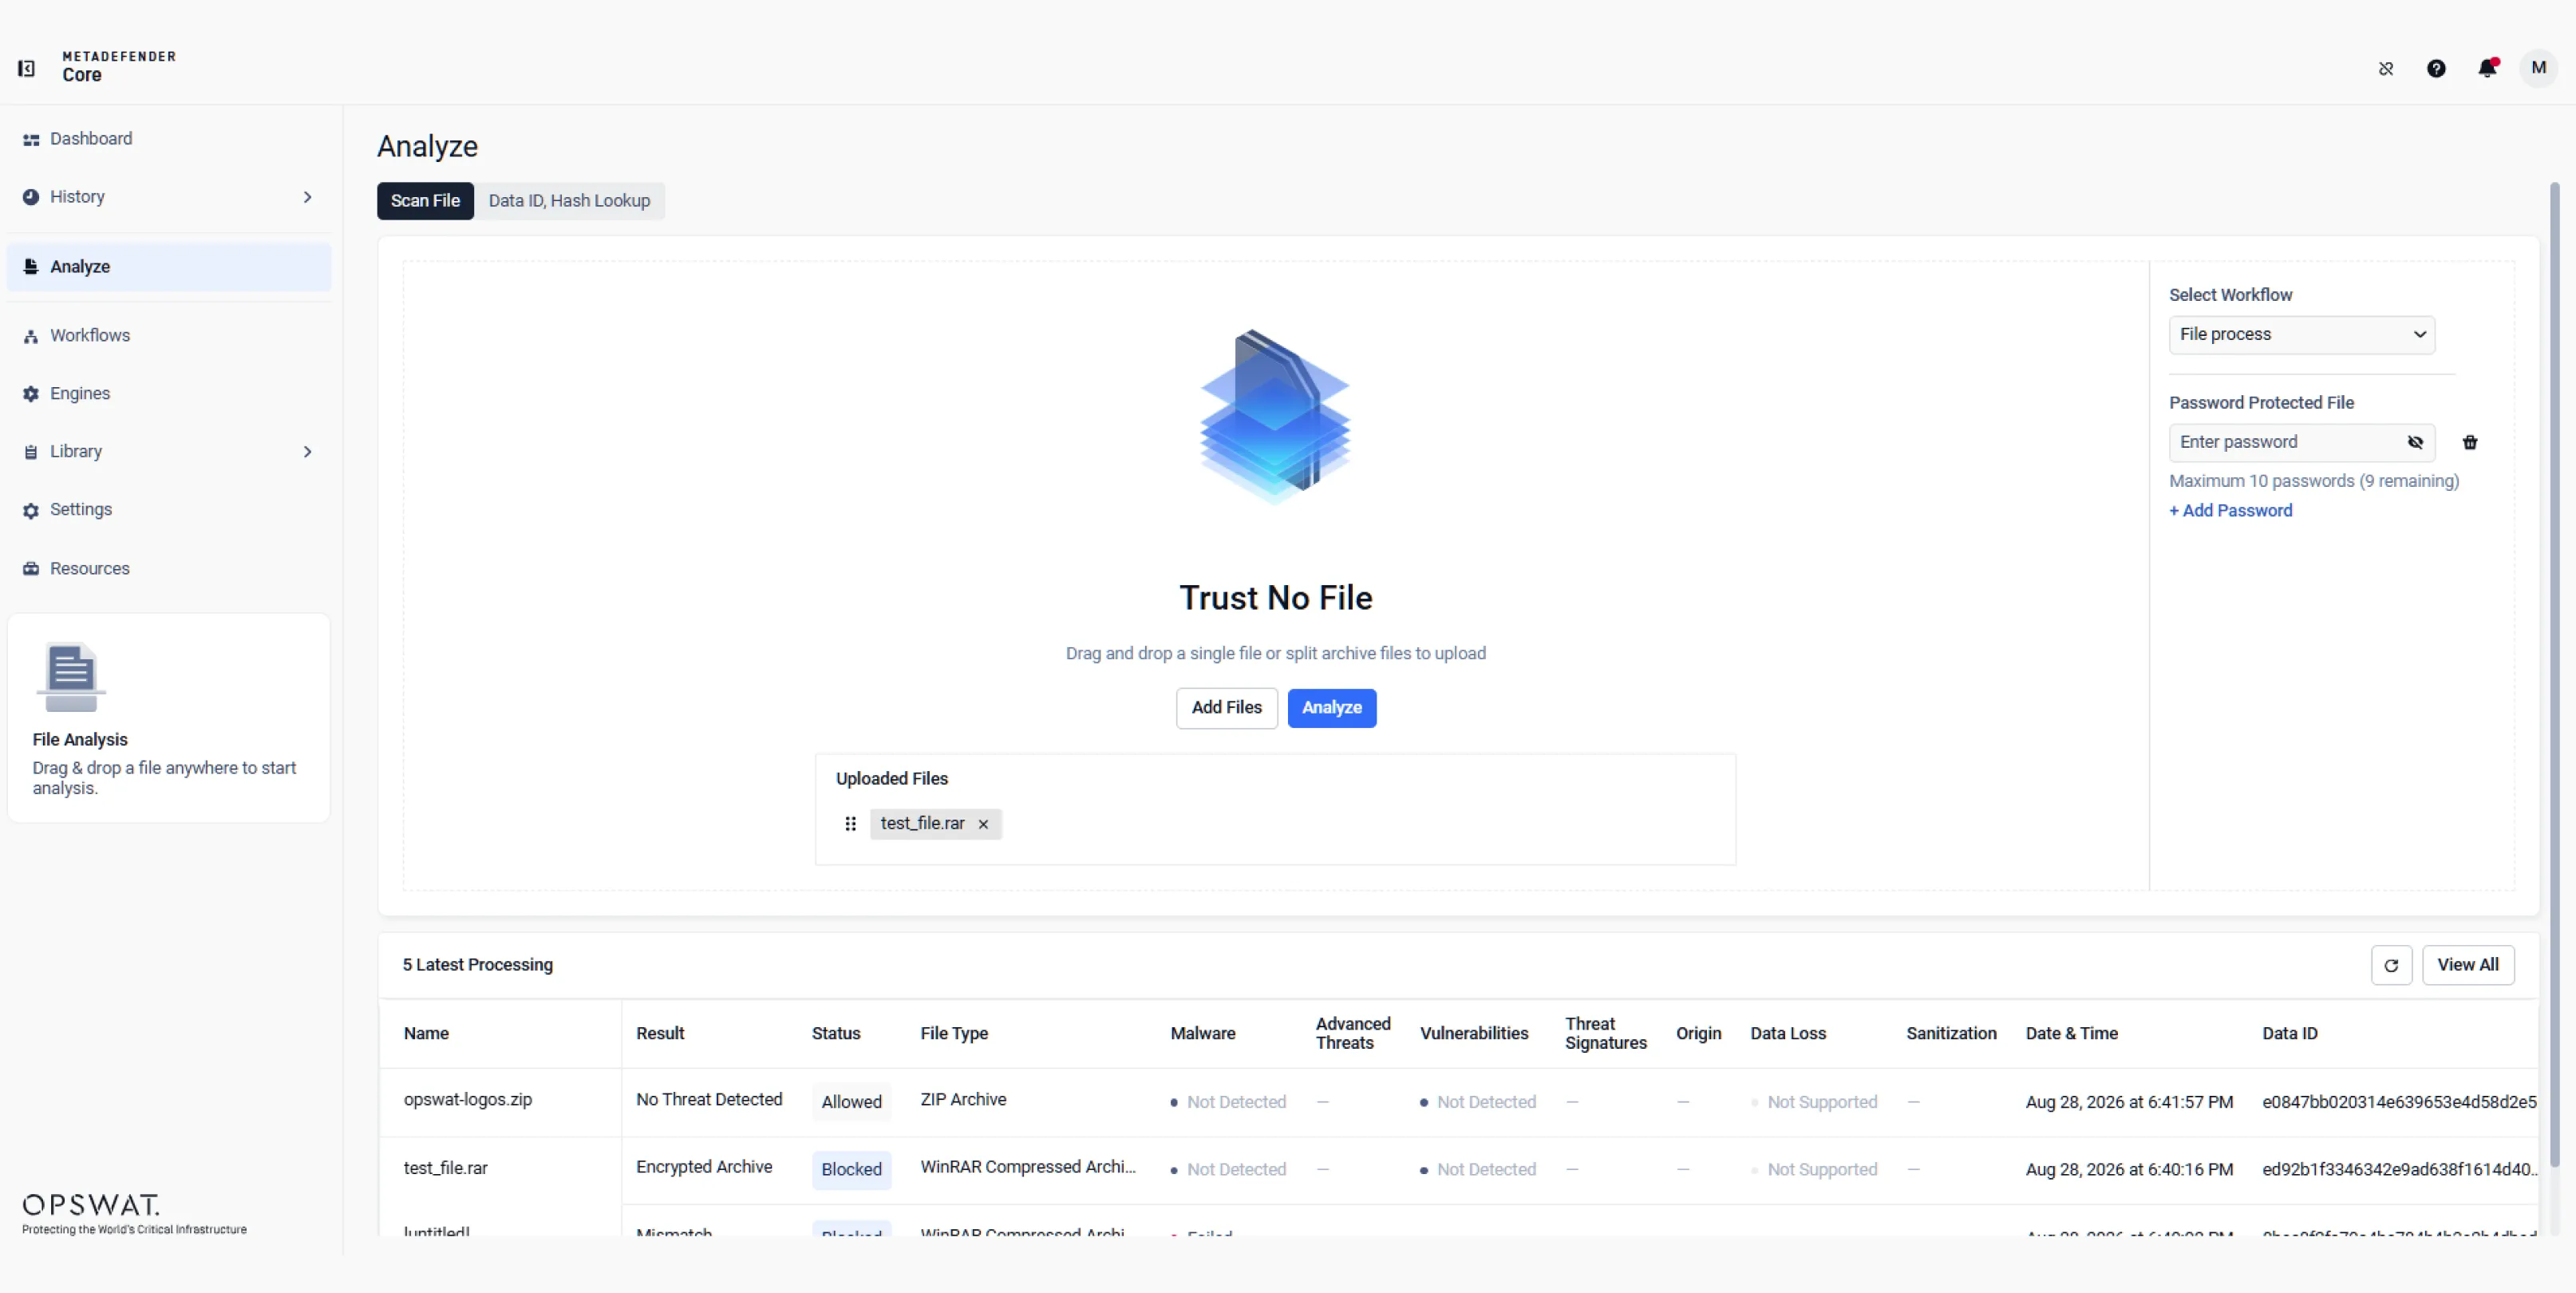
Select or upload a file, choose the desired workflow, and provide a password if required. Click Process to start scanning the file with the configured security engines.
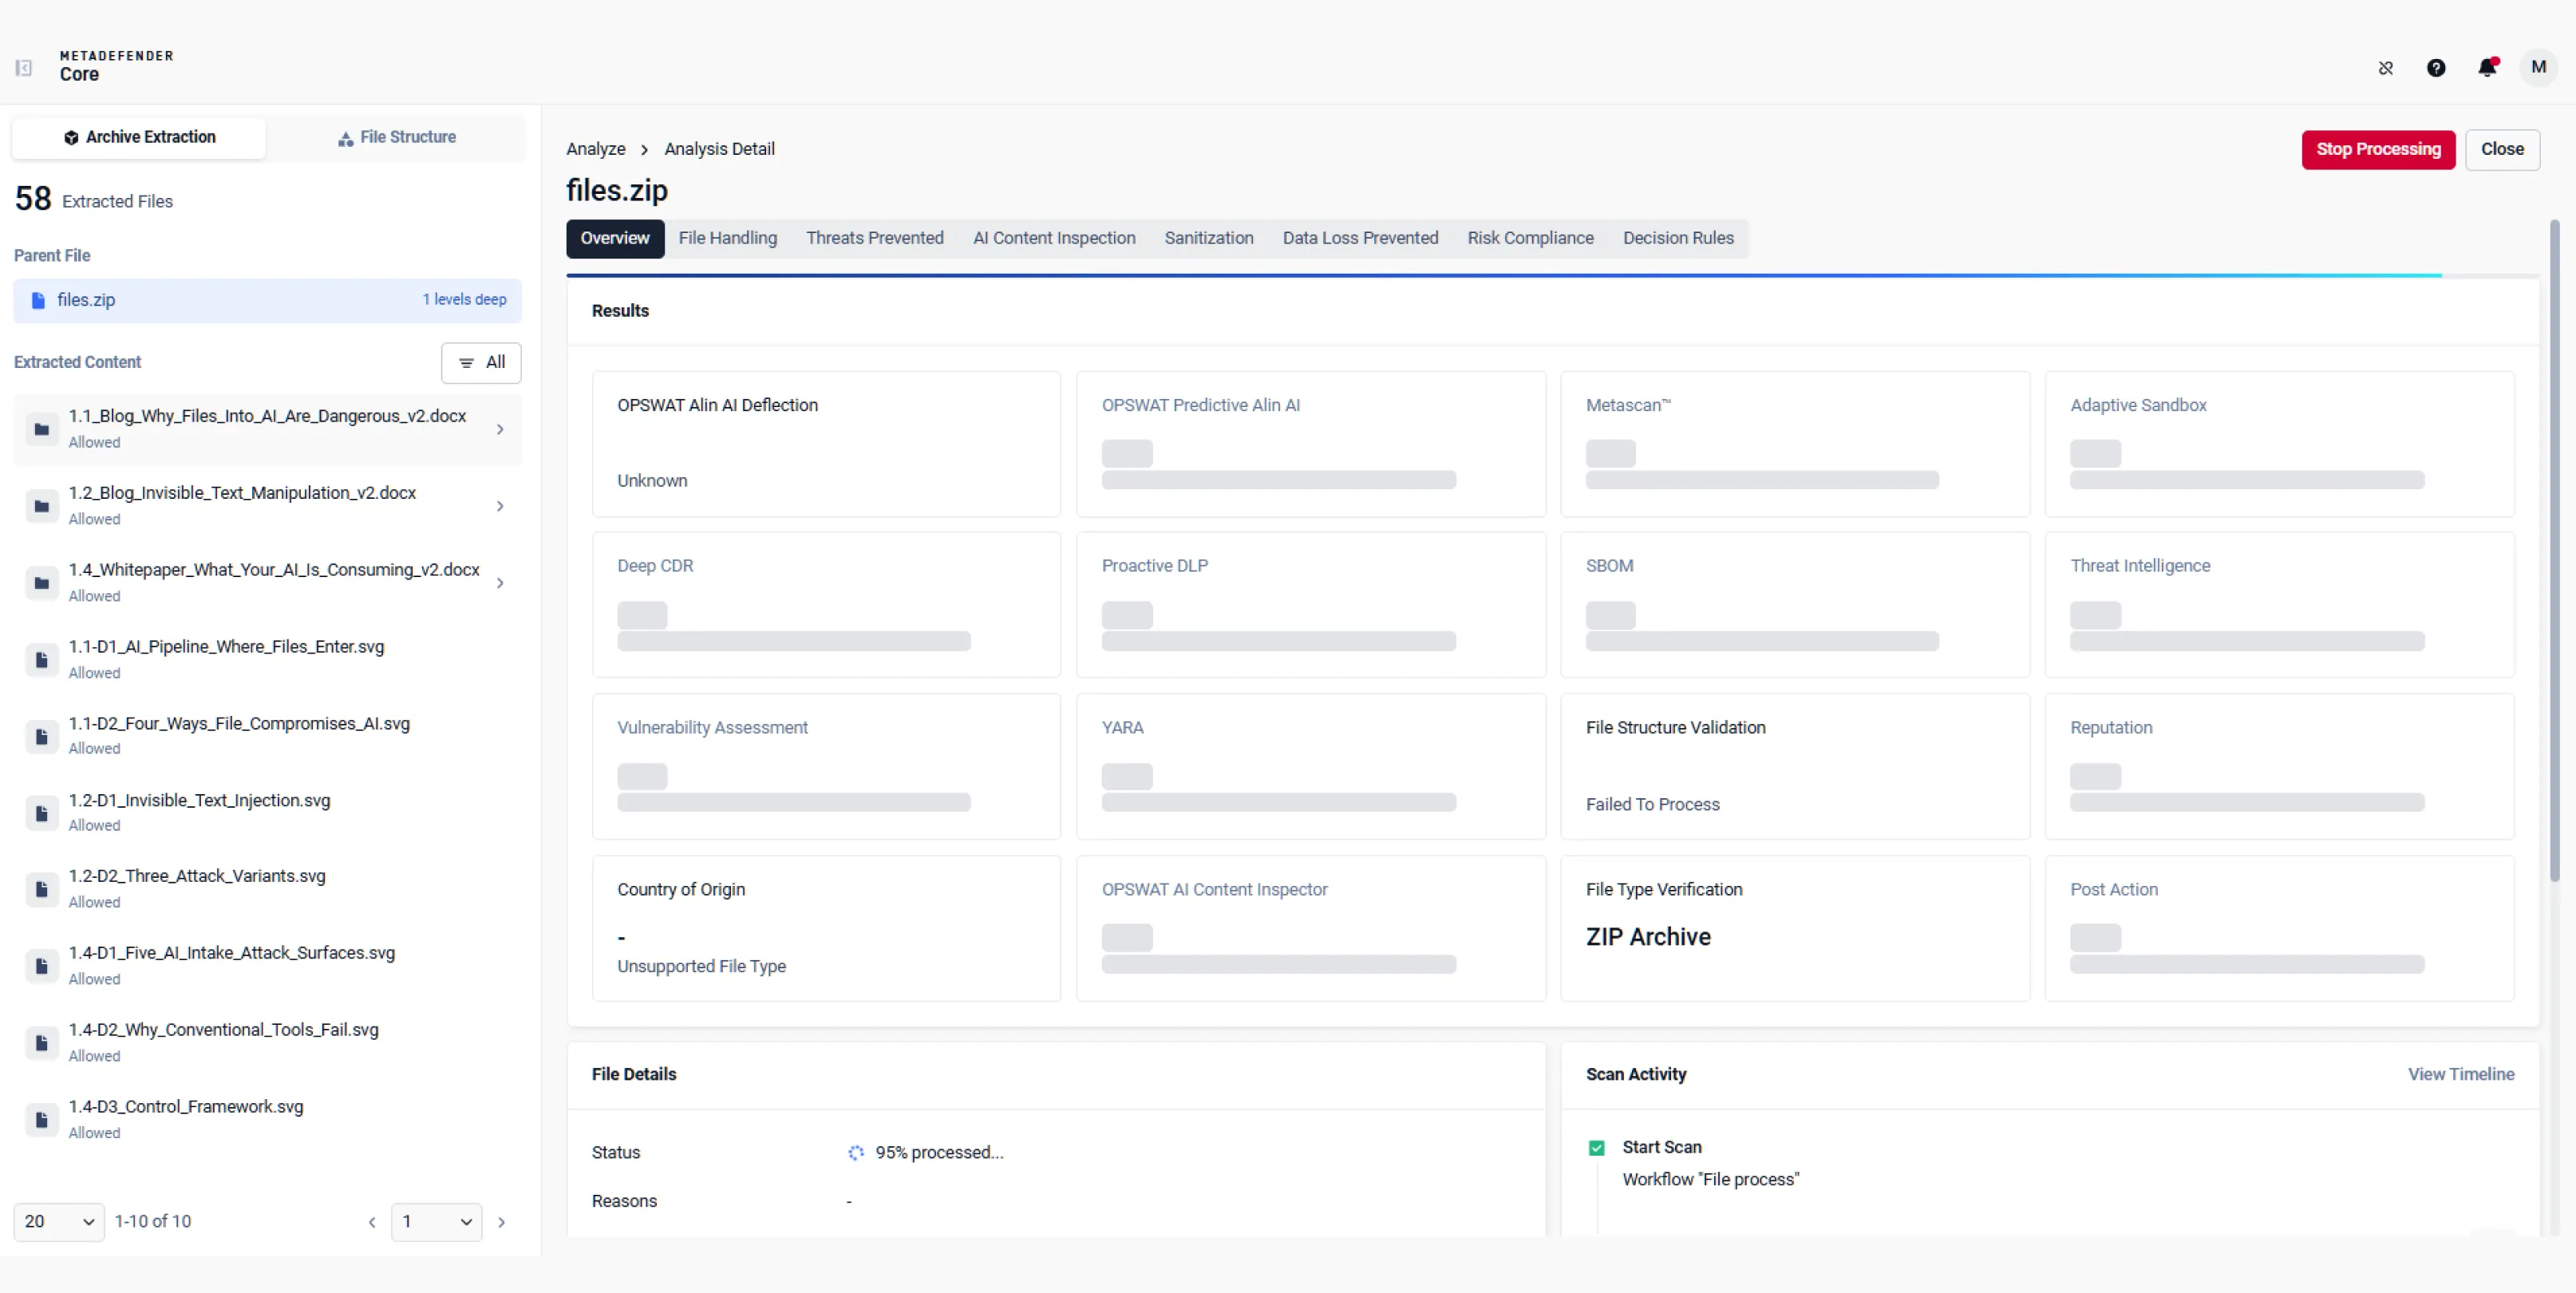
Files are going through different engines for malware and risk check. This process ensures that any potentially malicious content could not slip through the perimeter and reach end users.
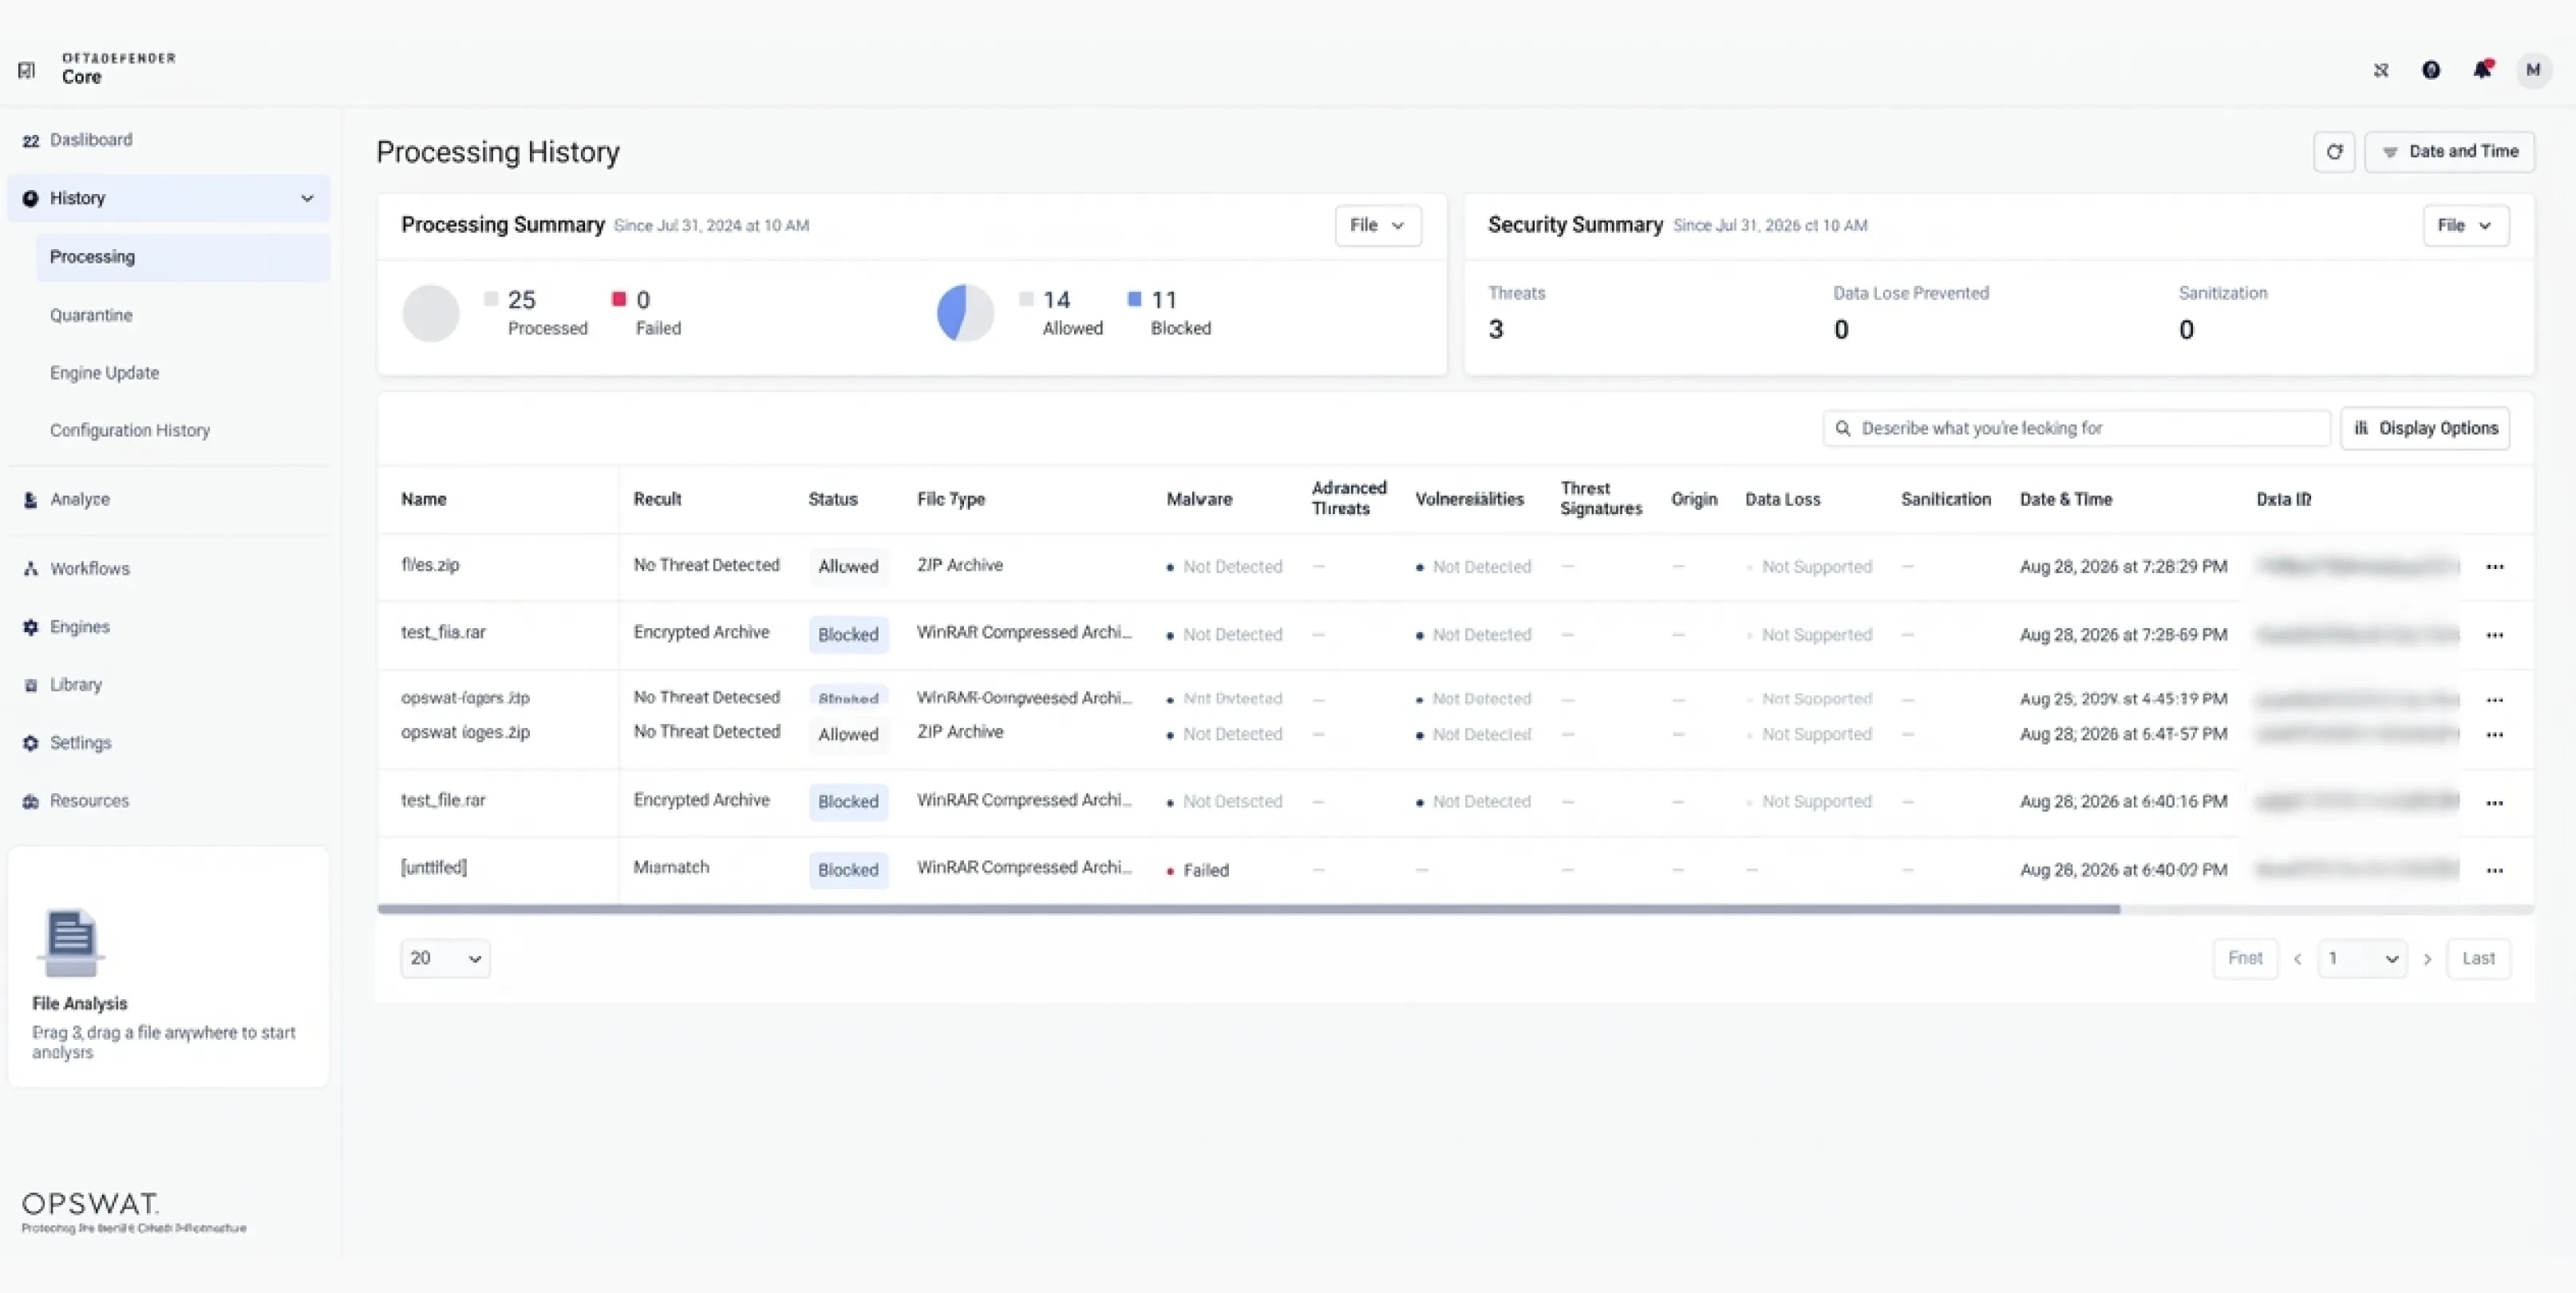
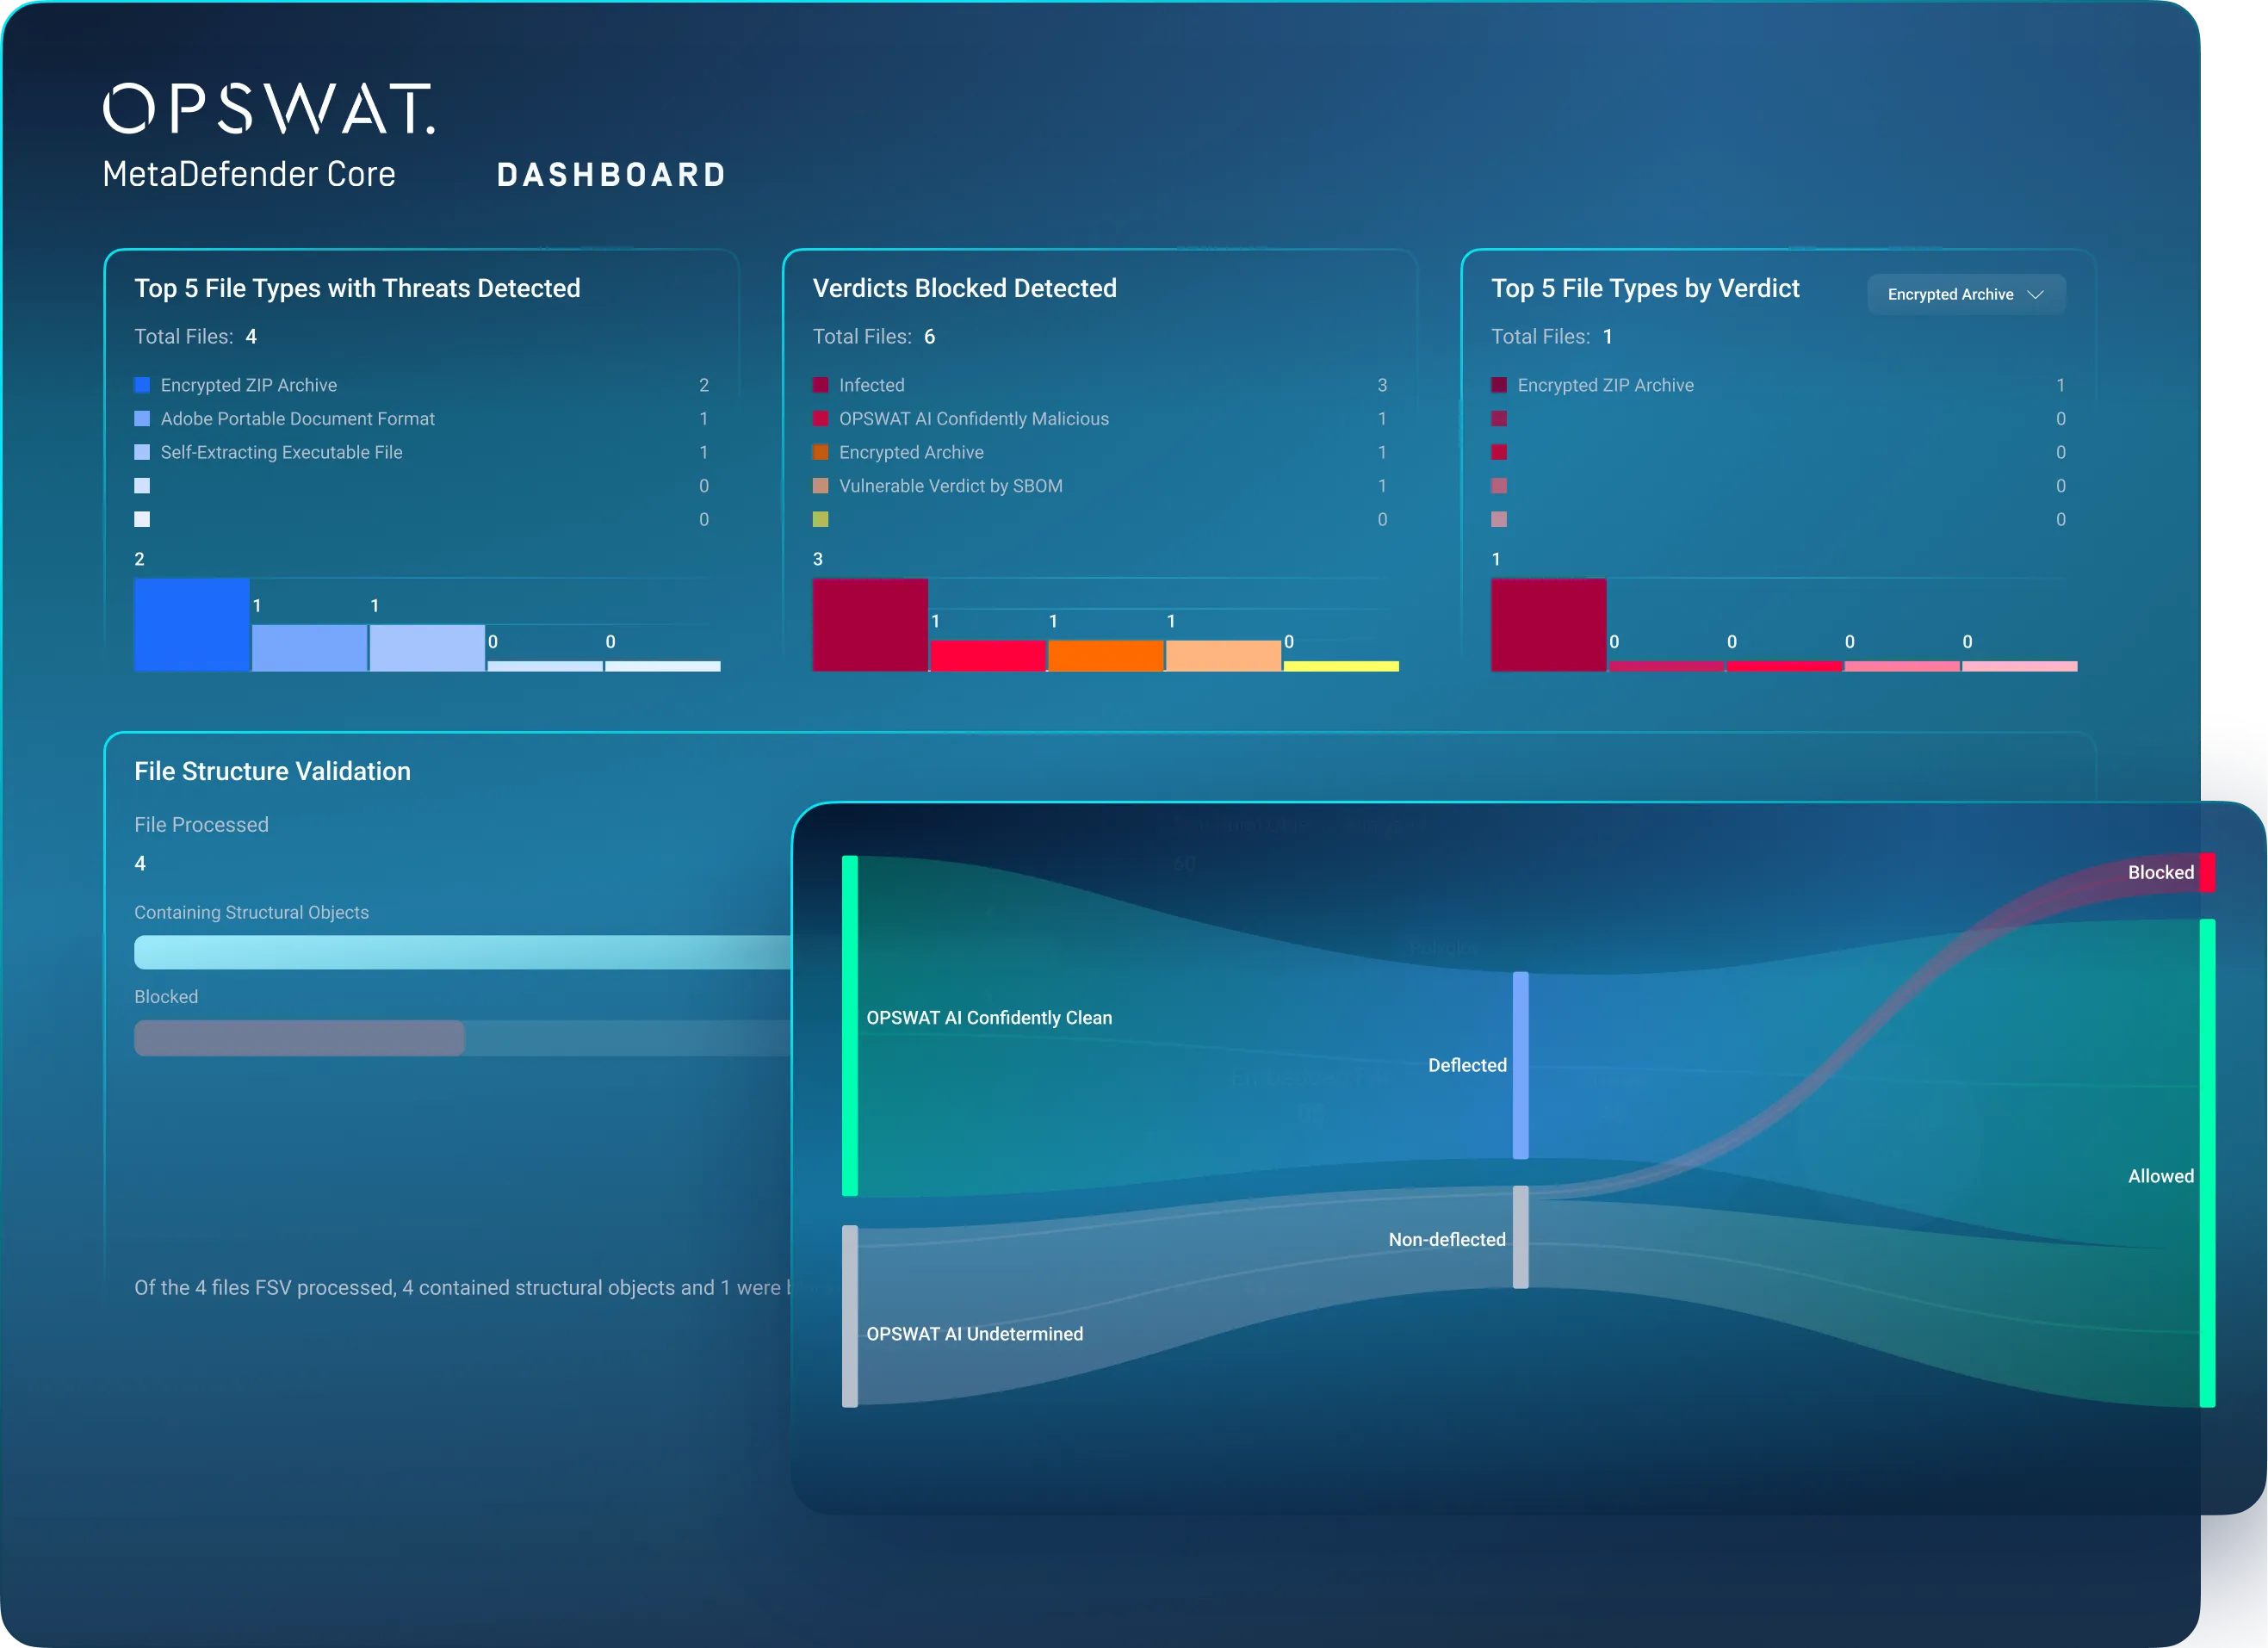
Monitor processed, allowed, blocked, and failed files. Search and filter results by file type, threat verdict, vulnerability, sanitization, origin, and processing time.
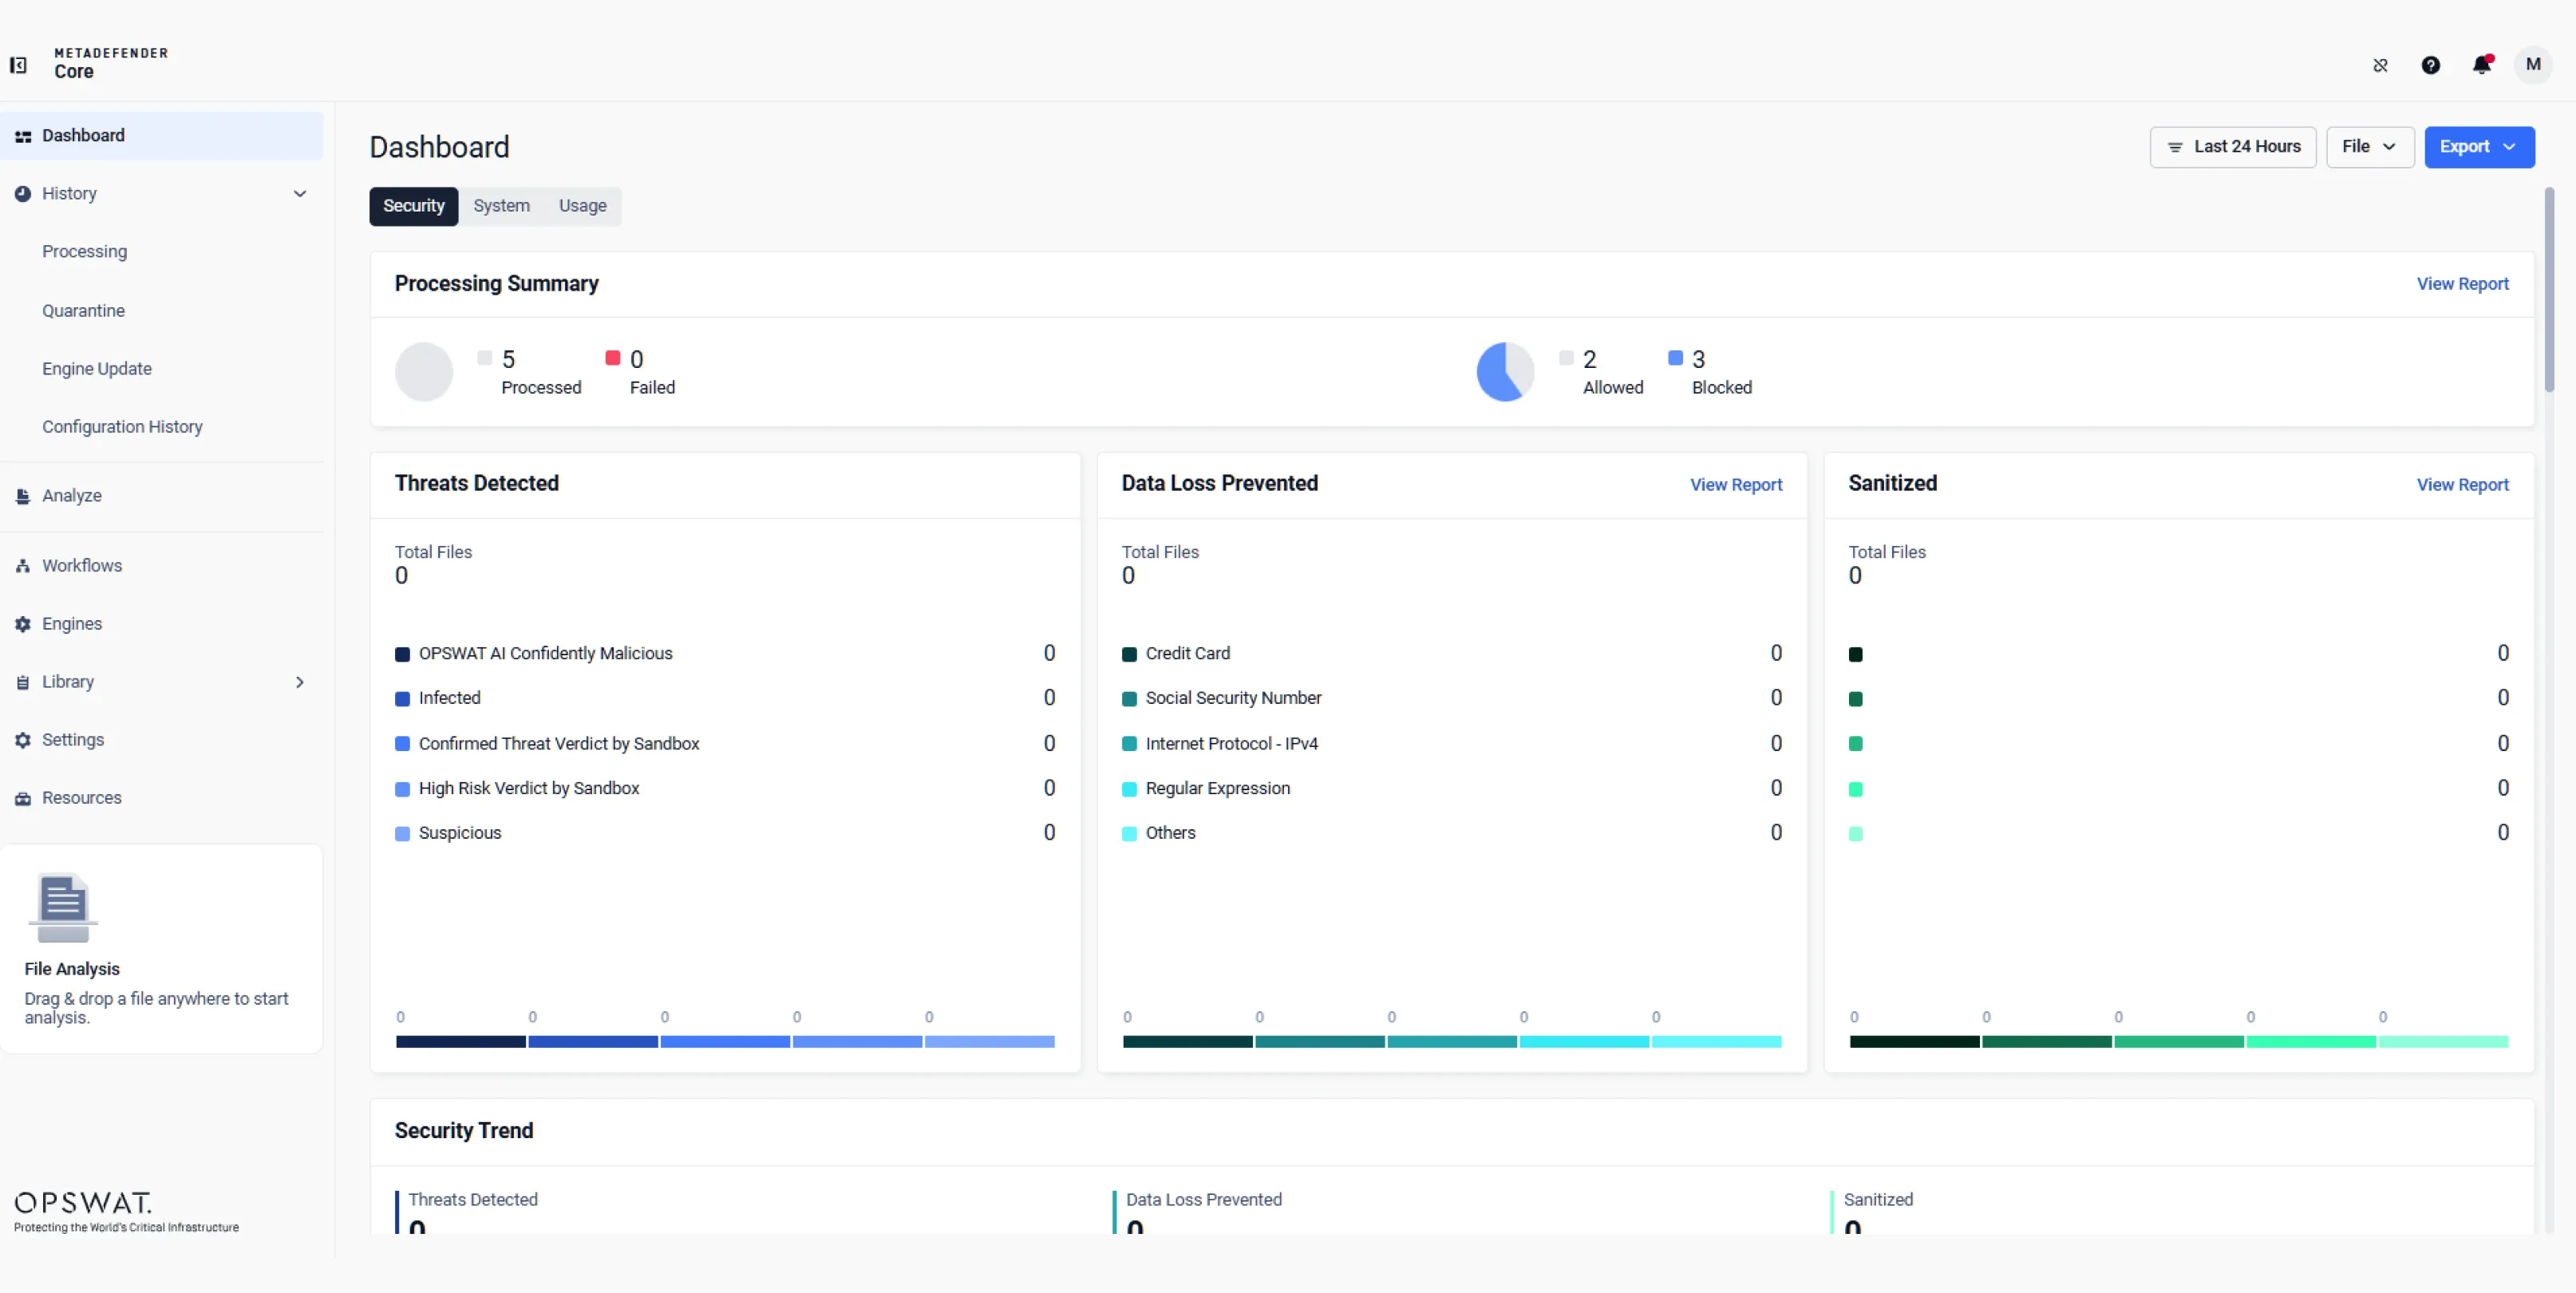
Explore Security reports for Threats Detected, Data Loss Prevented, Files Sanitized, CVE Trends, and Countries Detected, along with System health and Usage insights. Filter by time range and file type, review trends, and export results.
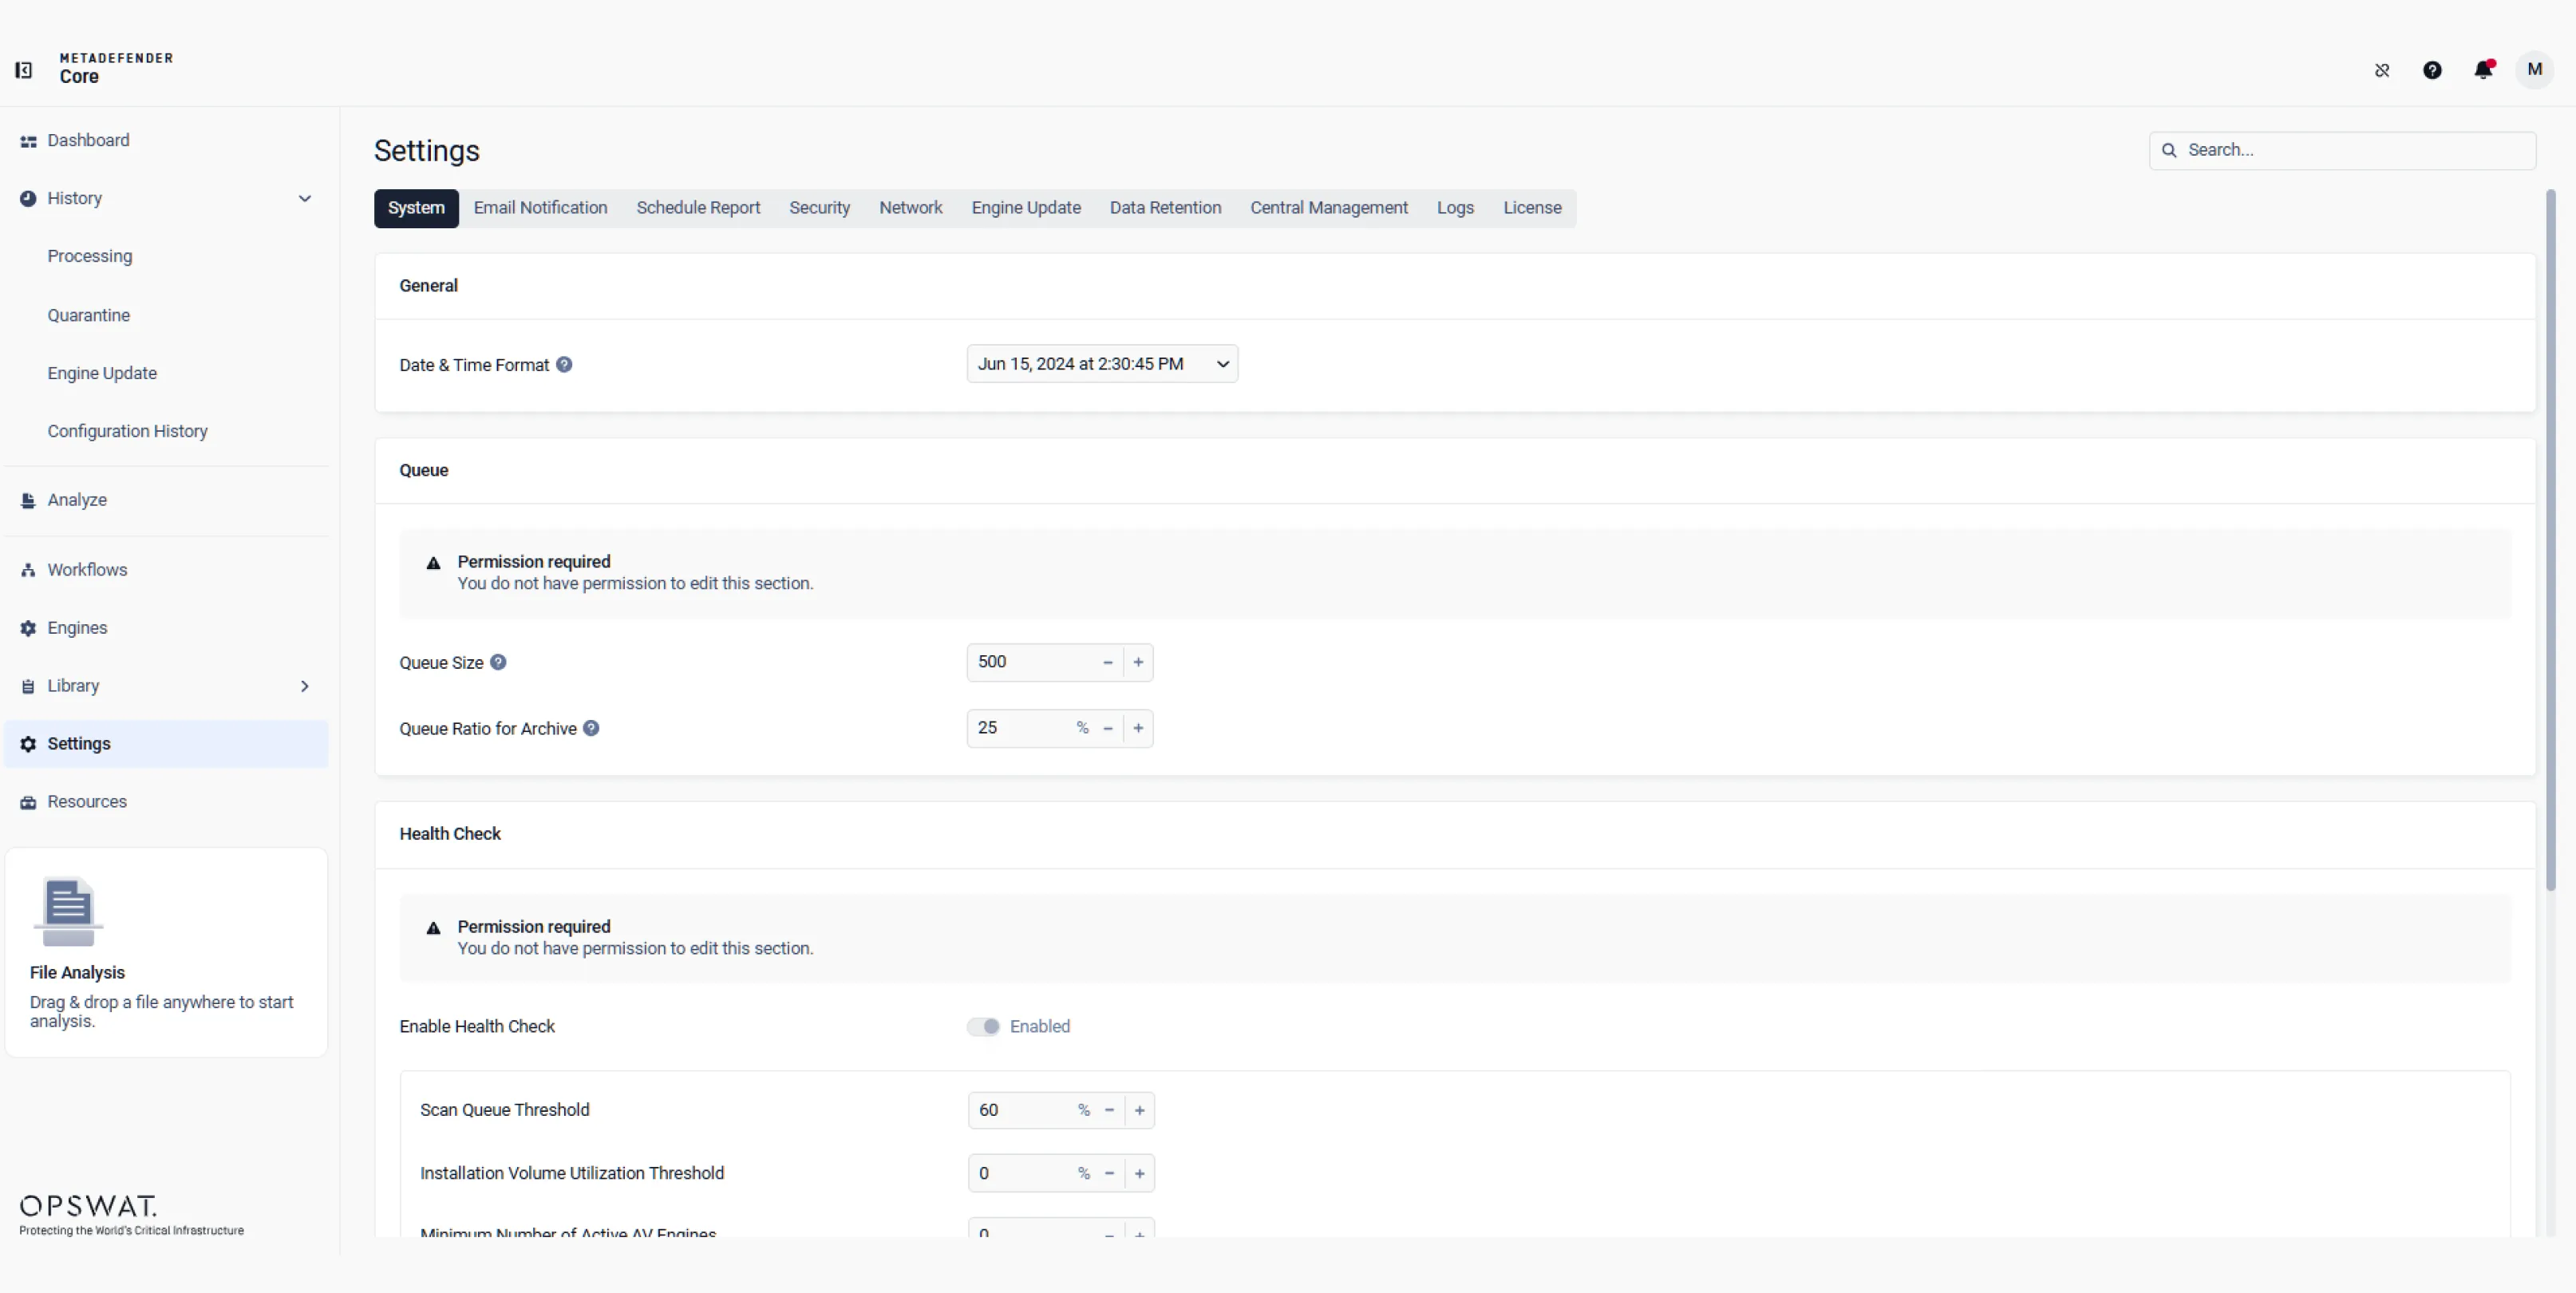
Configure system operations, email notifications, scheduled reports, security, network settings, engine updates, data retention, central management, logs, and licensing. Manage queue capacity and health thresholds to maintain reliable performance.
 Custom Workflow Management
Configure security aligned workflows to match your operational policies across email, file transfer, storage, or custom environments. Establish how files enter the system and how they are processed.
- Modular-Based Features
Use modular, layered detection and prevention engines, including Predictive Alin AI, Deep CDR™ Technology, Multiscanning, AI Content Inspector, Proactive DLP, Adaptive Sandbox and Threat Intelligence, to tailor file-processing flows to your operational needs and security requirements.
- Secure File Handling & Validation
Configure Archive Extraction, Compression, True File Type Detection, and File Structure Validation to ensure files are correctly identified, unpacked, processed, and verified before downstream analysis.
- Layered Threat Prevention & AI-Powered Detection
Combine Metascan, Predictive Alin AI, Threat Intelligence, Adaptive Sandbox, and Alin AI Deflection to identify known, unknown, and AI-generated threats through multi-engine scanning, reputation intelligence, behavioral analysis, and intelligent routing.
- AI Content & Fraud Detection
Configure AI Content Inspector to analyze text and images, identify AI-generated content, and detect potential fraud. Use its verdicts to assess risk before files enter critical workflows.
- Zero-Day Detection with Deep File Sanitization
Configure Deep CDR™ Technology to sanitize files by removing potentially malicious content and reconstructing safe, usable versions while preserving business-critical functionality before files enter downstream workflows.
- Sensitive Data Protection
Use AI-powered classification and pattern detection to identify and protect sensitive data. Configure rules to monitor file movement, reduce insider risk, and redact, block, or alert based on policy.
- SBOM Generation & Vulnerability Assessment
Analyze files, installers, and executables to generate an SBOM of components, versions, licenses, and dependencies. Identify known vulnerabilities and enforce risk-based policies before software enters critical environments.
- Decision Rules & Policy Enforcement
Configure YARA, Country of Origin, Reputation, Blocklist, Allowlist, and Post Action rules to evaluate file context and scan outcomes, then automatically allow, block, or route files according to policy.
- Uploading Files for Scanning
Select or upload a file, choose the desired workflow, and provide a password if required. Click Process to start scanning the file with the configured security engines.
- Concurrent Scanning with Multiple Engines
Files are going through different engines for malware and risk check. This process ensures that any potentially malicious content could not slip through the perimeter and reach end users.
- Processing History & Security Outcomes
Monitor processed, allowed, blocked, and failed files. Search and filter results by file type, threat verdict, vulnerability, sanitization, origin, and processing time.
- Security Reports & Trend Analysis
Explore Security reports for Threats Detected, Data Loss Prevented, Files Sanitized, CVE Trends, and Countries Detected, along with System health and Usage insights. Filter by time range and file type, review trends, and export results.
- System Configuration & Administration
Configure system operations, email notifications, scheduled reports, security, network settings, engine updates, data retention, central management, logs, and licensing. Manage queue capacity and health thresholds to maintain reliable performance.
AI-Powered Engines
100% Protection
of Deep CDR™ Technology Against Zero-Days and AI-Assisted Malware
Trusted by
2,100+
Organizations
Worldwide
99%+
Malware Detection Accuracy Across 30+ Anti-Malware Engines
200+ File Types and
30+ Archive Formats
#1 Market Leader
Complete File Trust With MetaDefender Core™
File Upload Security
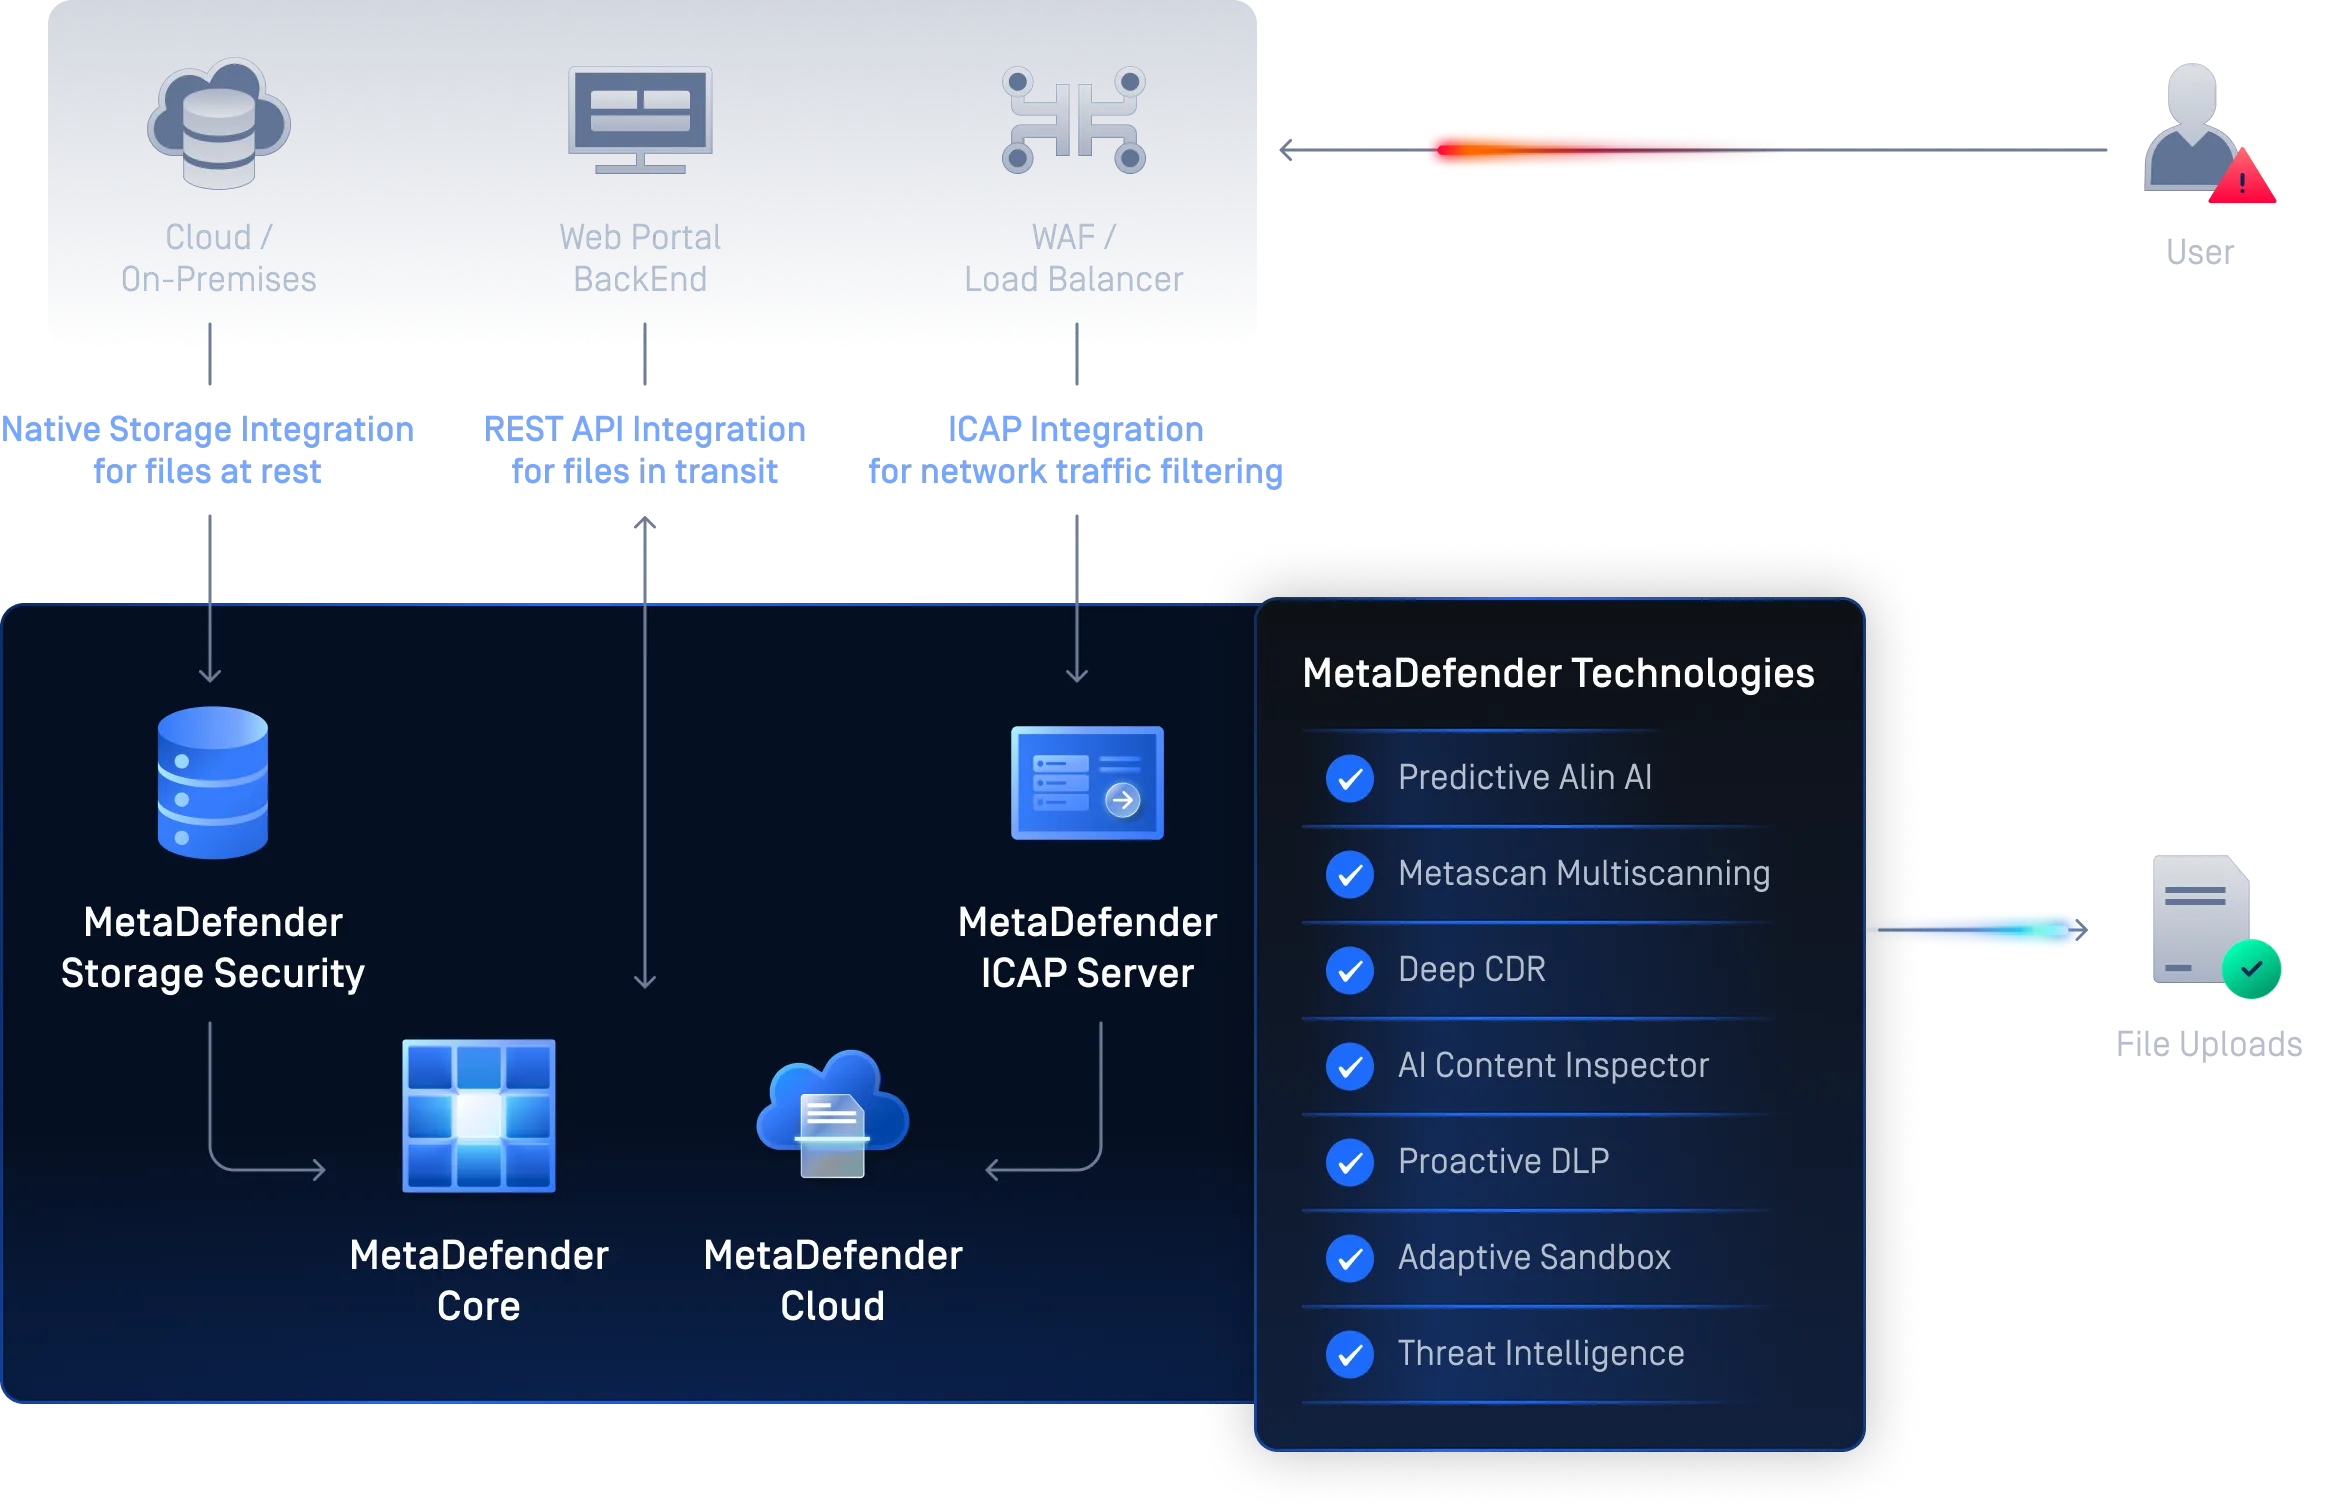
MetaDefender Core protects public portals and applications from file-borne threats by sanitizing every uploaded file with Deep CDR™ Technology and scanning in parallel with 30+ anti-malware engines. It applies zero-trust principles at the perimeter, detects spoofed file types, and inspects encrypted archives to prevent ransomware and data leakage without disrupting the user experience.
File Download Security
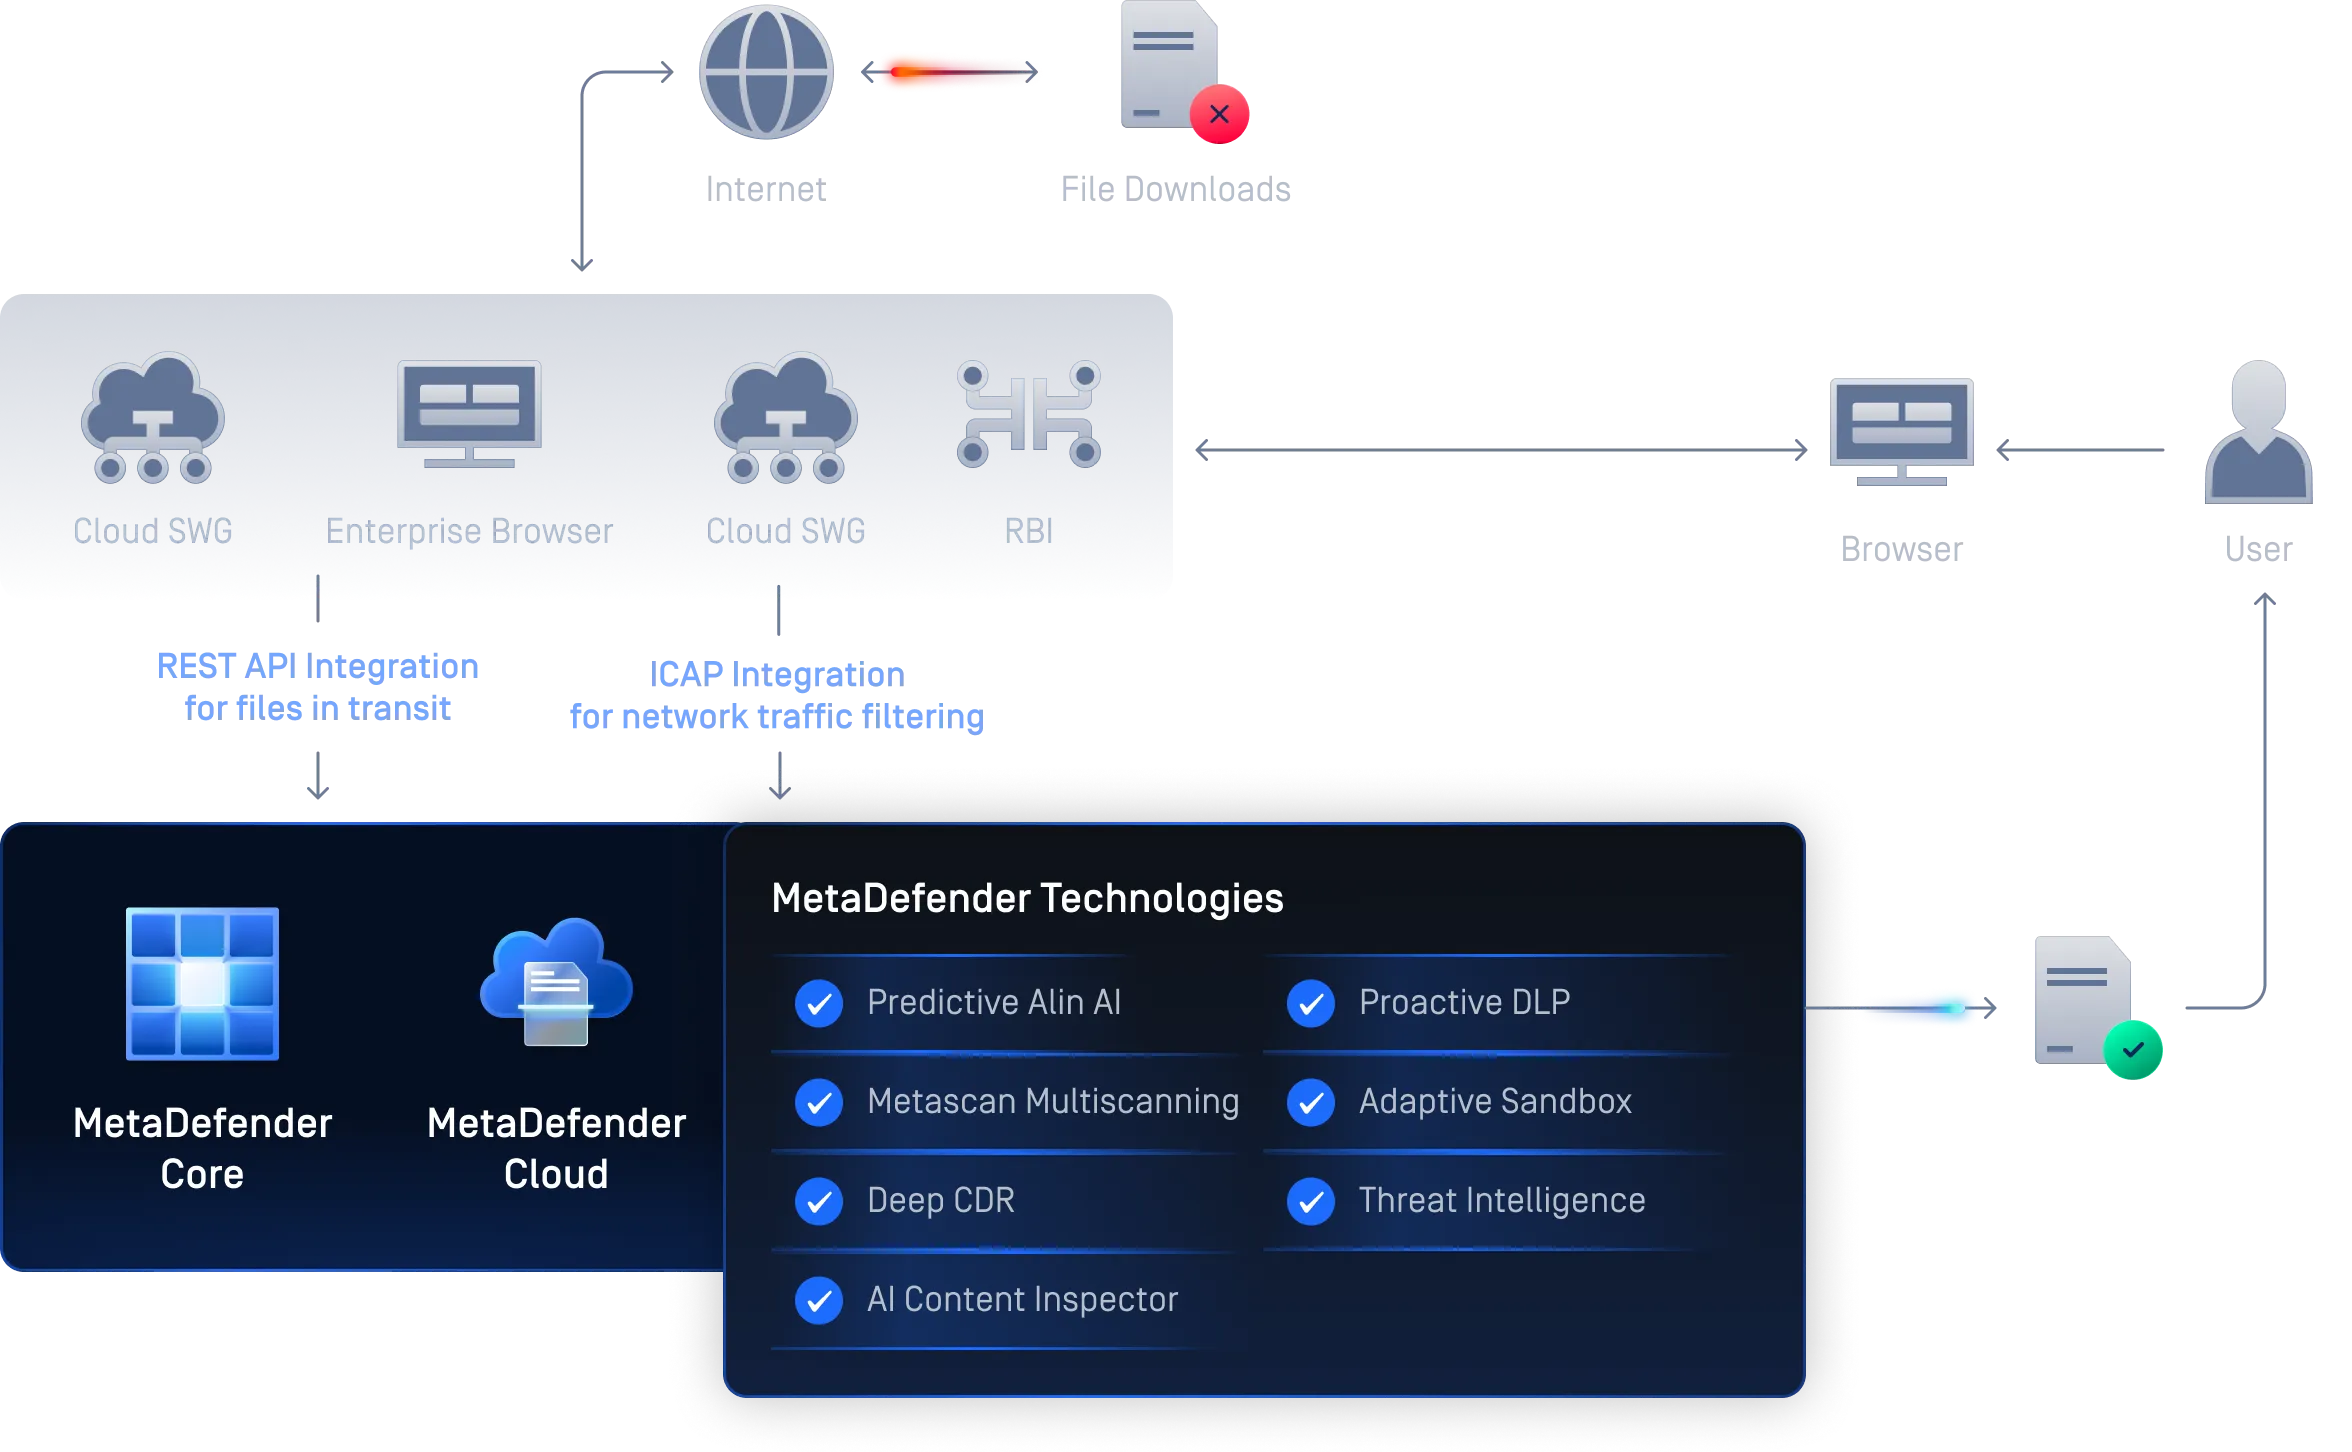
MetaDefender Core ensures downloads are free from potential malware across browsers and secure web gateways by applying deep file sanitization and multi-engine malware scanning before execution. It blocks disguised or evasive threats that standard filters miss, maintains productivity, and provides full audit visibility for compliance and investigation.
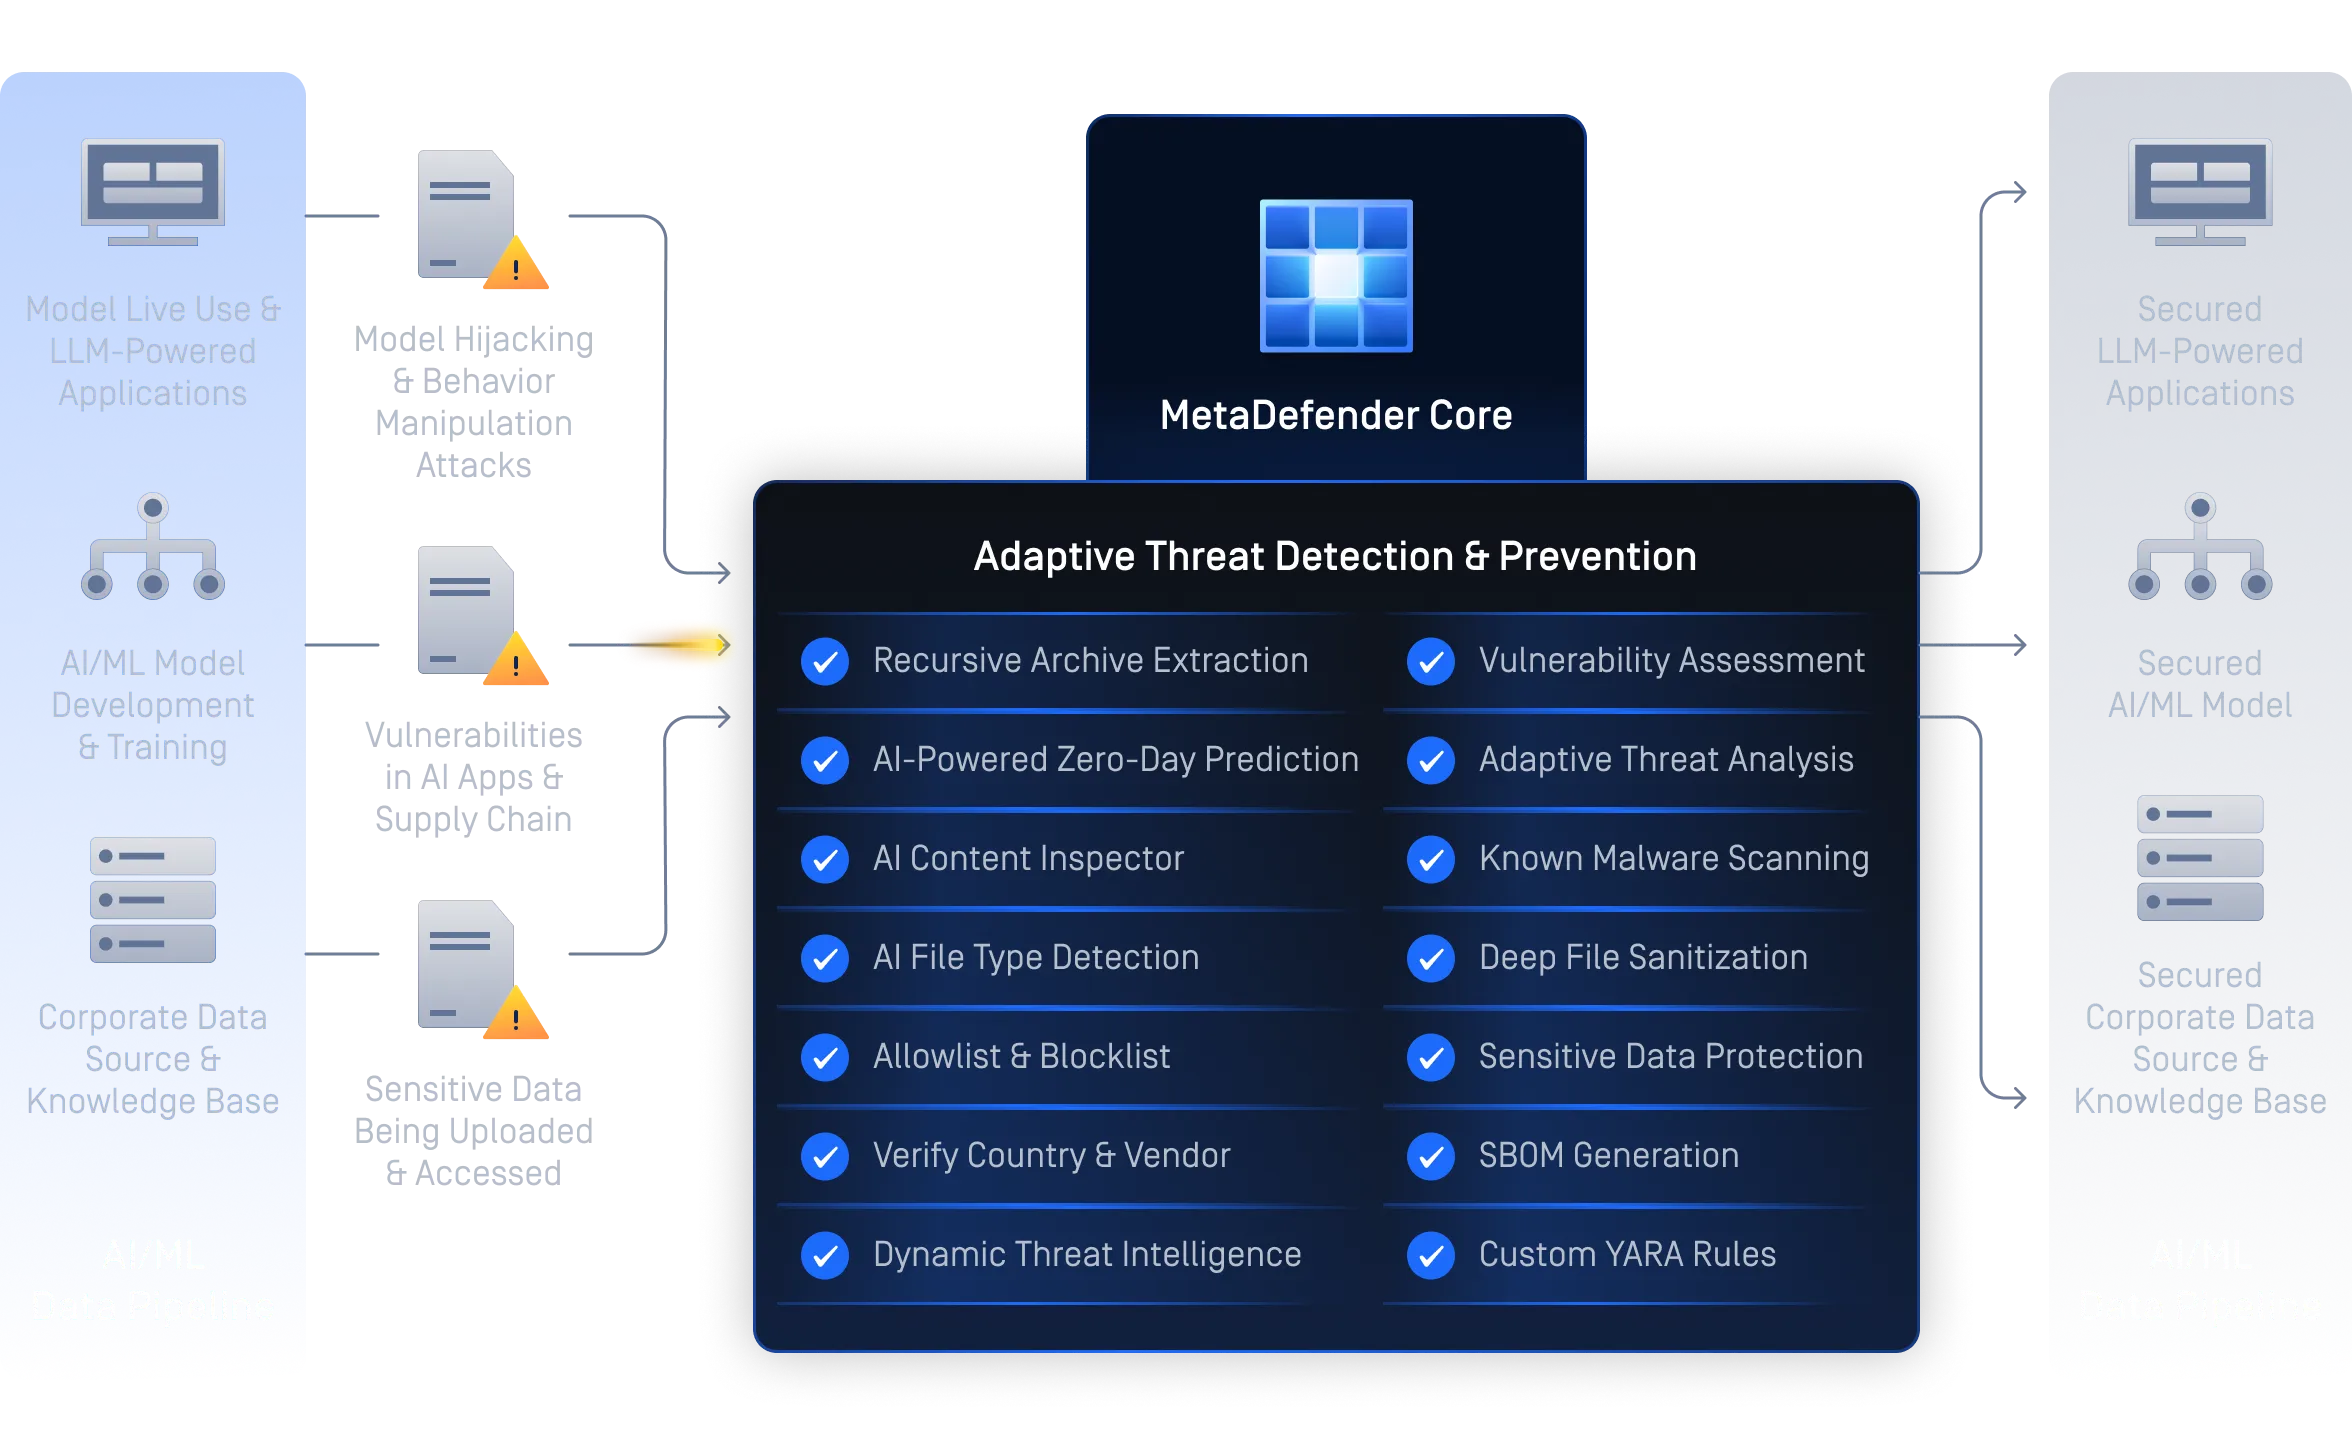
Secure AI and ML Data Pipeline
MetaDefender Core secures AI data pipelines and workflows by sanitizing and validating every dataset, model, and dependency before use. It detects malware and vulnerabilities in ML artifacts, generates SBOMs for software transparency, and applies Proactive DLP to protect sensitive data, enabling trusted and compliant AI development and deployment.
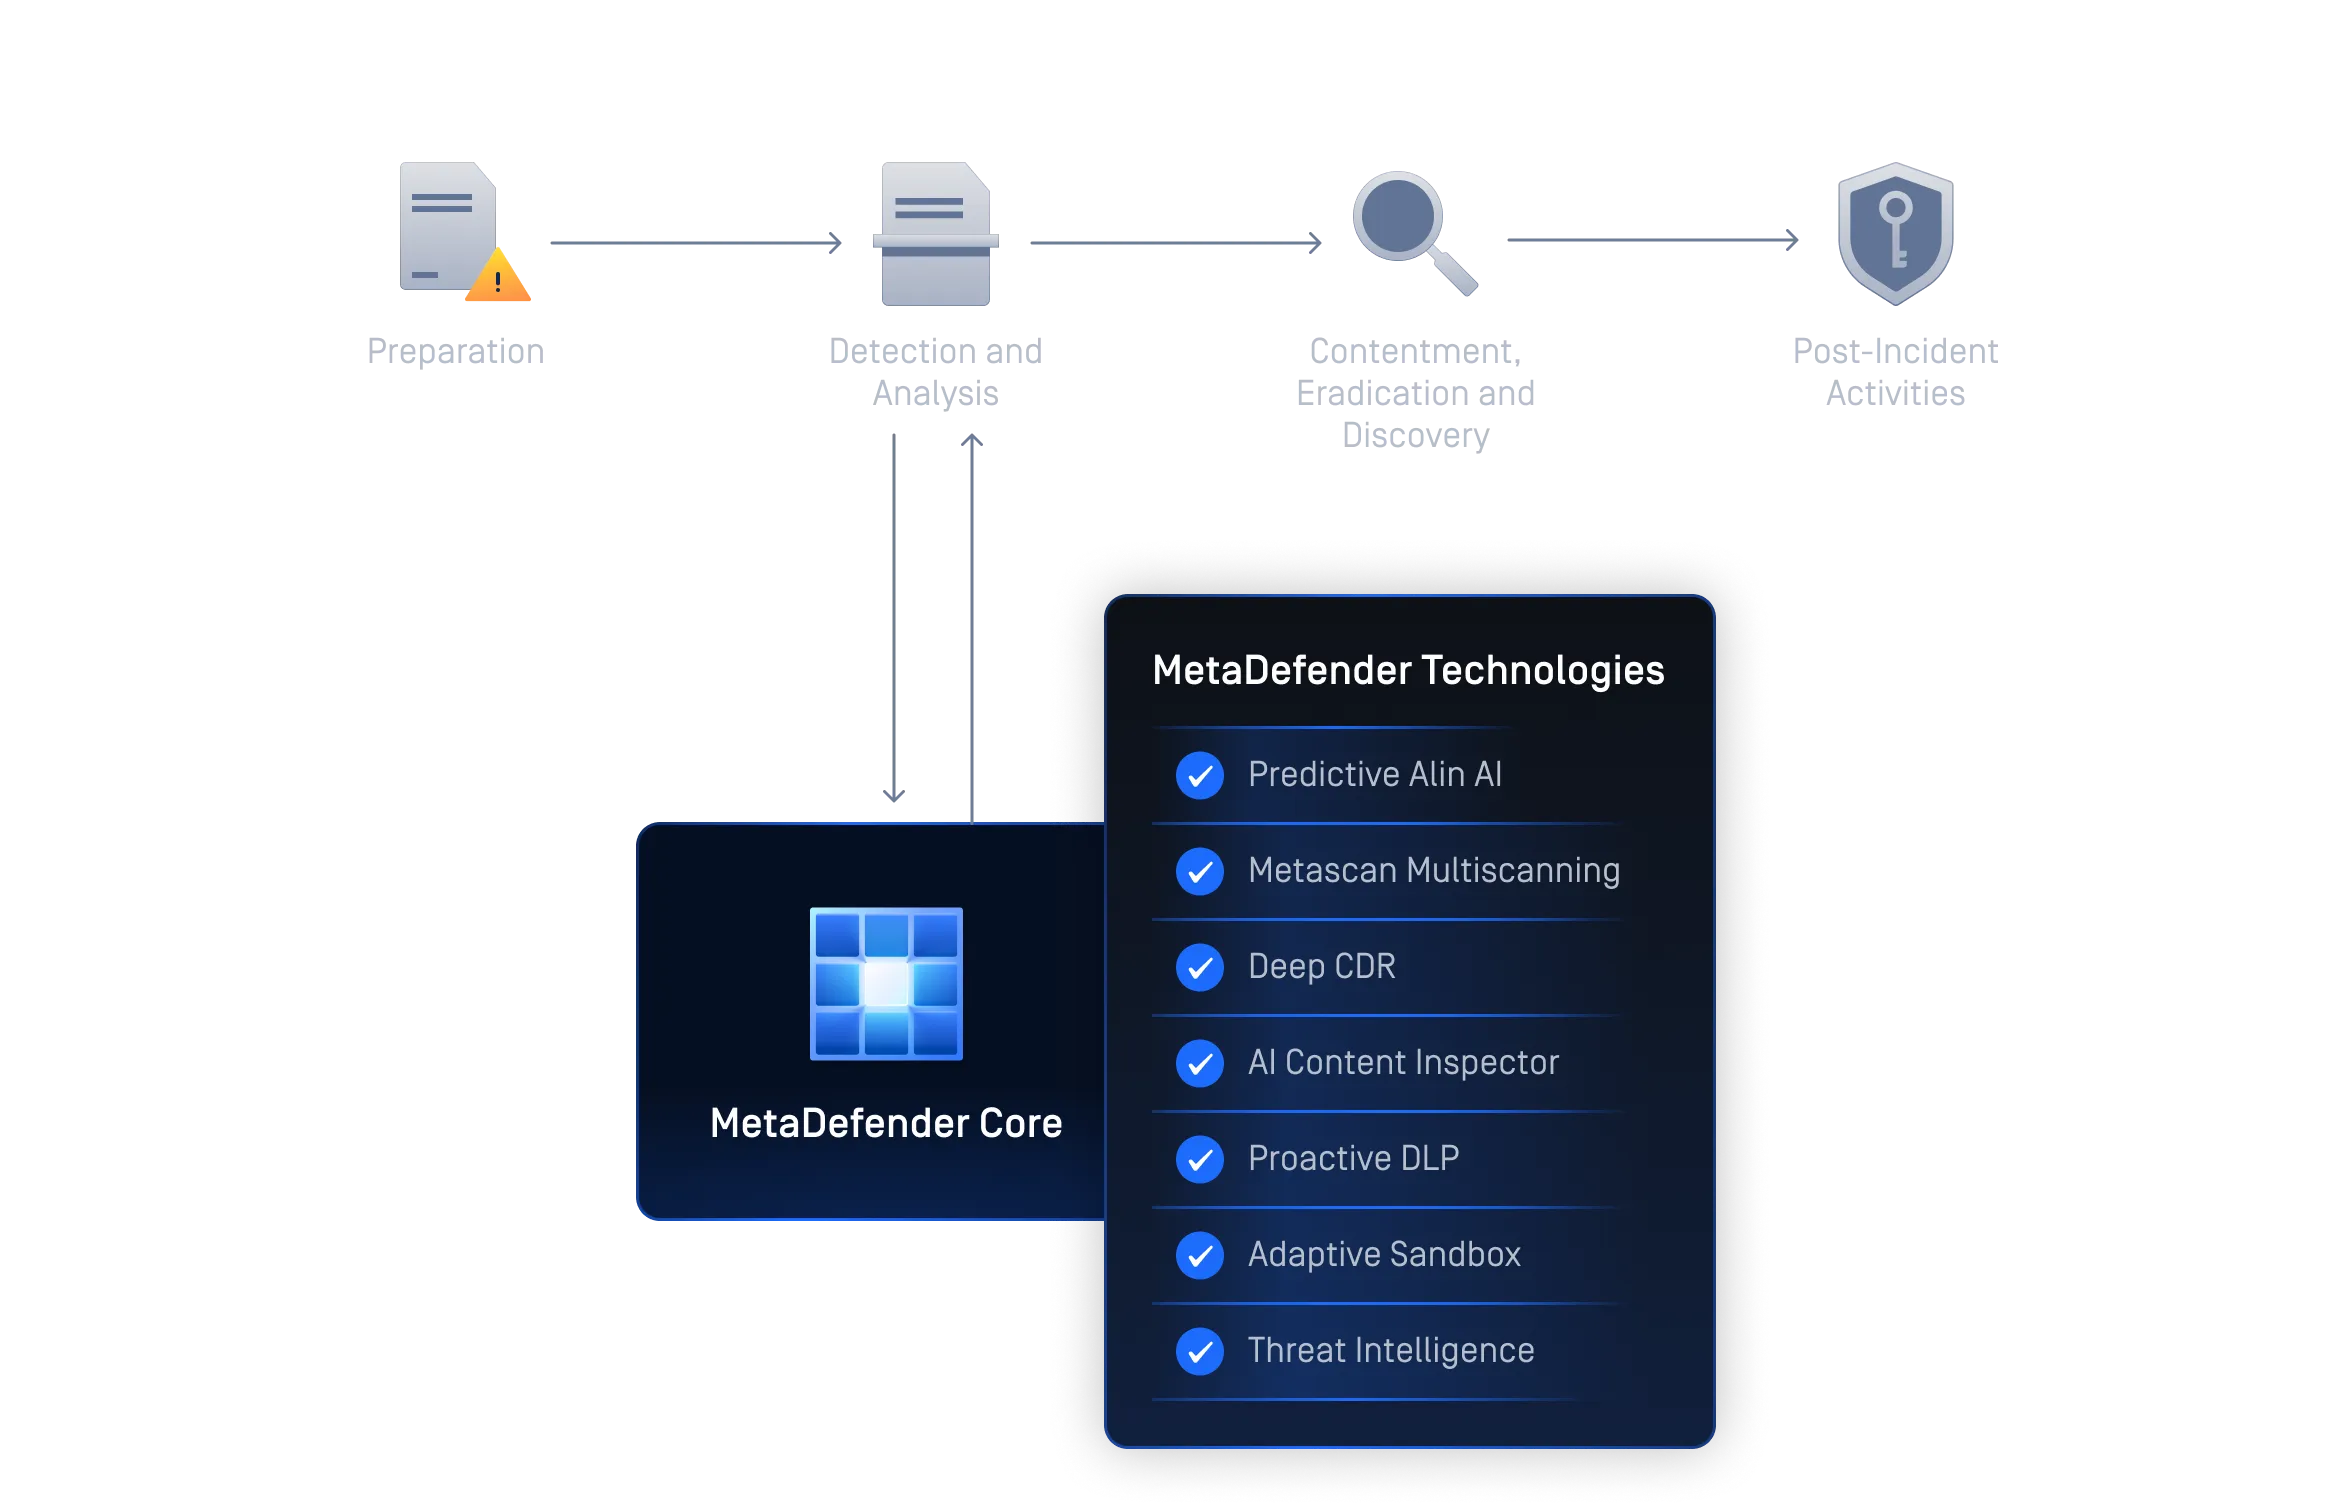
Secure Forensics Investigation for SOC Teams
Deploy Anywhere. Secure Everywhere.
Designed for complex and regulated environments, MetaDefender Core adapts to your architecture and security needs while maintaining performance, resilience, and compliance.
Virtual Machines
Ideal for high-security and controlled environments. Maintain full data sovereignty while ensuring predictable performance and centralized management.
Containers
Optimized for Kubernetes-native and containerized environments. Supports dynamic scaling and flexible orchestration for modern teams.
SaaS
Choose from flexible managed deployment options that scale with your needs, with minimal setup and no infrastructure overhead.
Distributed Cluster
Designed for large-scale or mission-critical environments. Provides parallel processing, high availability, and centralized control for uninterrupted security.
Proven Protection for the World’s Most Secure Environments
- “We believe that OPSWAT and FileZen S are indispensable to our city in order to conduct operations that are safe and do not compromise efficiency.”Sho SawadaChief of ICT Promotion Section , Planning and Finance Department, Muroran City Hall
- “OPSWAT’s was far superior compared to the sanitization engines proposed by other companies.”Kouji DaichoSenior Manager of the Information System Section, Digital Promotion Office, Fuji City
- By reducing triage times, minimizing resource requirements, and enhancing reliability through automation, the team can now more efficiently combat the evolving landscape of digital threats. This success story is a testament to the power of OPSWAT’s innovative spirit and how industry-leading technology is changing the fight against cybercrime. A Government’s Cybersecurity Specialist Engineering Manager for Systems Infrastructure, Genesis Energy
- “With OPSWAT we are confident that the sensitive data and information of our customers is secure.”Zahi Ben-AbuHead of Security and Infrastructure Communication, Clalit Health Services
Aid Compliance with Regulatory Requirements
Designed for regulated environments, MetaDefender Core enforces secure file handling and documentation practices aligned with major global standards. Boost your compliance posture without compromising business continuity.
Get Started in 3 Simple Steps

Connect with Our Experts
Review your cybersecurity goals, assess your current workflows, and find the best deployment plan for your environment. Fill out the form below to get started.
Integrate Seamlessly
MetaDefender Core integrates easily via REST API with portals, file shares, email systems, and DevOps pipelines.
Protect with Confidence
With MetaDefender Core, your environment gains continuous protection from file-borne threats using our market-leading Metascan Multiscanning, Deep CDR™ Technology, and Threat Intelligence technologies. Get in-depth analyses, comprehensive assessment reports, and actionable recommendations.
Recommended Resources
MetaDefender Core Datasheet
MetaDefender Core Product Brochure
MetaDefender Core for Secure Forensics Investigation
MetaDefender Core for Advanced Threat Intelligence for SOC Teams
MetaDefender Core for Secure AI Data Pipeline & LLM Applications
MetaDefender Core - The Platform Guide
0 results. Please try again.
