File-Based Vulnerability
Assessment
Detect known software vulnerabilities by directly analyzing files before applications, or libraries ever execute.
File-Based Vulnerability Assessment proactively identifies vulnerable software components at the file level,
closing security gaps left by traditional post-installation scanners.
- Pre-Installation Detection
- Binary-Level Insight
- Reduced Attack Surface
PatentedTechnologyU.S. 9749349 B1
2.5k
Supported Vendors
30k+
Associated CVEs With
Severity Information
3M
Identified Active
Vulnerable Hashes
Analyze
Executables and
Installers
Identify Risks Without System Footprint Reliance
Scan Rest-State and Running Applications
Traditional Vulnerability Scanning
Leaves Critical Gaps
Post-installation scanning and footprint-based detection miss vulnerabilities in software before deployment,
leaving systems exposed to potential threats.
Vulnerabilities Are Detected Too Late
Most scanners identify vulnerabilities only after software is installed and running, creating a window where attackers can exploit known weaknesses.
Incomplete Visibility Into Software Components
Traditional tools rely on system footprints, registry entries, or package managers that can be missing, altered, or intentionally hidden.
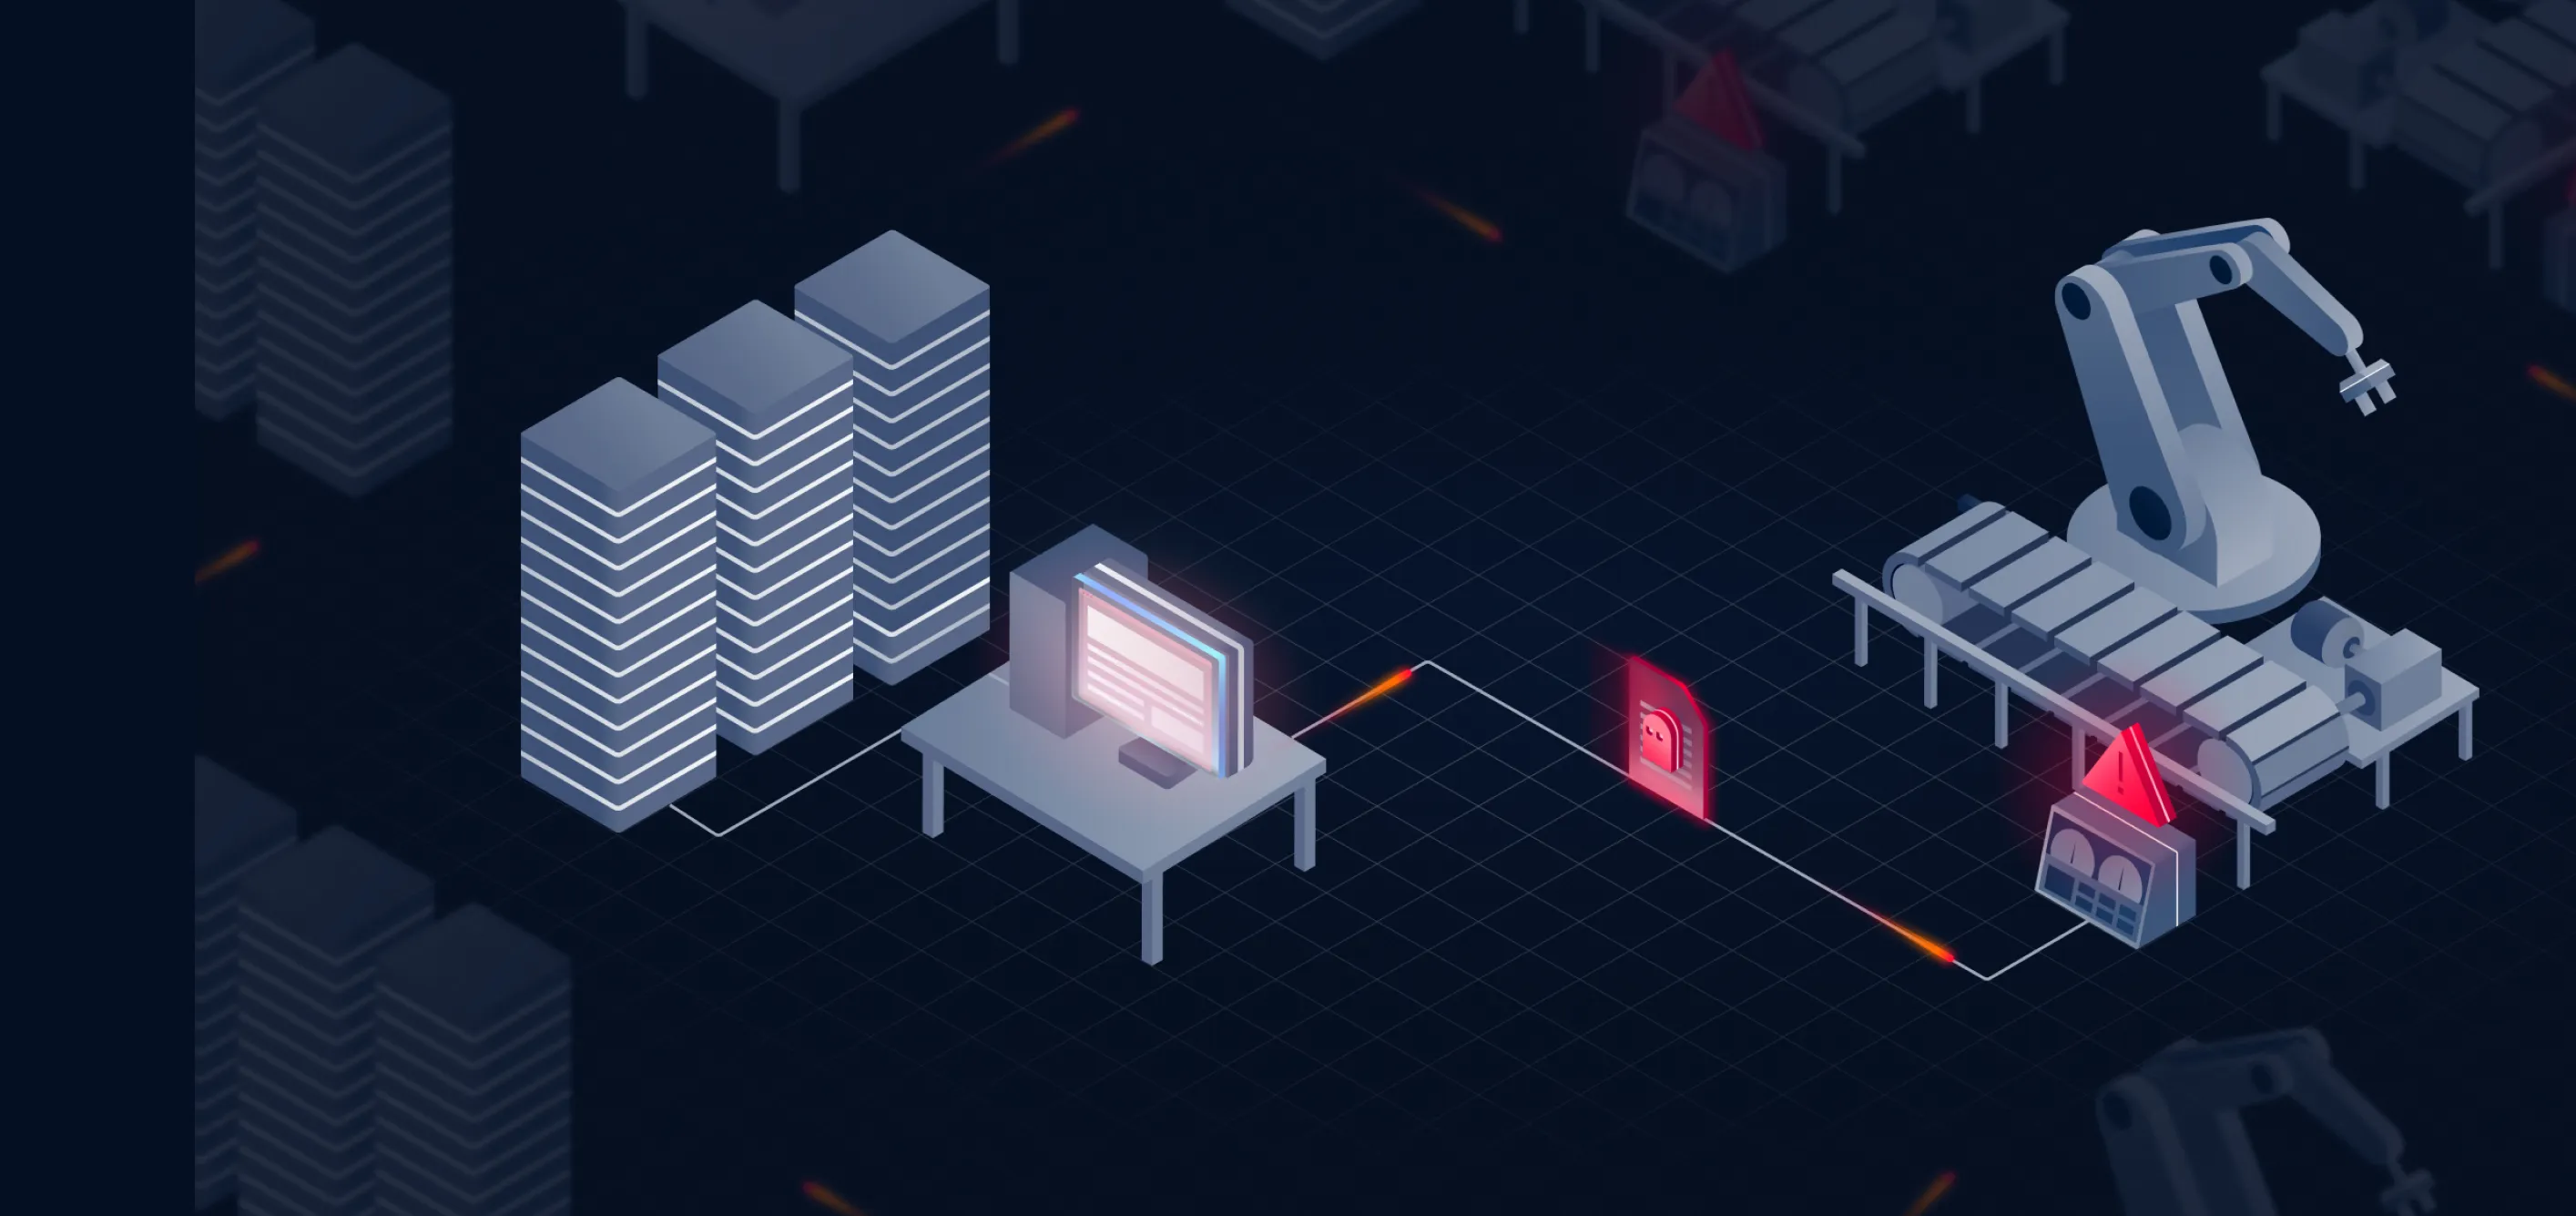
High Risk in Isolated and OT Environments
Air-gapped, OT, and critical infrastructure environments cannot afford vulnerable software entering networks undetected through removable media or updates.
- Late Detection
Vulnerabilities Are Detected Too Late
Most scanners identify vulnerabilities only after software is installed and running, creating a window where attackers can exploit known weaknesses.
- Incomplete Visibility
Incomplete Visibility Into Software Components
Traditional tools rely on system footprints, registry entries, or package managers that can be missing, altered, or intentionally hidden.
- High Risk
High Risk in Isolated and OT Environments
Air-gapped, OT, and critical infrastructure environments cannot afford vulnerable software entering networks undetected through removable media or updates.
Proactive Vulnerability Detection at the File Level
File-Based Vulnerability Assessment identifies vulnerable software by directly analyzing files before installation, execution, or network access.
Pre-Installation
Vulnerability Detection
Scan files before deployment to identify known vulnerabilities and prevent risky software from entering environments in the first place.
Binary-Level Software
Intelligence
Analyze executables, installers, and libraries directly—without relying on installed software footprints or system state.
Protection for High-
Security Environments
Secure air-gapped, OT, and critical systems by assessing files before they reach isolated networks.
How File-Based Vulnerability Assessment Works
OPSWAT analyzes files directly and correlates them with known vulnerabilities using advanced software intelligence.
Key Features
Pre-Execution Vulnerability
Detection
Stops vulnerable software before it executes, significantly reducing exposure and eliminating blind spots left by post-installation scanning.
Footprint-Independent Analysis
Detect vulnerabilities without relying on registry entries, package managers, or installed software artifacts.
Broad File Format Coverage
Supports a wide range of binaries, including applications, installers, and shared libraries.
Deploy Anywhere, Integrate Everywhere
Scalable, comprehensive file security solution that integrates seamlessly and follows your files wherever they go.
Cloud
Scalable vulnerability assessment delivered through OPSWAT cloud services.
On-Prem
Ideal for regulated, air-gapped, or high-security environments.
Hybrid
Flexible deployment combining cloud and on-premises controls.

OPSWAT Works Where You Work
Prevent threats and zero-day attacks with easy to deploy, integrate, and maintain solutions that fit into your existing technology stack. Integrate via REST API or native connectors to support a variety of deployment scenarios. We offer solutions for cloud-native, containerized, and locally hosted applications.