OPSWAT Research Center
Your View Into Malware Research & Detection Insights
Explore reports and blogs on zero-day detection, Deep CDR™ Technology, anti-malware market share, and package efficacy—powered by OPSWAT malware telemetry, threat research, and real-world security analysis.
Reports
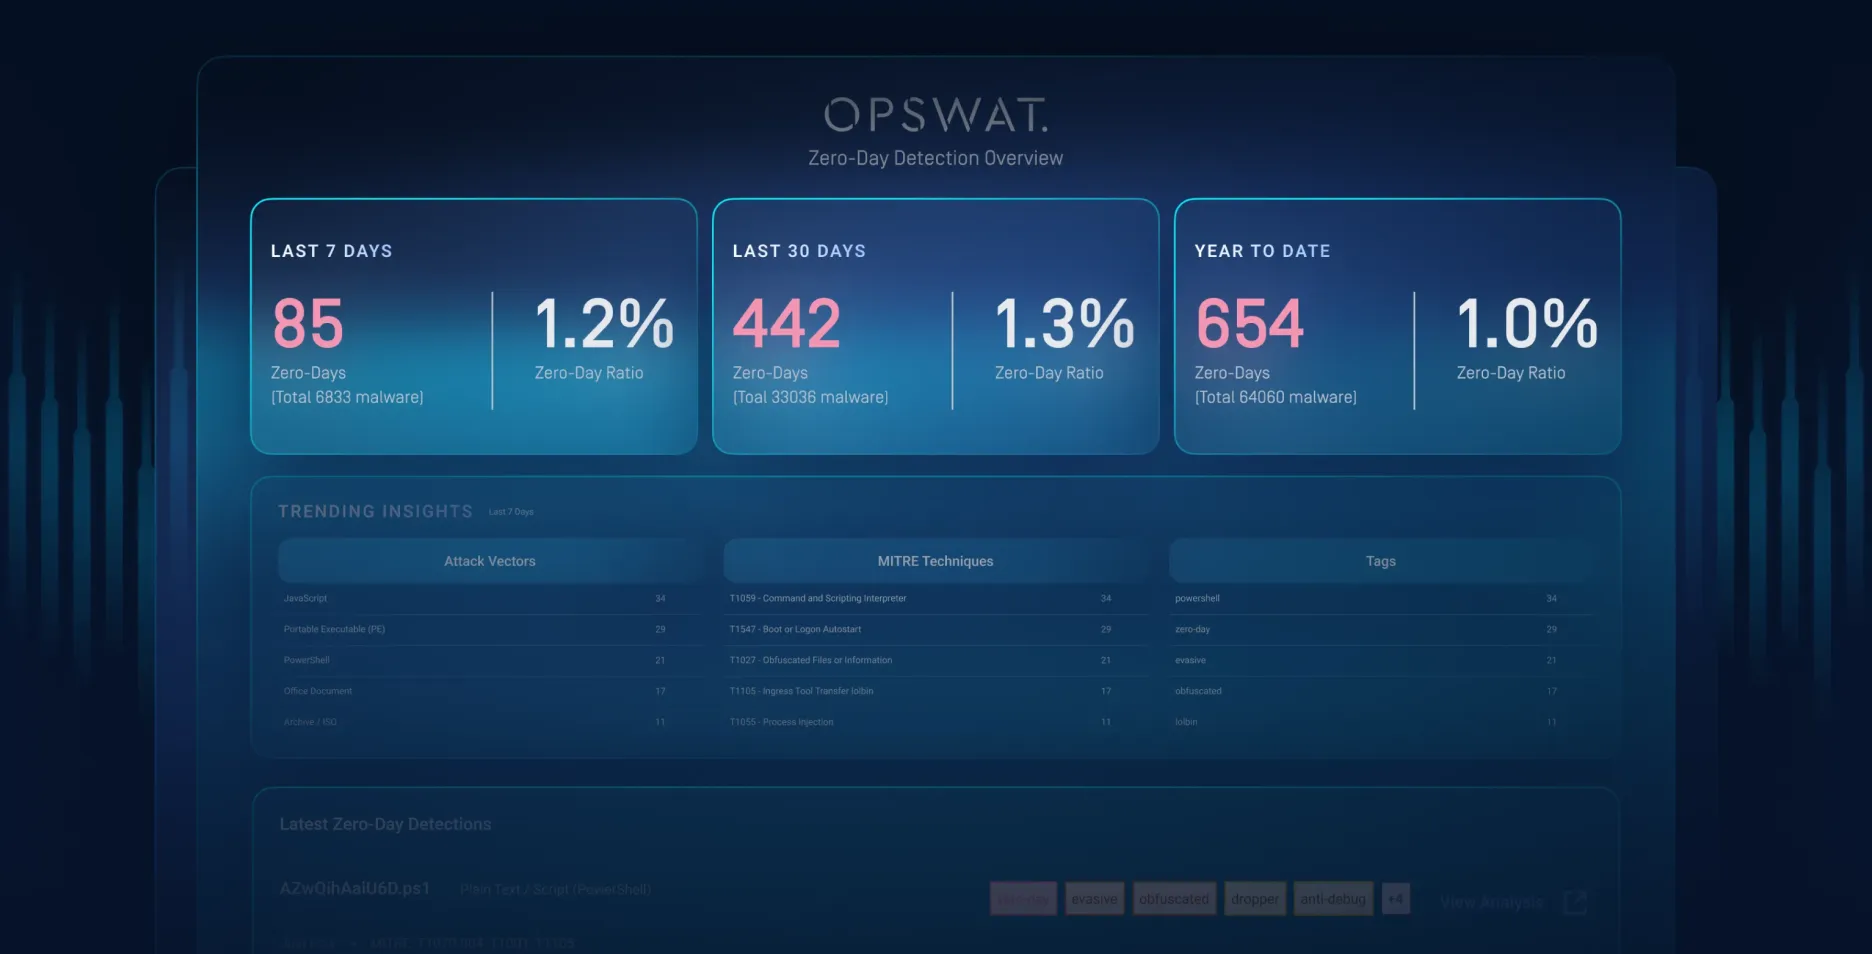
Zero-Day Detection Report
Explore the latest zero-day malware trends, evasive file behaviors, and emerging attack patterns uncovered through OPSWAT threat analysis.
Package Efficacy Report
This report lists the most searched-for threats from the MetaDefender Cloud database over the past month, along with detection rates for our MetaDefender Core Packages.
Anti-malware Market Share Report
Obtain market share data for leading anti-malware and next-gen antivirus vendors, including their top products.
Deep CDR™ Technology Report
This report shares data on infected files cleaned by OPSWAT MetaDefender Cloud, based on samples from customers and community members.
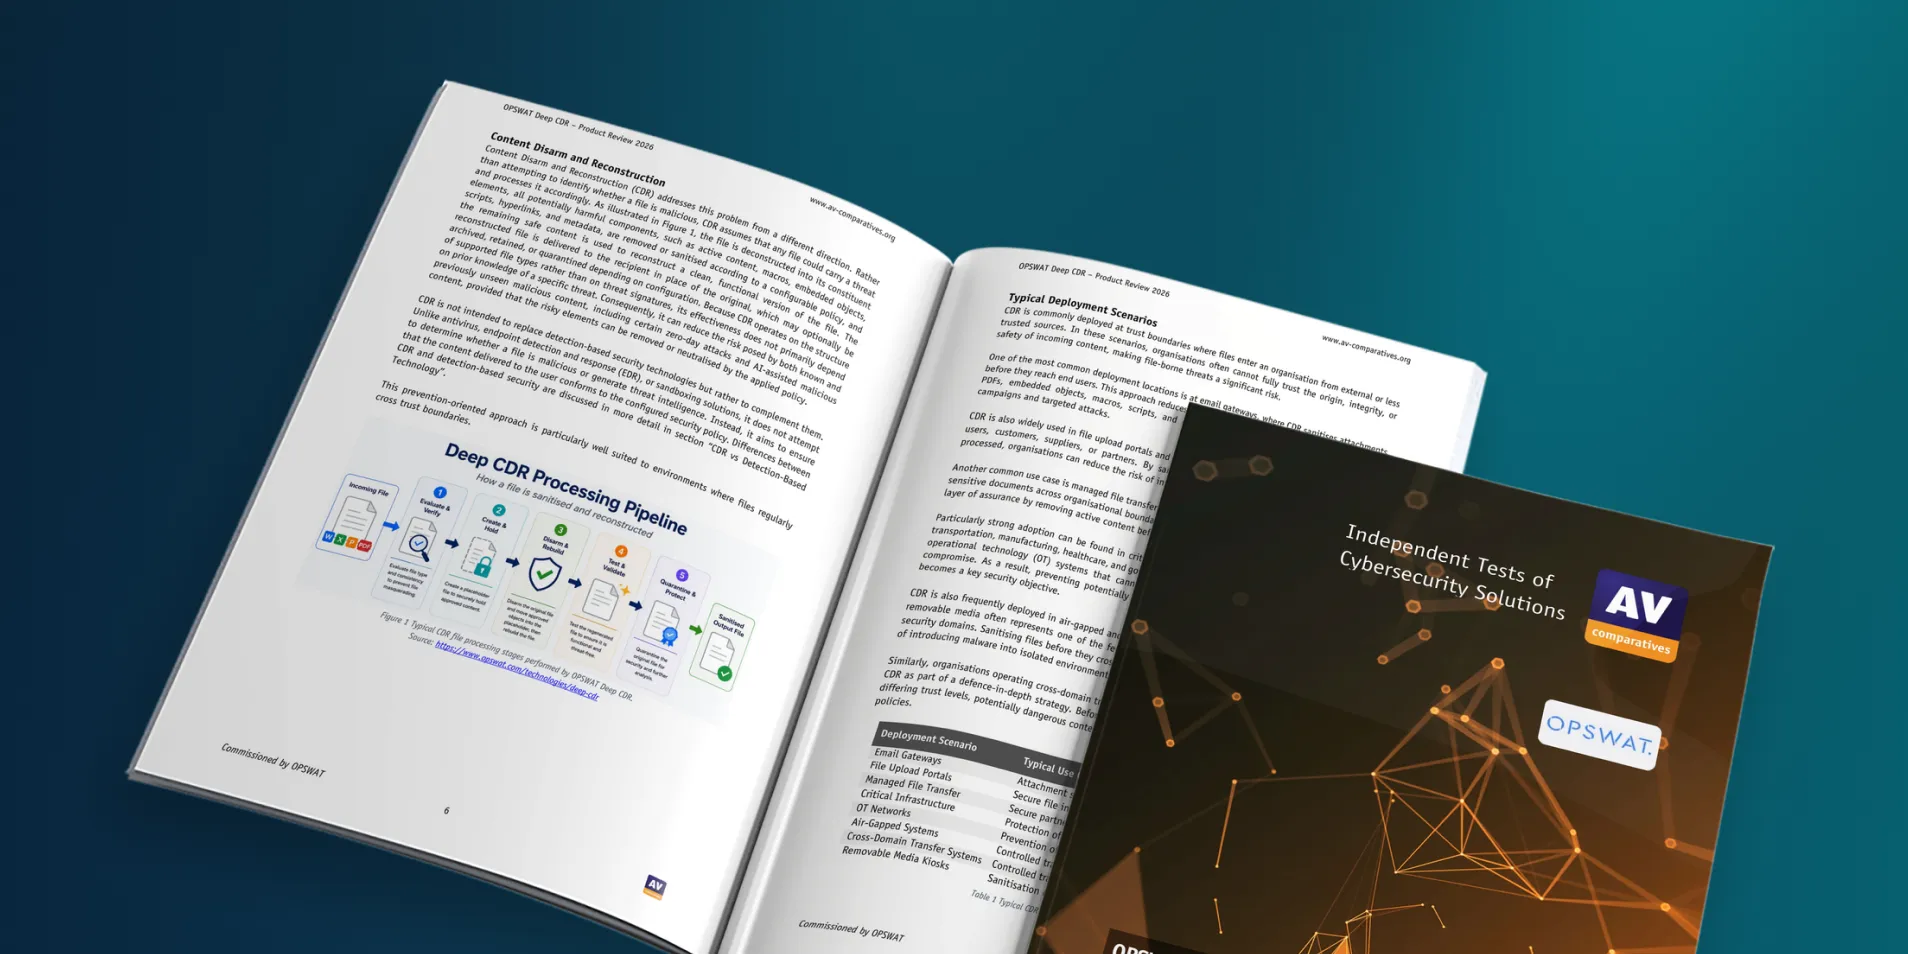
2026 AV-Comparatives Testing Confirms 100% Sanitization Rate of Deep CDR™ Technology
Covering 300+ test cases across most evasive file-borne attacks.
Ponemon Institute State of File Security
2025 OPSWAT Threat Landscape Report
2025 ICS/OT Cybersecurity Budget: Spending Trends, Challenges and the Future
Why Multi-Layered Defense is Critical in Application Security
Email Security Threats Against Critical Infrastructure
Explore the Threat Intelligence
Behind the Trends
Access deeper analysis, investigate suspicious files, and explore multi-layer malware detection through the FileScan community.
Join thousands of security professionals researching threats in real time.
Create a free account to analyze files and access deeper threat intelligence insights.
Make Emerging Threat Intelligence Accessible
Cyber threats evolve every minute.
Security teams need faster access to intelligence that helps them detect and stop attacks earlier.
The OPSWAT Research & Intelligence Center was created to:
- Increase visibility into the global threat landscape
- Provide transparent insights into malware activity
- Empower security professionals with real analysis data
- Strengthen collaboration across the security community
Because the best defense against emerging threats is shared intelligence.