Centralized Patch Management Across On-Premises, Air-Gapped, and Cloud Environments
MetaDefender Endpoint provides advanced management for devices across cloud, air-gapped and on premise environments
- Vulnerability Management
- Streamlined Updates
- Expanded Visibility
Why Patch Management Remains a Persistent Challenge
Air-gapped networks, delayed updates, limited visibility, and manual processes make it difficult to maintain security, compliance, and operational resilience.
Patching devices in isolated OT, ICS, and segregated environments demands extensive manual effort and coordination. Most IT-centric patch tools stop at the perimeter and leave these segments fully exposed.
Unpatched systems stem from more than just oversight. Software incompatibilities, fear of downtime, lack of vendor support, and sprawling third-party application estates all contribute. Missed patches accumulate silently, widening the attack surface where downtime and safety risks are highest.
Patching critical systems risks outages. Rigid deployment windows, forced reboots, and lack of controls leave teams choosing between security and availability.
Regulatory frameworks such as NIS2, CIS, NIST, and ISO 27001 demand evidence of timely patching across your entire estate. Without an advanced patching tool with automated audit trails, compliance preparation becomes a weeks-long manual exercise.
Separate tools for multiple operating systems and third-party applications create visibility gaps and reconciliation overhead. Teams waste hours cross-referencing siloed consoles instead of closing vulnerabilities.
How Does Patch Management Work?
From internet-connected enterprise endpoints to fully isolated OT networks, patch management with MetaDefender Endpoint unifies detection and remediation across deployments.
Air-Gap Readiness
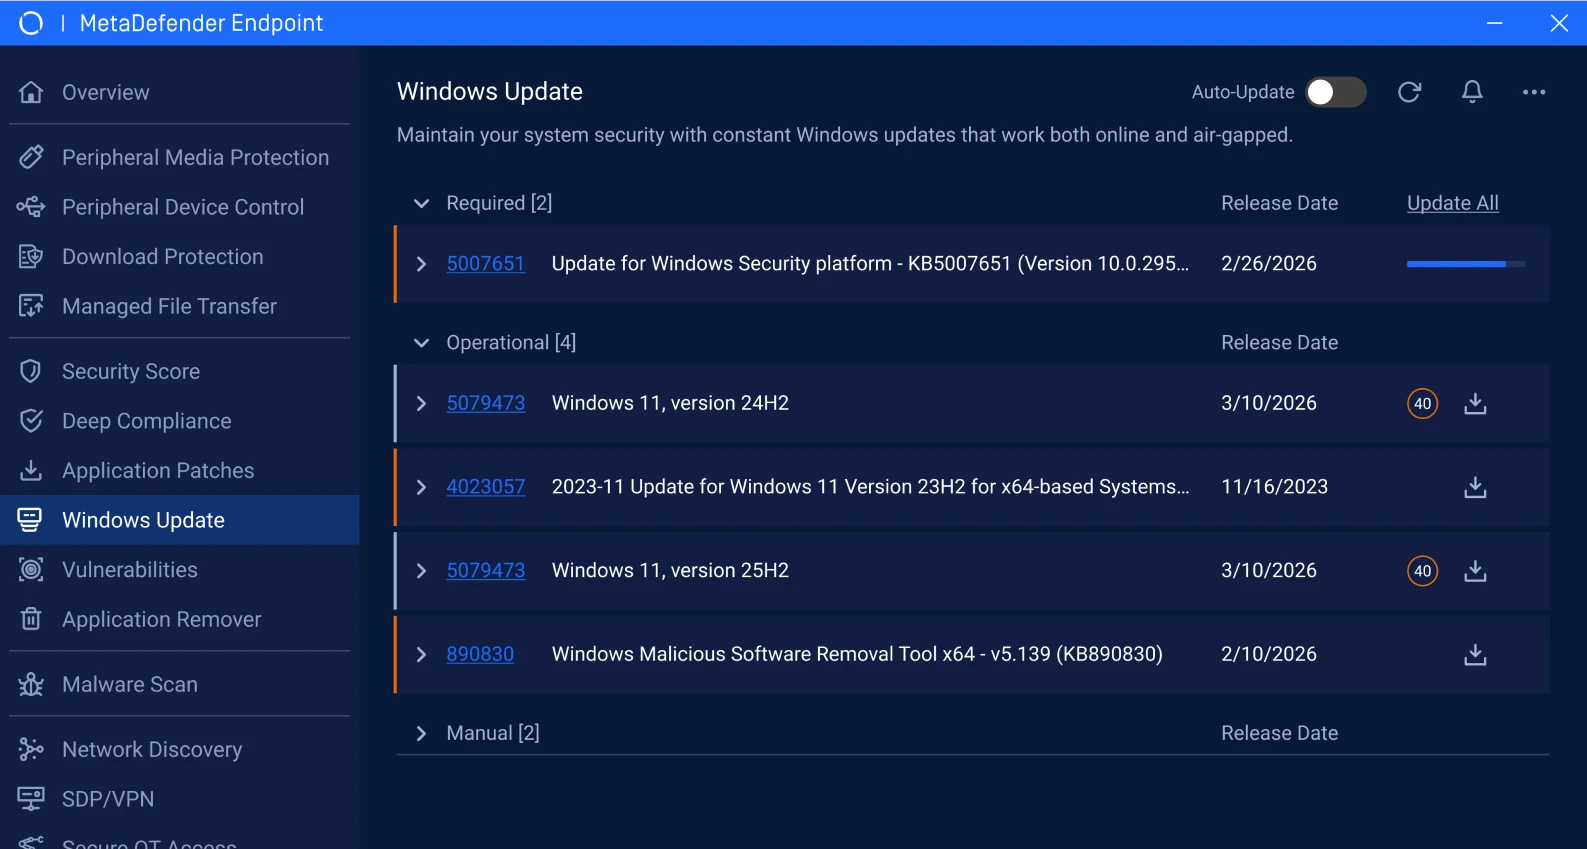
Purpose-built for isolated OT, ICS, and segregated environments. Securely deploy patches to air-gapped endpoints with the same automation and audit trail as connected systems, with full patch status visibility maintained even when systems are completely disconnected.
Detect & Remediate Vulnerabilities
Stay ahead of your vulnerabilities. Continuous asset inspection and CVSS-based risk prioritization surface the vulnerabilities that matter most. Identify CVEs and automatically patch third-party apps and OS updates.
Uptime Assurance
Patch on your terms, never at the cost of availability. Flexible patch scheduling, unattended patching for background deployment, configurable maintenance windows and reboot behavior mean patches never compromise uptime.
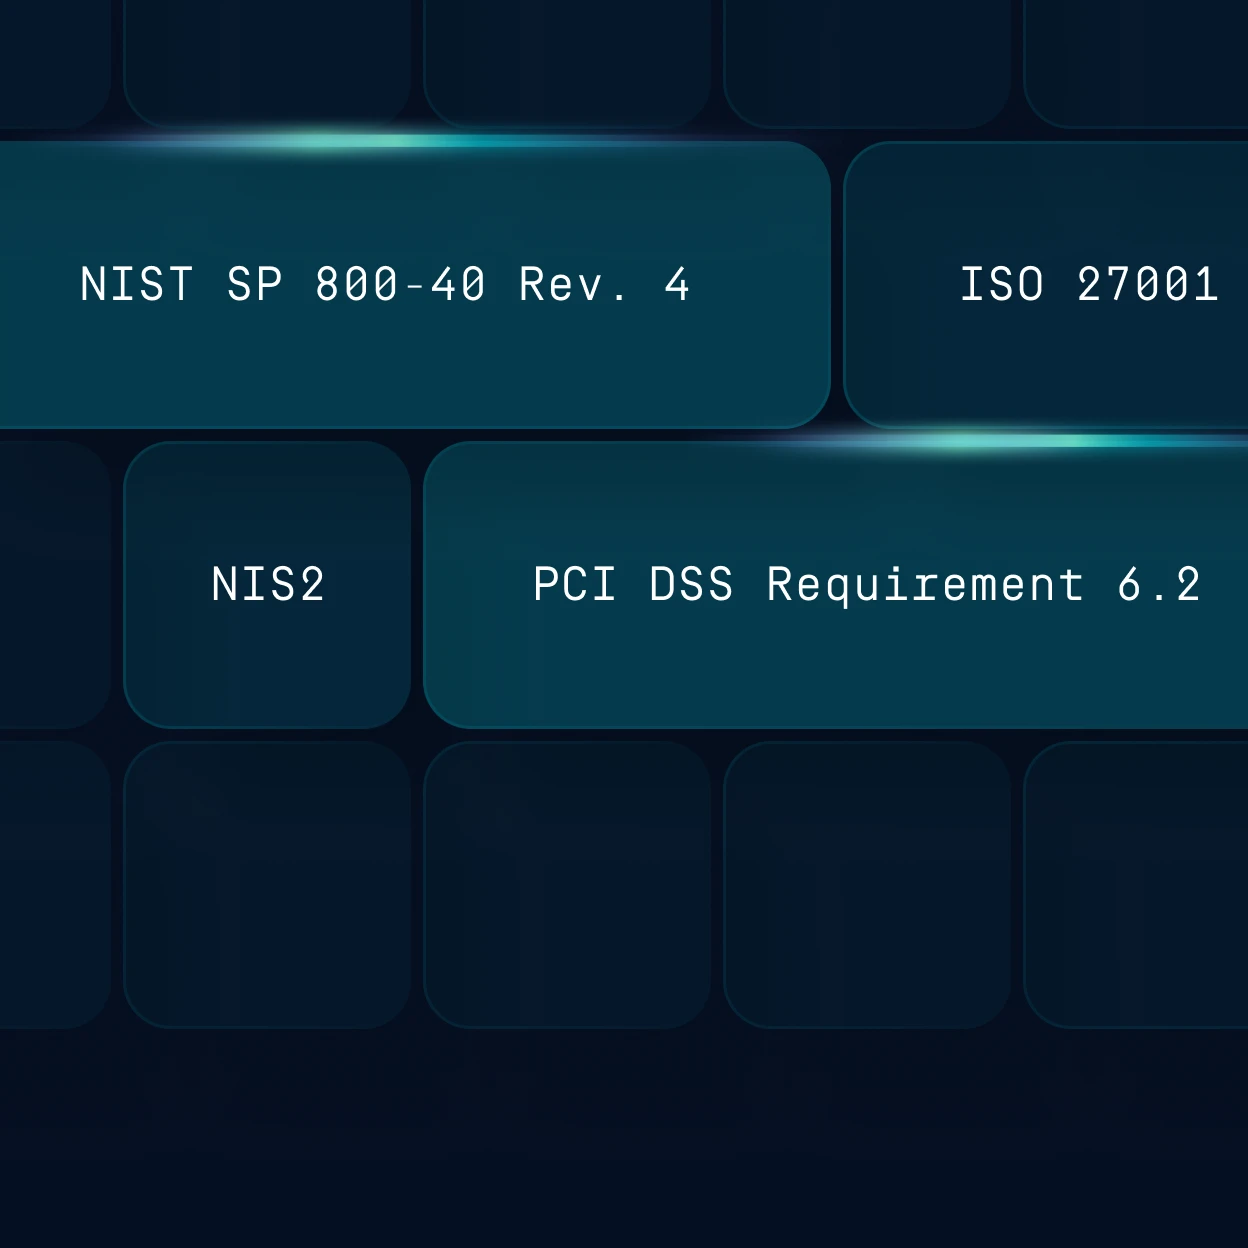
Compliance Ready
Automated patching remediates vulnerabilities on schedule across your entire estate, including air-gapped environments, while immutable logs provide full traceability and audit-ready evidence on demand.
Flexible Deployment
MetaDefender Endpoint can be deployed in the cloud, on-premises, or in a fully air-gapped environment. It is a single platform that adapts to your infrastructure and needs.
Patching Across Environments from a Single Platform
Everything you need to patch with confidence. From isolated OT networks to enterprise internet-connected endpoints, every feature is built to close vulnerabilities faster without disrupting operations.
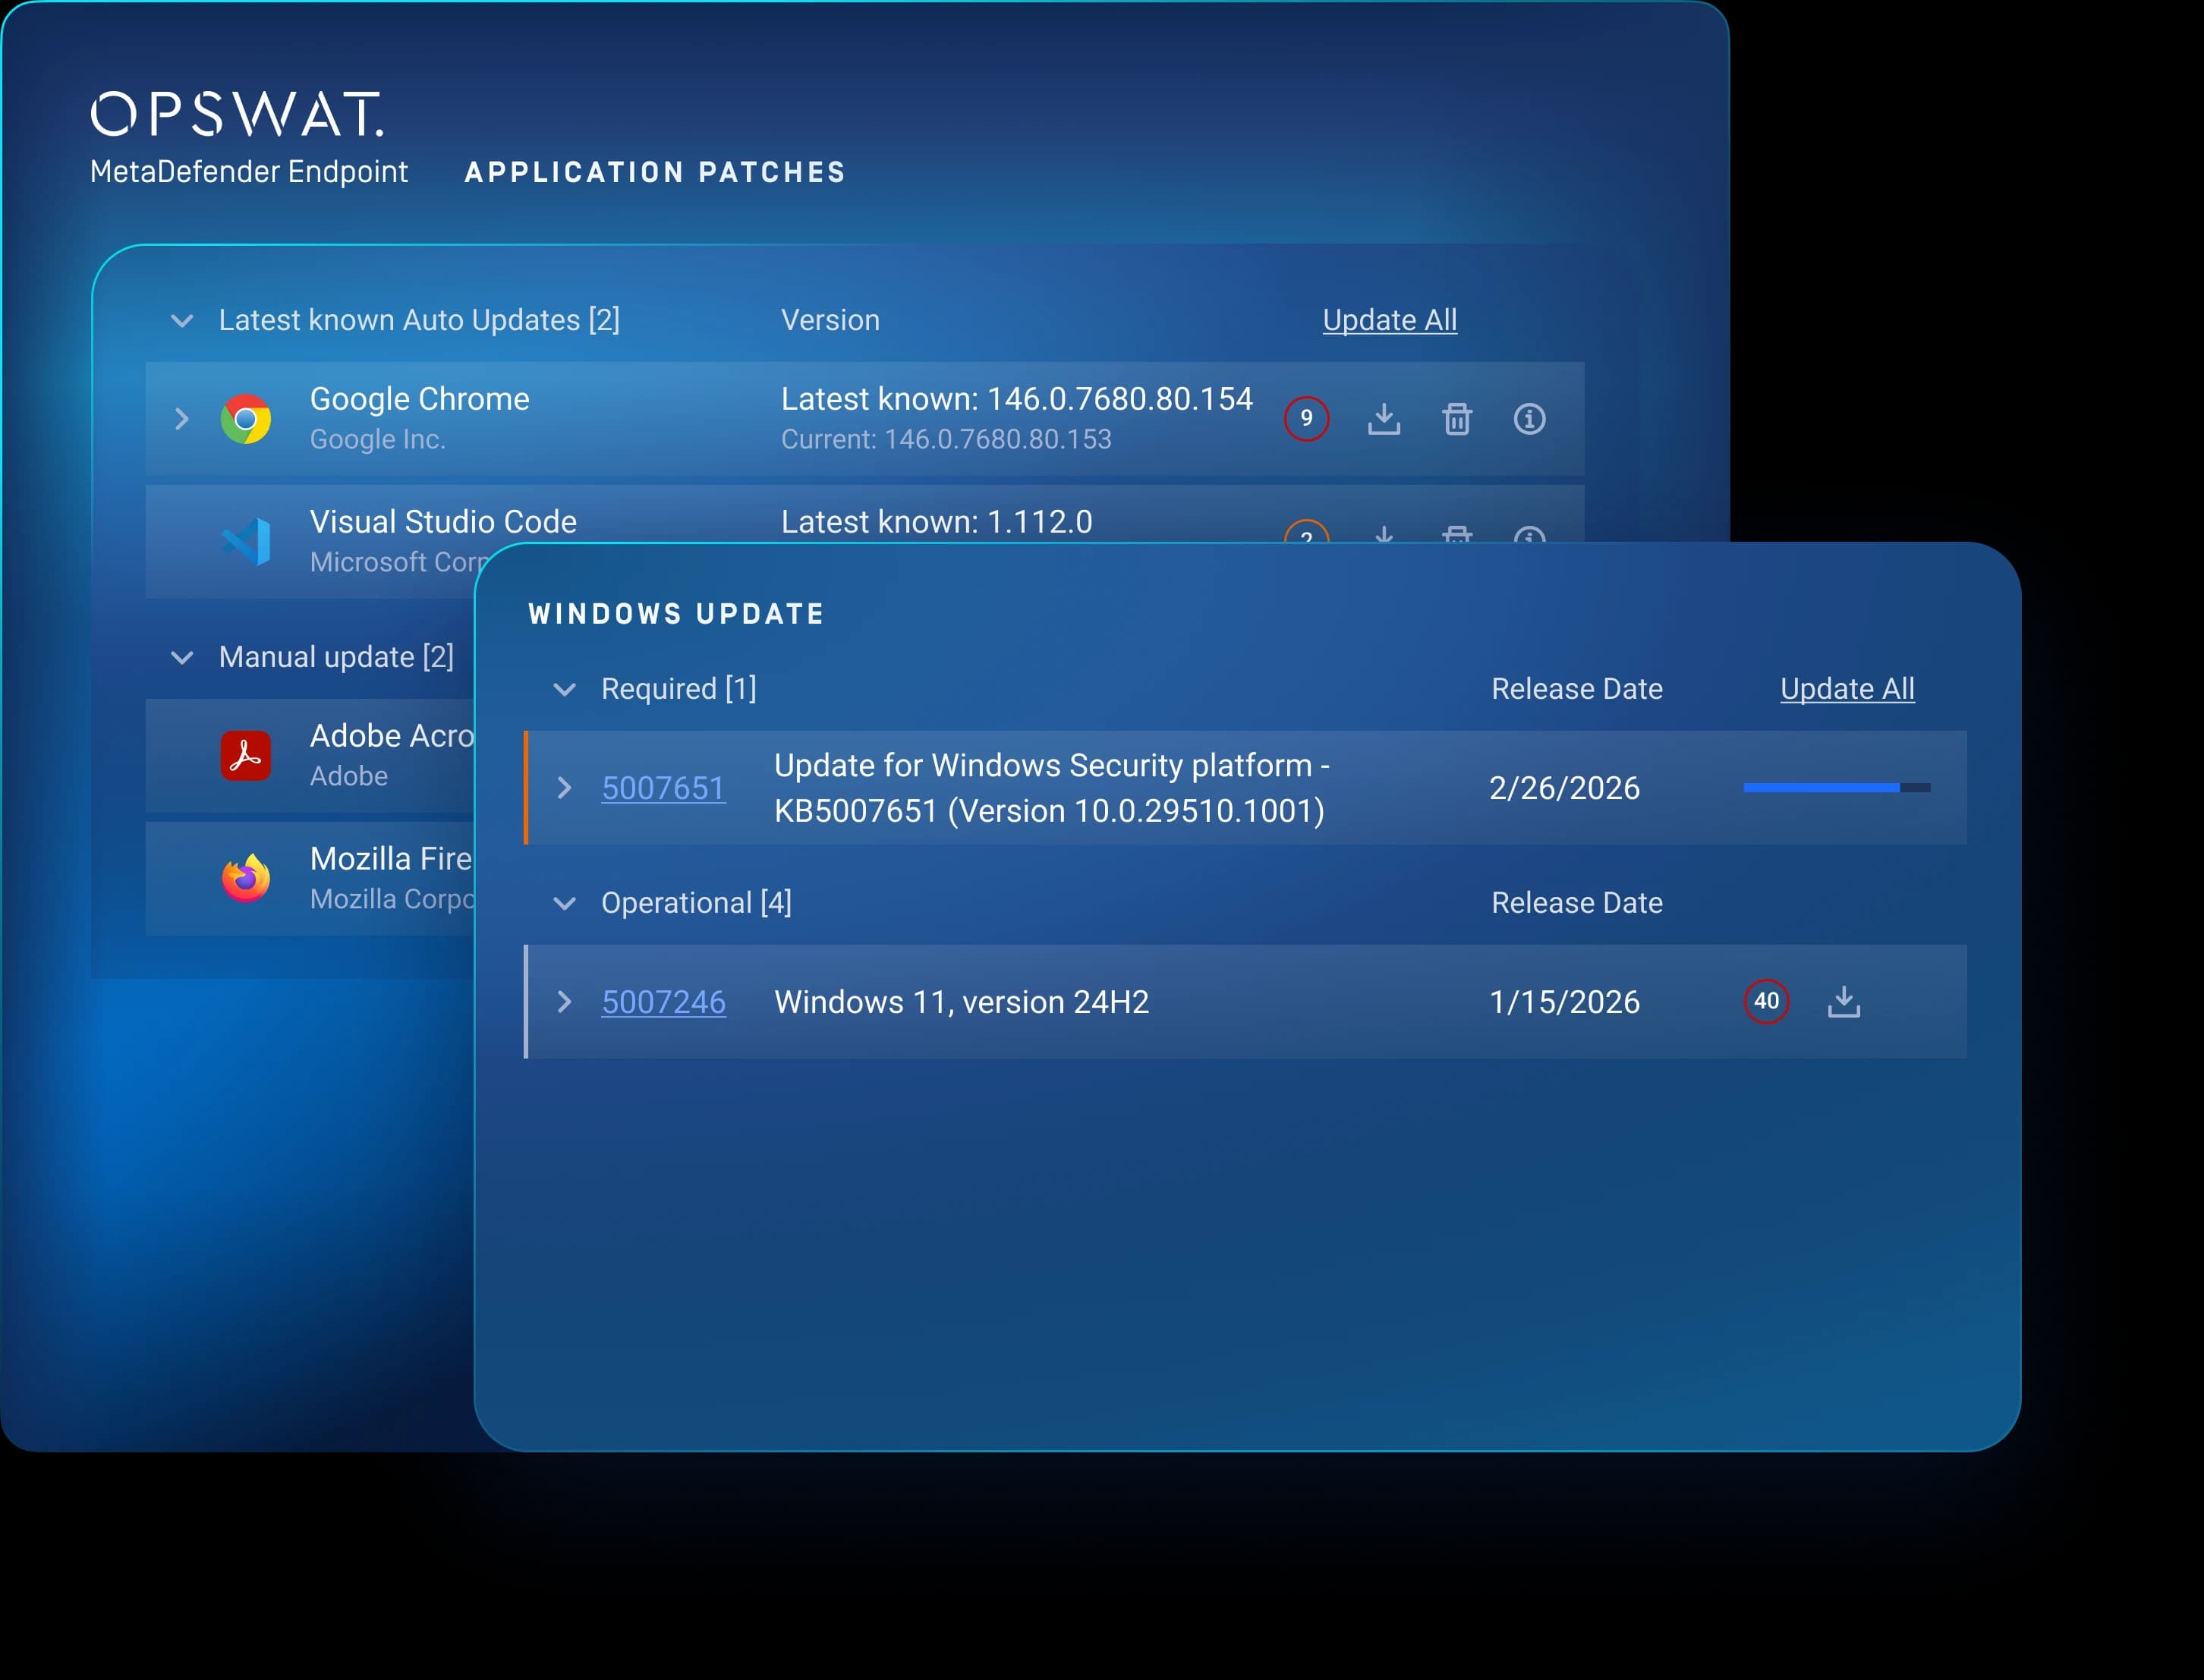
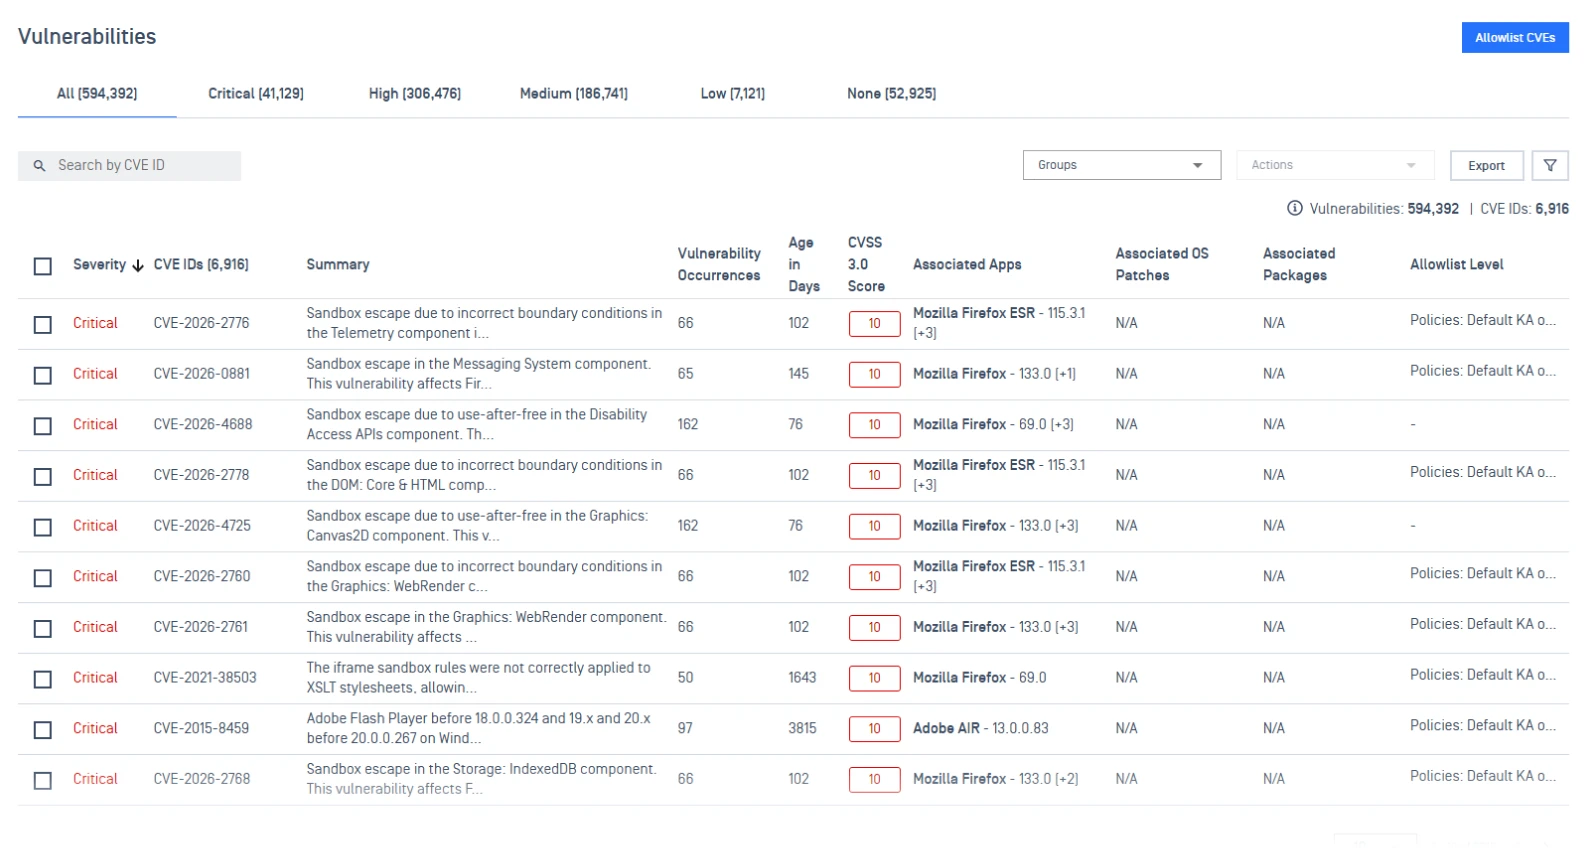
Detect vulnerabilities across 975+ applications with CVSS-based severity scores, actionable insights, and recommended fixes to accelerate remediation.
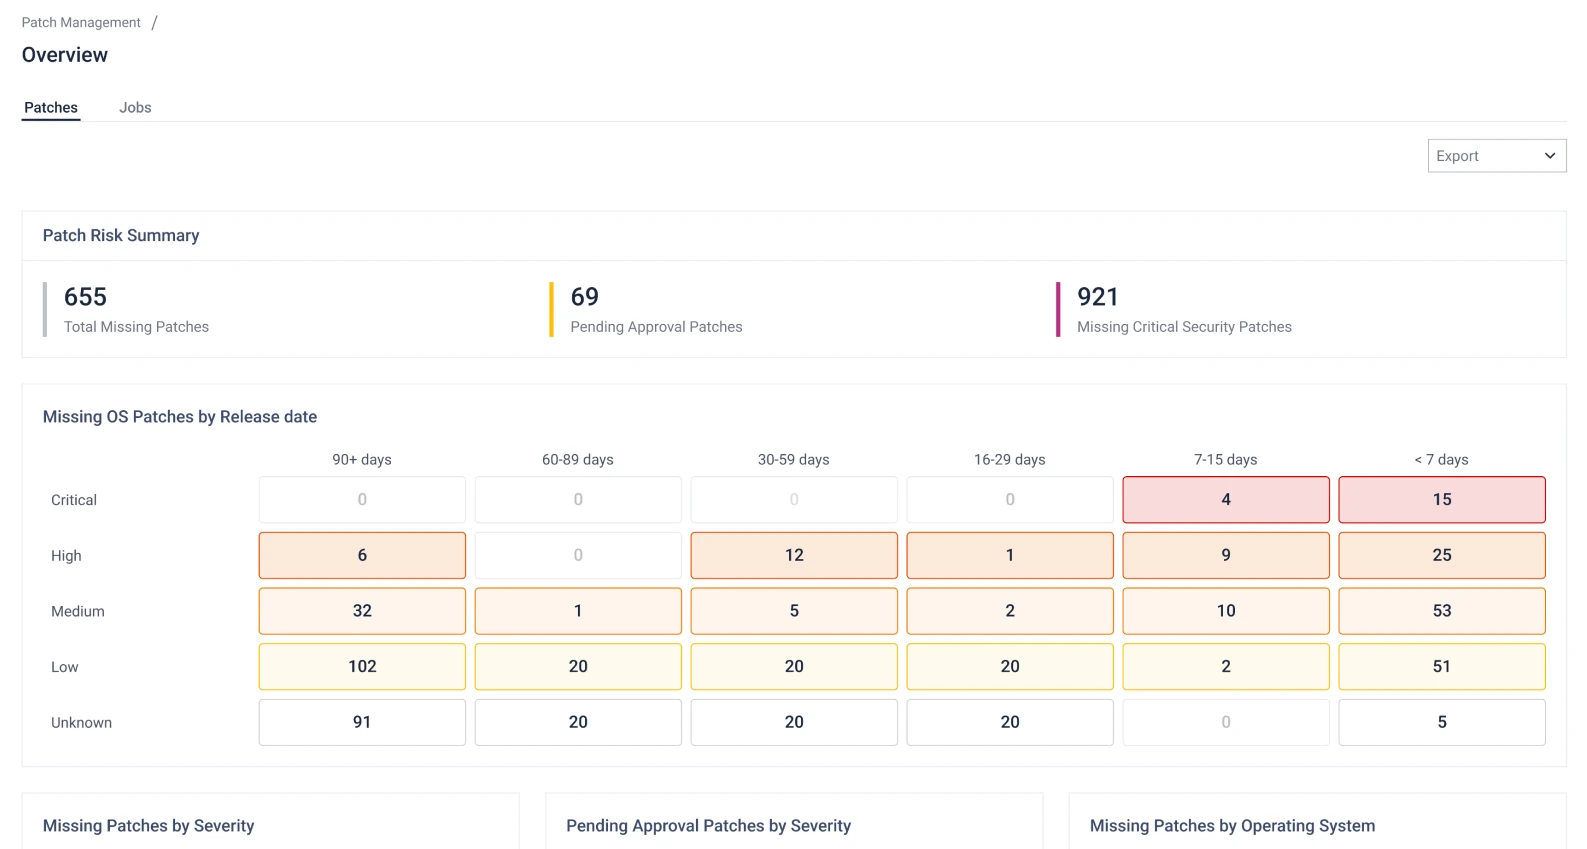
Know the status of every patch, on every endpoint, operating system, and third-party applications with real-time dashboards. Get a unified view of patch status across the entire estate, eliminating the blind spots that come with siloed tools.
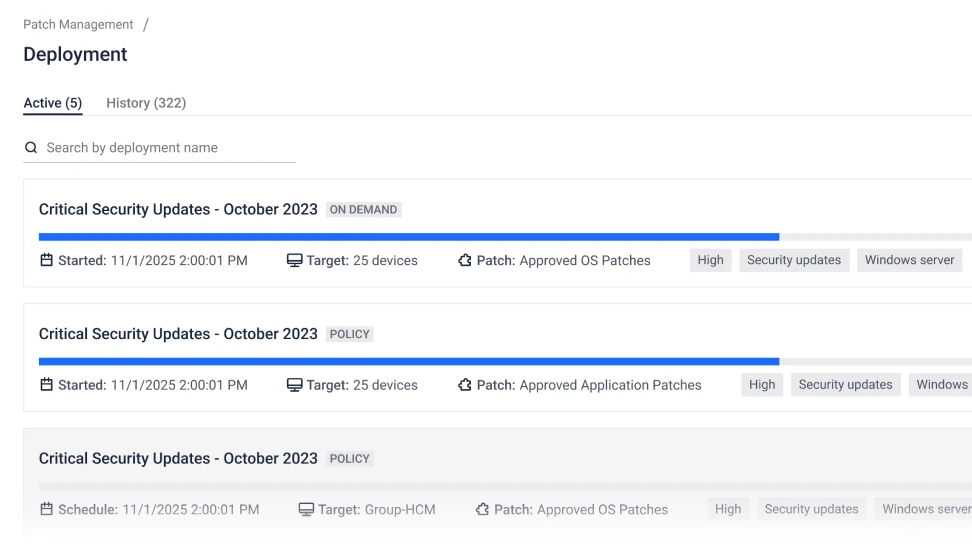
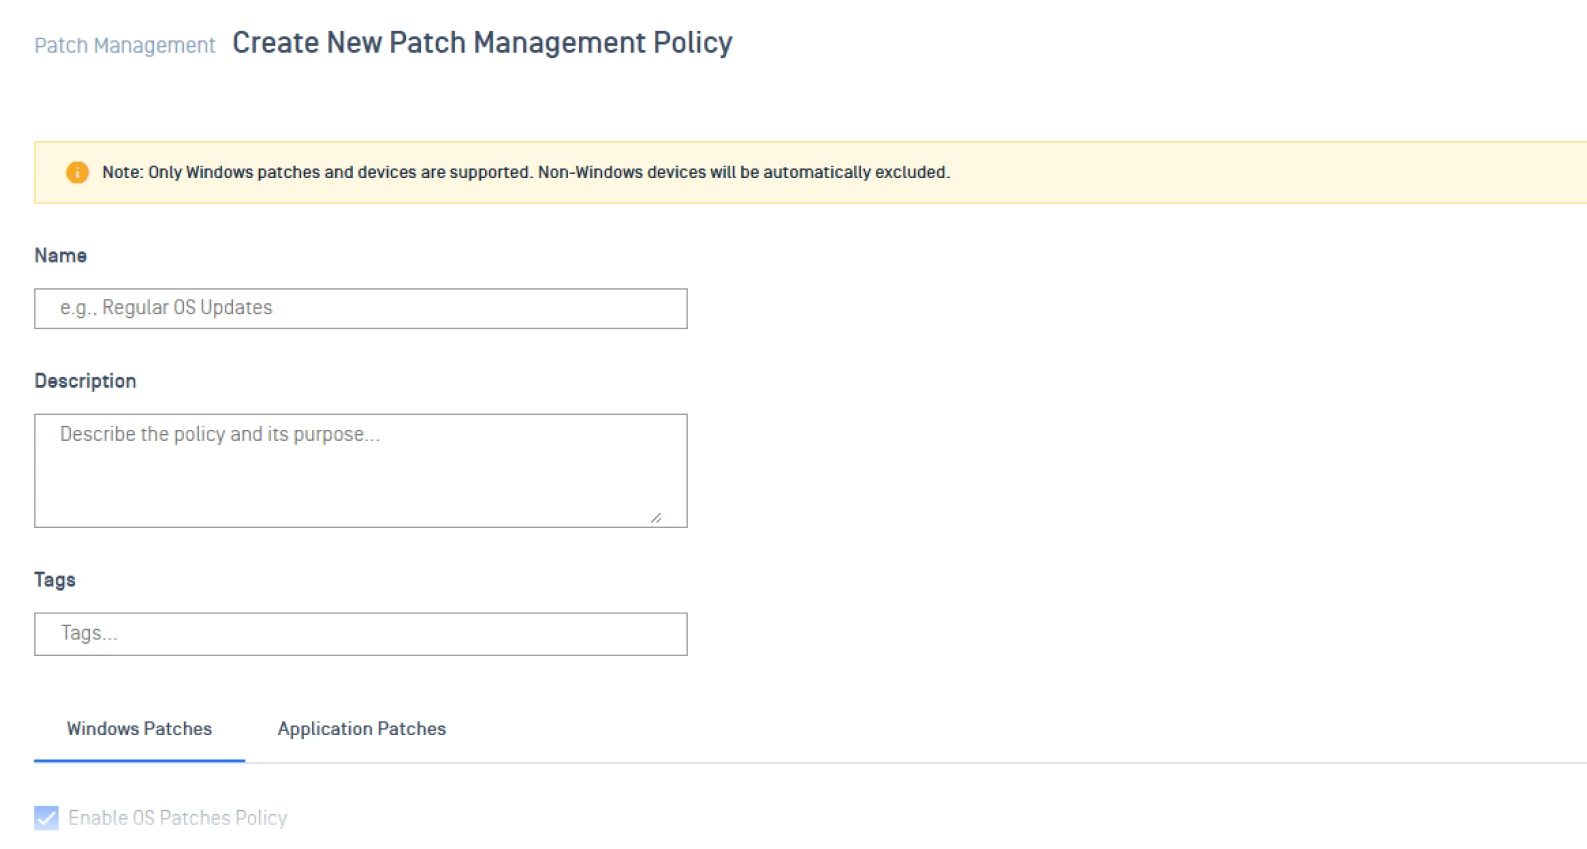
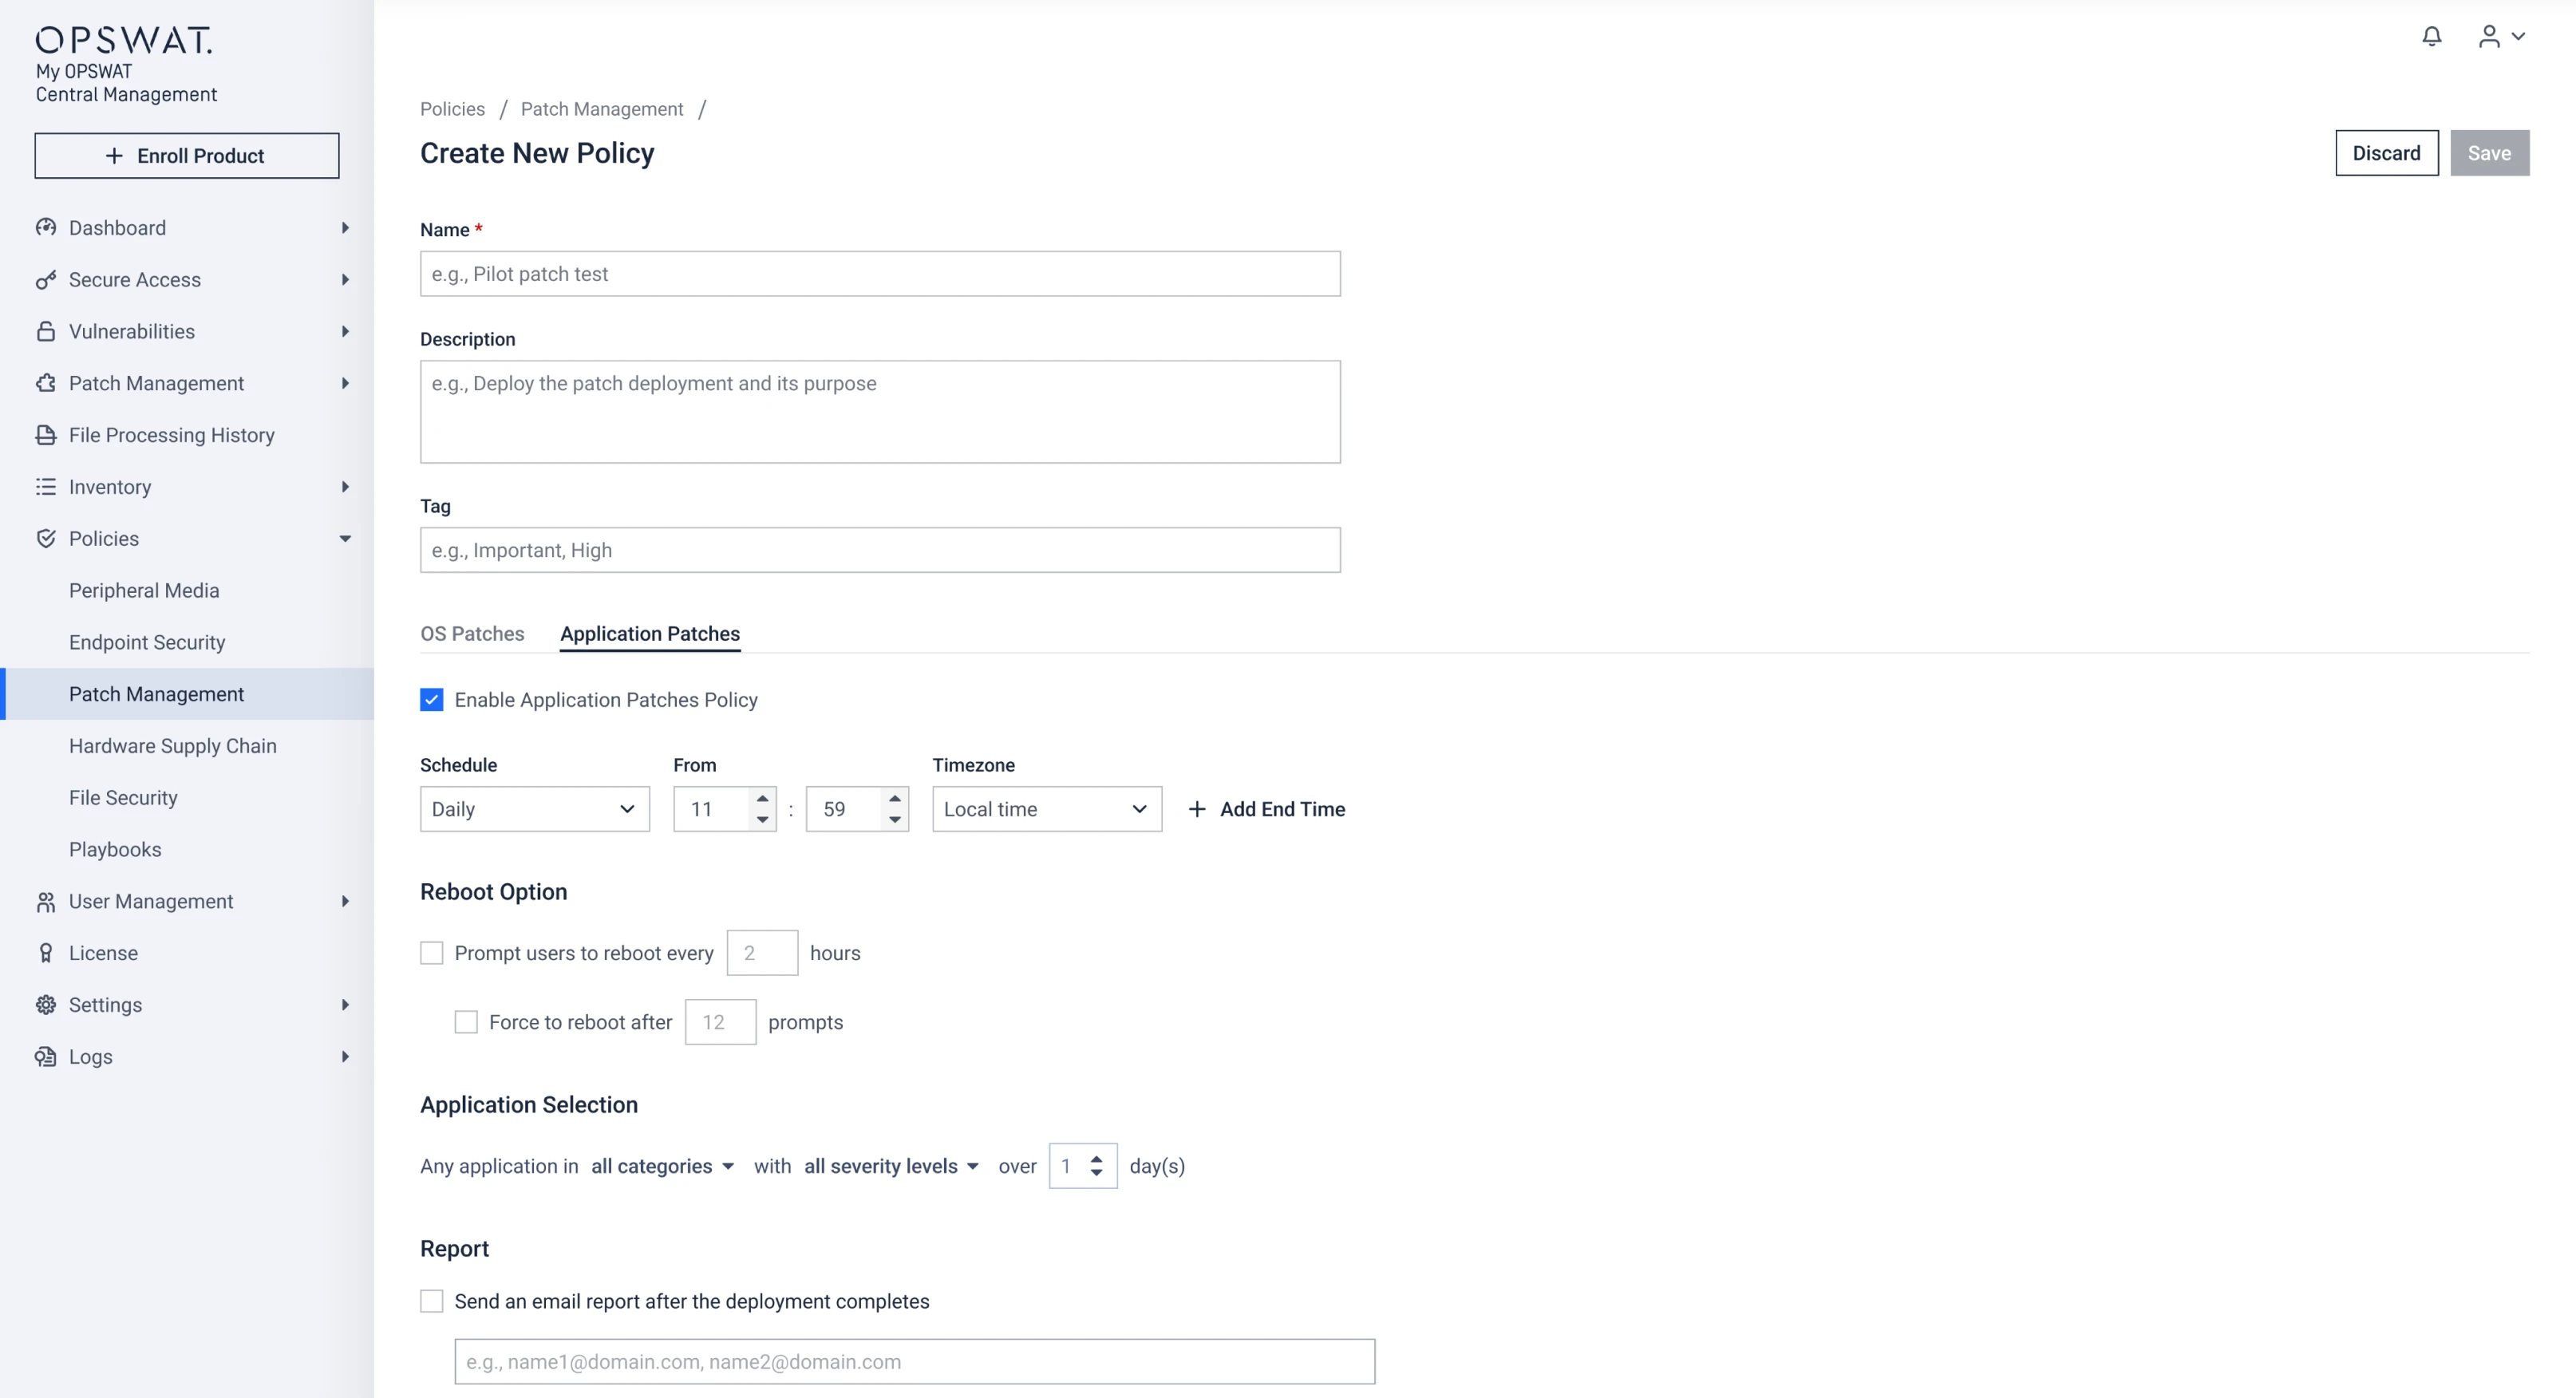
Manage and monitor your patching operations, whether it’s on-demand or recurring. Define maintenance windows, reboot behavior, and multiple rollouts that align with your operational calendar with automated workflows and zero manual intervention.
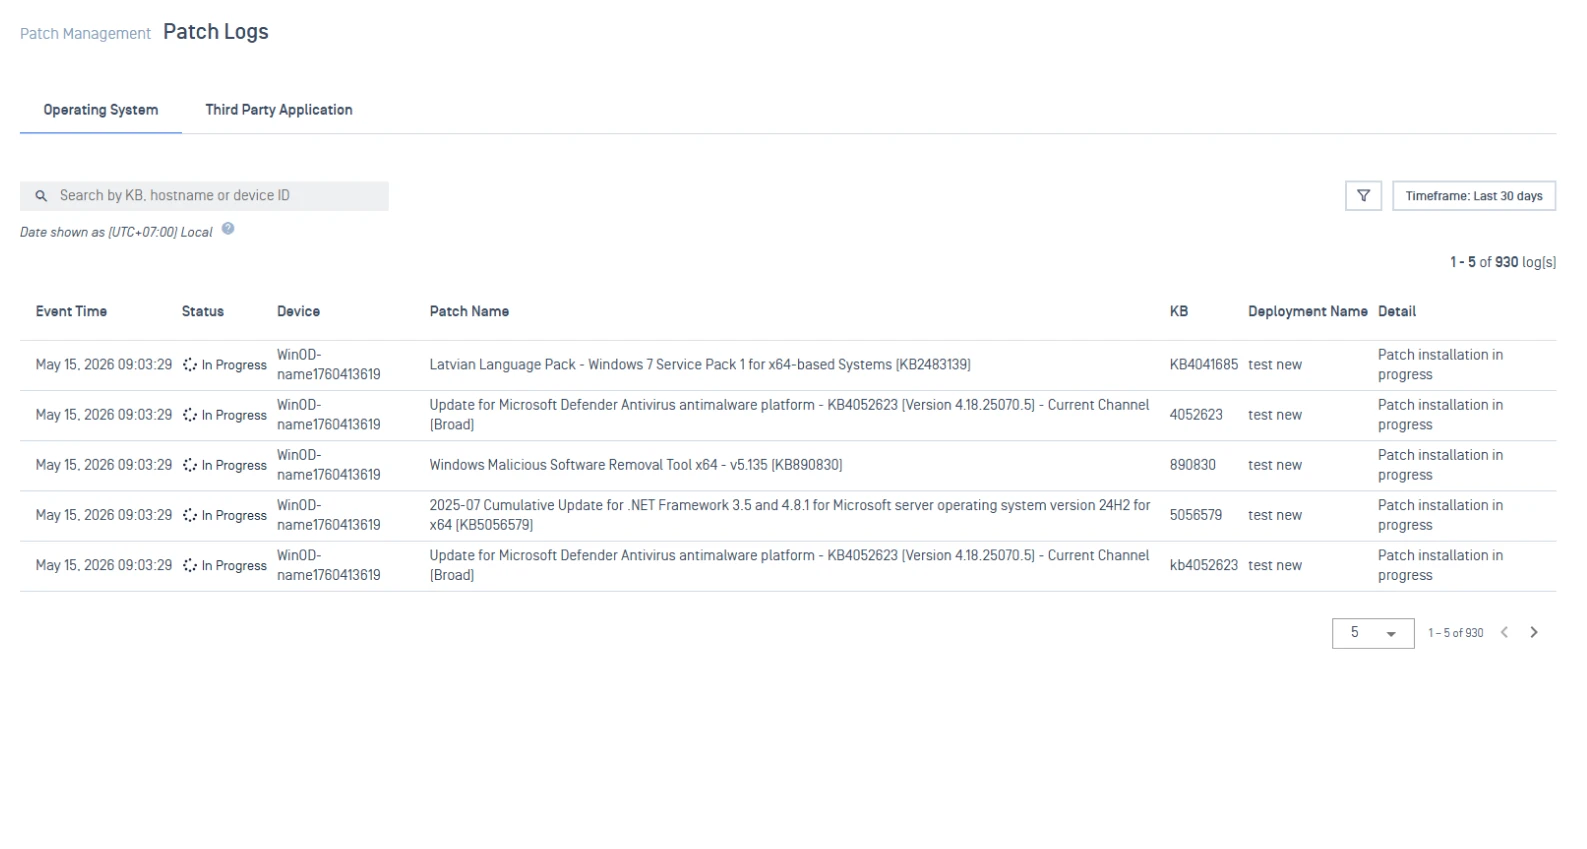
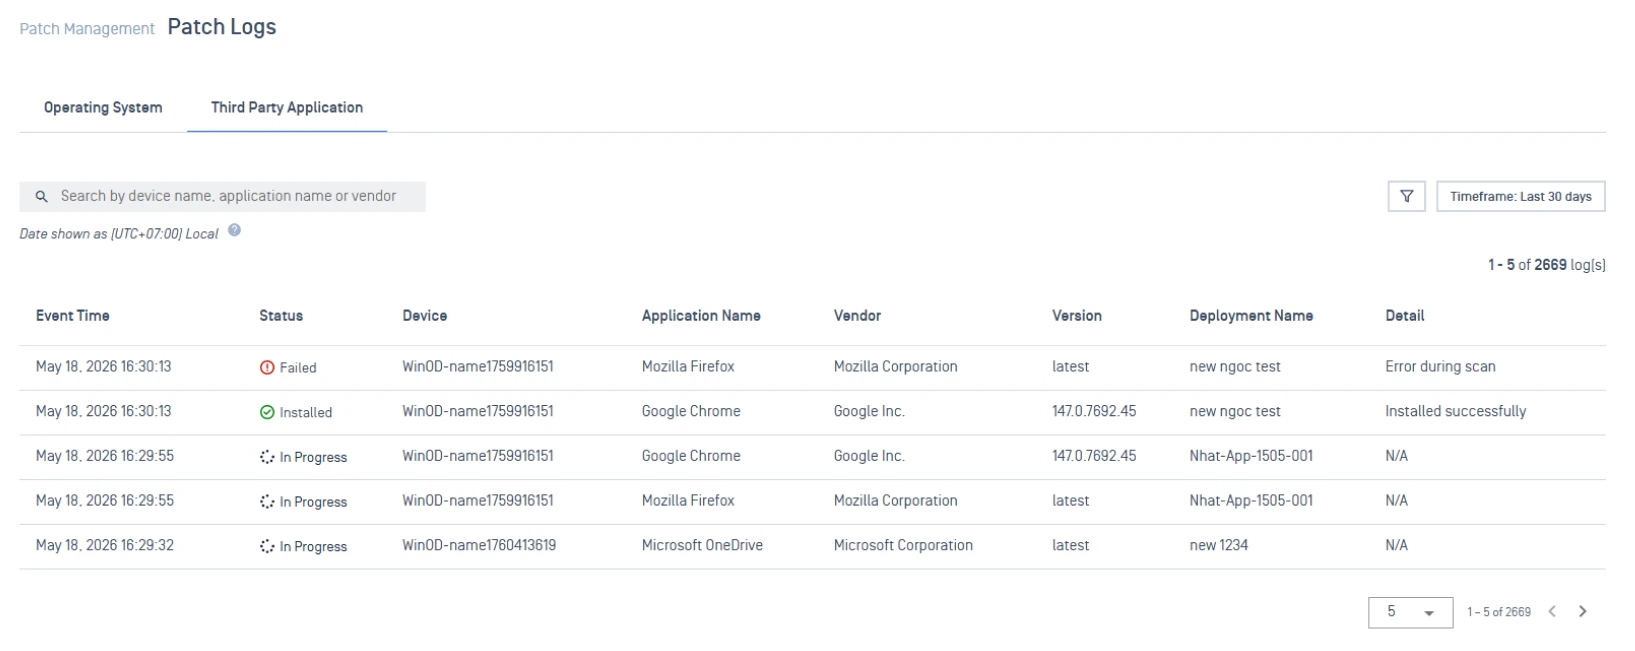
See every patch event across deployments with tamper-proof logs and an end-to-end audit trail. Whether you're preparing for an internal review, a regulatory audit, or an incident investigation, the evidence is always retrievable.
- My OPSWAT Central Management
 MetaDefender Endpoint
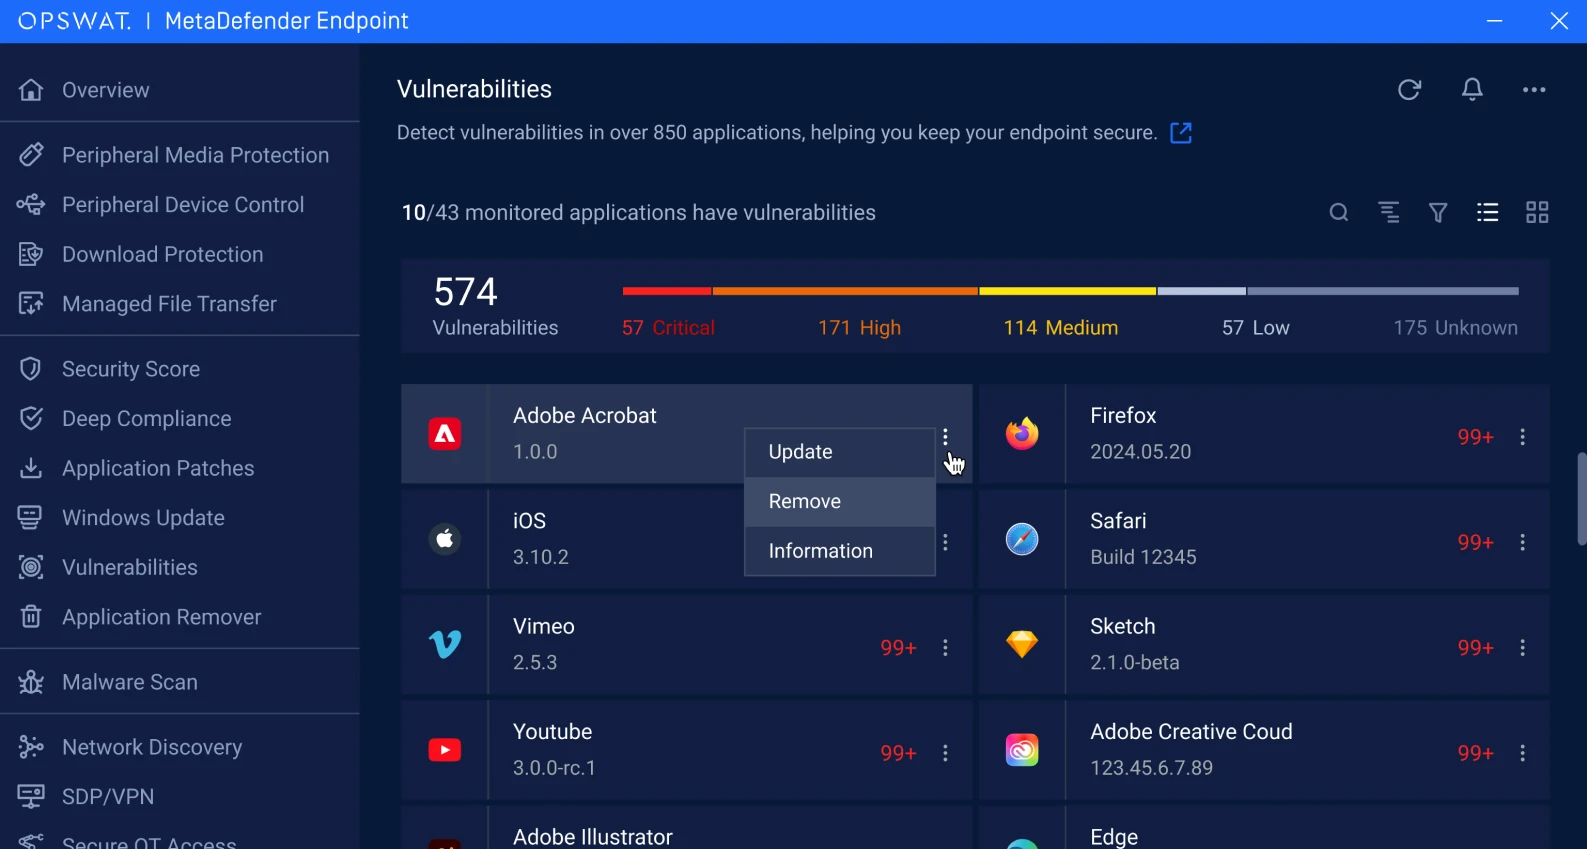
- My OPSWAT Central Management
 MetaDefender Endpoint
- My OPSWAT Central Management
 MetaDefender Endpoint
- My OPSWAT Central Management
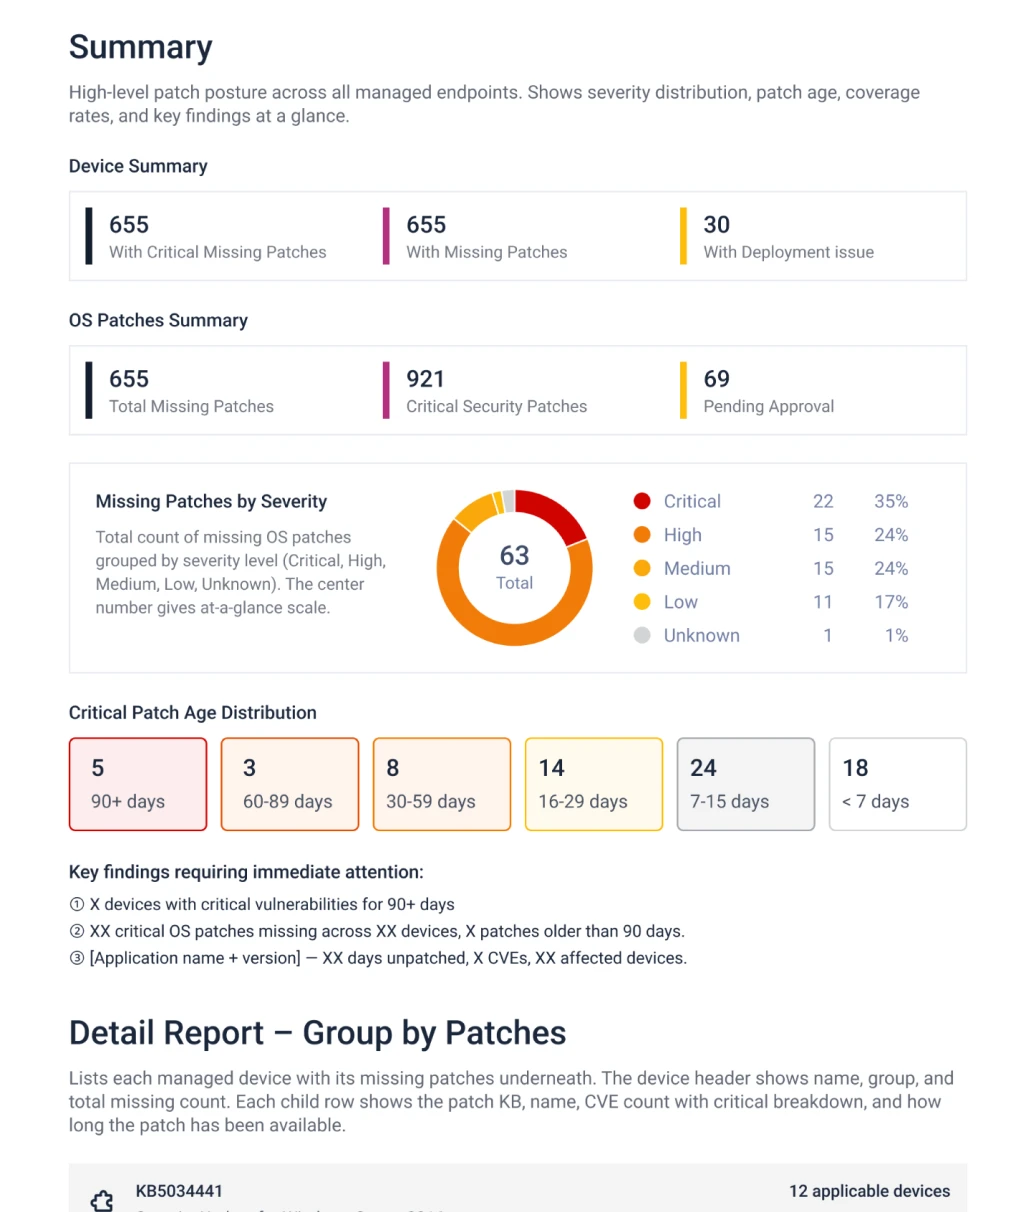
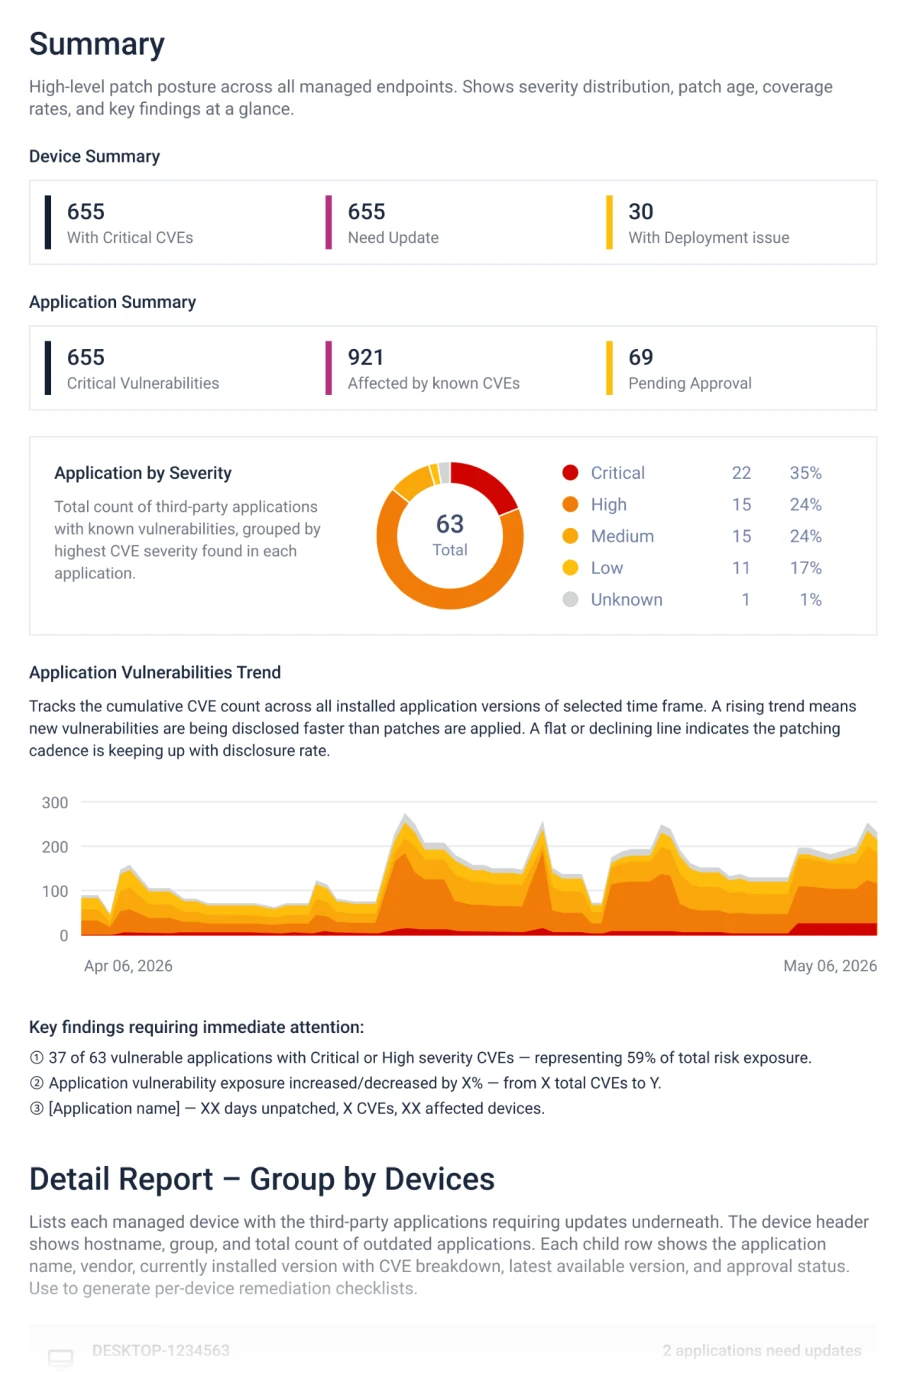
Generate customizable reports to meet your compliance and operational needs. Reports can be filtered by severity level, endpoint group, or deployment name, and can be exported in formats aligned with major compliance frameworks, including NERC CIP, NIS2, and NIST CSF.
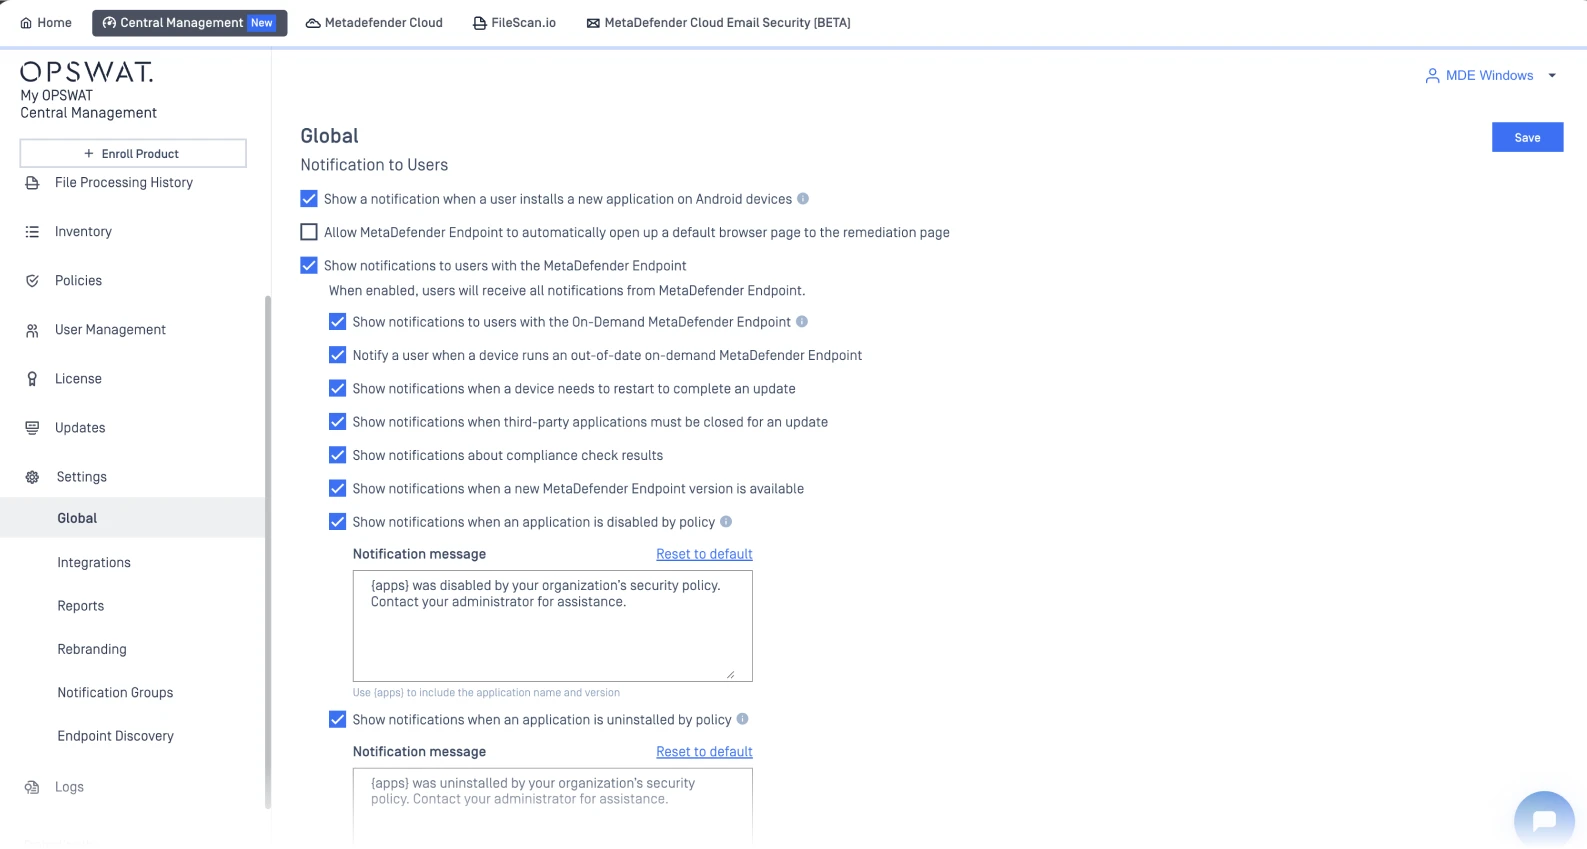
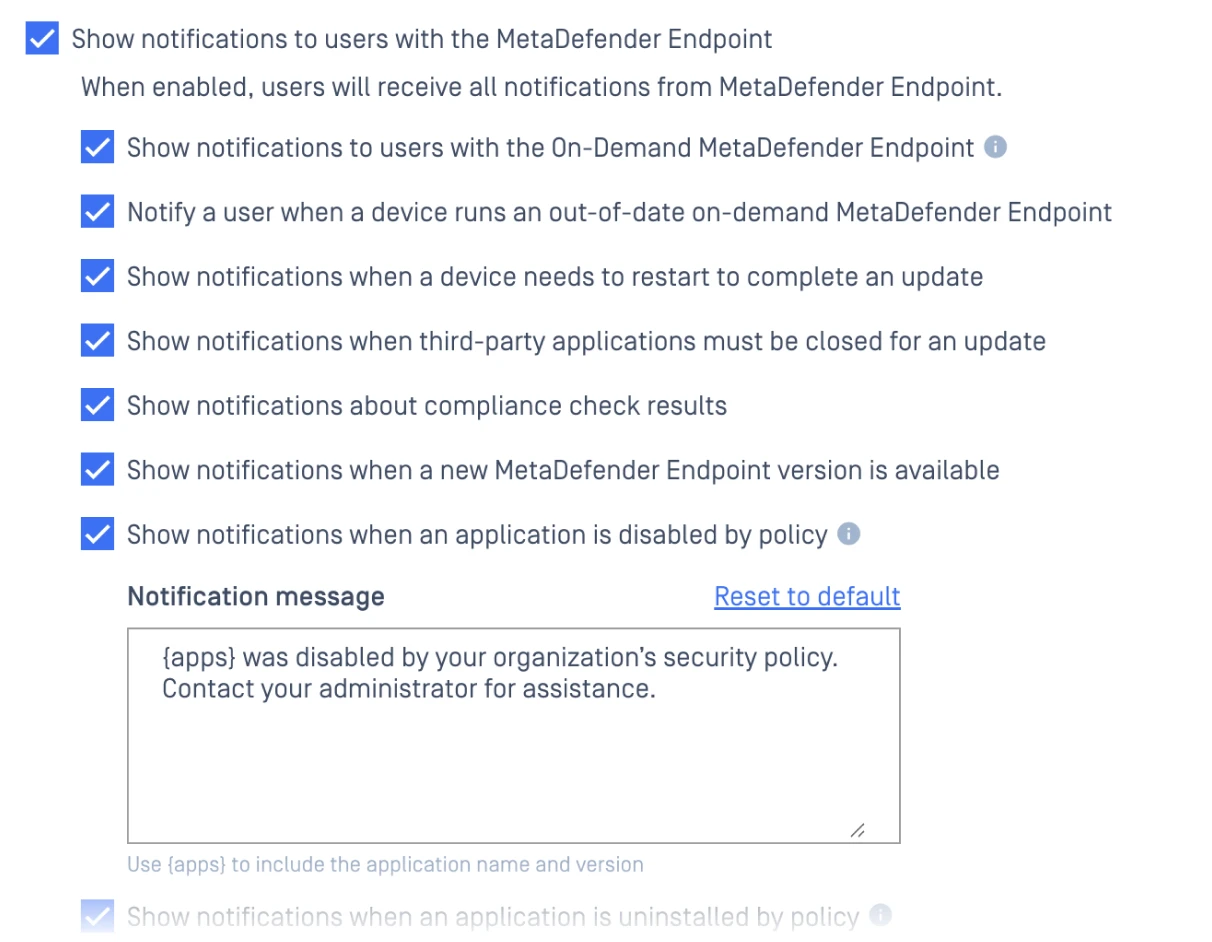
Purpose-built for the critical infrastructure. Suppress all pop-ups, notifications, and user interface elements and enable patches to deploy in the background. Users stay focused while security operations continue.
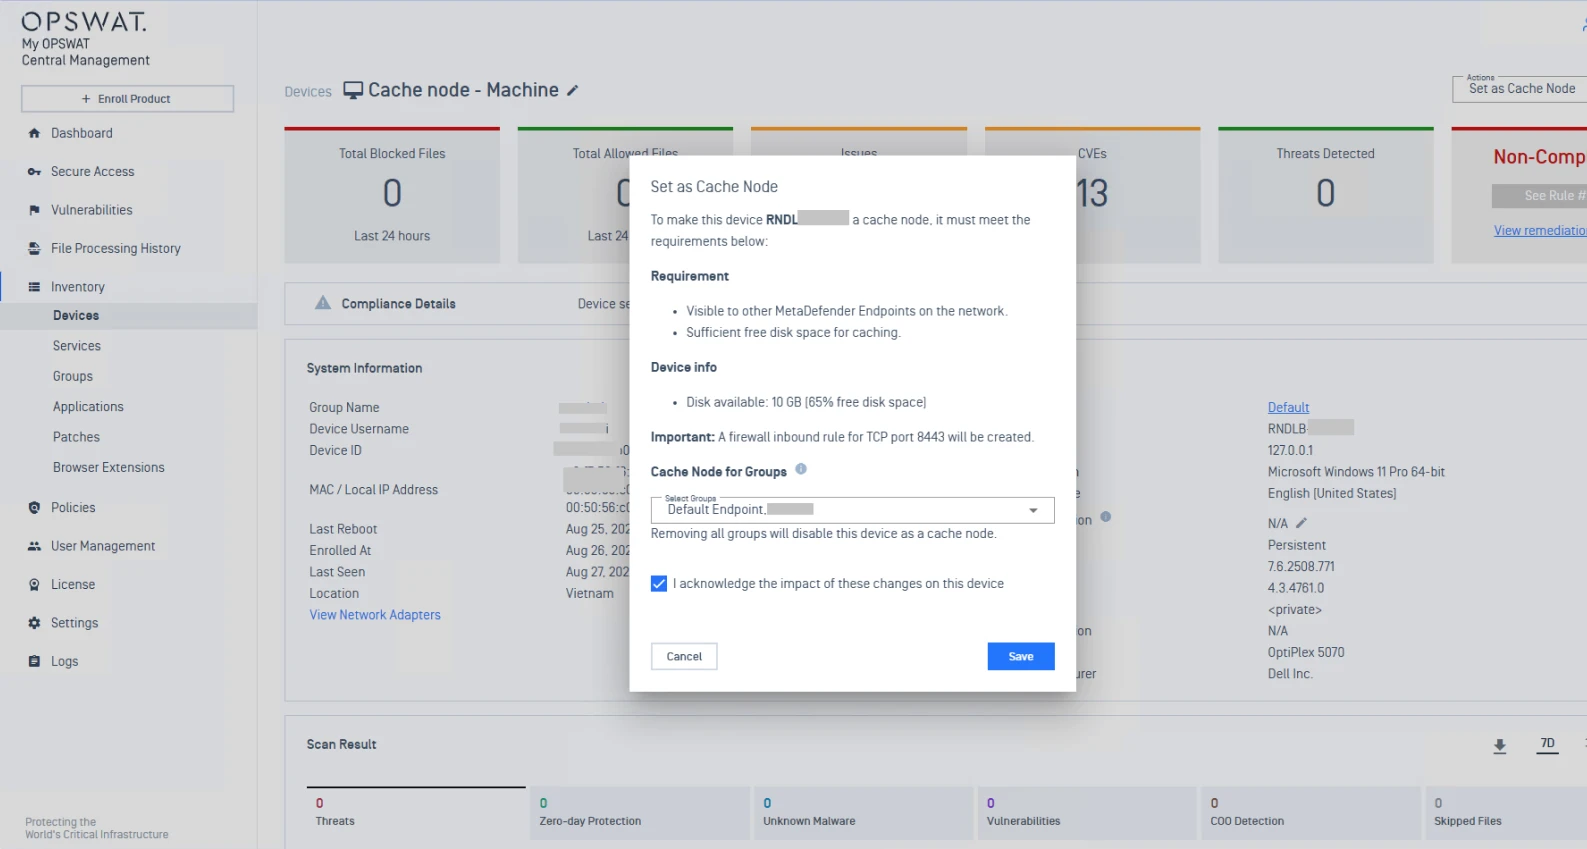
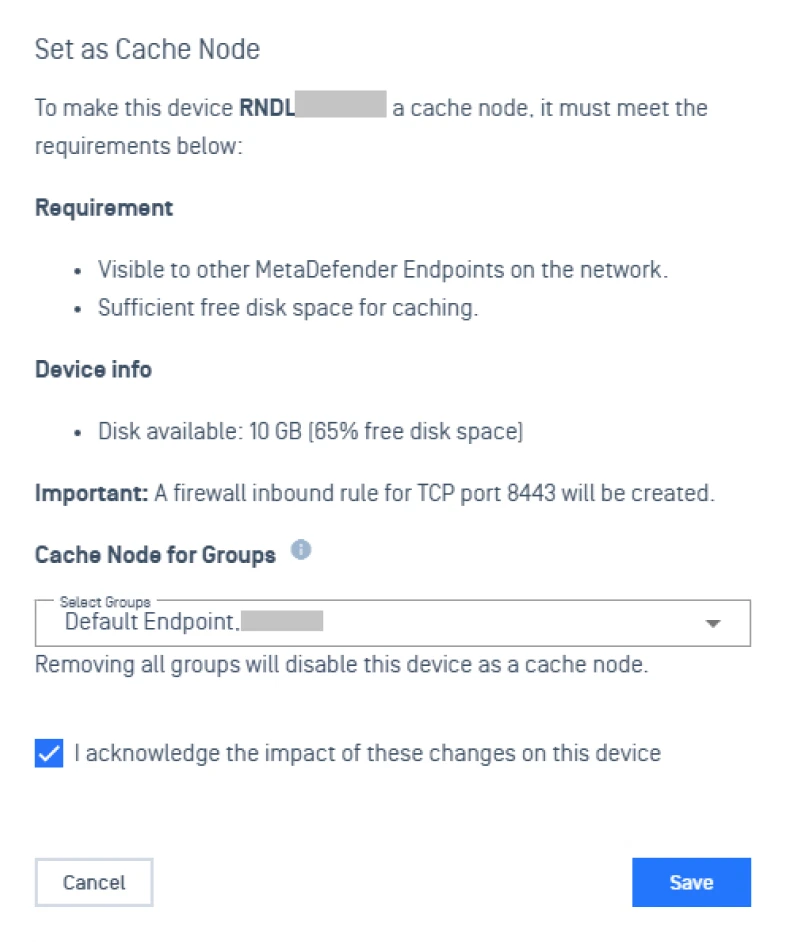
Distribute patch content via local cache nodes to reduce bandwidth usage and accelerate deployment across large or distributed estates.
- My OPSWAT Central Management
- My OPSWAT Central Management
- My OPSWAT Central Management
Product Walkthrough
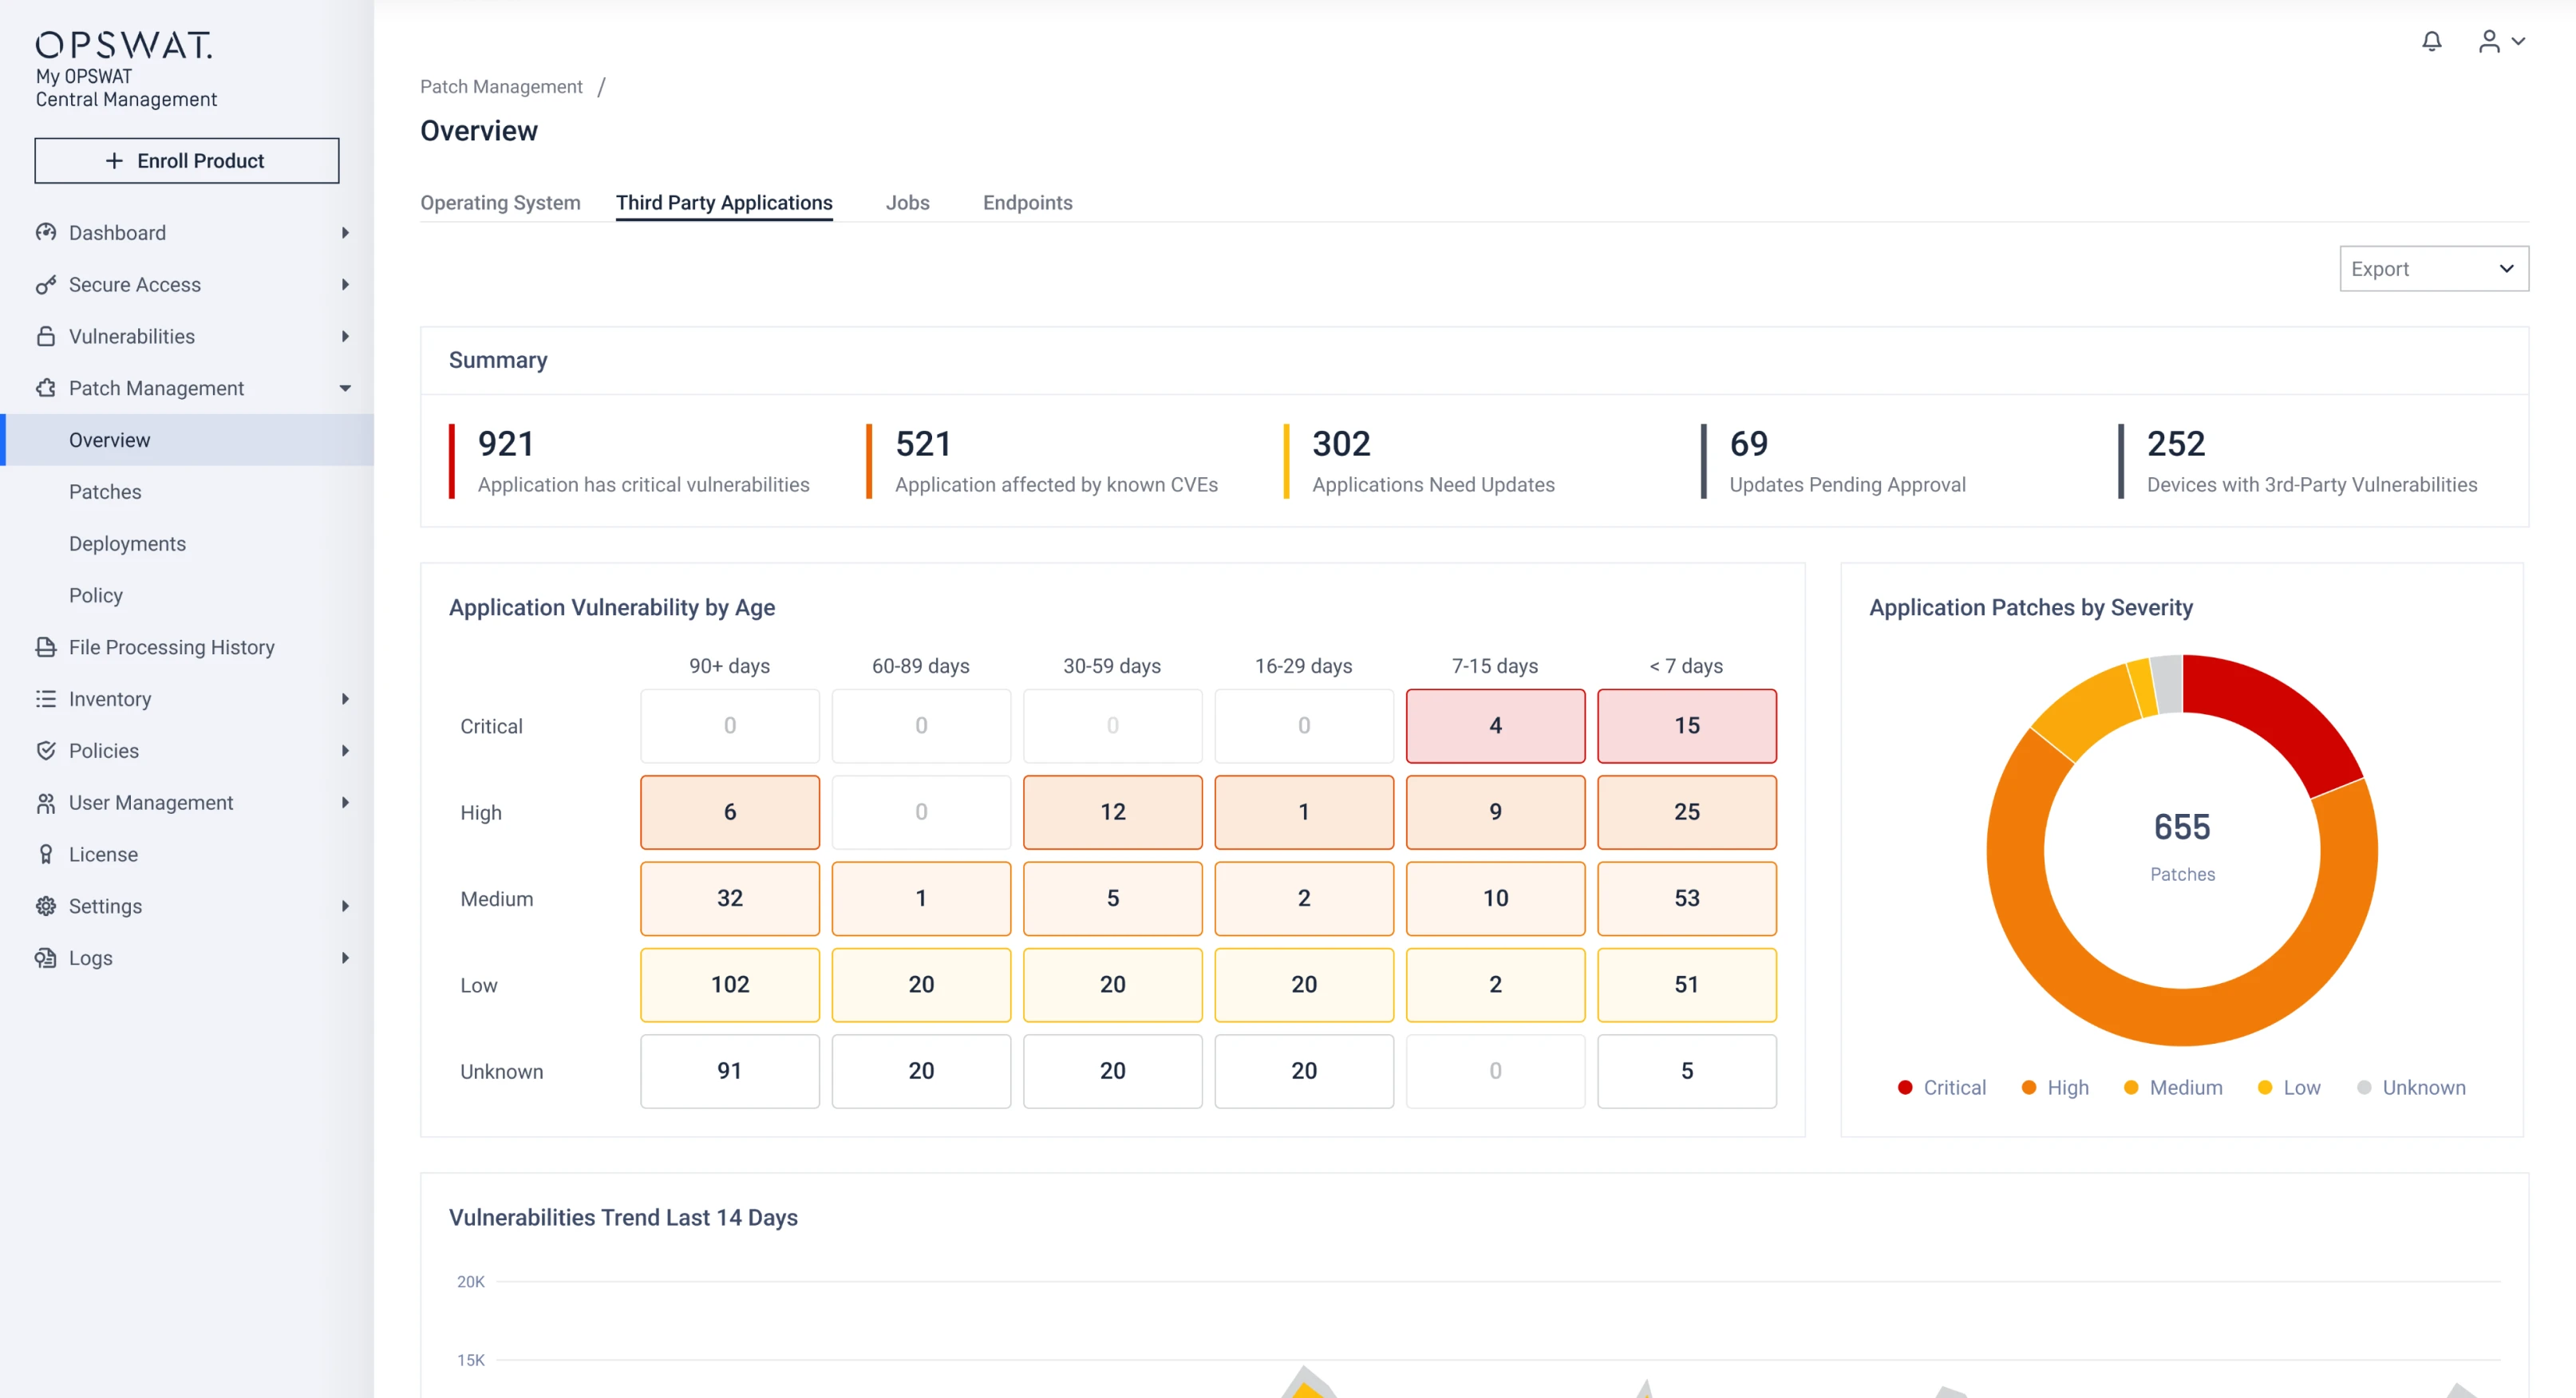
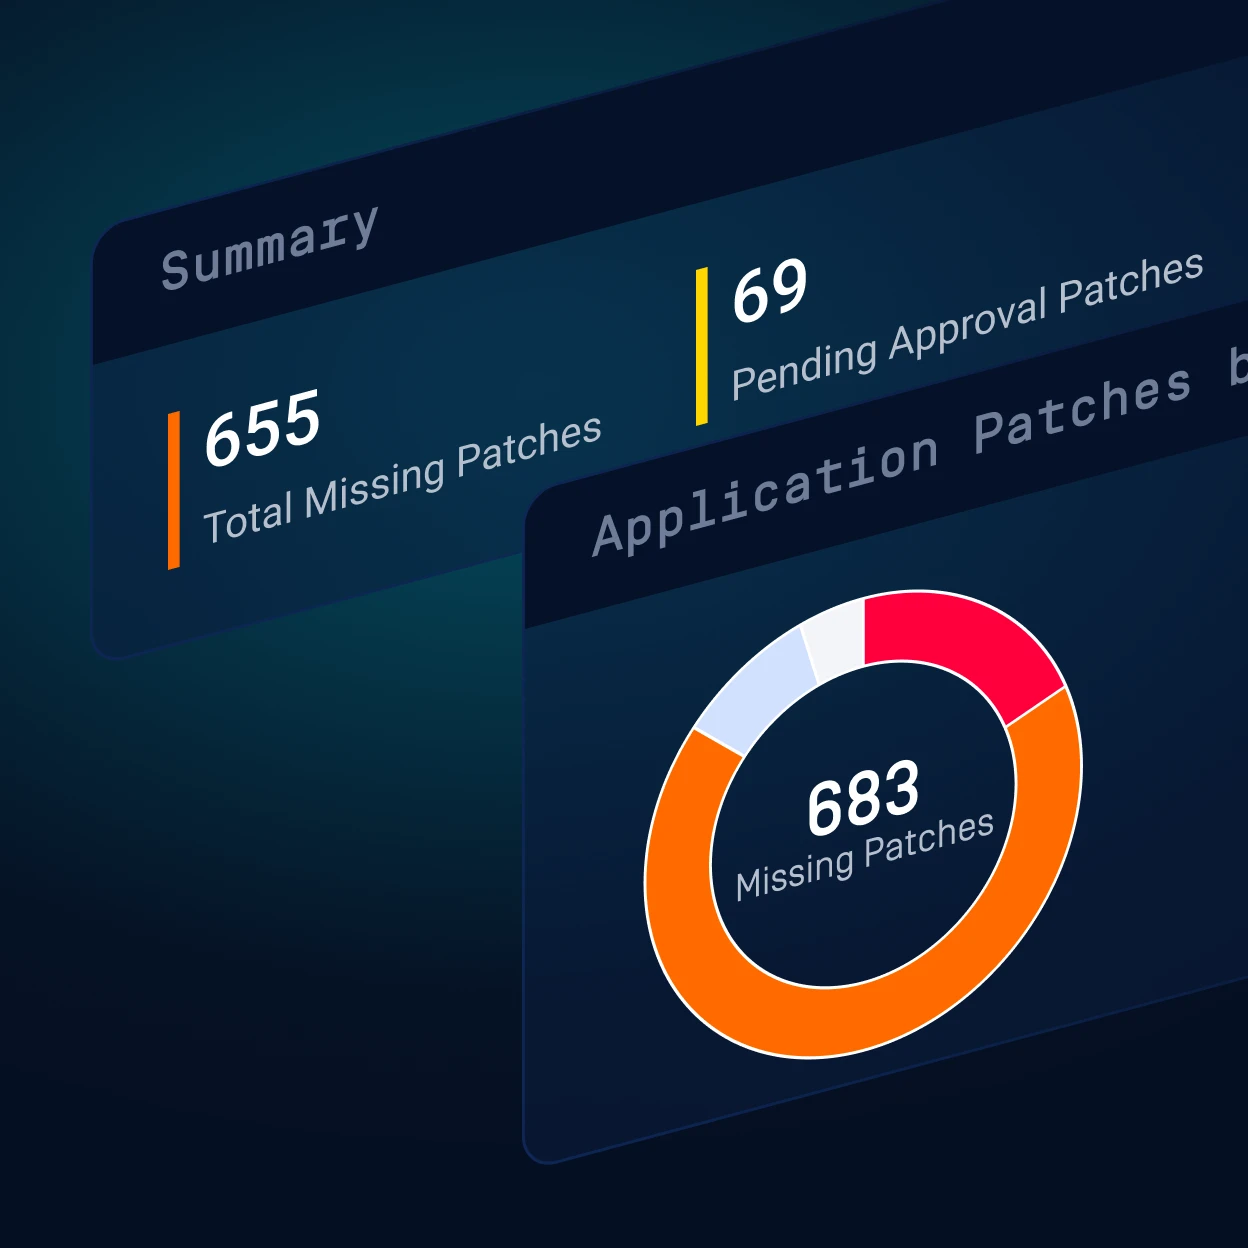
For seamless monitoring and management, you can view a centralized, real-time overview of the organization's patching status via My OPSWAT™ Central Management. It visualizes key actionable insights on patches and deployments, prioritizing high-risk vulnerabilities for faster remediation.
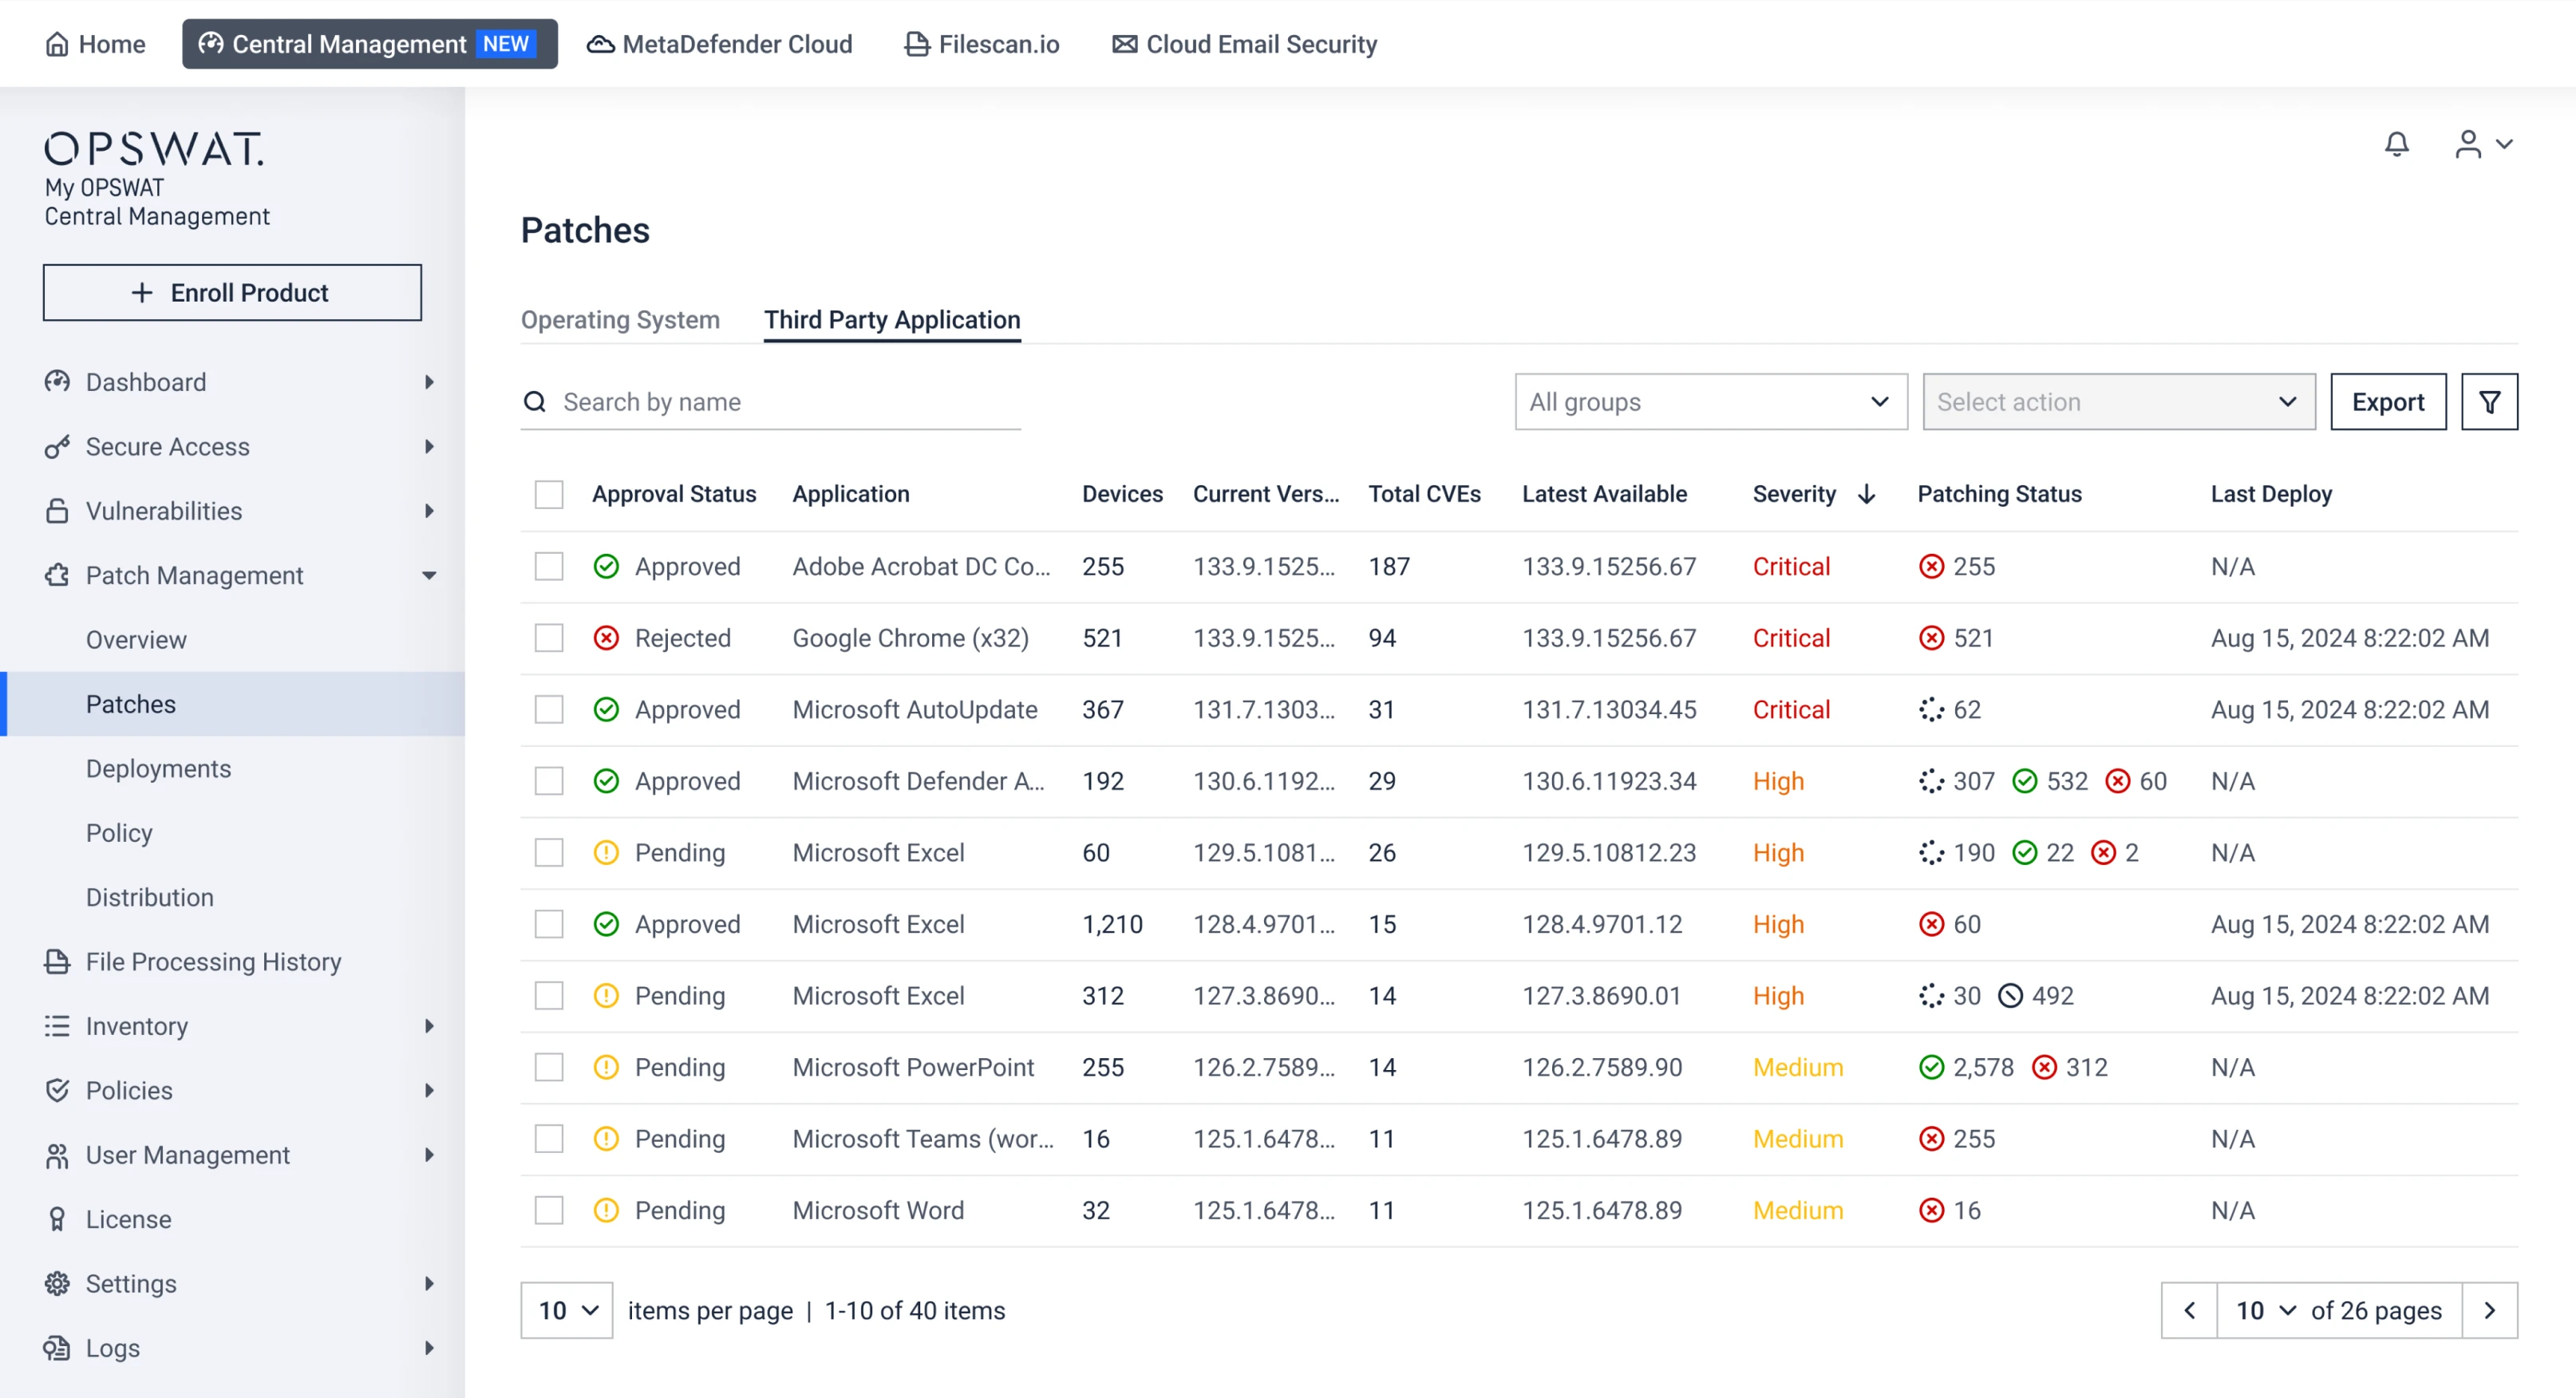
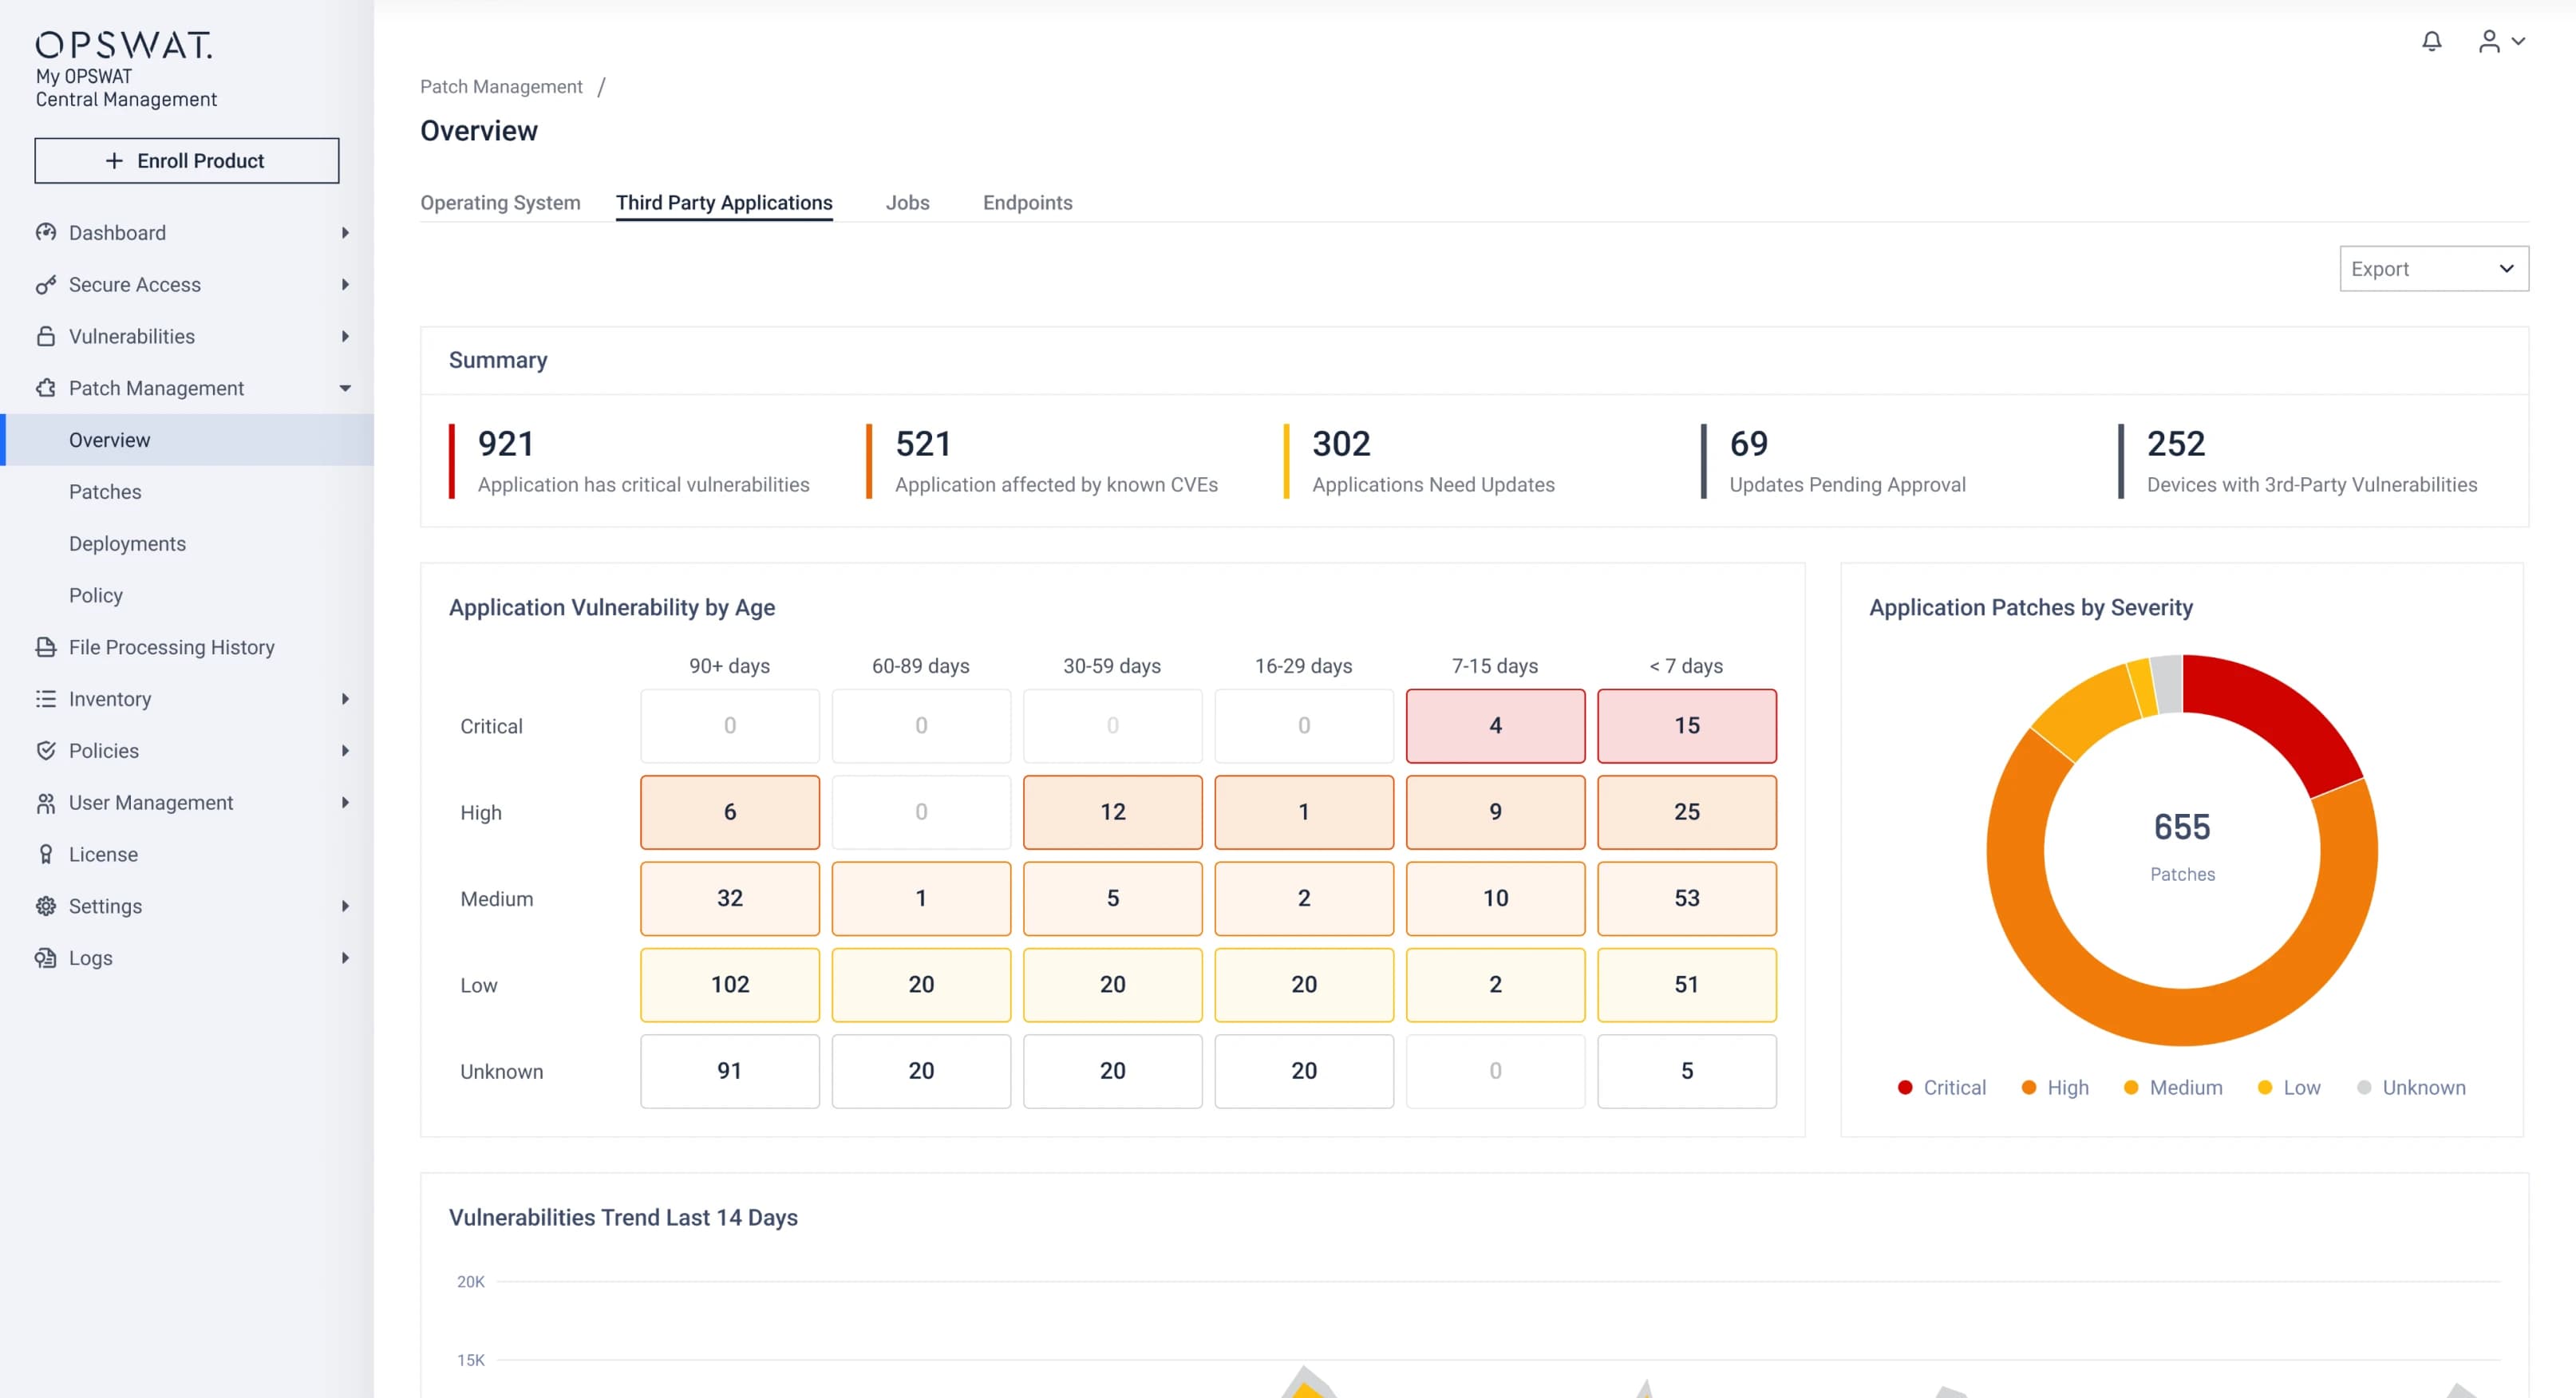 View a Real-Time Dashboard
For seamless monitoring and management, you can view a centralized, real-time overview of the organization's patching status via My OPSWAT™ Central Management. It visualizes key actionable insights on patches and deployments, prioritizing high-risk vulnerabilities for faster remediation.
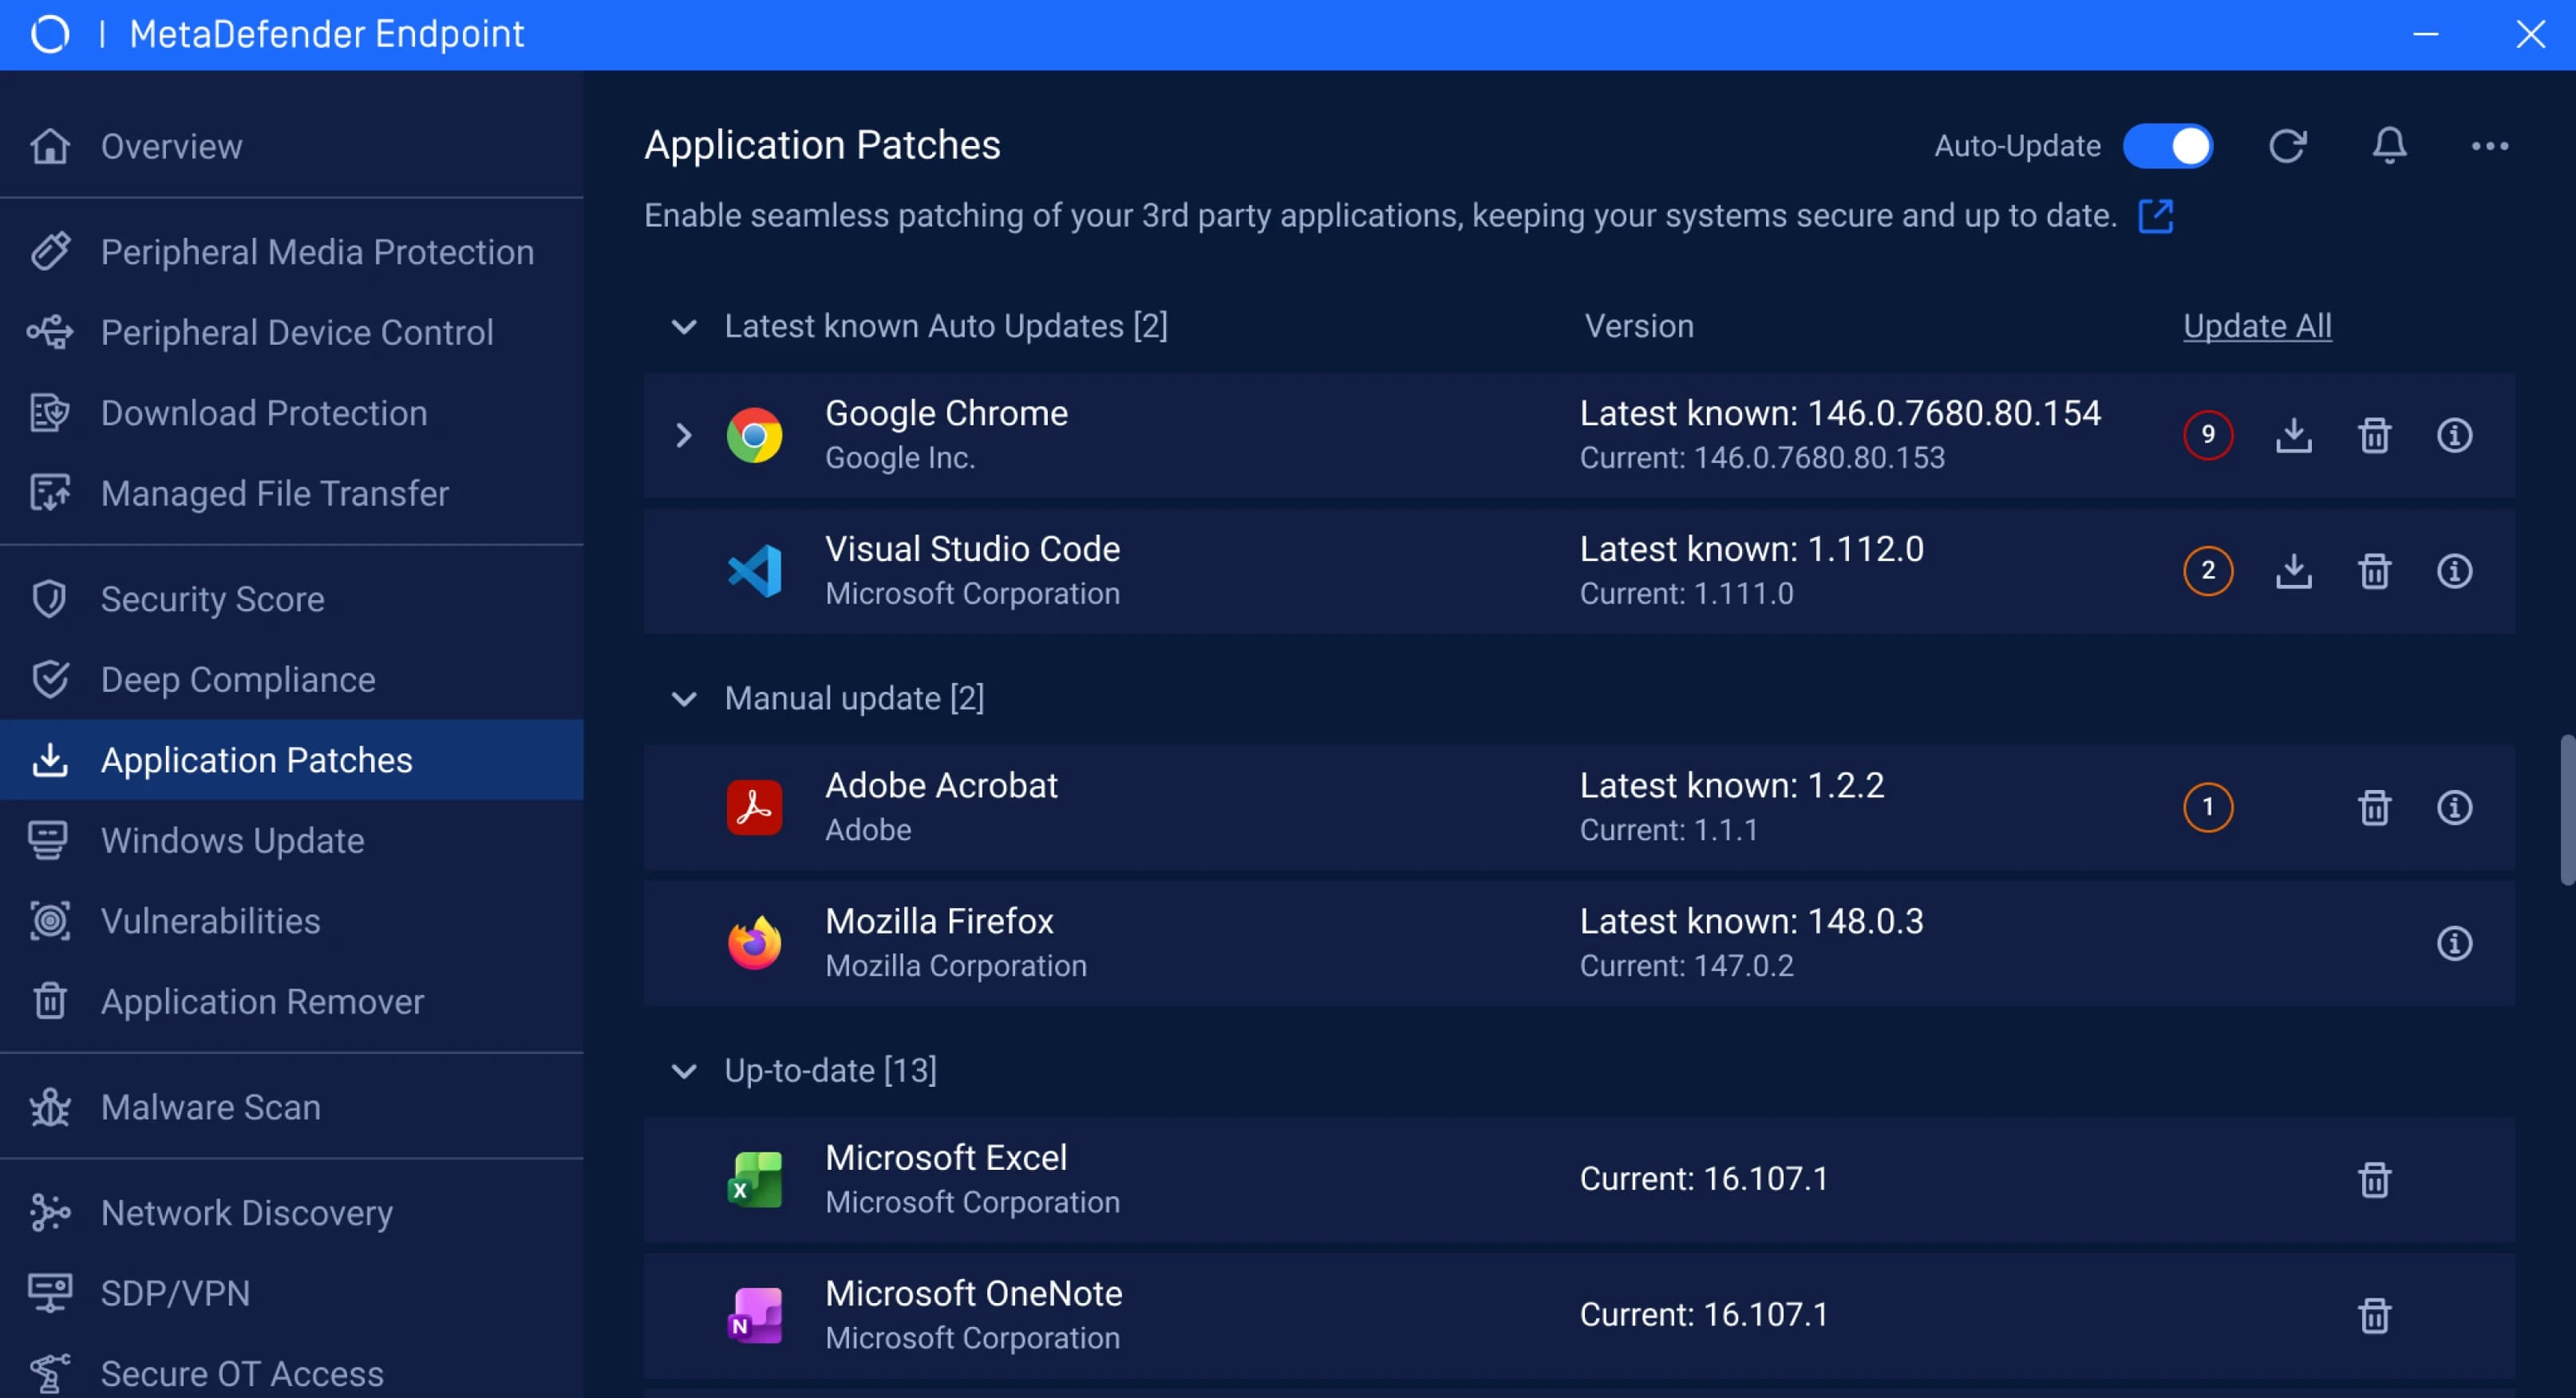 Actively Detect Missing Patch
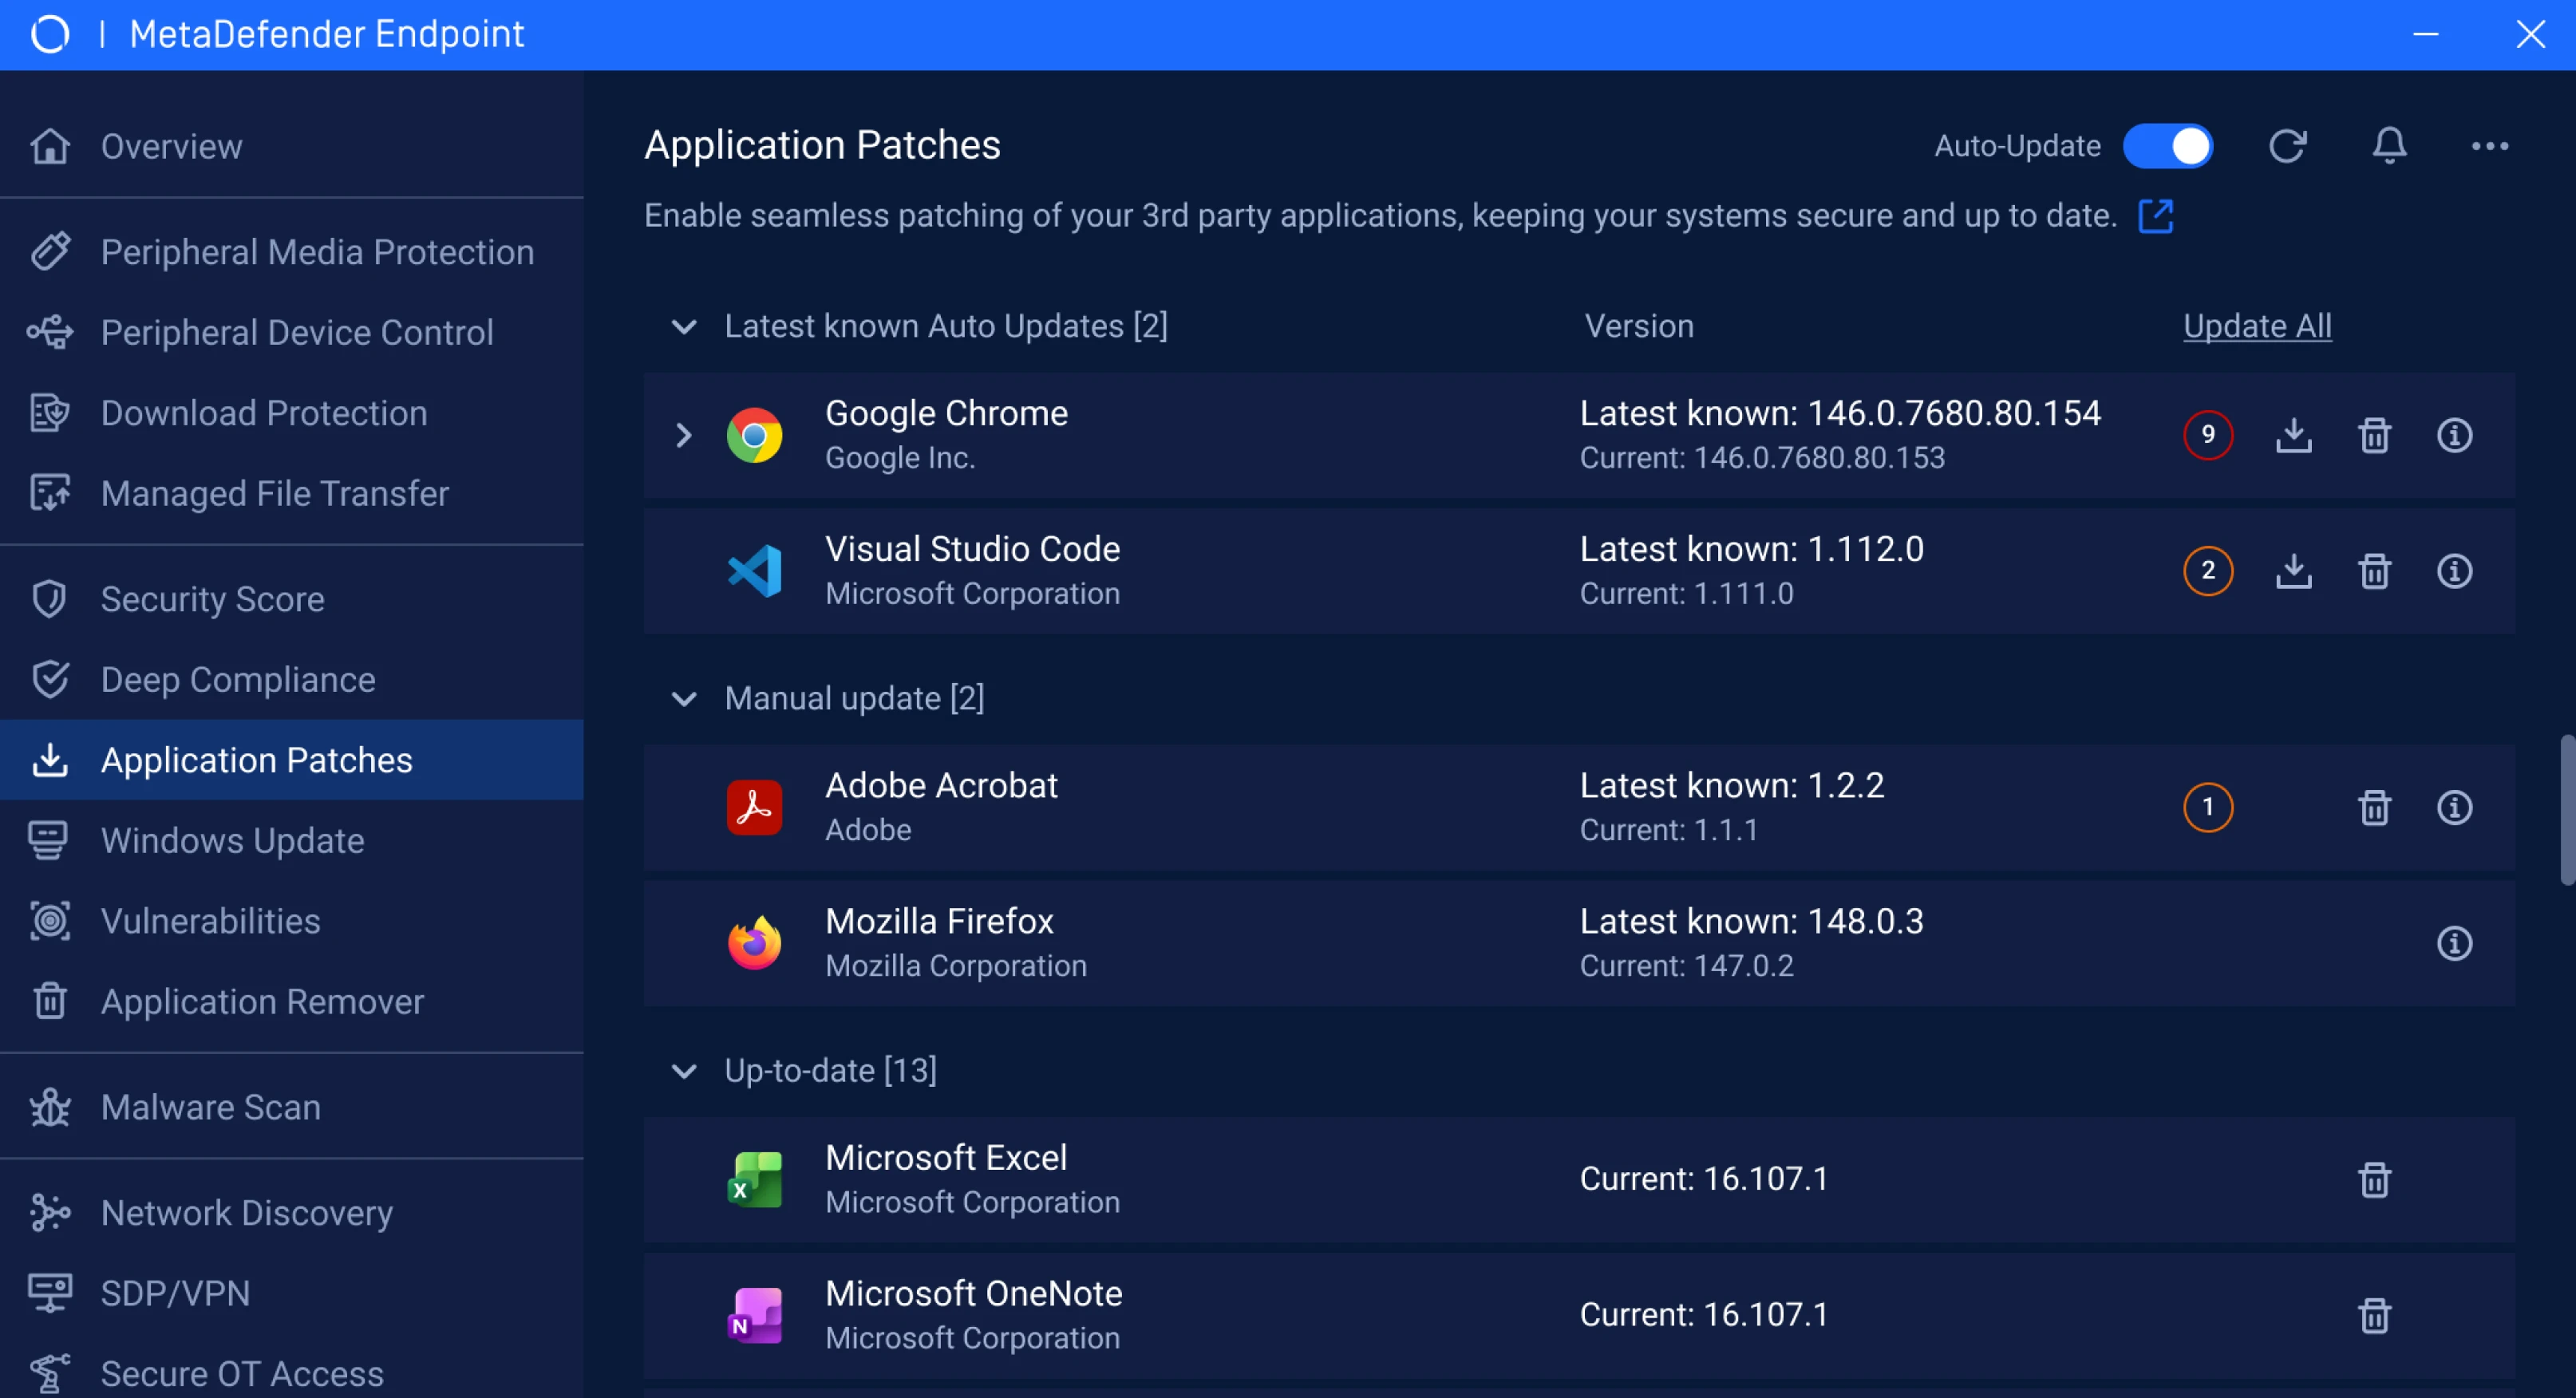
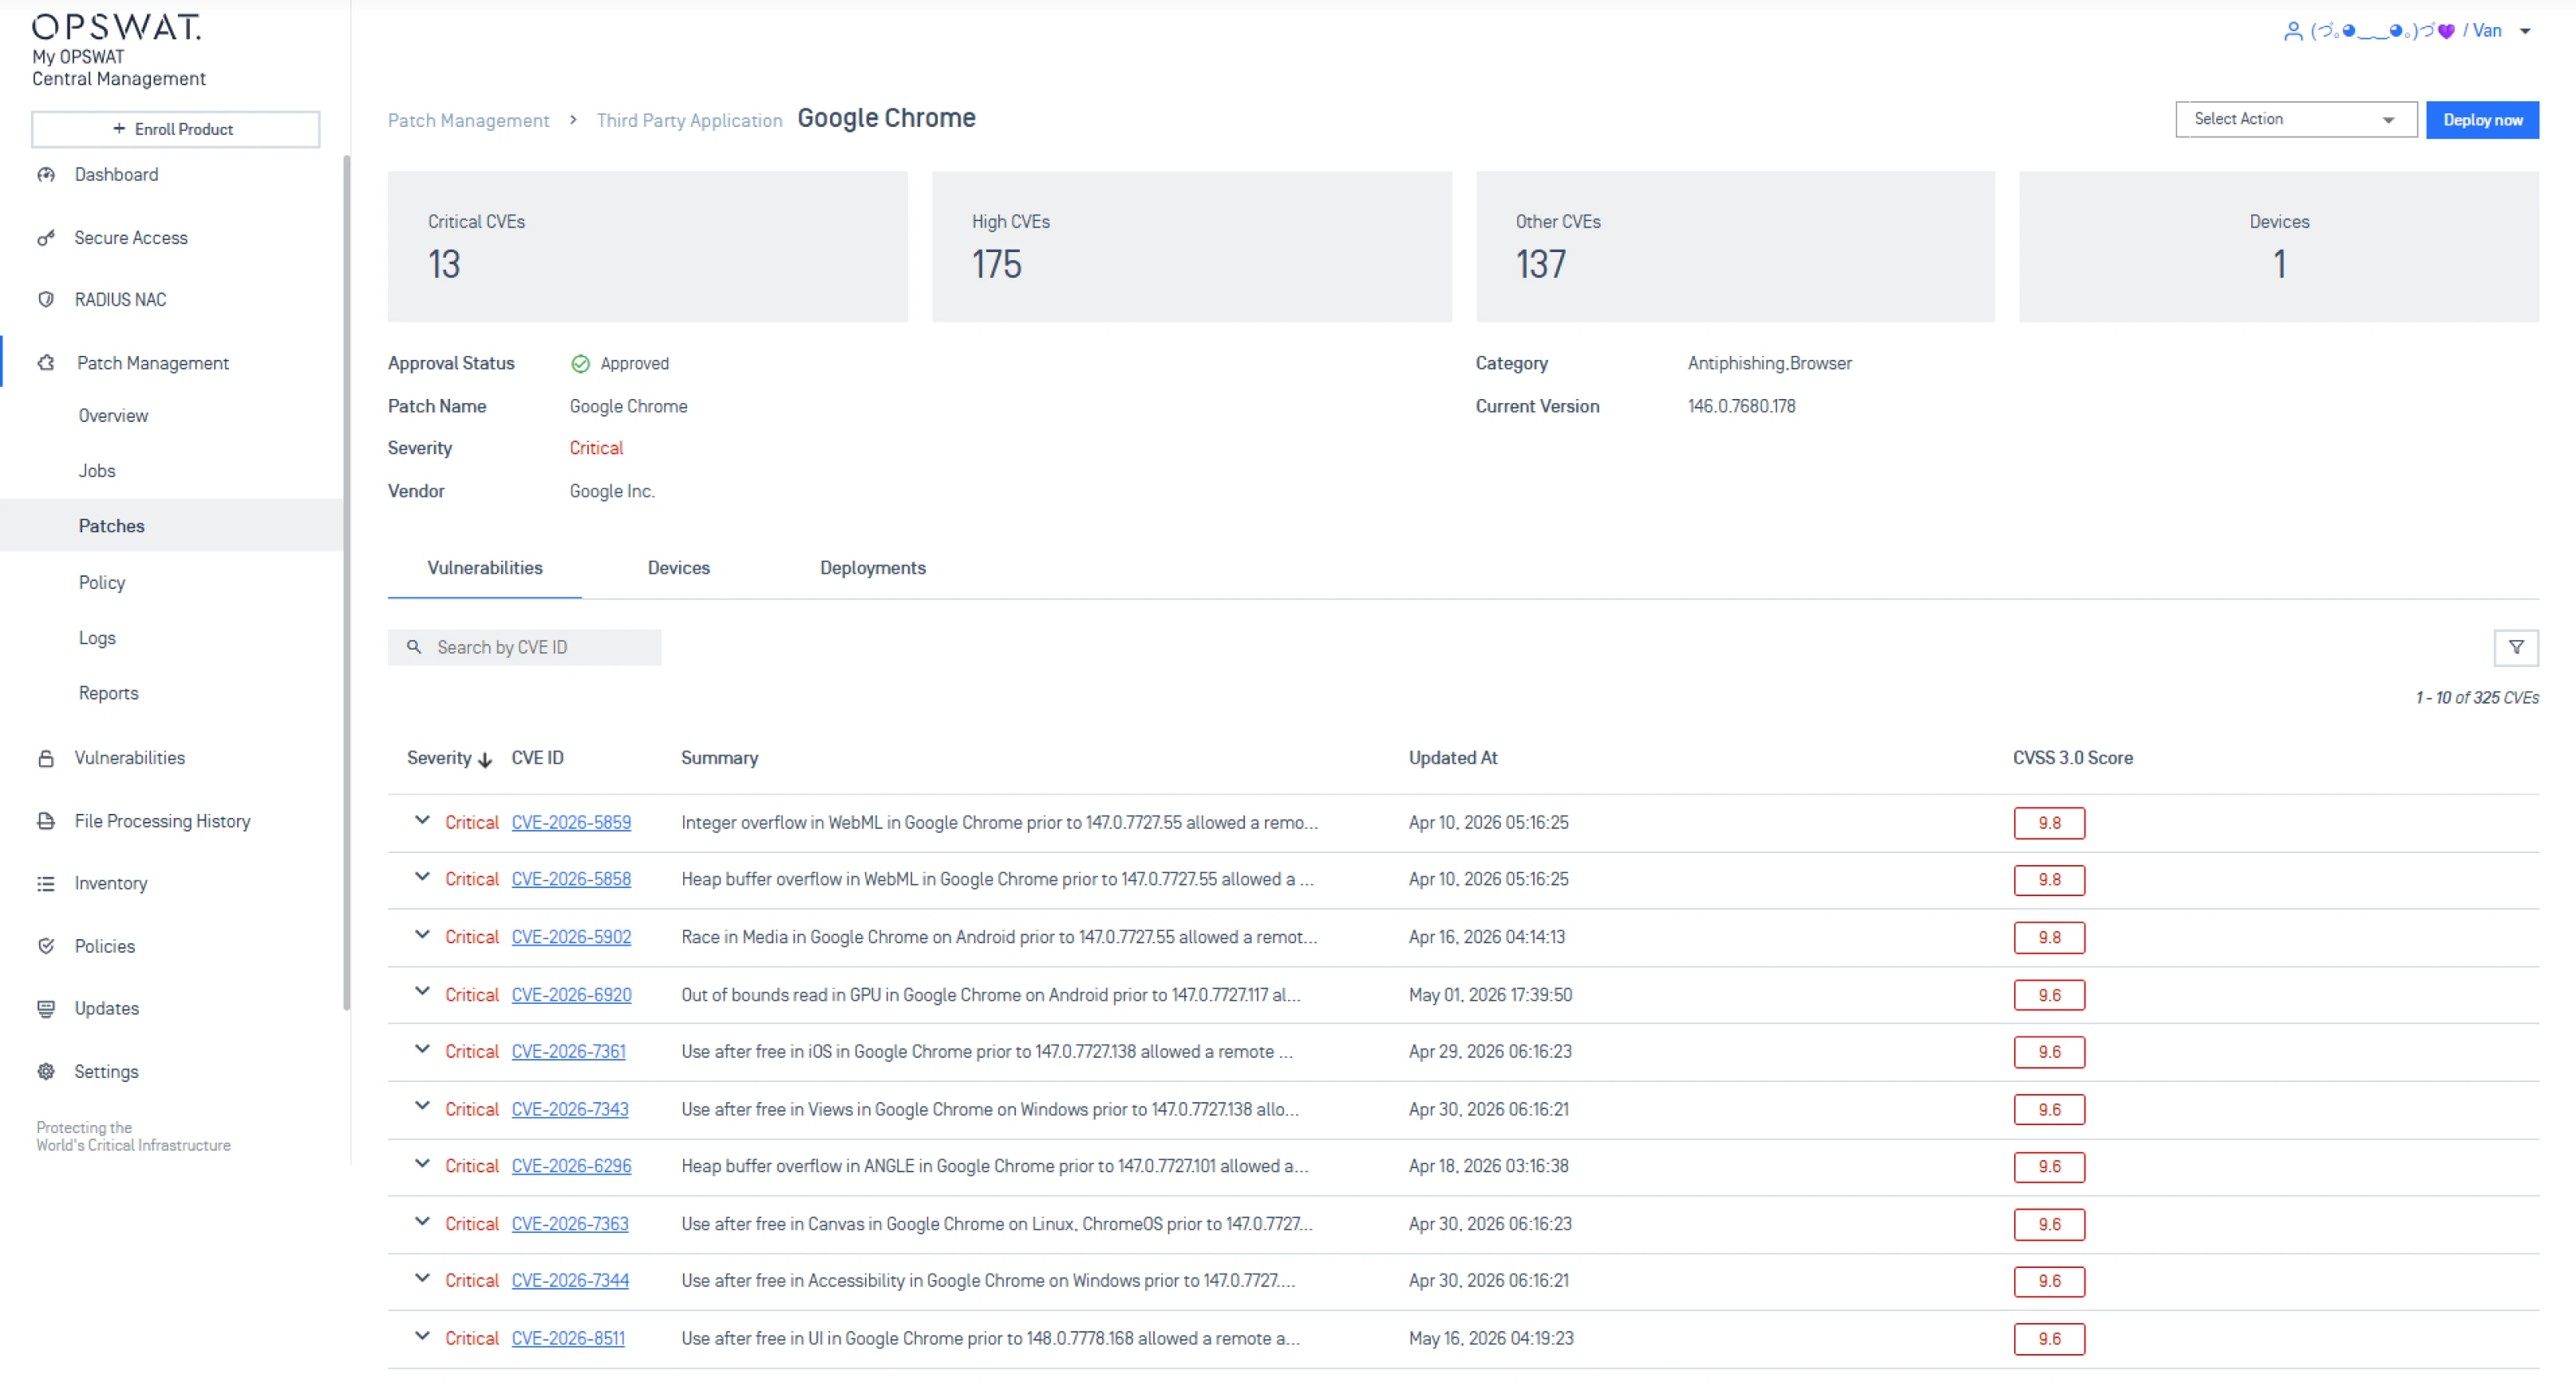
MetaDefender Endpoint actively detects and reports missing patches
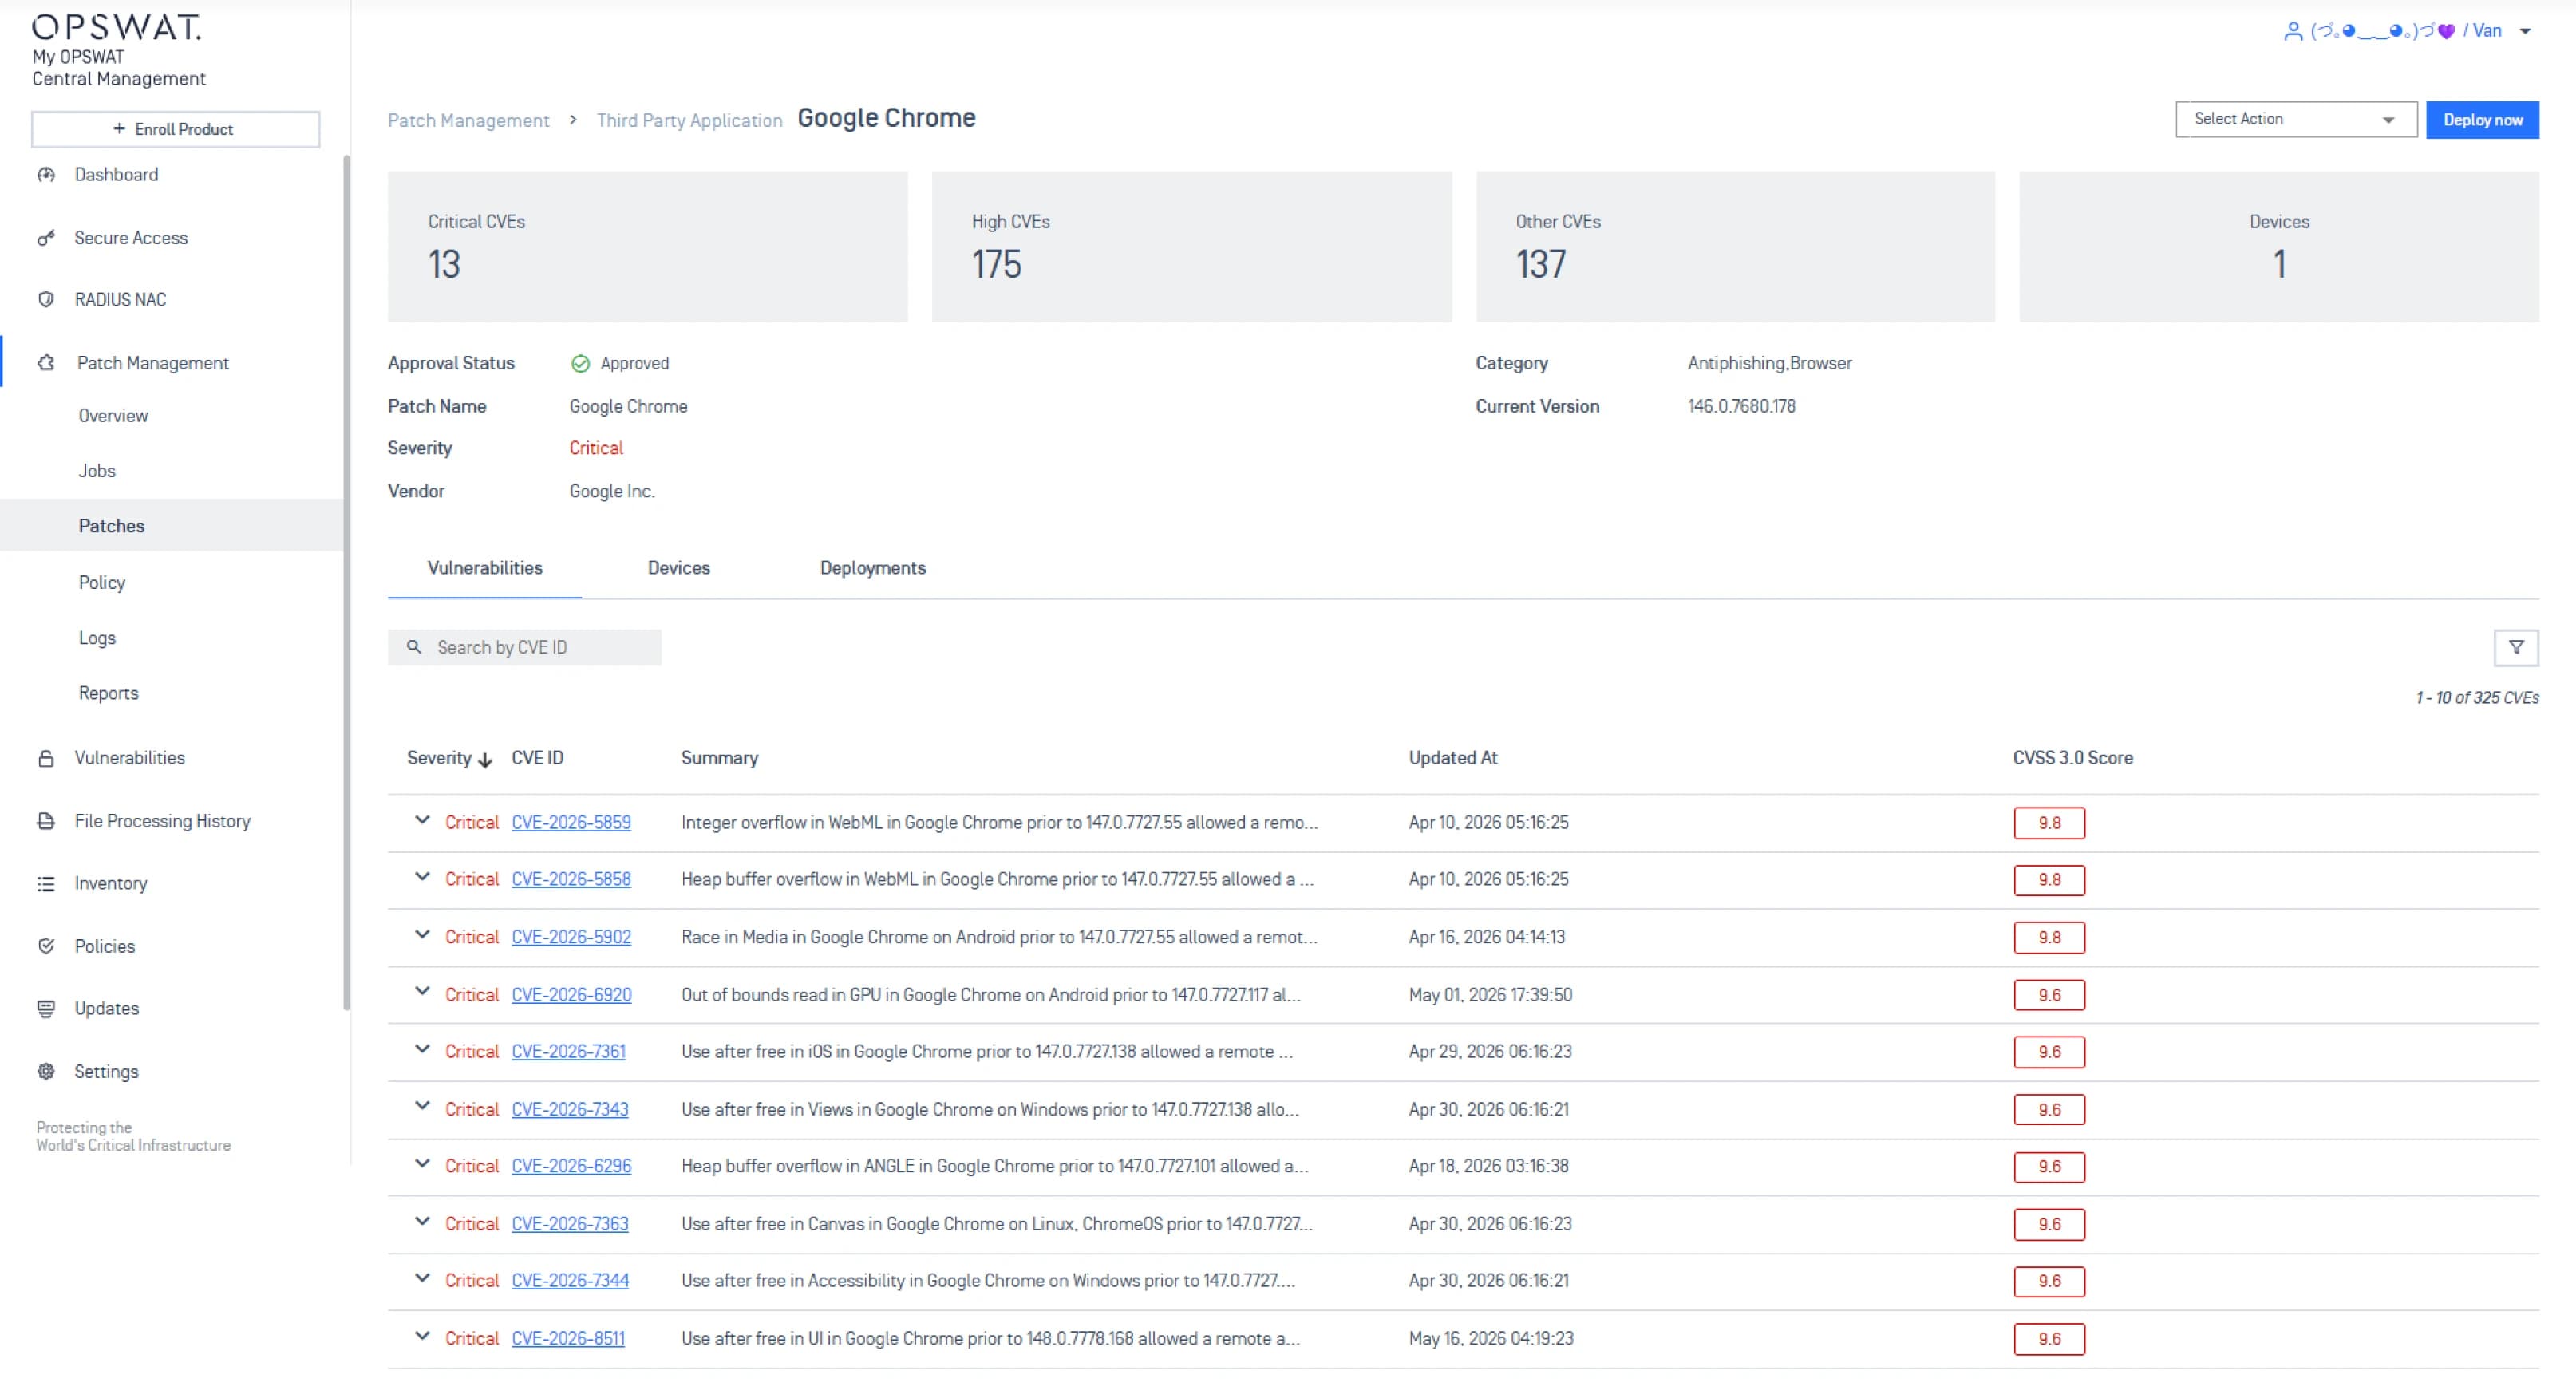 Real-time Visibility
When a vulnerability is detected, it's instantly highlighted in the management console in My OPSWAT Central Management with severity level, CVE details, and affected asset information.
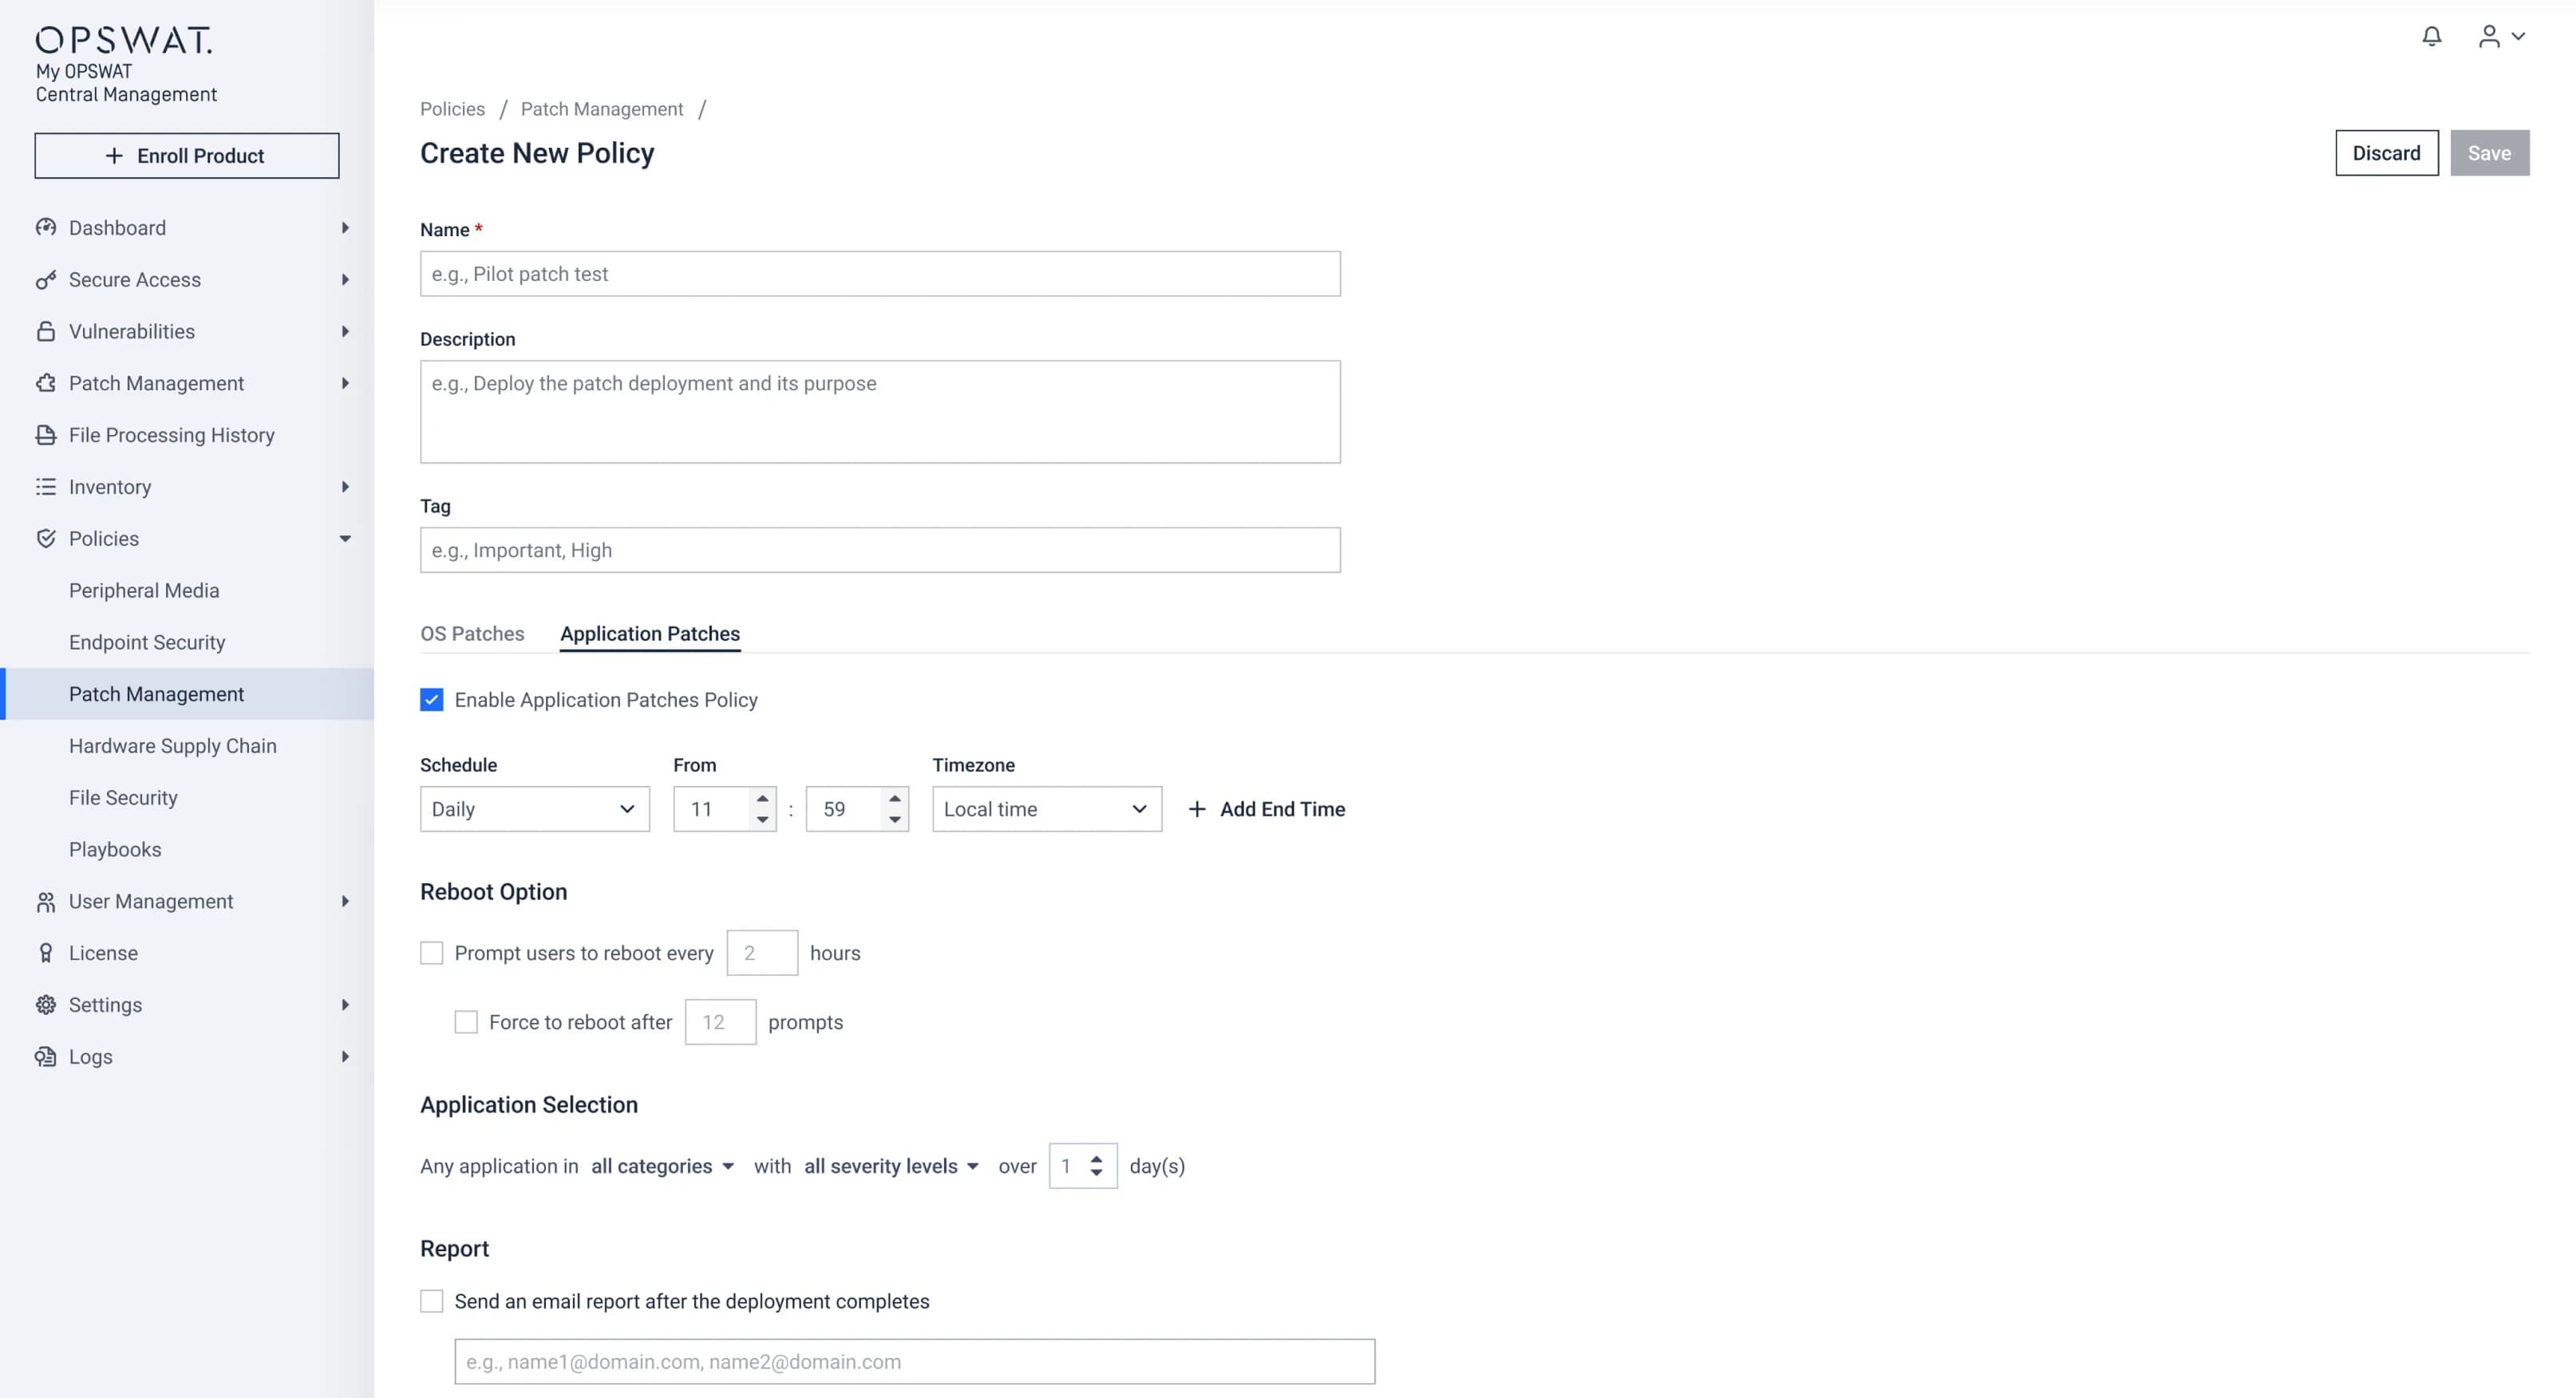 Schedule Patching with Flexibility
Through the management console in My OPSWAT Central Management, administrators review the flagged vulnerability, select affected endpoints or groups, and schedule deployment, setting up the rollout window, and customizing reboot behavior.
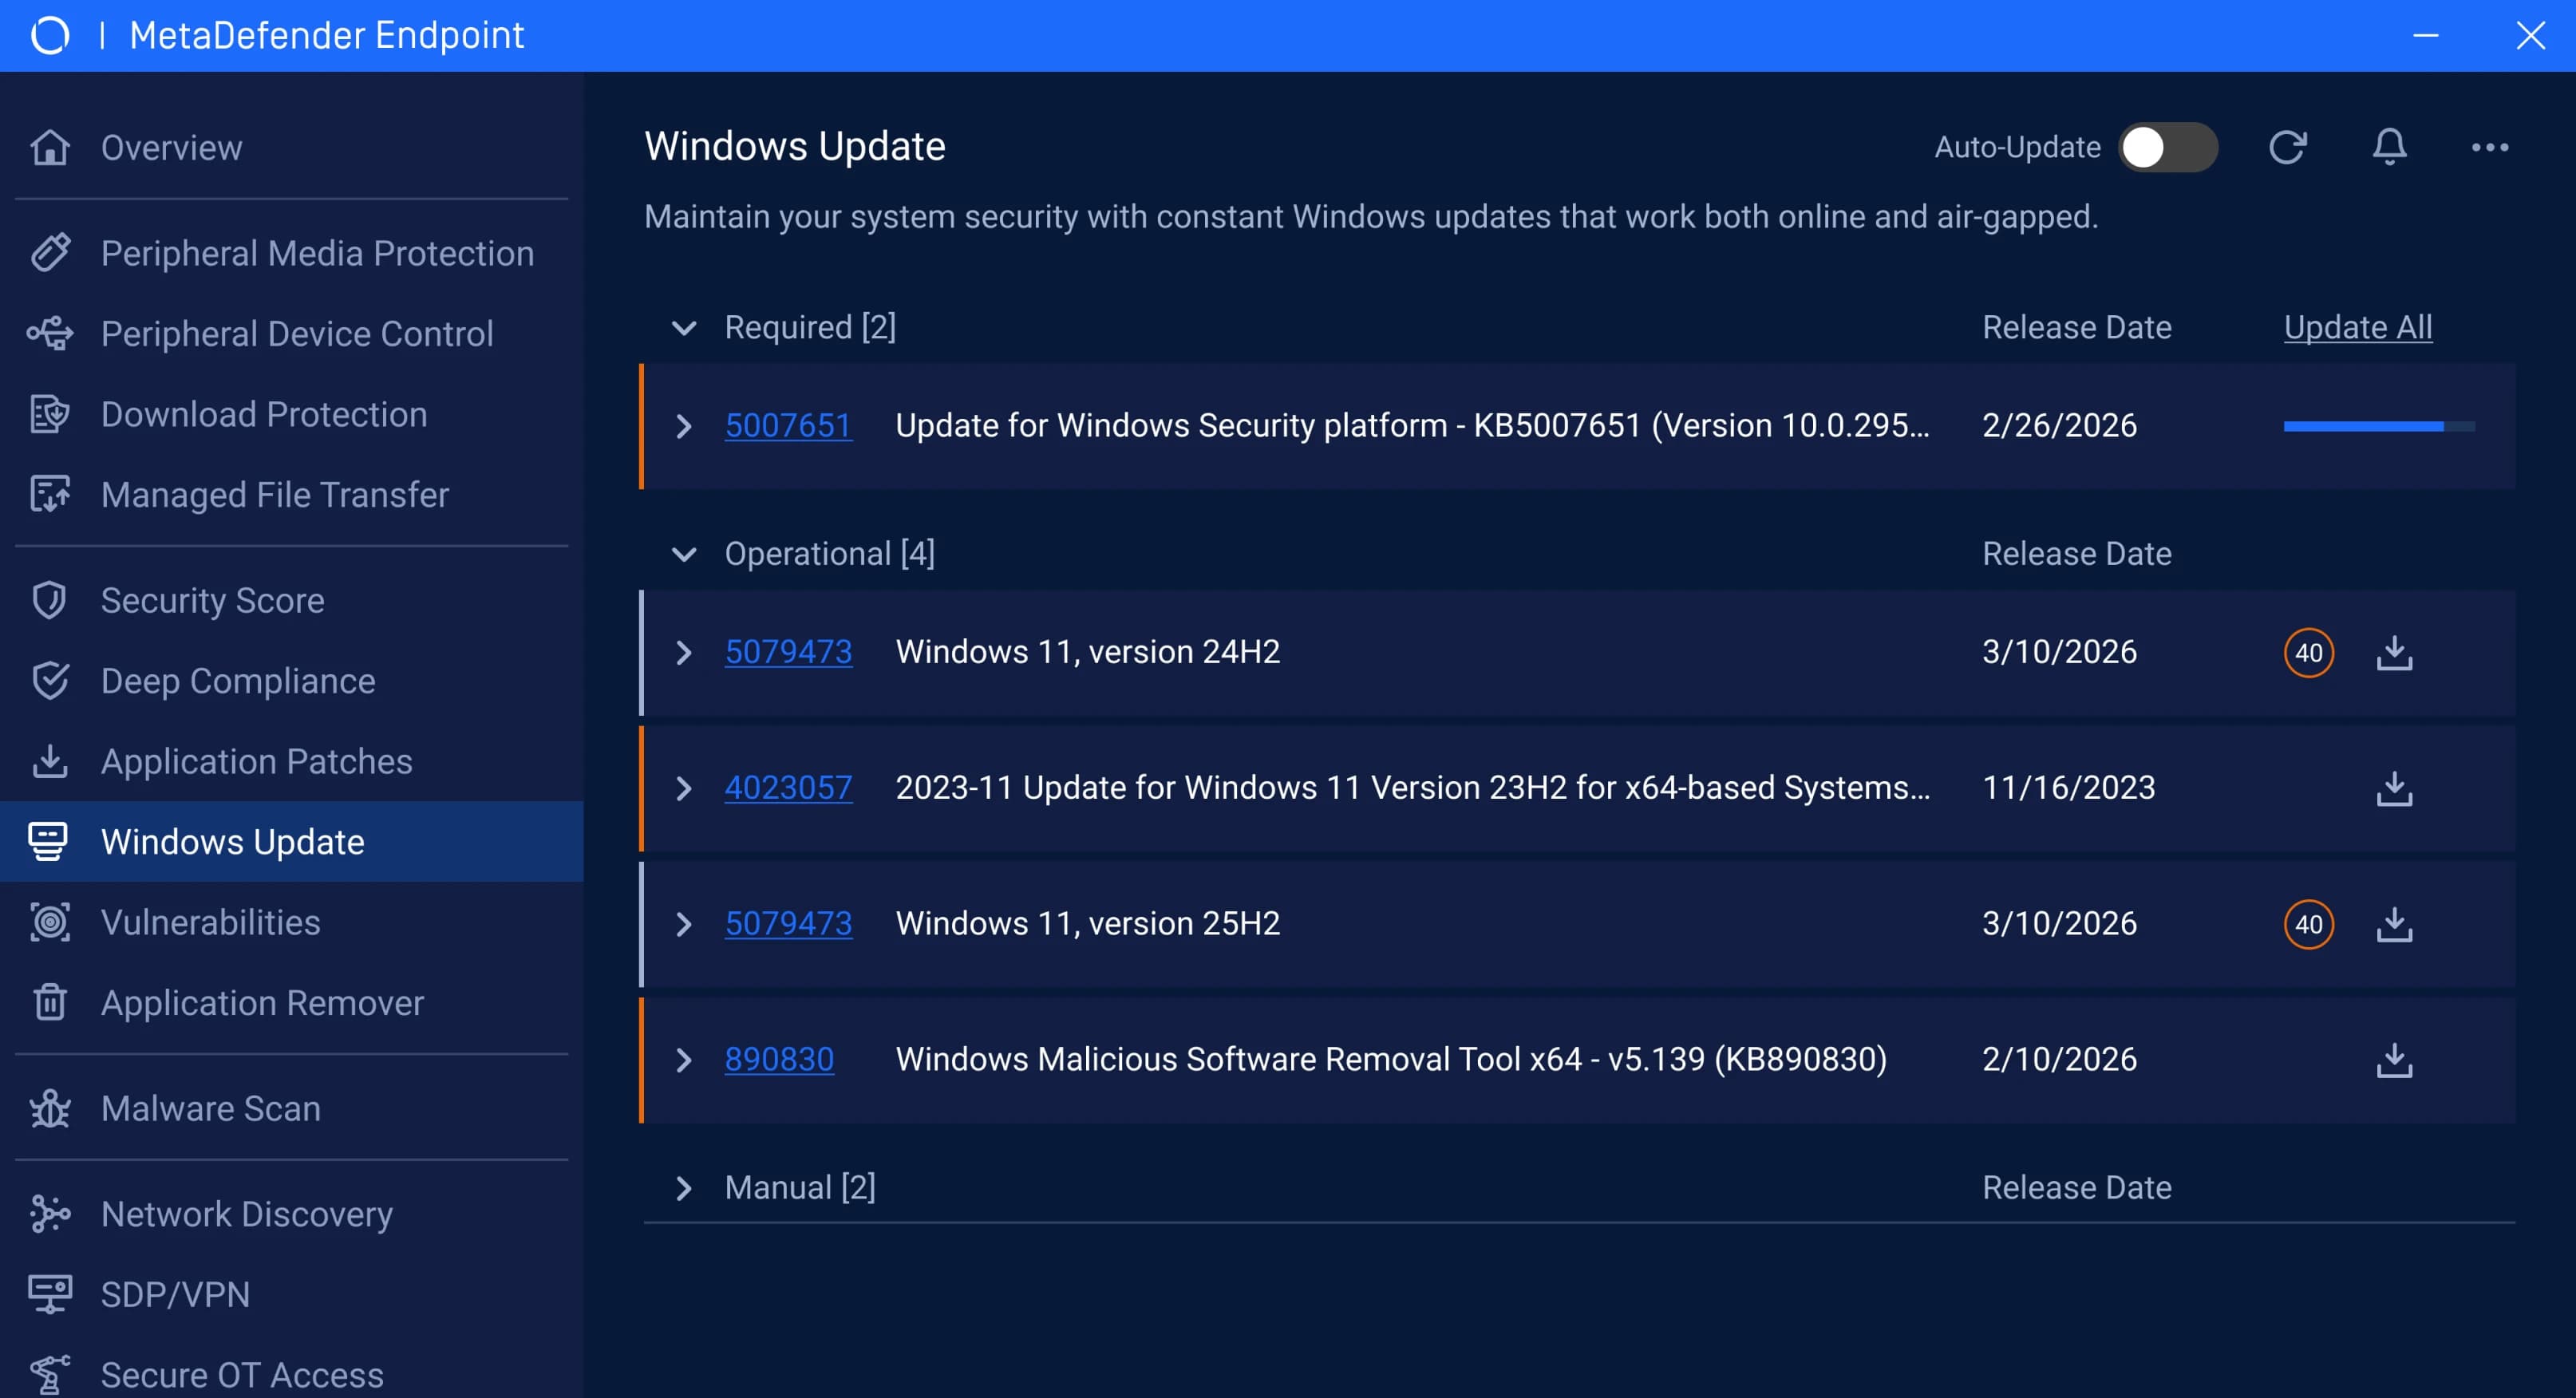 Automatically Deploy Across Endpoints
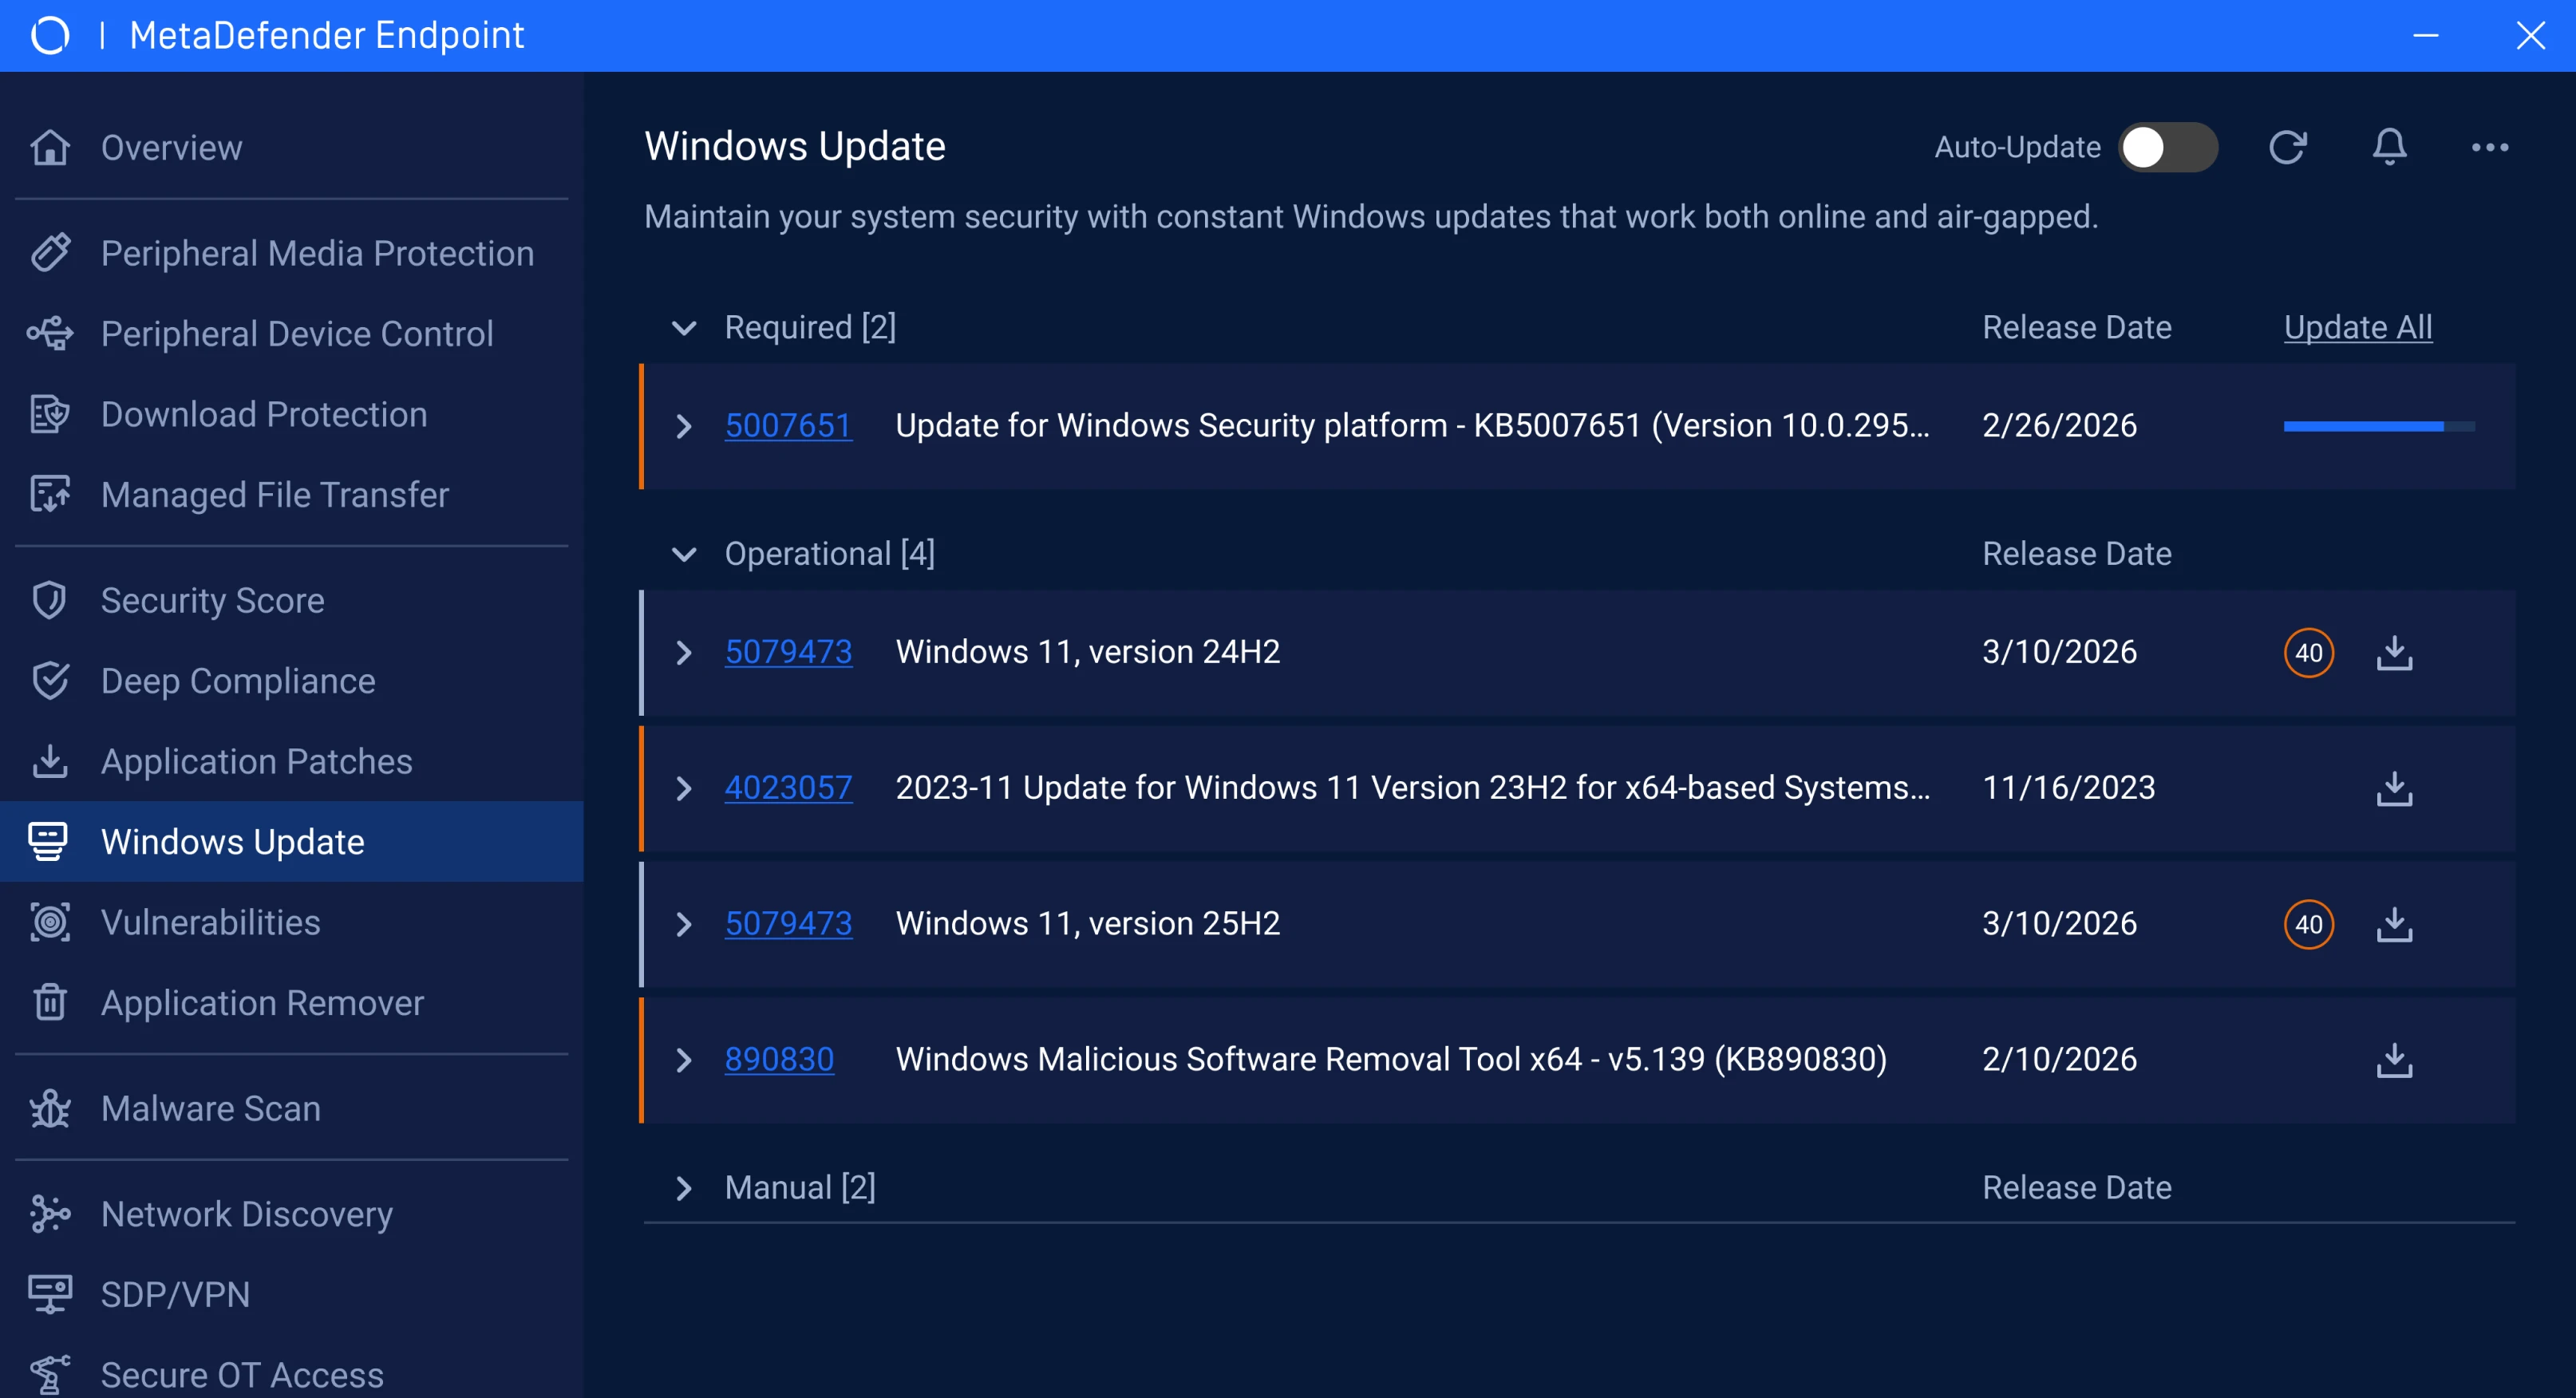
At the scheduled time, the platform automatically distributes verified patches across all targeted endpoints, no manual intervention is needed.
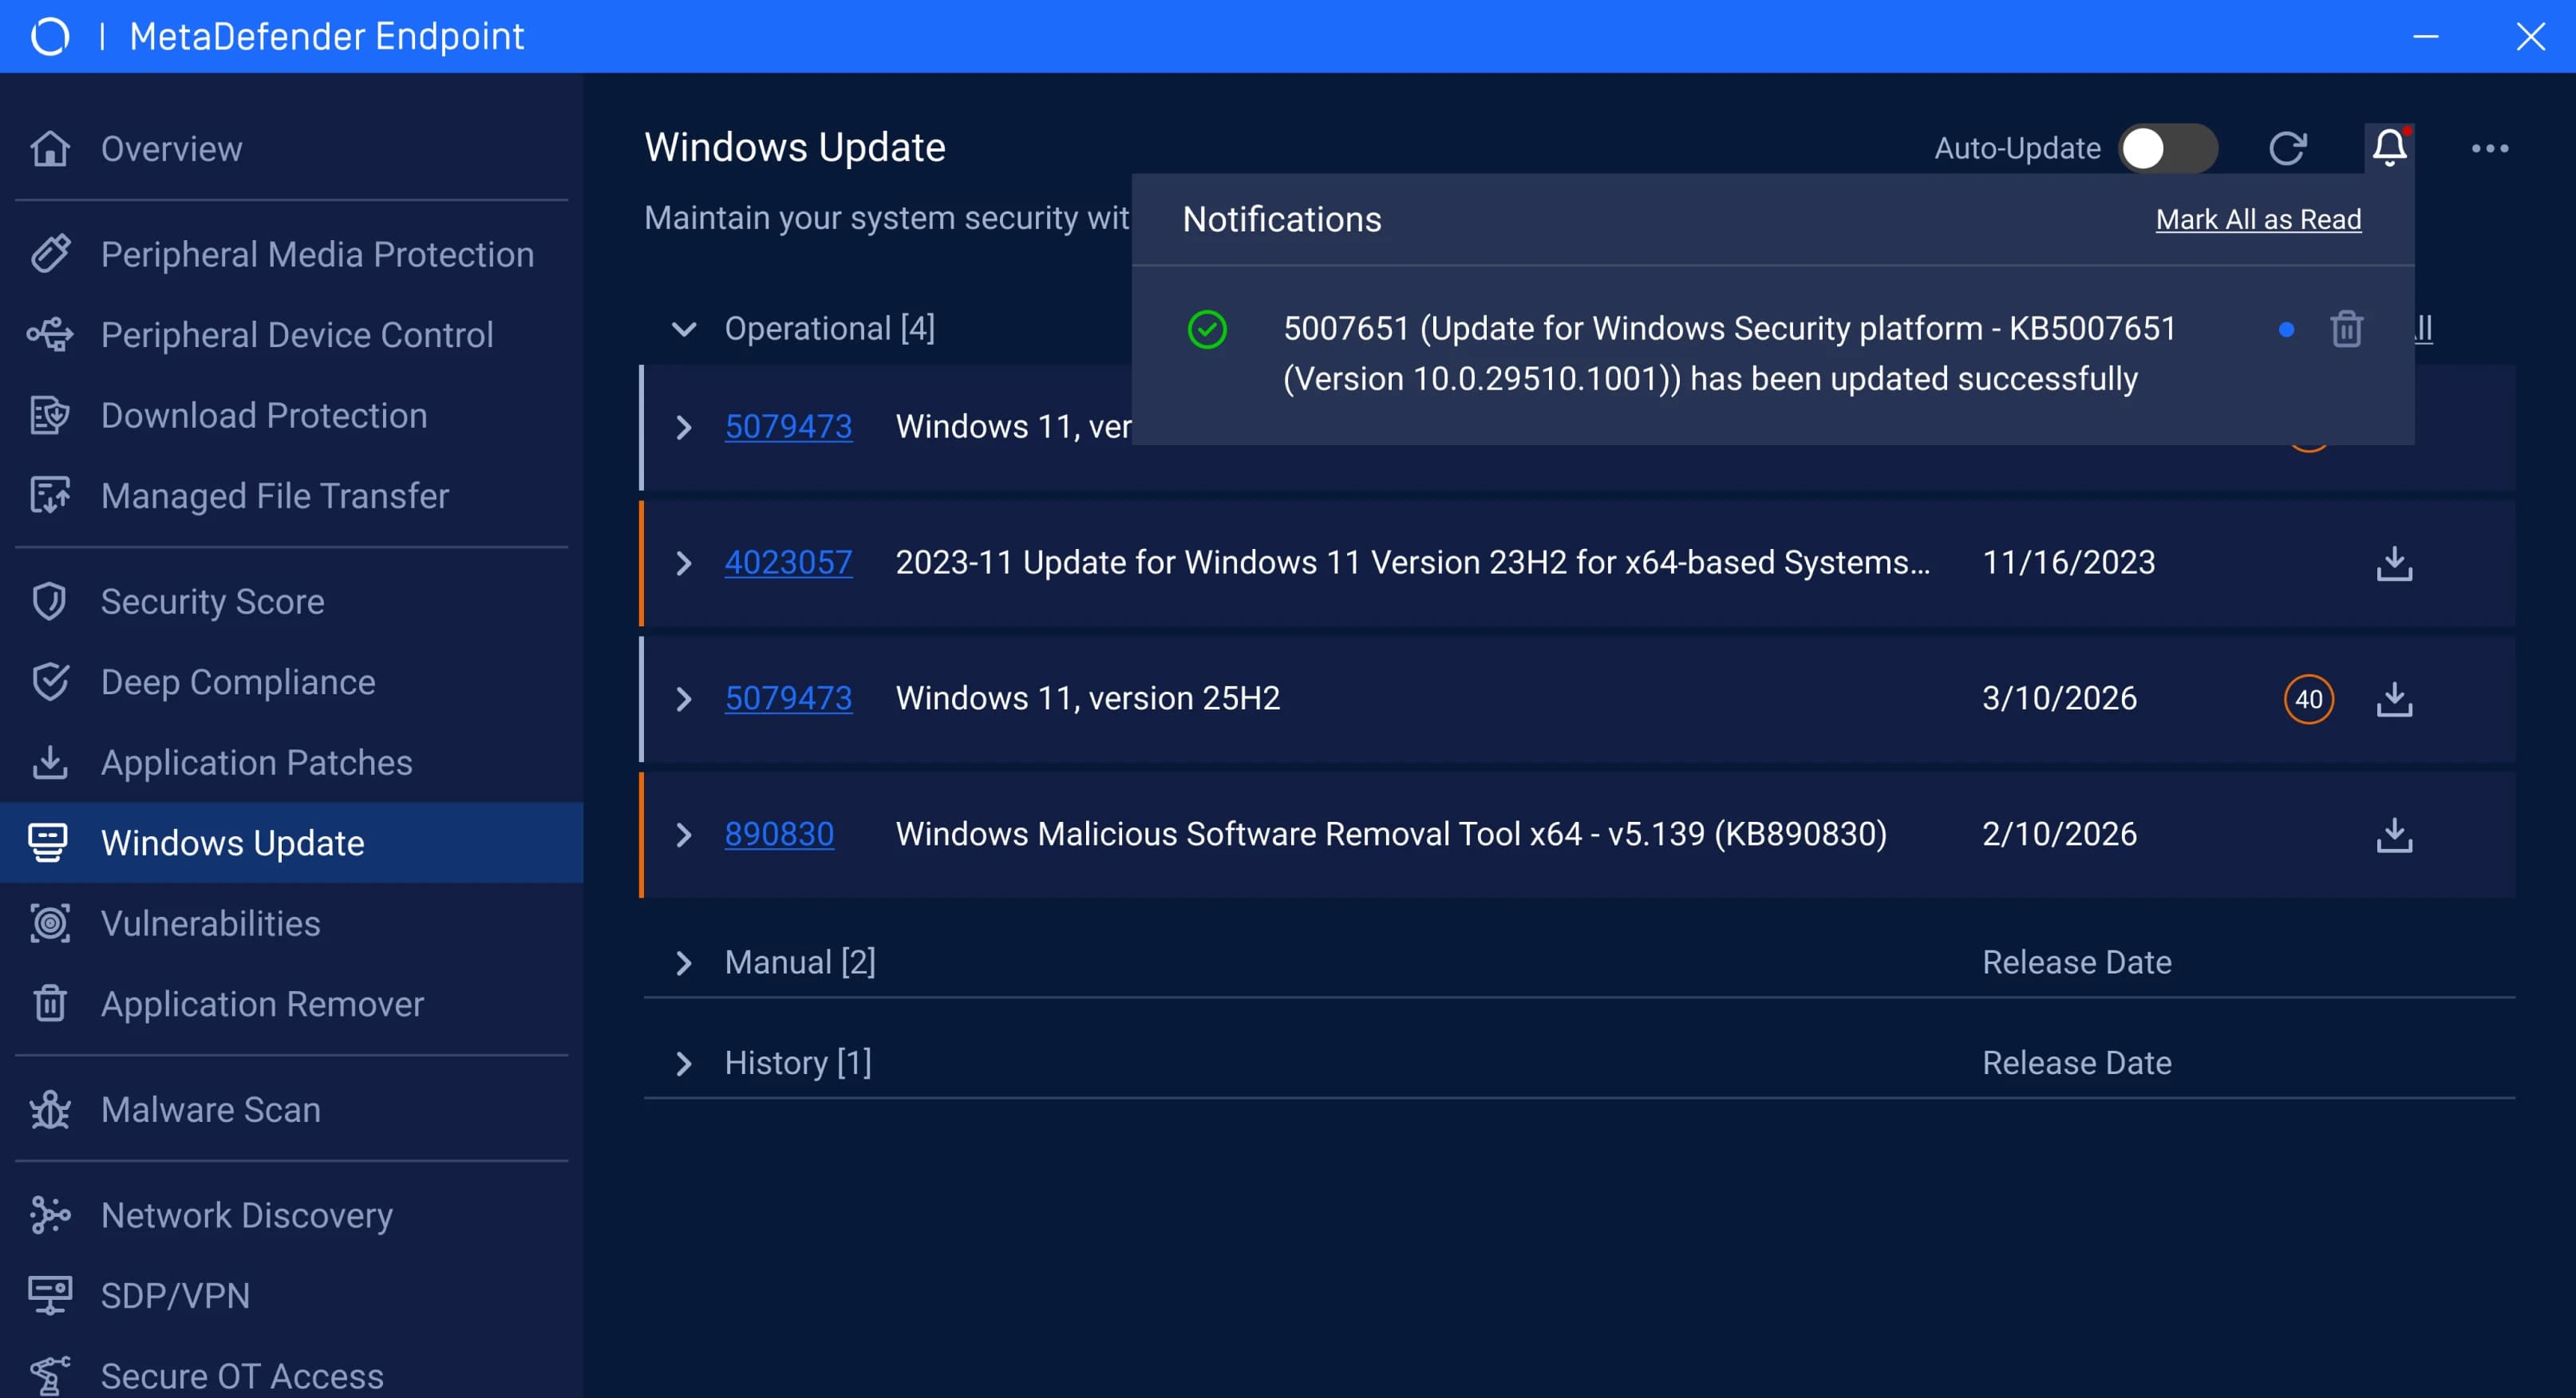 Receive Real-time Notifications
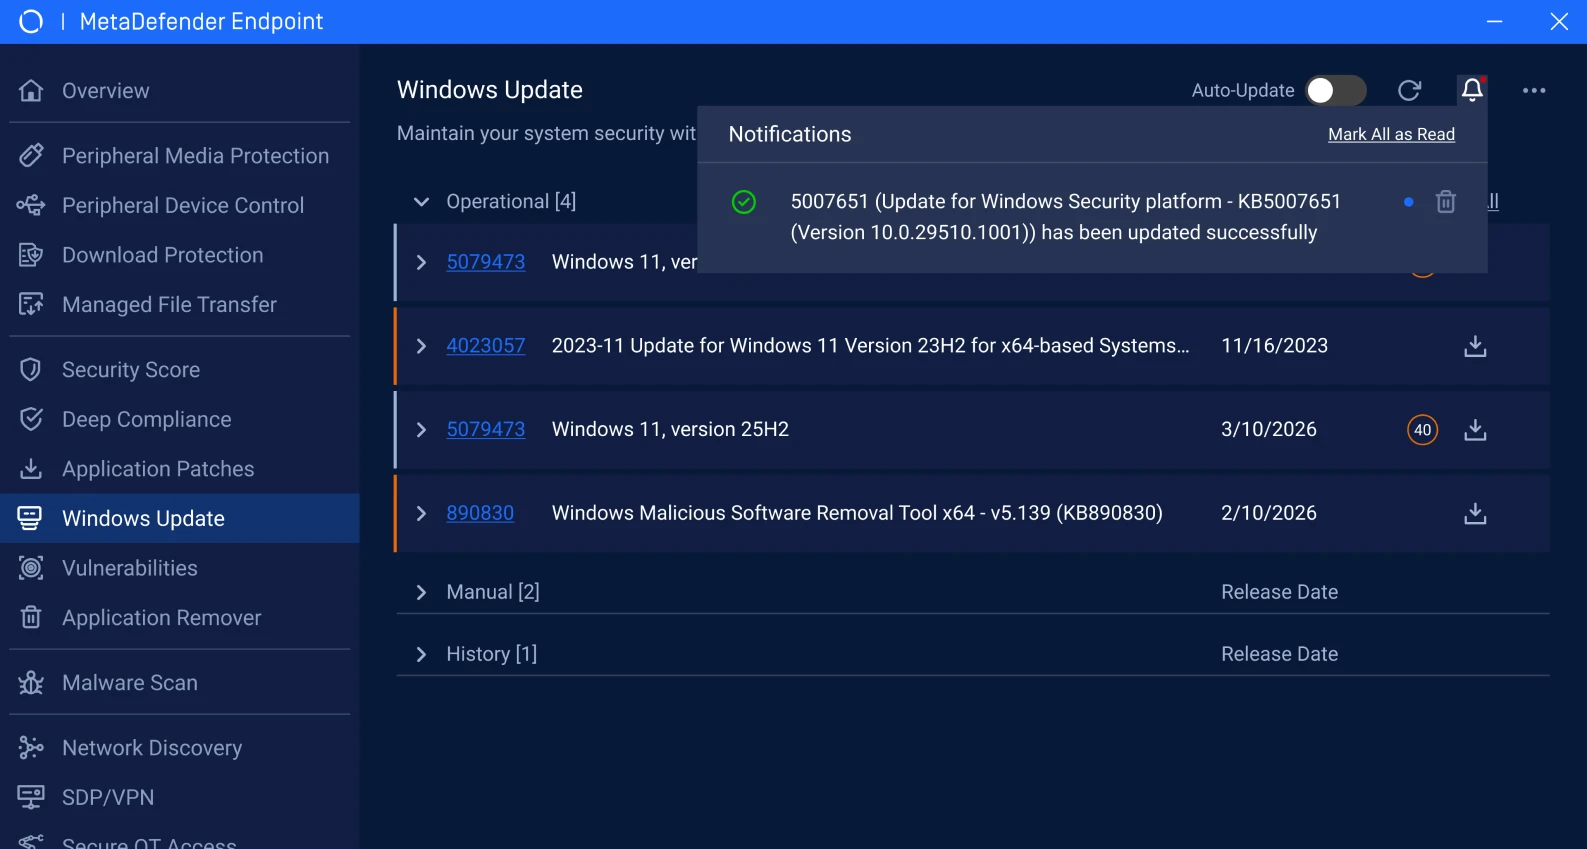
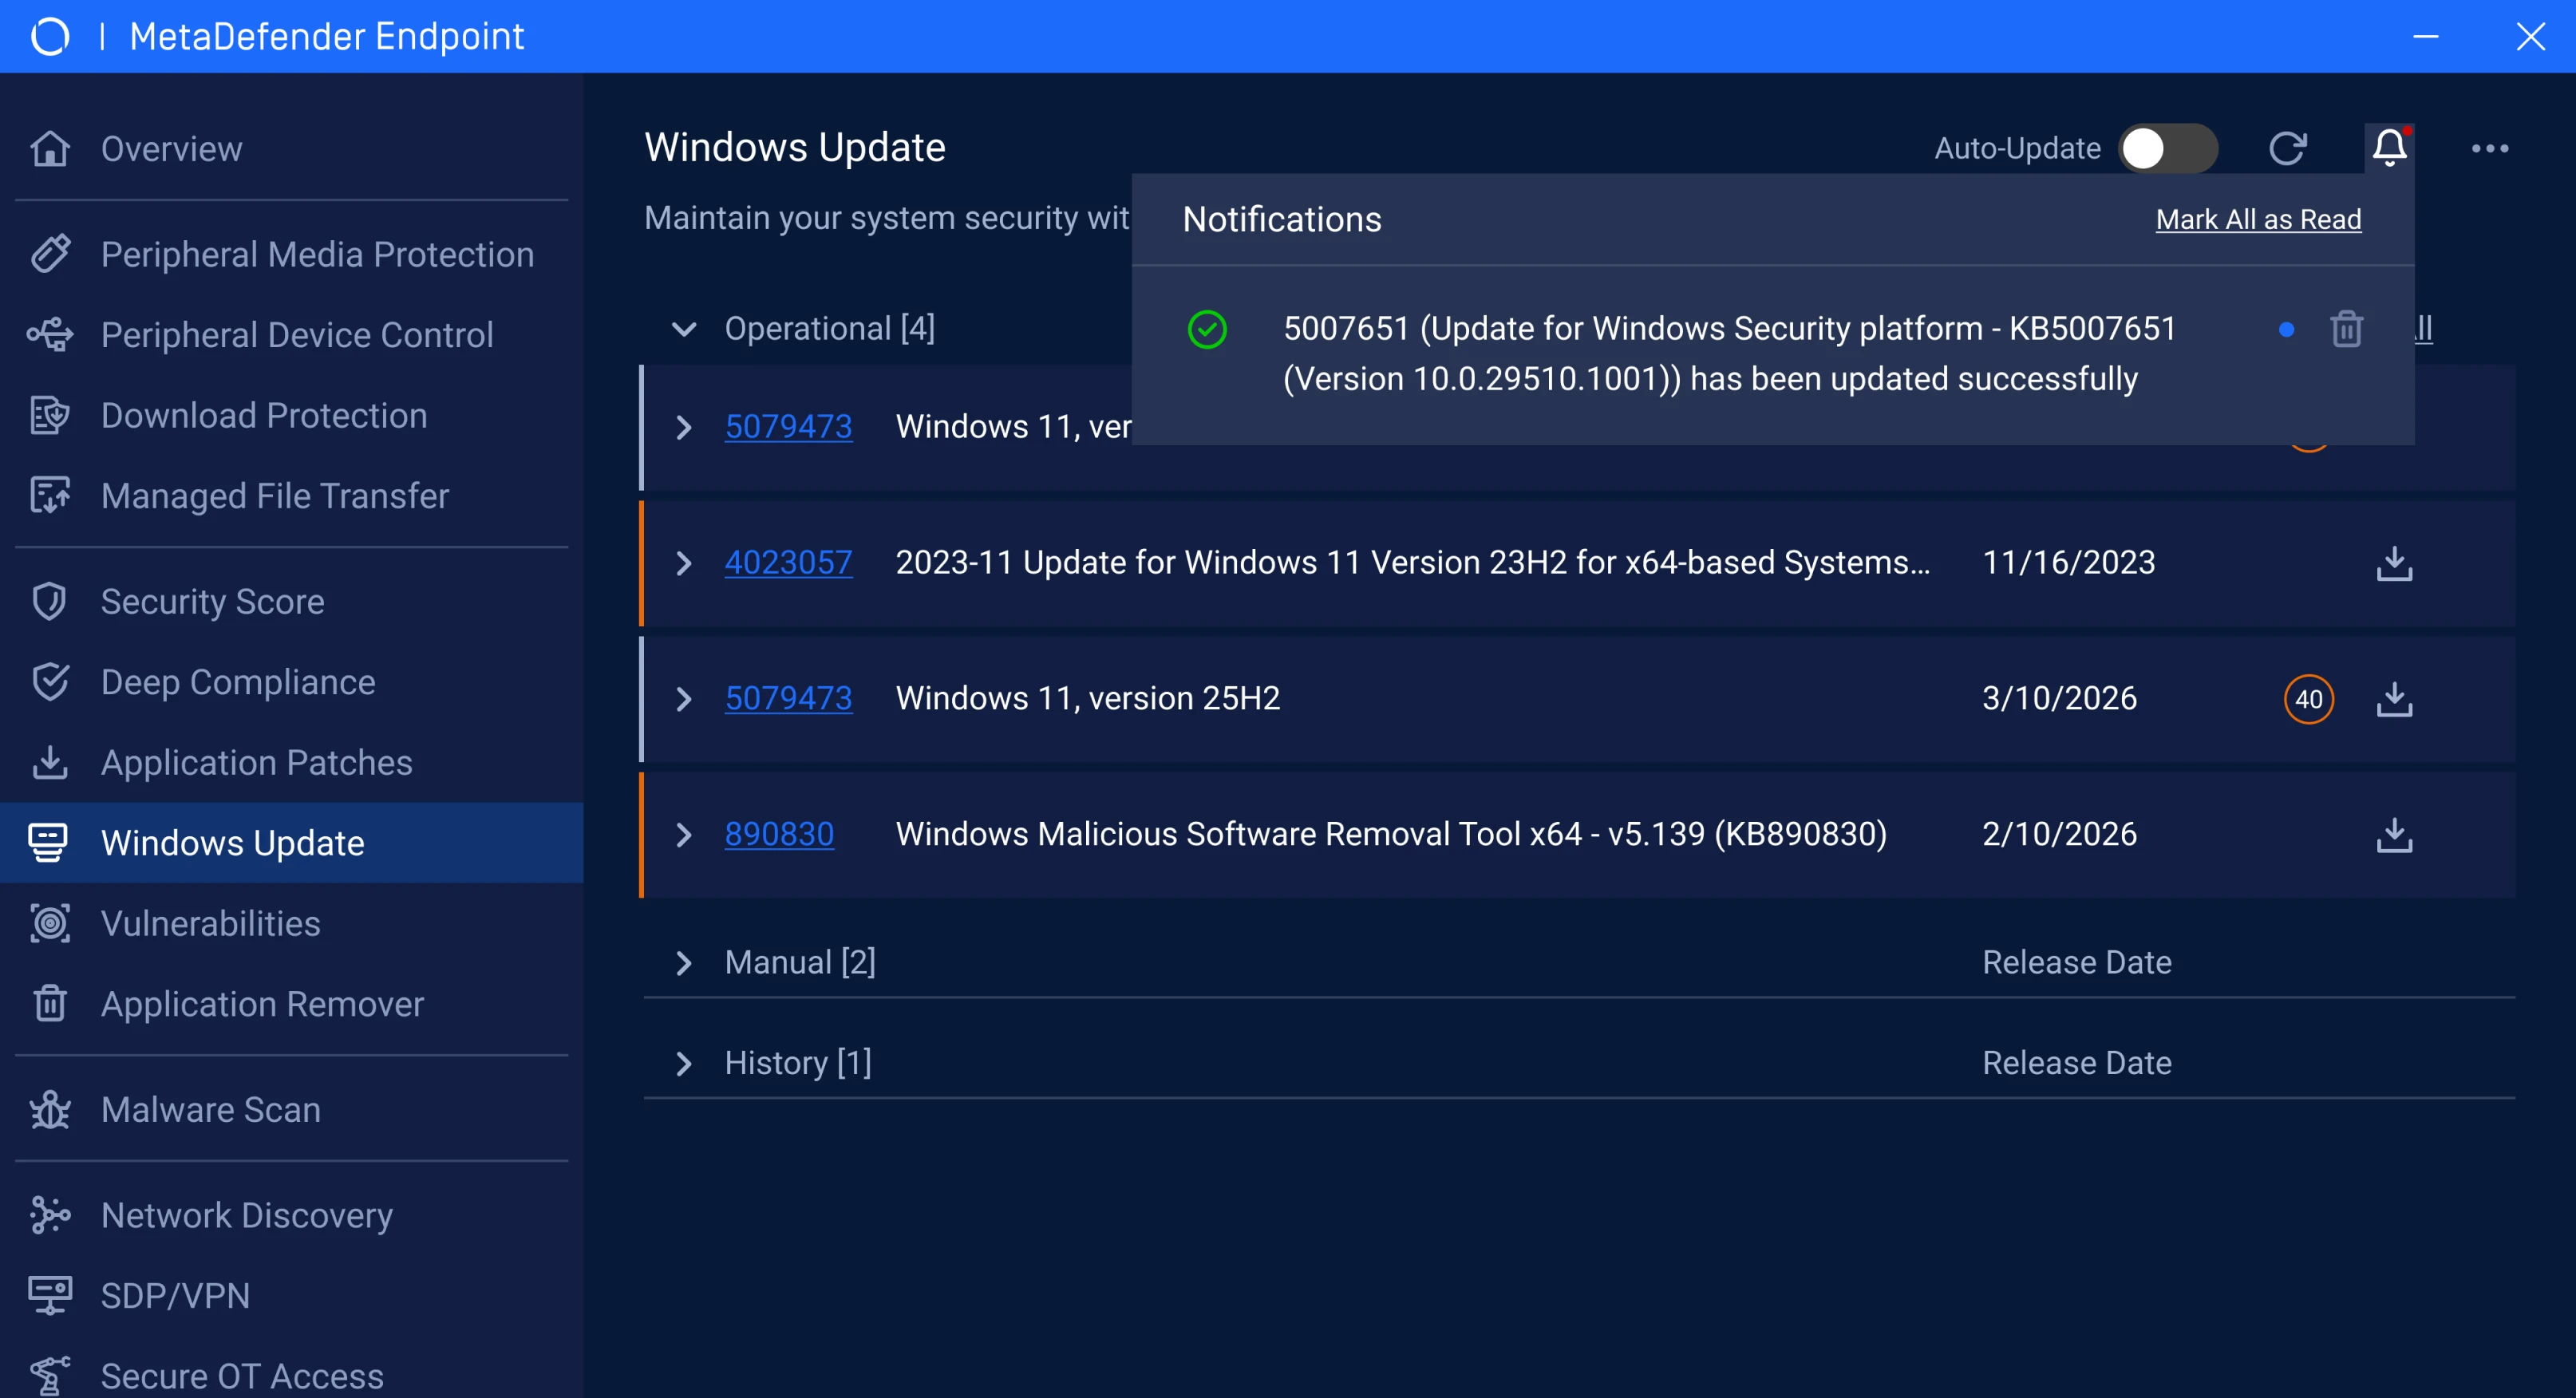
Gain full awareness with installation results notifications delivered to end users on MetaDefender Endpoint.
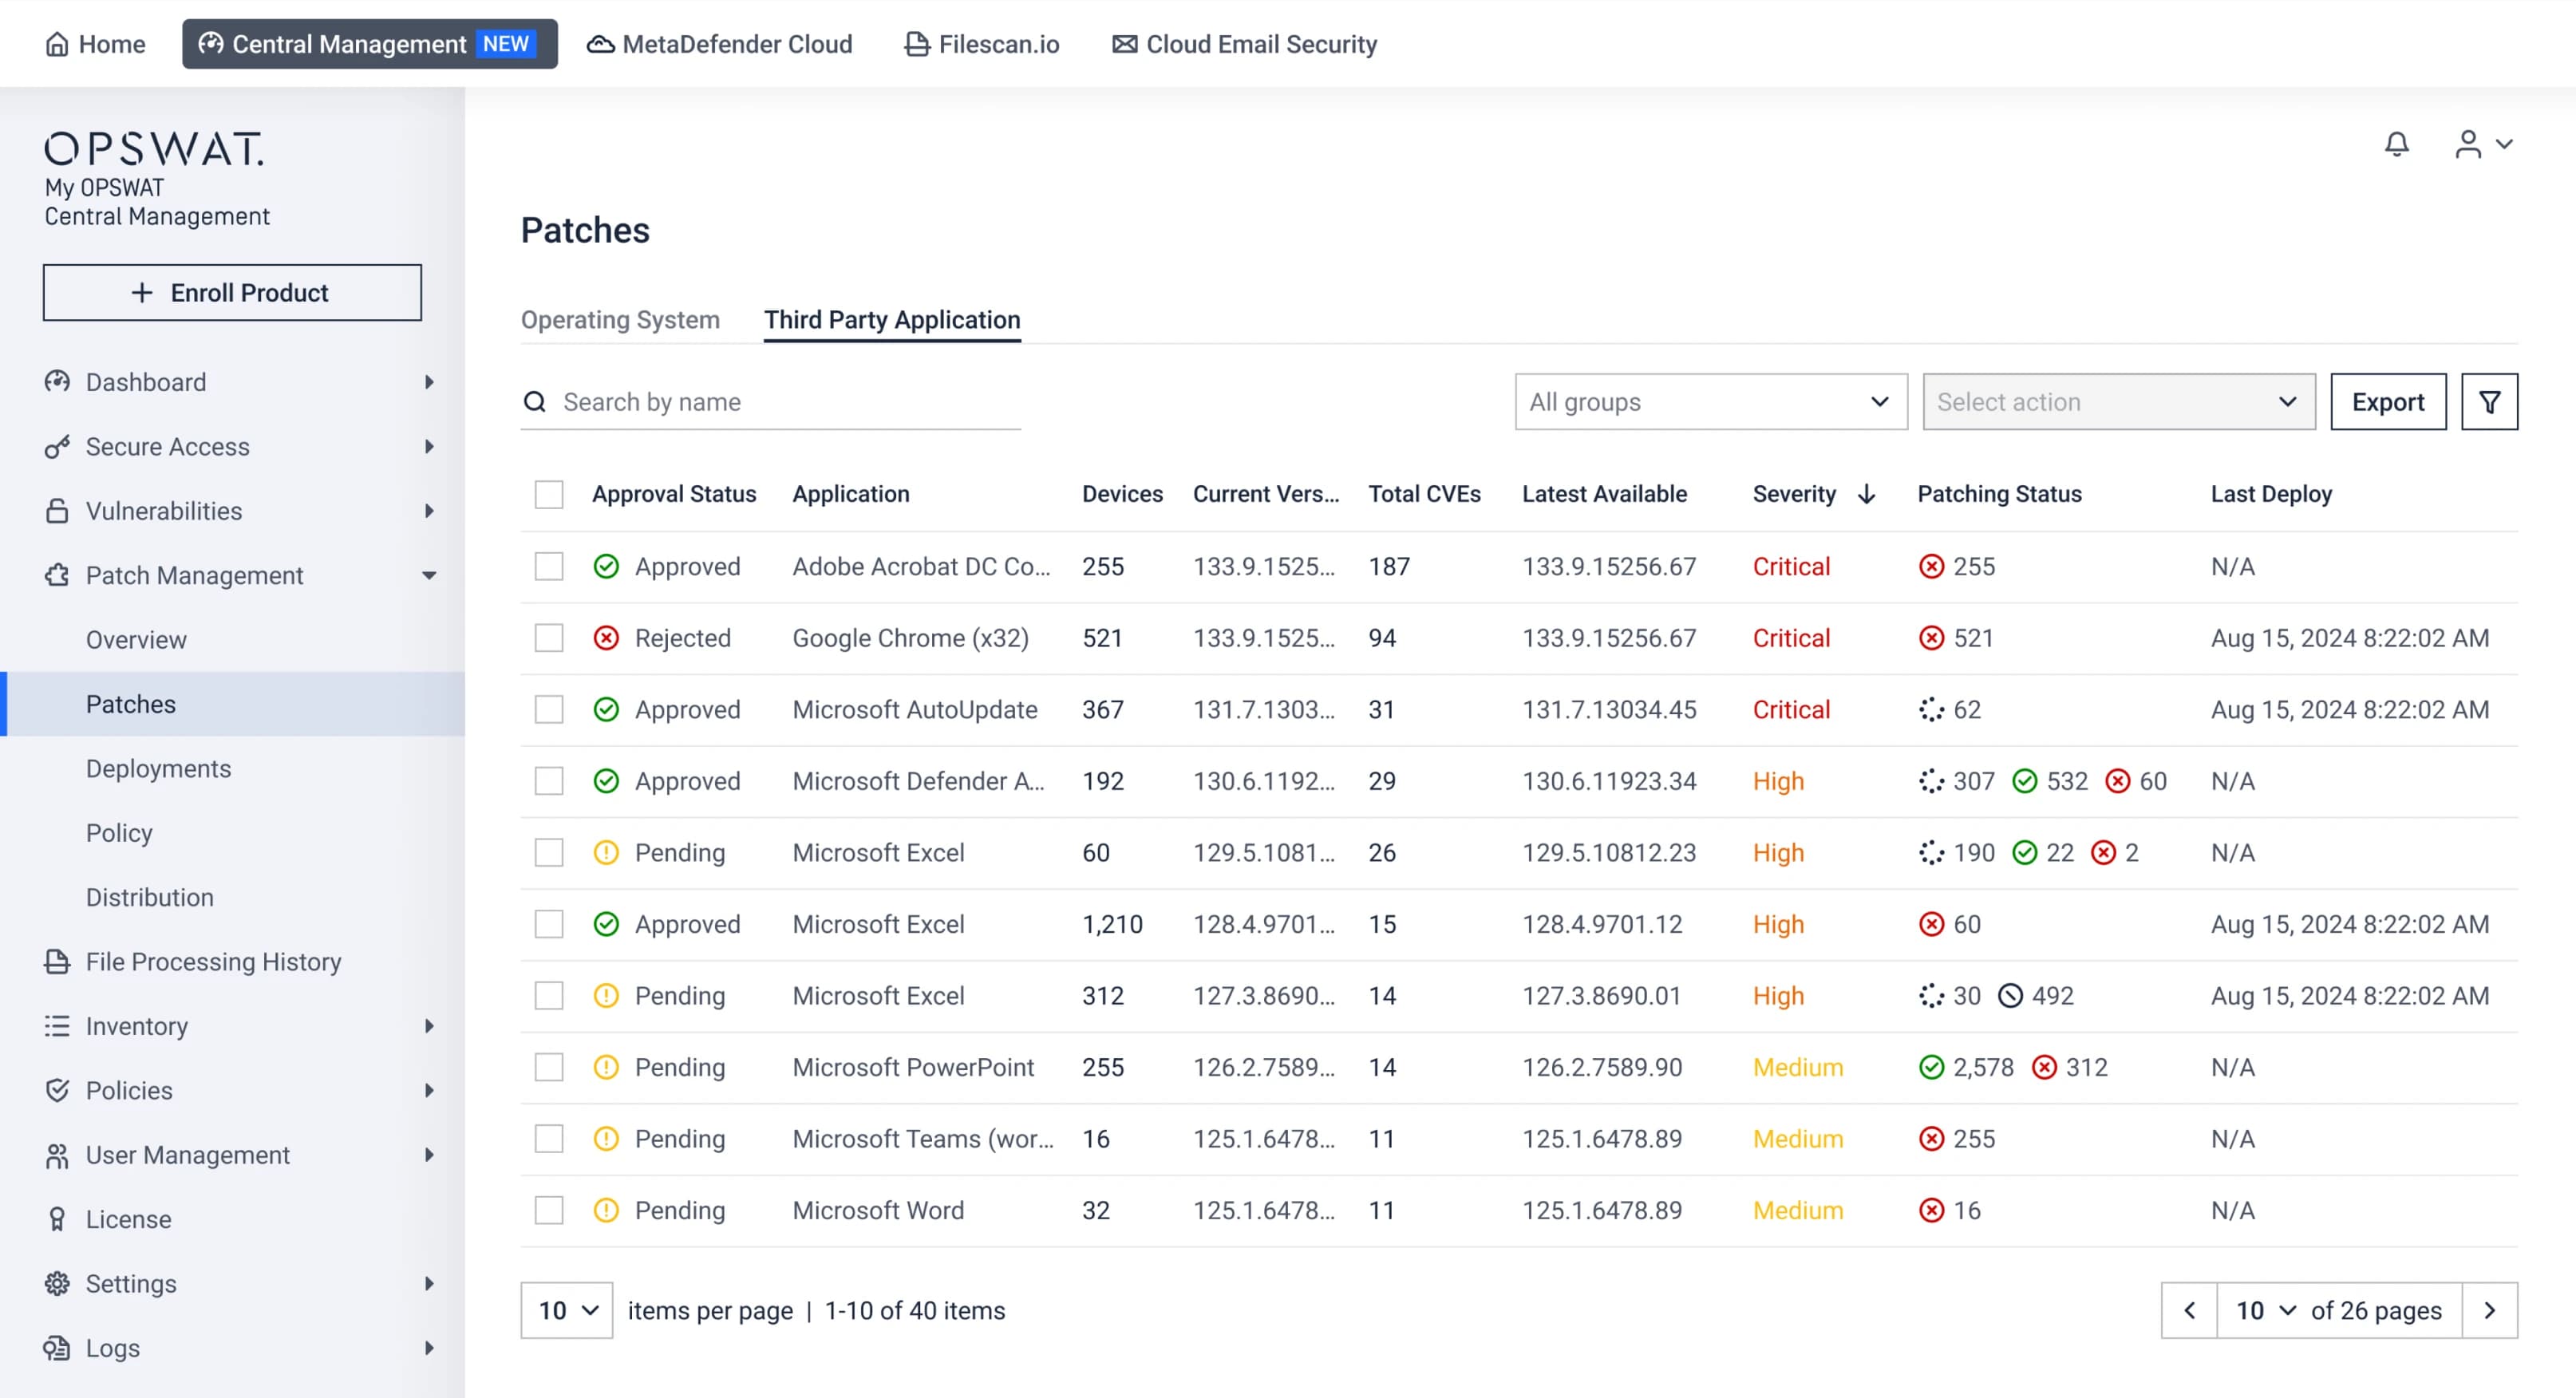 View Patching Status in the Management Console
Patching status are recorded in the management console for full visibility and auditability.
Air-Gapped Patching
The Choice of
Top 20 Tier-1 Vendors
Automatic Patching
425+ Supported Applications
Vulnerability Detection
975+ Supported Applications
Compliance Ready
Flexible Deployments
Why OT Teams Choose MetaDefender Endpoint for Patching
Unlike IT-centric Patch Tools adapted for OT, MetaDefender Endpoint is purpose-built for critical infrastructure and works the same whether endpoints are connected, hybrid, or fully air-gapped. Features OPSWAT offers that general-purpose patch tools typically do not:
Feature |
MetaDefender Endpoint |
IT-centric Patch Tools |
|---|---|---|
Air-Gapped by Design Patch fully disconnected endpoints with the same automation and audit trail as connected systems. |
||
OT-Appropriate, Distraction-Free Suppress pop-ups, notifications, and interruptions on operator screens while patches deploy in the background. |
||
Broad Coverage from One Management Console Windows, macOS, and Linux (including legacy systems), plus 1,200+ third-party applications and OS updates. |
||
Audit-Ready Compliance Tamper-evident logs and exportable, filterable reports aligned to NERC CIP, NIS2, and NIST CSF. |
||
Bandwidth-Efficient at Scale Local cache nodes reduce bandwidth and speed deployment across large or distributed estates. |
||
Unified Management Centralized visibility and control through My OPSWAT Central Management. |
Flexible Deployment
Whether your infrastructure lives in the cloud, on-premises, or in a fully isolated air-gapped environment, our solution works across your deployment model
Proven by Control System Owners
Audit-Ready Patch Compliance for Critical Infrastructure
A growing set of security frameworks now require timely patching and vulnerability remediation, including NIS2, NIST SP 800-40 Rev. 4, ISO 27001, PCI DSS Requirement 6.2, CIS Controls, and GDPR. MetaDefender Endpoint helps critical infrastructure teams meet and demonstrate those requirements: every patch action is captured in tamper-evident logs, with exportable, filterable reports showing what was patched, when, by whom, and the outcome, across connected and air-gapped endpoints.
Get Started in 3 Simple Steps
Recommended Resources
MetaDefender Endpoint Datasheet
Endpoint Management
Strengthening Vendor Laptop Security
Securing Critical IT Networks with MetaDefender Endpoint
FAQs
MetaDefender Endpoint supports flexible deployment across cloud, on-premises, hybrid, and fully air-gapped environments, covering both IT and OT infrastructure.
Air-gapped patch management is the process of discovering and remediating software vulnerabilities on endpoints that have no internet connection, such as isolated OT and ICS systems. MetaDefender Endpoint delivers it by detecting missing patches and deploying approved updates to disconnected endpoints, with the same automation and audit trail used on connected systems.
Yes. MetaDefender Endpoint patches operating systems and third-party applications in both internet-connected and fully air-gapped environments, including isolated OT and ICS networks. Disconnected endpoints receive the same automated patching, policy control, and patch-status visibility as connected systems.
In an air-gapped environment, MetaDefender Endpoint detects missing patches and reports status to My OPSWAT Central Management without requiring internet access on the endpoint. Administrators upload approved patch packages to the console, schedule deployment, and the platform applies updates to the isolated endpoints, maintaining full patch-status visibility even when systems stay disconnected.
MetaDefender Endpoint is built for critical infrastructure, not adapted from IT. Unlike general-purpose patch tools, it patches fully air-gapped and OT endpoints, runs in a distraction-free mode that avoids interrupting operators, and records a tamper-evident audit trail for regulated environments, while still covering standard Windows, macOS, and Linux estates.
MetaDefender Endpoint supports patching for Windows, macOS, and Linux, including legacy systems, along with third-party applications such as browsers, productivity suites, developer tools, and security software. It detects vulnerabilities in 975+ applications with CVSS-based severity scores and recommended fixes, and automatically patches 425+ third-party applications and OS updates.
Yes. With MetaDefender Endpoint, administrators define maintenance windows, reboot behavior, and multi-stage rollout rings that align with the operational calendar. This lets teams stage deployments and keep critical systems patched without compromising availability.
No. MetaDefender Endpoint includes a distraction-free mode that suppresses pop-ups and notifications and deploys patches silently during scheduled windows. Operators and end users are not interrupted while patching runs in the background.
Administrators upload patch packages to the management console in My OPSWAT Central Management, and MetaDefender Endpoint validates each package as authentic and untampered before deployment. This helps prevent the installation of corrupted or malicious updates.
MetaDefender Endpoint records every patch action in a tamper-evident audit log, capturing who approved it, when it was deployed, and the outcome. Reports are exportable and filterable on demand, so teams can demonstrate patch compliance for an audit without assembling evidence manually.
Many security and critical infrastructure frameworks require timely patching and vulnerability remediation, including NIS2, NIST SP 800-40 Rev. 4, ISO 27001, PCI DSS Requirement 6.2, CIS Controls, and GDPR. MetaDefender Endpoint helps organizations meet and demonstrate these requirements through automated patching and audit-ready reporting.