We’re proud to introduce MetaDefender Aether v2.2.0—the latest version of OPSWAT’s next-generation malware detection solution will help security professionals outsmart the threats of 2025 and beyond. This release isn’t just an update; it redefines how malware is detected, analyzed, and mitigated.
MetaDefender Aether v2.2.0: Smarter, Faster, Stronger
1. Zero-Day Office Document Support
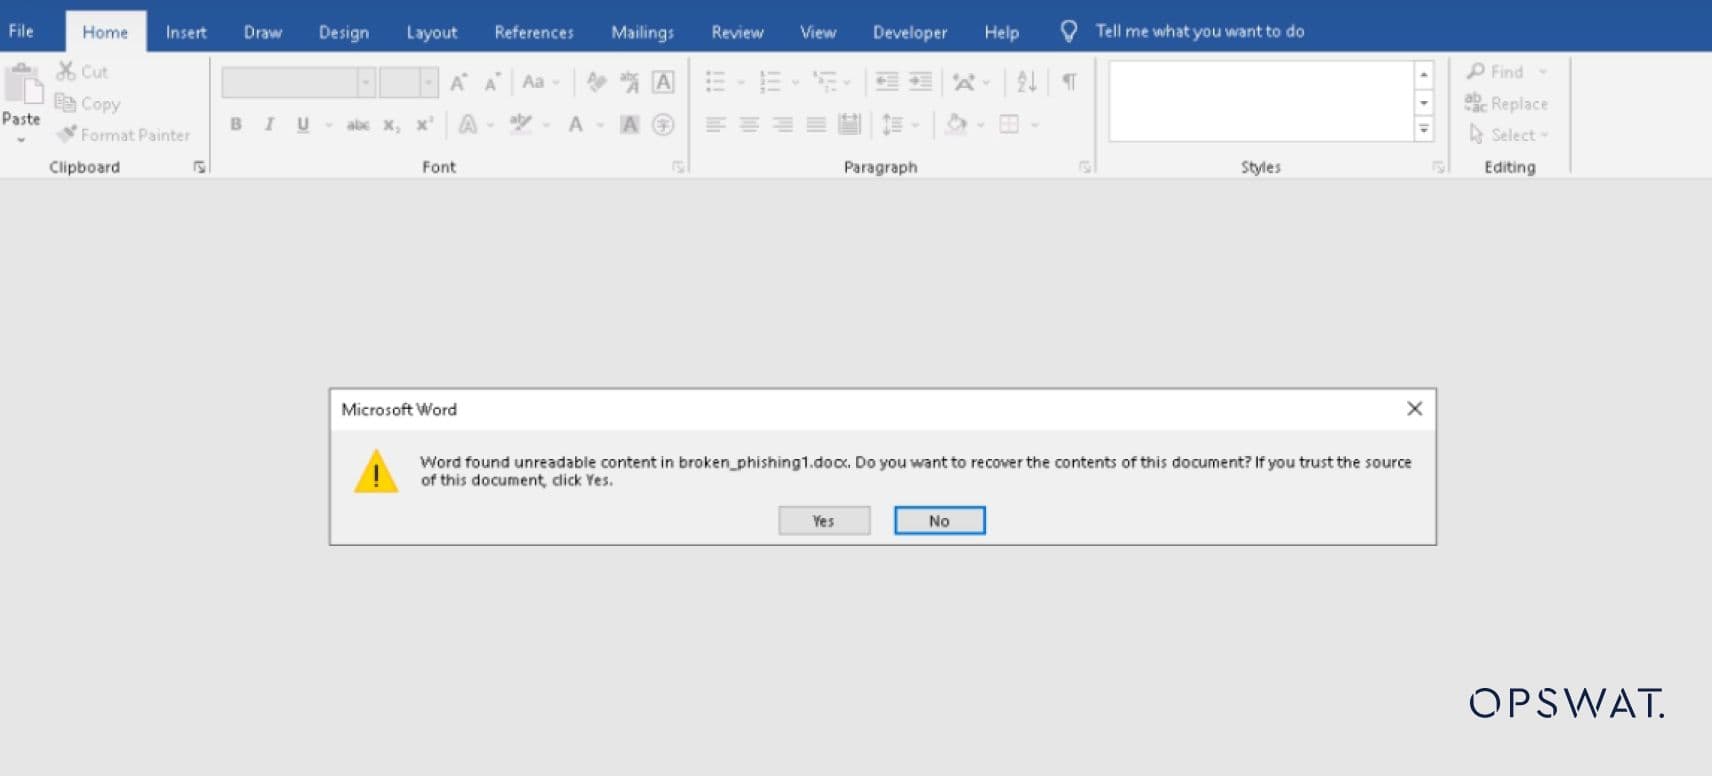
Zero-day malware often hides in corrupted Office files, exploiting vulnerabilities that evade traditional analysis. MetaDefender Aether v2.2.0 introduces the ability to recover and analyze these broken documents—a critical capability for detecting previously evasive threats targeting Office file vulnerabilities.
Why it Matters: Proactively stop advanced threats that rely on user interaction to execute, ensuring no attack goes unnoticed.
2. Concatenated Archives Detection
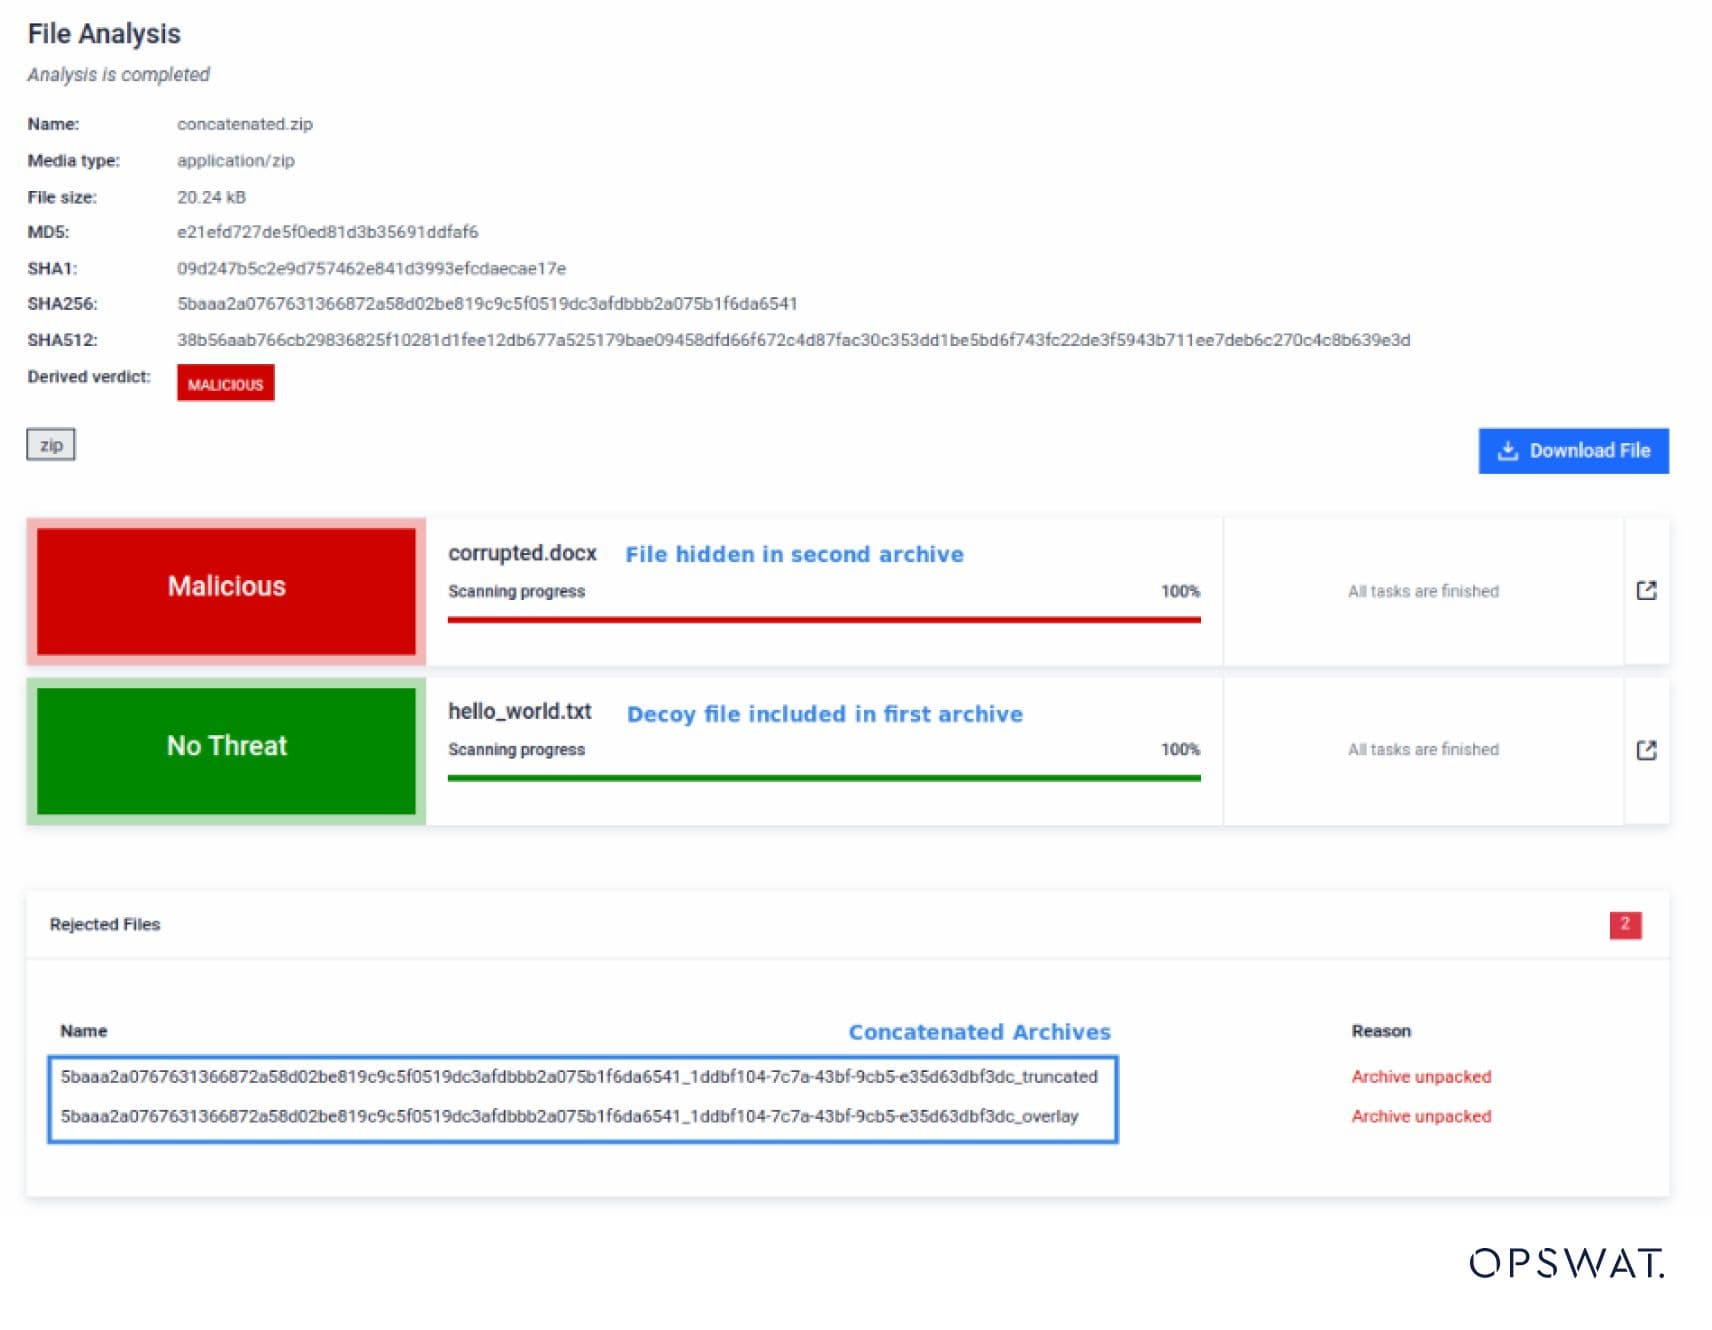
Attackers increasingly use archive concatenation—merging multiple archives into a single file—to confuse detection systems. With v2.2.0, our sandbox can analyze every layer of concatenated archives, exposing hidden payloads that might otherwise slip through.
Why it Matters: Uncover sophisticated malware hidden within complex archive structures, providing stronger defenses against sophisticated evasion tactics.
3. Mitigation for Bloated Executables
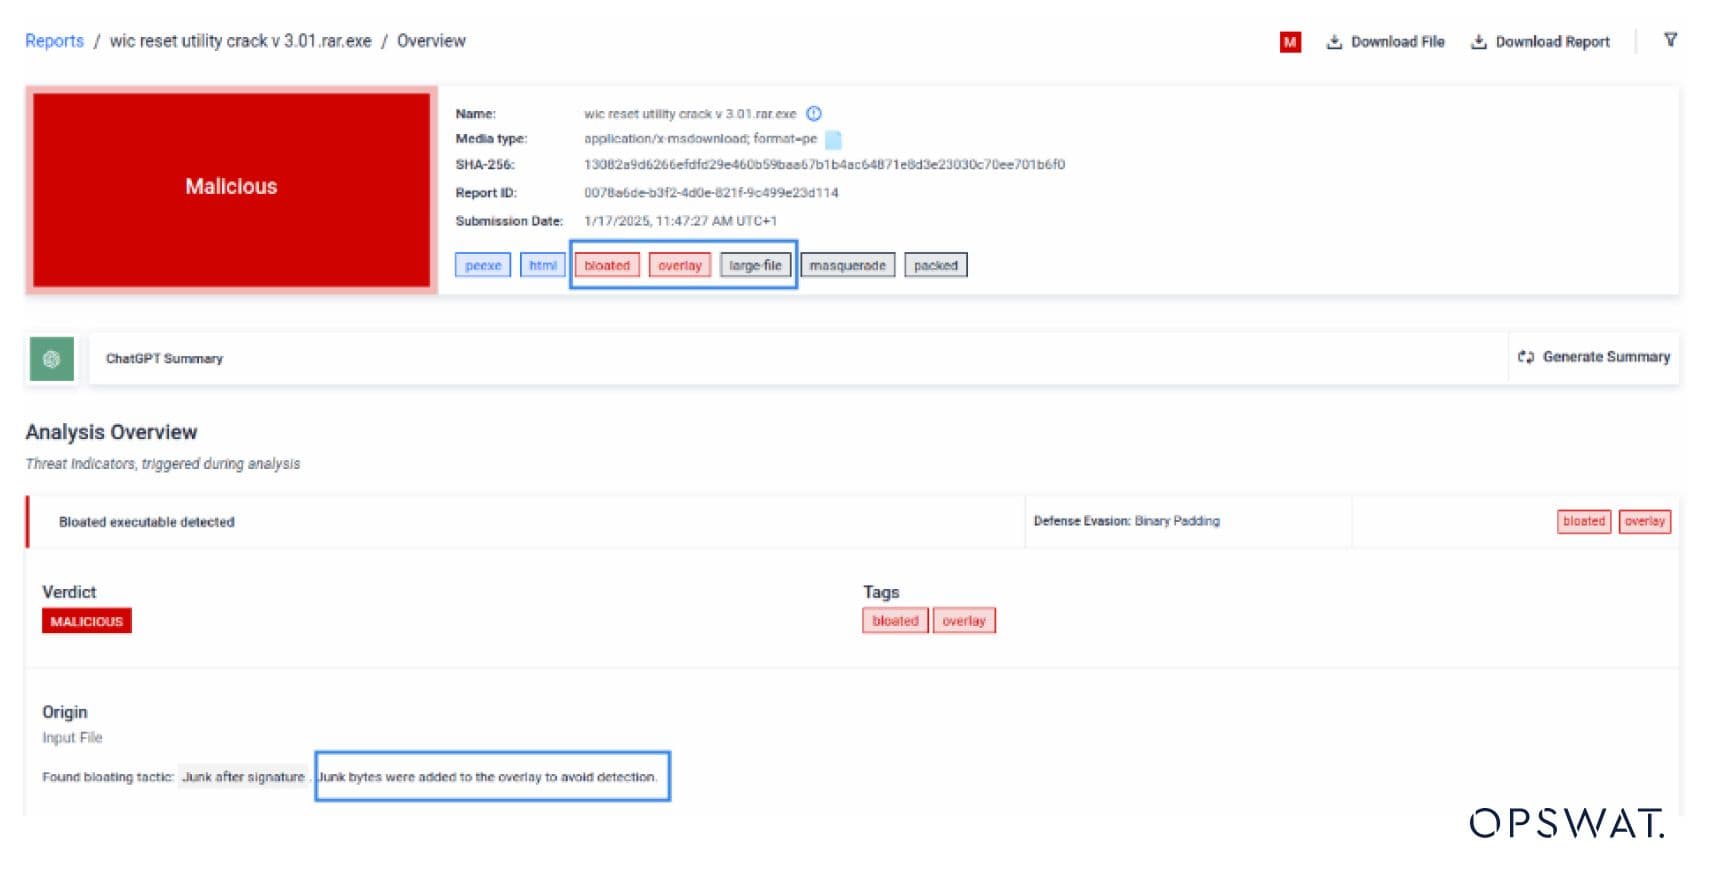
Malware authors create artificially inflated executables to overwhelm sandbox environments. MetaDefender Aether v2.2.0 now identifies and shrinks these files, stripping unnecessary junk to streamline analysis without sacrificing accuracy.
Why it Matters: Enhance scan performance and ensure reliable detection even under heavy file loads.
Smarter, Context-Aware Detection
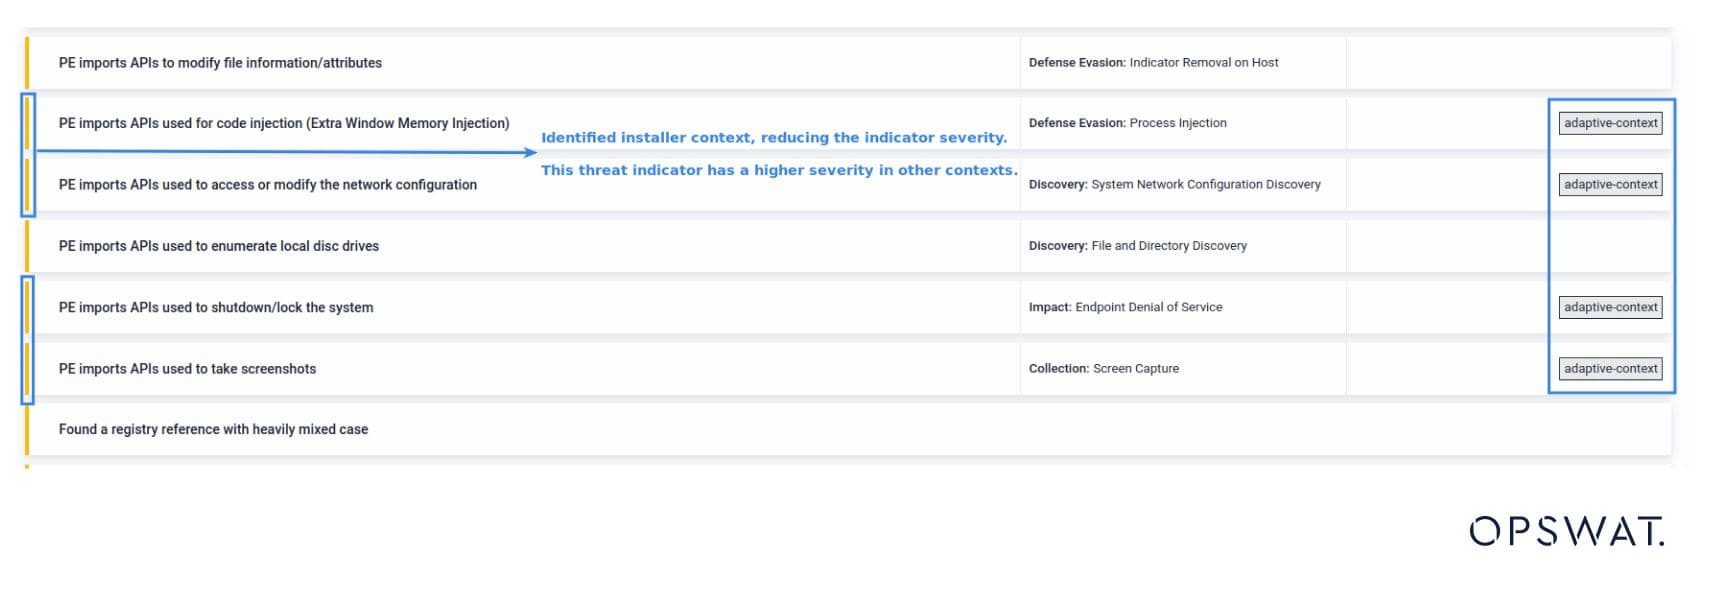
Traditional sandboxes often flag behavior that’s common to both legitimate and malicious software, leading to false positives. In this release, we’ve introduced Adaptive Threat Indicators to provide context-aware detection. By evaluating whether a file is a trusted, signed application or a suspicious, packed executable, the system delivers smarter and more accurate verdicts.
Why it Matters: Reduce false positives and enable security teams to focus on real threats with greater confidence.
Enhanced Malware Family Coverage
MetaDefender Aether v2.2.0 adds detection for notable malware families such as Lumma Stealer, Remcos, and others. These updates include improved configuration extraction to deliver high-value IOCs like C2 (Command & Control) addresses, which are essential for proactive defense strategies.
Why it Matters: Expanded threat coverage ensures you stay ahead of emerging malware trends.
Optimized User Experience and Deployment
We believe that powerful cybersecurity tools should also be easy to use. That’s why MetaDefender Aether v2.2.0 includes:
- A New Setup Wizard: Simplifies initial configuration, licensing setup, and integration with the MetaDefender Cloud Reputation API, ensuring a smooth start for new users.
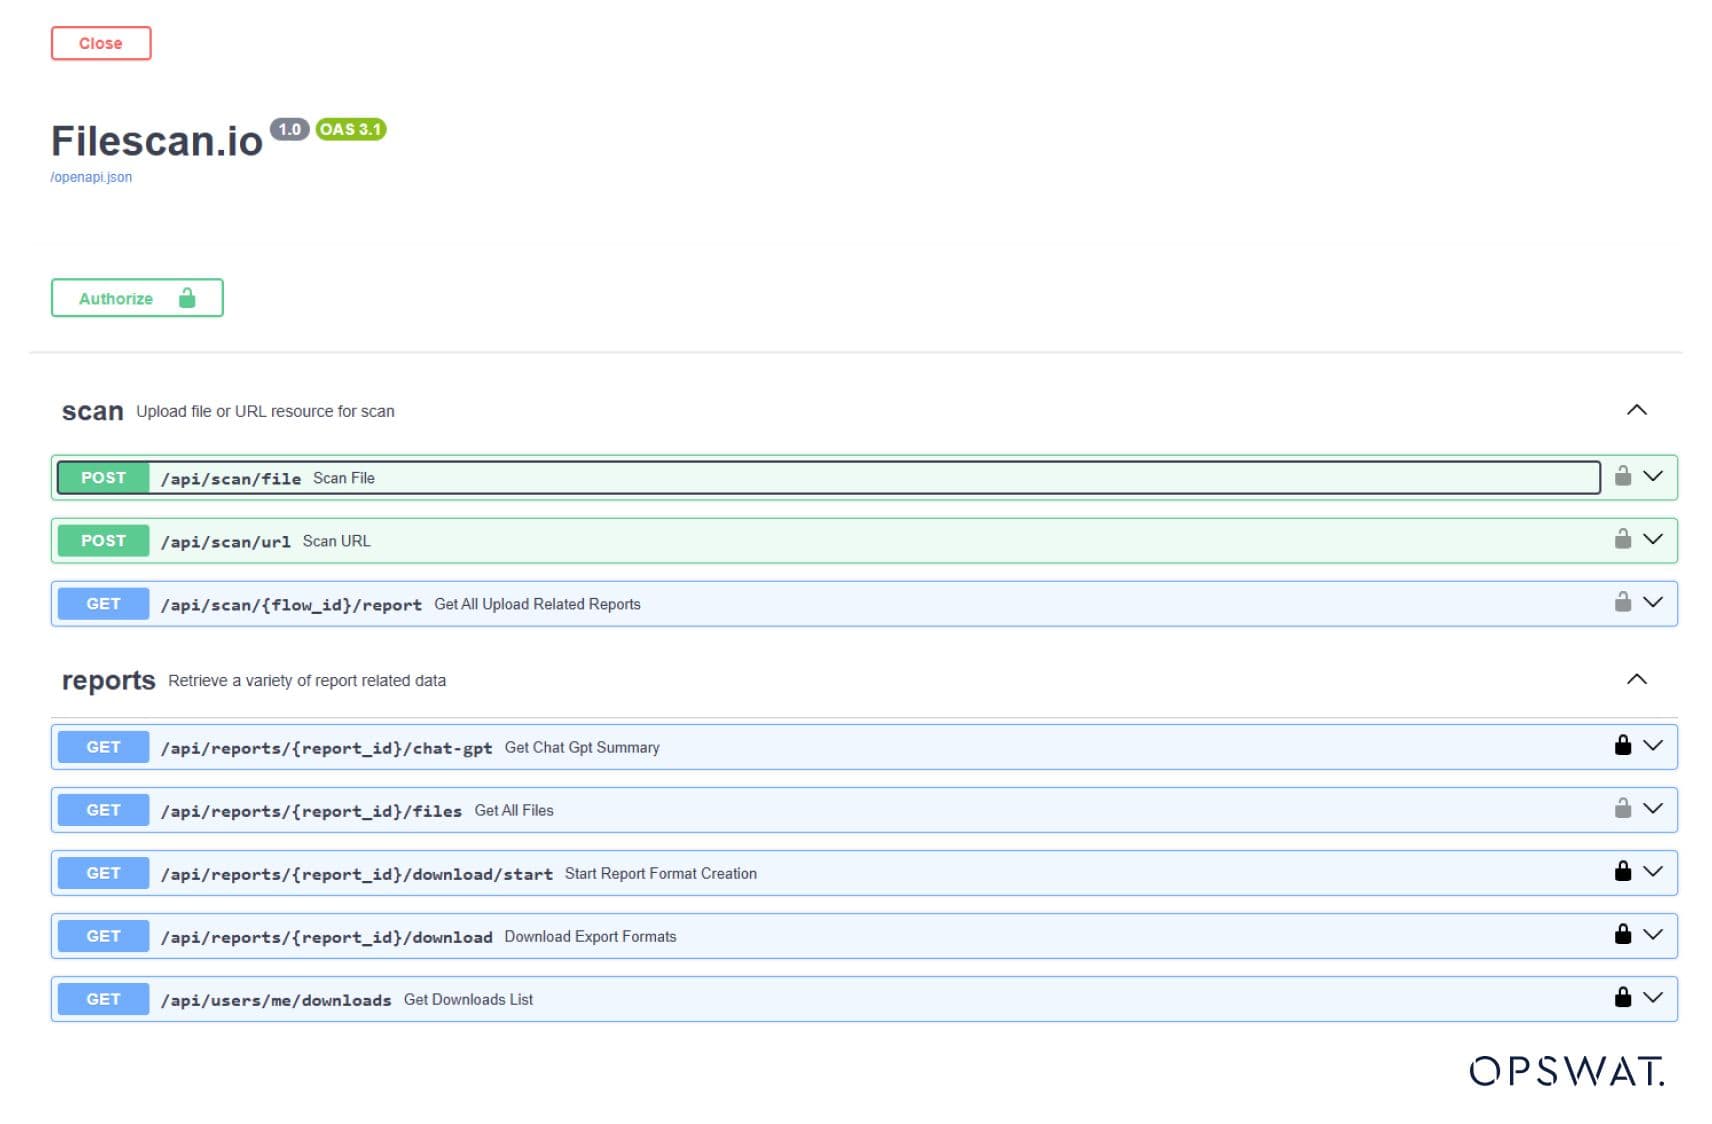
- Improved Navigation: Features like a close button on the API page and customizable username lengths make navigating the platform more intuitive.
- Extended API Documentation: Interactive API page on Filescan.IO - Next-Gen Malware Analysis Platform allow users to test integrations directly, streamlining the setup process.
Profiles: Simplified and Flexible Scan Configurations
We’ve replaced outdated scan modes with Profiles, which offer preset configurations that can be fine-tuned based on your specific needs. Profiles allow administrators to customize scan settings, disable features, and adjust timeout values for better performance—whether in MetaDefender Core or Standalone deployments.
Why it Matters: Faster, more efficient scans can be tailored to your environment.
New Capabilities Security into the Future
MetaDefender Aether v2.2.0 introduces several additional features to strengthen your security posture for 2025 and beyond:
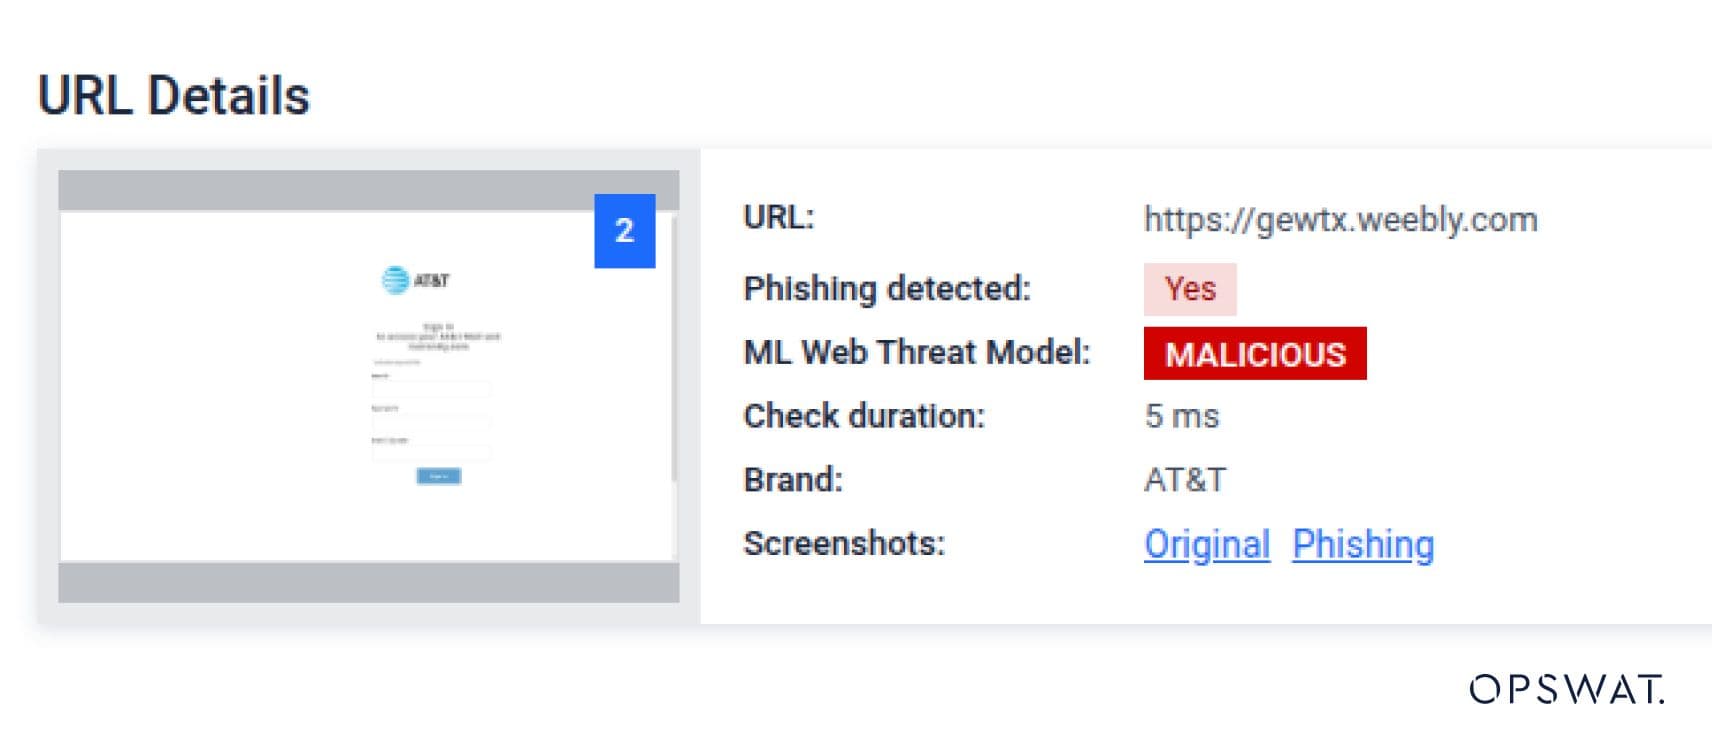
- WebThreat URL Detection: Advanced phishing detection powered by network data analysis improves protection against malicious URLs.
- JavaScript-Compiled PE File Support: Enables unpacking and decompilation of JavaScript-compiled PE files for deeper analysis.
- Malicious Technique Detection: Identifies advanced attack vectors like disabling Data Execution Prevention (DEP) and Authenticode evasion (SigFlip).
- Support for RedHat 9: Adds compatibility for enterprise environments with online installations.
Protection Built for Tomorrow’s Threats
MetaDefender Aether v2.2.0 empowers security teams to stay one step ahead of threats. From advanced evasion resistance to smarter, context-aware detection, this release offers the tools you need to combat the most sophisticated threats with confidence.
With enhancements that boost detection accuracy, streamline workflows, and expand compatibility, MetaDefender Aether v2.2.0 is the comprehensive solution to mature your cybersecurity defenses.
Experience the future of malware detection. Try MetaDefender Aether v2.2.0 today and discover how it can transform your security operations. Start your free trial now and stay ahead of 2025’s most evasive threats!