OPSWAT is excited to announce the release of MetaDefender Drive™ v4.3.0, a major release with new, advanced security features to prevent unauthorized configuration changes, improve visibility, and ensure consistent scanning policy enforcement. Significant performance enhancements have also been included in this release.
Centralized Scanning Profile: Advanced Access Control to Enhance Scan Policy Management
Ensuring that third-party vendor laptop scanning protocols are followed adequately across multiple locations is challenging, especially in air-gapped environments with strict regulatory compliance requirements. A minor, unintentional change in the scan configurations can increase the risk of security breaches. Starting with MetaDefender Drive v4.3.0 and MetaDefender Drive Toolkit v3.7.0, administrators have more remote control over MetaDefender Drive usage to enhance security and prevent unauthorized usage.
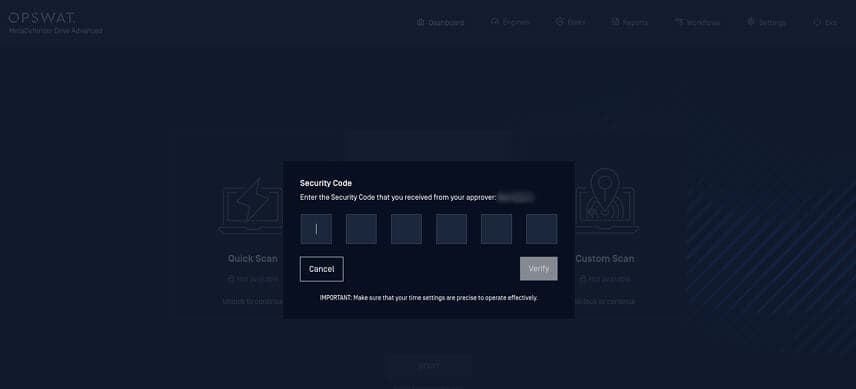
MetaDefender Drive can be locked to restrict unauthorized scan configuration changes. Field Operators can only update engine versions and perform full scans. Any other actions require administrator’s approval.
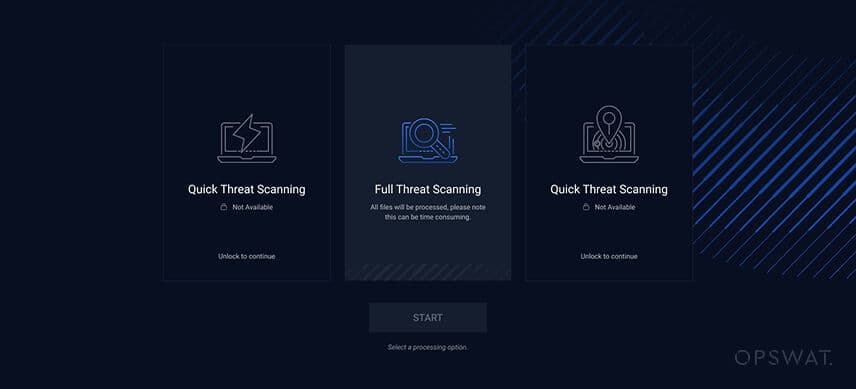
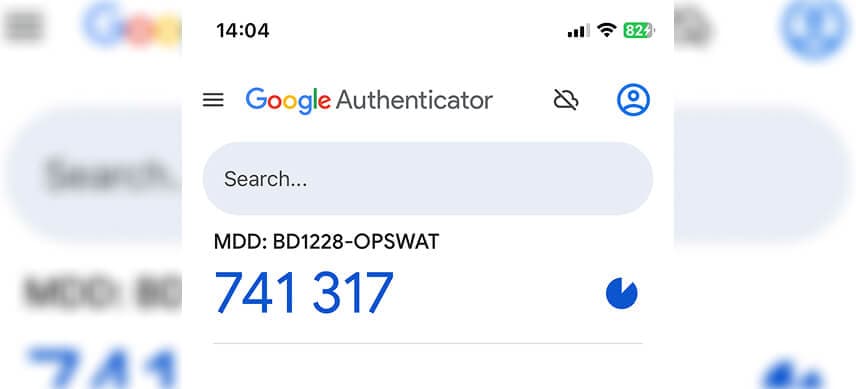
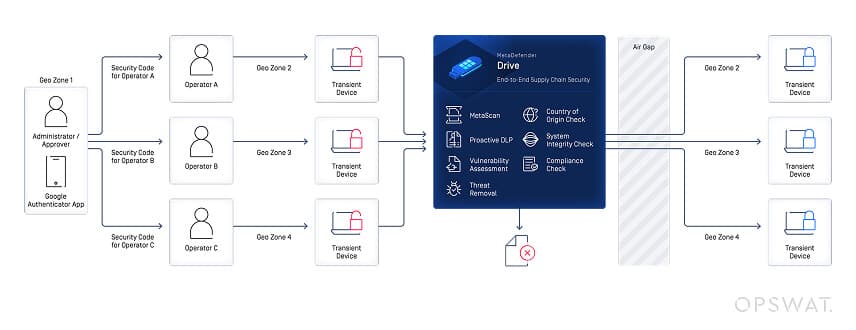
MetaDefender Drive Administrators can assign Approvers, who are responsible for authorizing MetaDefender Drive operators to have fully functional access using a 6-digit OTP (one-time password).
The Centralized Scanning Profile feature comes with many key benefits:
- Remote Scan Policy Enforcement: Admins can remotely enforce scan policy across multiple sites.
- Admin-Approved Changes: Any scan configuration changes require admin approval.
- Regulatory Compliance Assurance: Helps organizations comply with industry security standards by enhancing access control policies.
Setting up User Roles from MetaDefender Drive Toolkit
Managing and operating MetaDefender Drive through the Centralized Scanning Profile feature involves three user roles:
- Administrator: Responsible for provisioning MetaDefender Drive from the MetaDefender Drive Toolkit interface.
- Approver: Can be assigned by the Administrator to authorize Operators to unlock MetaDefender Drive. Administrators can also perform the Approver role.
- Operator: The field operators of MetaDefender Drive.
Locking MetaDefender Drive and assigning an Approver can be performed in a few simple steps:
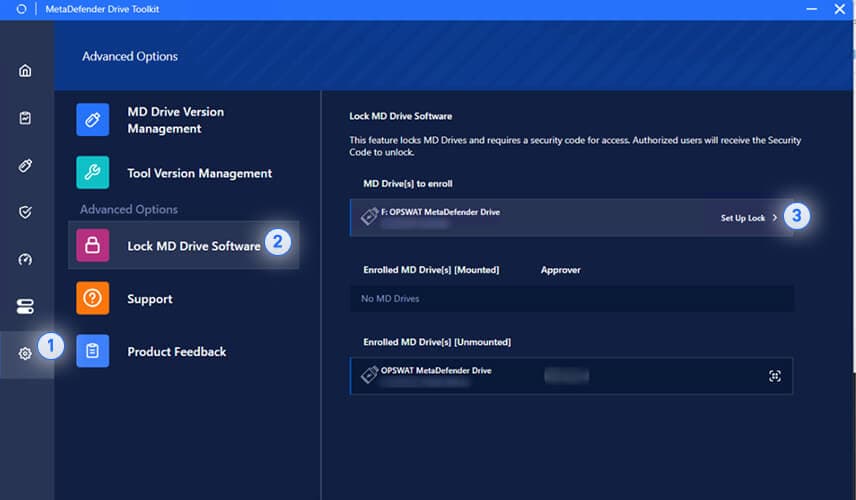
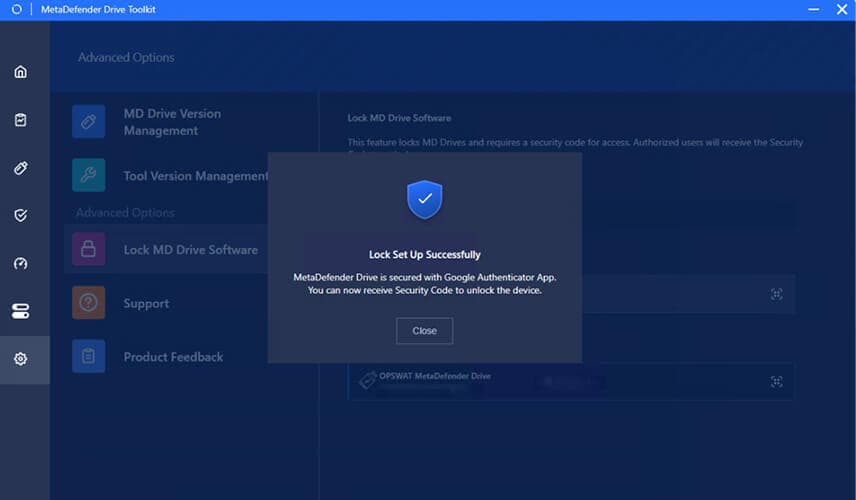
- Under the Setting tab, go to Advanced Options, and click Lock MD Drive Software. Then, select the MetaDefender Drive to lock.
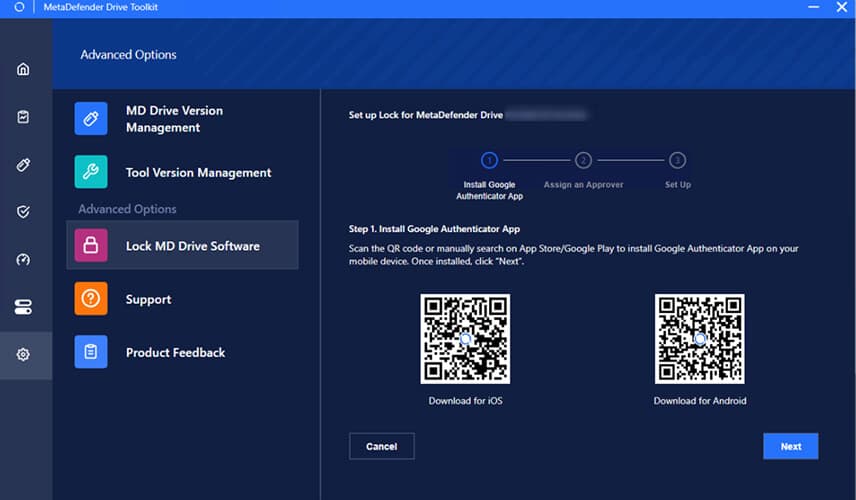
- Install the Google Authenticator Application to generate a 6-digit OTP (one-time password).
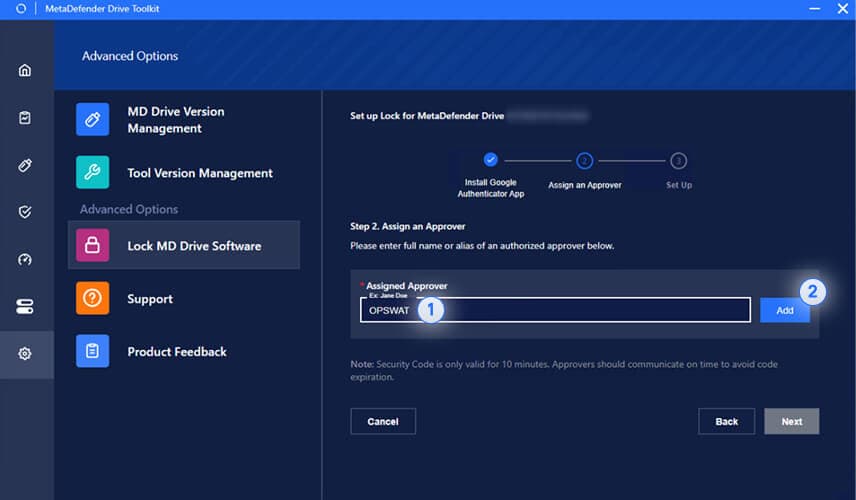
- Enter a name to identify the Approver, then click Add.
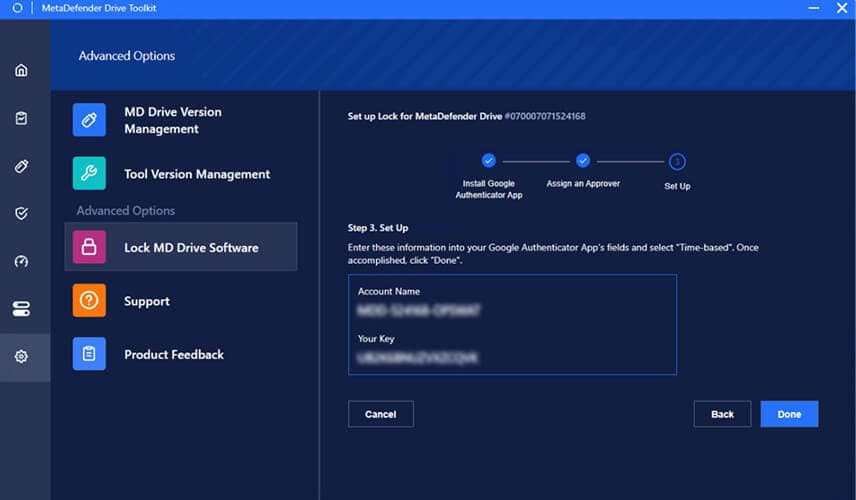
- Enter the MetaDefender Drive credentials (Account Name and Your Key) into the Google Authenticator app for secure OTP generation.
- A pop-up will confirm successfully locking MetaDefender Drive.
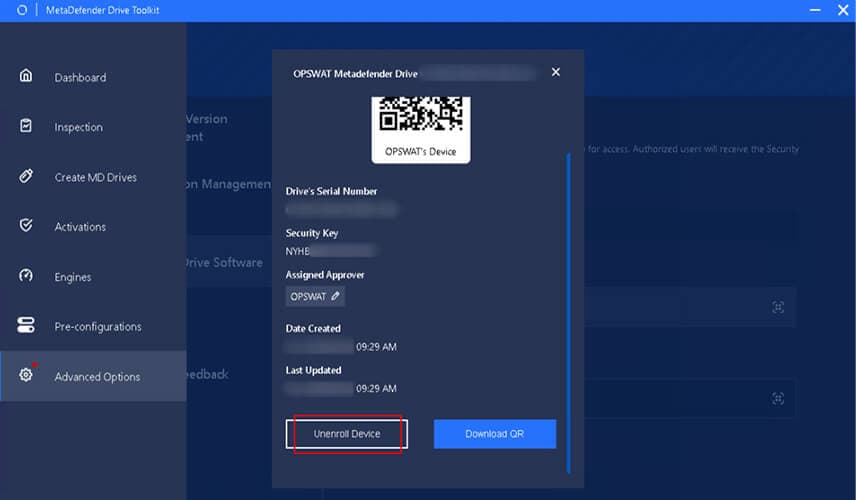
Administrators can also unenroll a MetaDefender Drive by clicking Unenroll Drive from the drive’s information pop-up:
New Enhancements
More performance enhancements and feature improvements have been implemented in the latest releases of MetaDefender Drive v4.3.0 and MetaDefender Drive Toolkit v3.7.0:
- Selective Report Sync: Users can now manually choose the reports to sync with My OPSWAT Central Management, adding better control to report management.
- Optimized Support Package Sizes: The size of the generated support packages now ranges from 2GB to 6GB instead of 4GB to 12GB, accelerating troubleshooting and reducing upload times.
- Self-Protection Against Unauthorized Files: Automatically detects and removes unauthorized files during boot and when connected to MetaDefender Drive Toolkit to maintain integrity and security.
Release Details
- Product: MetaDefender Drive
- Release Date: March 20, 2025
- Release Notes: Learn more here
To update MetaDefender Drive, download the latest version of MetaDefender Drive Toolkit and follow the installation instructions
* For a full list of supported file systems, view the MetaDefender Drive datasheet.
