Every update to MetaDefender Endpoint helps security teams protect critical infrastructure and enables more efficient operations. This release includes Windows (v7.6.2609), macOS (v10.4.2609), and Linux (v15.6.2609) platforms. It gives administrators more control over how Peripheral Media Protection responds in the field, offers embedded anti-malware engine definition updates in fully air-gapped environments, and improves visibility over file audit trail.
What’s New in MetaDefender Endpoint
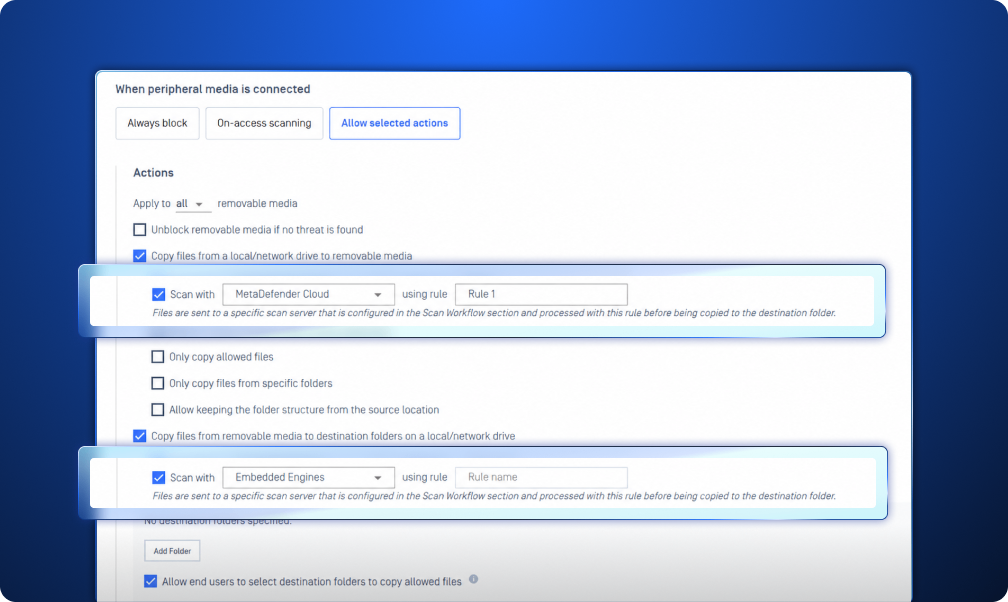
Configurable Direction-Specific Rules for Peripheral Media Protection
Peripheral media introduces risk in both directions. Data can enter an endpoint from removable media and sensitive files can be transferred from the endpoint to external media. This release enables MetaDefender Endpoint administrators to configure direction-specific scanning workflows in Peripheral Media Protection, protecting critical endpoints from potentially malicious files while also providing an additional layer of control over data moving from and to removable media.
Update Embedded Anti-Malware Engine Definitions in Air-Gapped Environments
Security teams operating in fully air-gapped environments can now set up and update embedded anti-malware engine definitions without requiring internet connectivity, enabling organizations to maintain their protection while keeping critical endpoints segregated from external networks. This also gives administrators more control and flexibility within their controlled environment, helping maintain protection without compromising the isolation required by sensitive or critical systems.
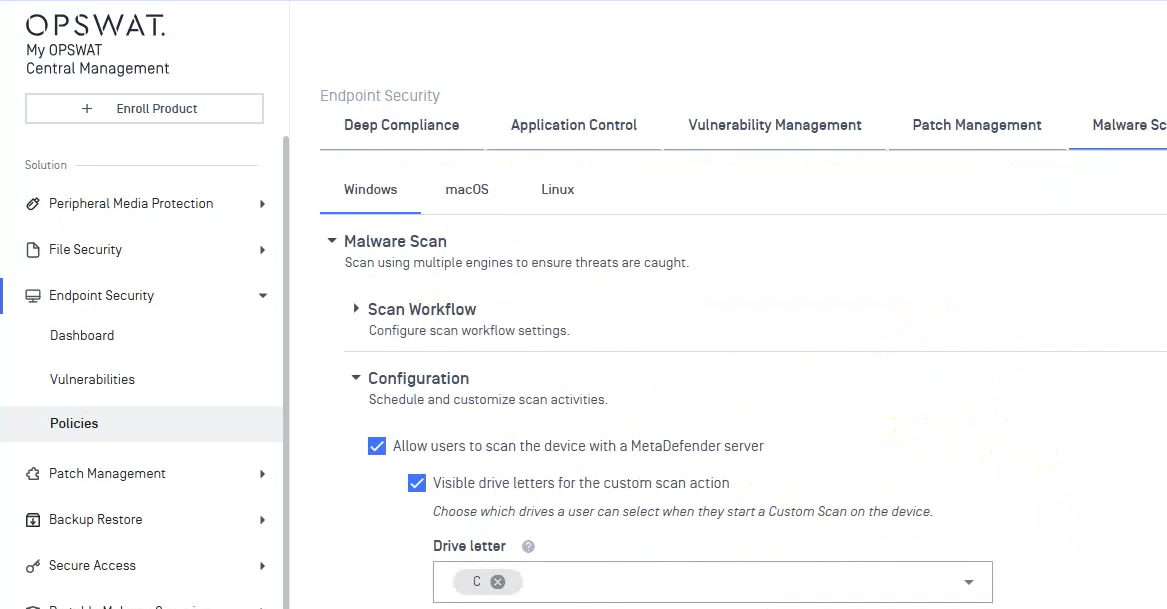
More Control Over Custom Scanning for Administrators
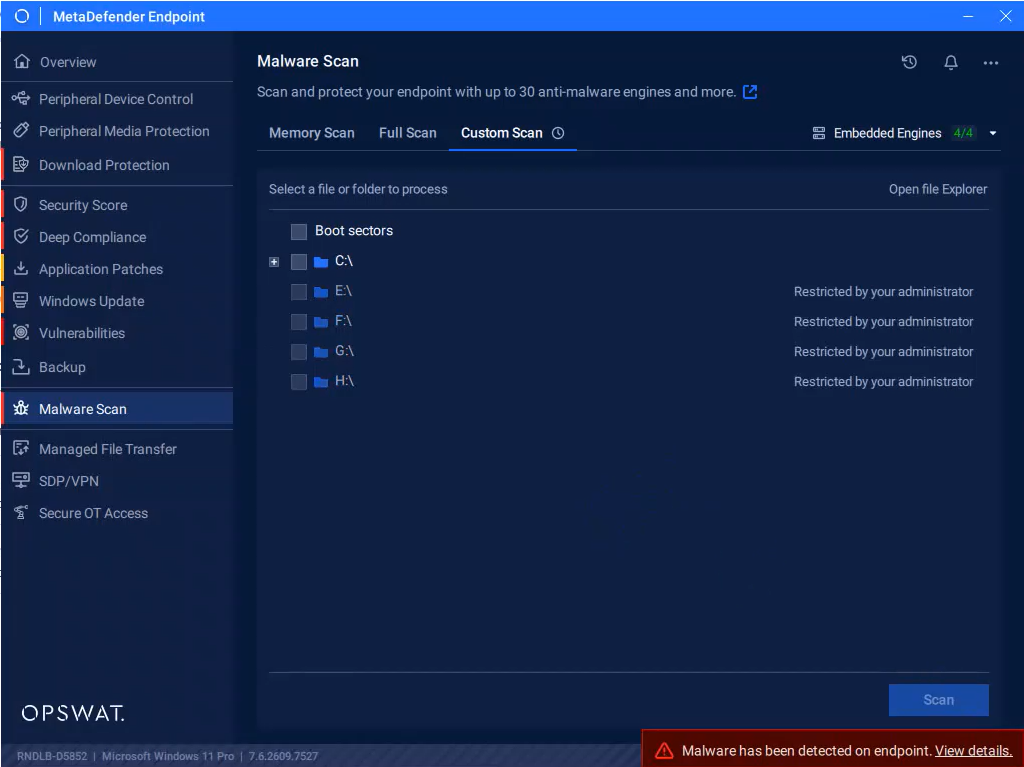
Administrators can now control which local drives users can view and select when running a Custom Scan through Malware Scan. This provides more granular control over the scanning experience and helps organizations align user-accessible scan locations with their security policies. Limiting visibility to appropriate drives enables administrators to simplify the user experience while reducing the risk of users accessing or scanning locations outside the intended scope.
Extend File Audit Trails Across the OPSWAT Ecosystem
MetaDefender Endpoint now supports file audit trails for files scanned by the product for the first time, contributing to a more complete view of a file journey across OPSWAT products.
Rather than treating each scan as an isolated security event, this capability contributes to broader file journey visibility across the OPSWAT ecosystem. Security teams can use this information to better understand where a file has been scanned and how it has moved through different security controls, helping provide greater context when investigating files and security events.
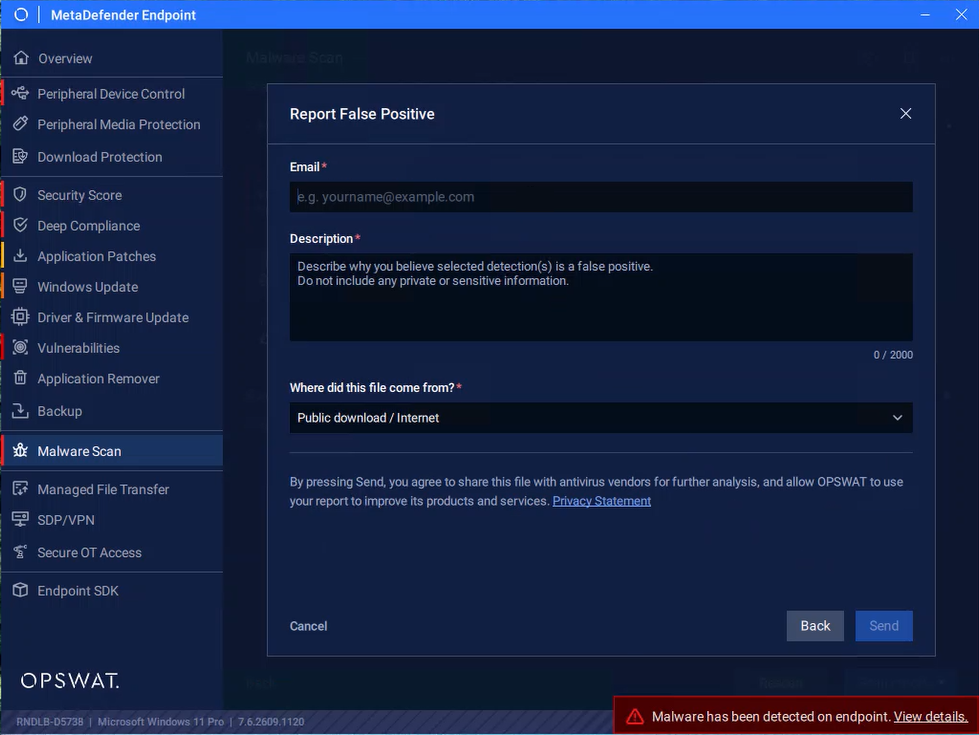
Submit Suspected False Positives Directly from Malware Scan
When a legitimate file is incorrectly identified as malicious, providing context quickly helps accelerate the review process. Users can now submit suspected false positives directly from the Malware Scan interface, including a rationale and the file’s origin.
By capturing this context at the point of detection, security teams can gain more relevant information for investigation without requiring a separate workflow. This makes suspected false positives easier to report while keeping the process closely connected to the original scanning event.
What's New in MetaDefender Endpoint Validation
Add Trusted Peripheral Devices to the Linux Allow List
With the new enhancement in MetaDefender Endpoint Validation for Linux, users can now add specific peripheral devices by vendor, product ID, or instance path to allowlist and exempt them from the validation process. Each change is protected by challenge-based code or administrator password confirmation, helping ensure that only authorized users can modify the list
Administrators can also reset the allow list whenever needed. Once approved, listed devices bypass blocking and validation, providing a controlled way to accommodate trusted peripherals without interrupting established workflows.
Next-Level Endpoint Management Solution
Discover why worldwide organizations, institutions, and entities trust MetaDefender Endpoint to protect critical endpoints. Talk to an expert today to learn more.

