
This article applies to all My OPSWAT Central Management products deployed on Windows, macOS, Linux, Android and iOS systems.
As of 2 June 2020, My OPSWAT Central Management customers require a Platinum tier account in order to enable or use Threat Detection via MetaDefender Cloud.
This means that free My OPSWAT Central Management and free MetaDefender Cloud users can no longer enable or use Threat Detection via MetaDefender Cloud.
If your account does not support threat detection via multi-scanning with MetaDefender Cloud, and you attempt to enable threat detection with MetaDefender Cloud as a scan source in one of your My OPSWAT Central Management policies, that policy will be considered Invalid.
The system will notify you as to the nature and cause of your invalid policy, as illustrated below, and you can opt to either disable the notification or adjust the relevant setting. To fix invalid policies, please Read This.
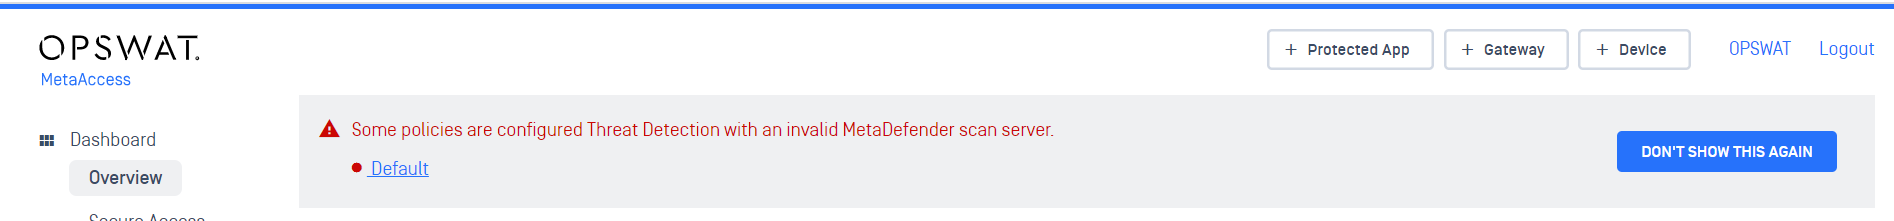
In the event that you configure one or more invalid policies:
You will not be permitted to confirm or implement any policy changes until the invalid setting has been corrected.
MetaDefender Endpoint will not perform any threat detection scans, even if a scan is scheduled in your policy.
All users can still leverage MetaDefender’s ground-breaking Threat Detection technology by adding one or more native MetaDefender Core servers to their account, if they have not done so already.
To explore this option, or to explore qualifying MetaDefender Cloud options, please contact the OPSWAT Sales team.
If you have further queries, concerns or issues regarding Invalid Policies And How To Enable Threat Detection, please open a Support Case with the OPSWAT team via phone, online chat or form, or feel free to ask the community on our OPSWAT Expert Forum.