
Knowledge Base
v1.0
Search this version
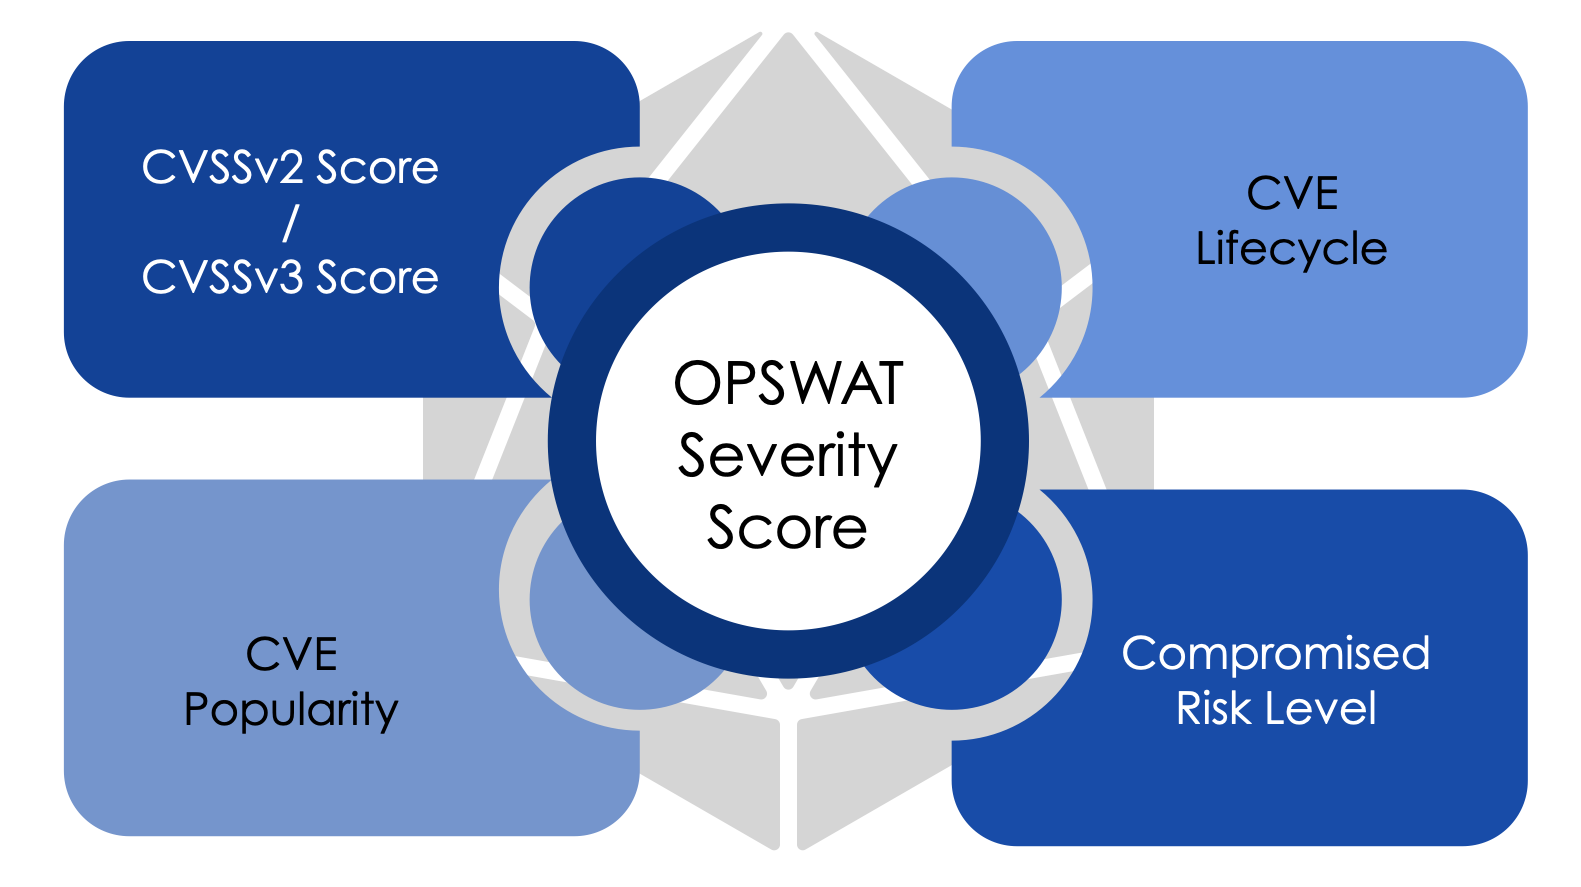
How is the Severity Score calculated for the Vulnerabilities?
Term | Definition |
|---|---|
CVSSv2/CVSSv3 | CVSS score is still a primary input. |
CVE Popularity | Indicating the activity level of the vulnerability. |
Compromised Risk Rate | Indicating the number of devices on which the vulnerability has been confirmed - sourced from real life machine data. |
CVE Lifecycle | Indicating the time elapsed since this vulnerability was first reported (case 0). |
Reference Online Documentation here: What is OPSWAT Severity Score in our Vulnerability Scanning Technology? - MetaDefender IT-OT Access
Last updated on
Was this page helpful?
Knowledge Base
Knowledge Base
Compliance
Patch Management
Vulnerability Assessment
Digital Signature Verification
Setup and Configuration
Customer Communication