
For SIEM integration such as Splunk, on MetaDefender Storage Security side, enable syslog to send to Splunk syslog server via specific protocol (TCP/UDP) and port. Then on that syslog server, configure to listen all incoming messages over the protocol and port.
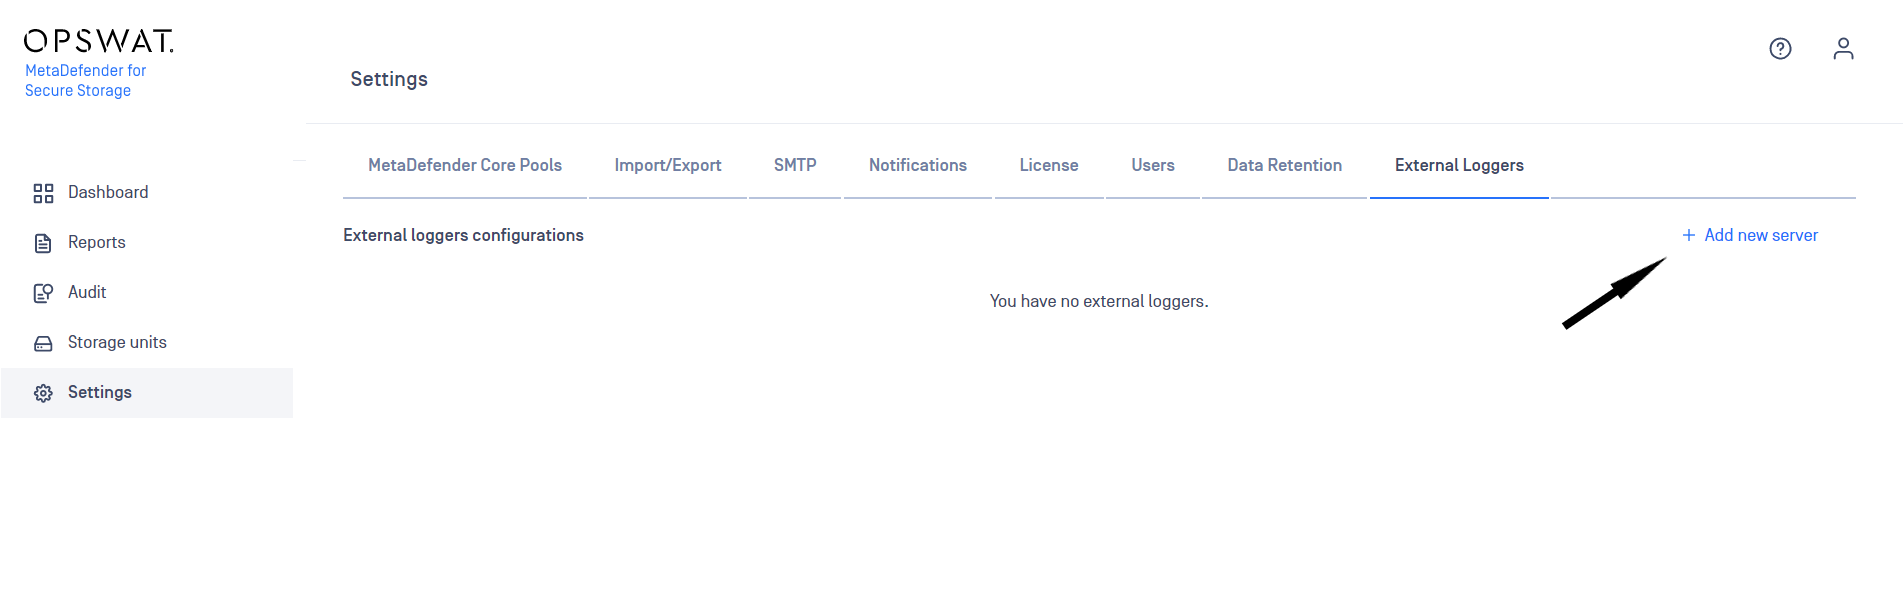
In order to add an external logger configuration:
Navigate to Settings -> External Loggers
Click on Add New Server button
Supported external logger integrations:
Syslog UDP with RFC5424 format
Kafka
Was this page helpful?
Configuration