Untrusted by Design, Proven by Testing: Inside Deep CDR™ Validation
AI is increasing the number of files moving through the enterprise, and it's getting harder to tell safe files from malicious ones. Deep CDR technology, trusted for classified networks and inter-agency file exchanges, doesn't need to tell them apart: it treats every file as untrusted, no matter who or what created it.
Join OPSWAT VP of Products George Prichici to see how Deep CDR technology is tested not just internally, but to the standards intelligence and defense agencies require, and how it's independently proven through penetration testing and specialized anti-malware testing labs, including AV-Comparatives' latest evaluation. You'll leave with a framework for holding any CDR vendor to the same standard.
Read the Book Behind the Approach
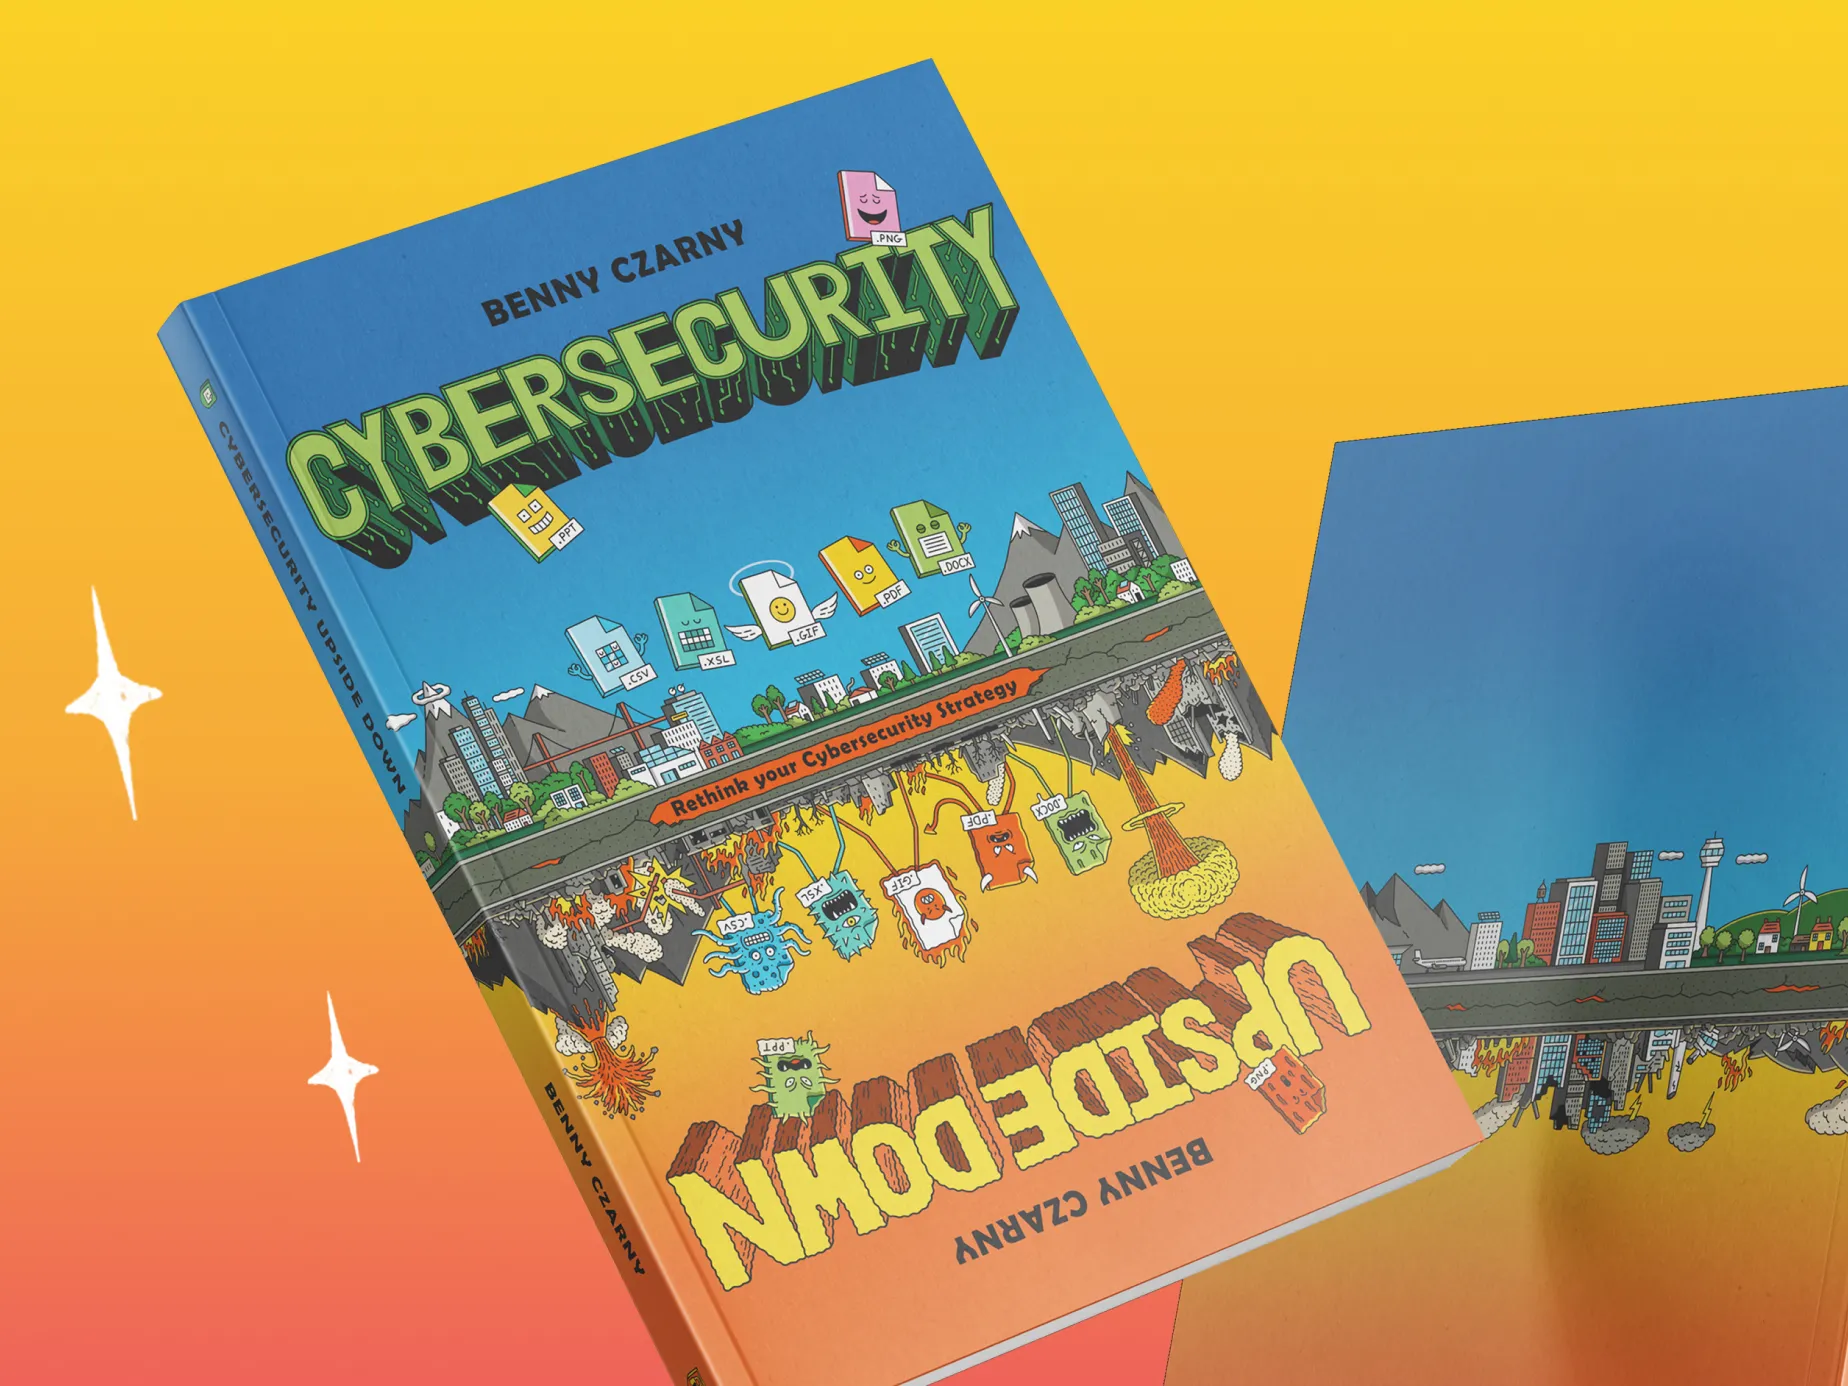
Cybersecurity Upside Down, by OPSWAT founder and CEO Benny Czarny, lays out the prevention-first thinking that Deep CDR™ Technology is built on, and that AV-Comparatives independently validated. A fitting primer for the webinar.
What AV-Comparatives Found
AV-Comparatives independently designed the methodology, ran the evaluation, and reached its own conclusions. Testing spanned three areas: how Deep CDR™ Technology handled live attack scenarios, how many file types it covered, and whether reconstructed files stayed usable. Here is a look at what the webinar will cover.
Tested Against Today's Toughest Attacks
From AI-assisted malicious content to macros, embedded executables, and nested archives, Deep CDR technology was evaluated across every major file-borne attack scenario, earning a 100% sanitization rate in AV-Comparatives' latest test. See how it held up in the webinar.
Coverage Across Enterprise File Types
Office documents, PDFs, images, archives, and the formats your teams exchange every day were all put through recursive sanitization, and the result held across every file type tested. The webinar breaks down the results.
Security Without Breaking the File
Removing threats is only half the job, the file still has to work. Reconstructed files stayed usable, preserving the layout, formatting, tables, formulas, and structure people rely on. The webinar details exactly what fidelity was retained and why.
Featured Speaker
George Prichici
George Prichici is the VP of Products at OPSWAT, leading the Application Security PLU. George’s background in technology spans over 15 years, in both product management and software engineering leadership positions. He’s a certified cloud solution architect and his focus and interest is in cybersecurity, cloud infrastructure, and machine learning.
