Secure Every Device Before and After Entering Critical Networks
Vendor laptops and other transient devices routinely connect to OT (Operational Technology) systems for maintenance, support, and updates. According to the 2026 SANS Survey: AI Threats to OT and ICS Security, 31% of respondents who experienced OT/control system incidents identified transient cyber assets, including vendor laptops, as an initial attack vector.
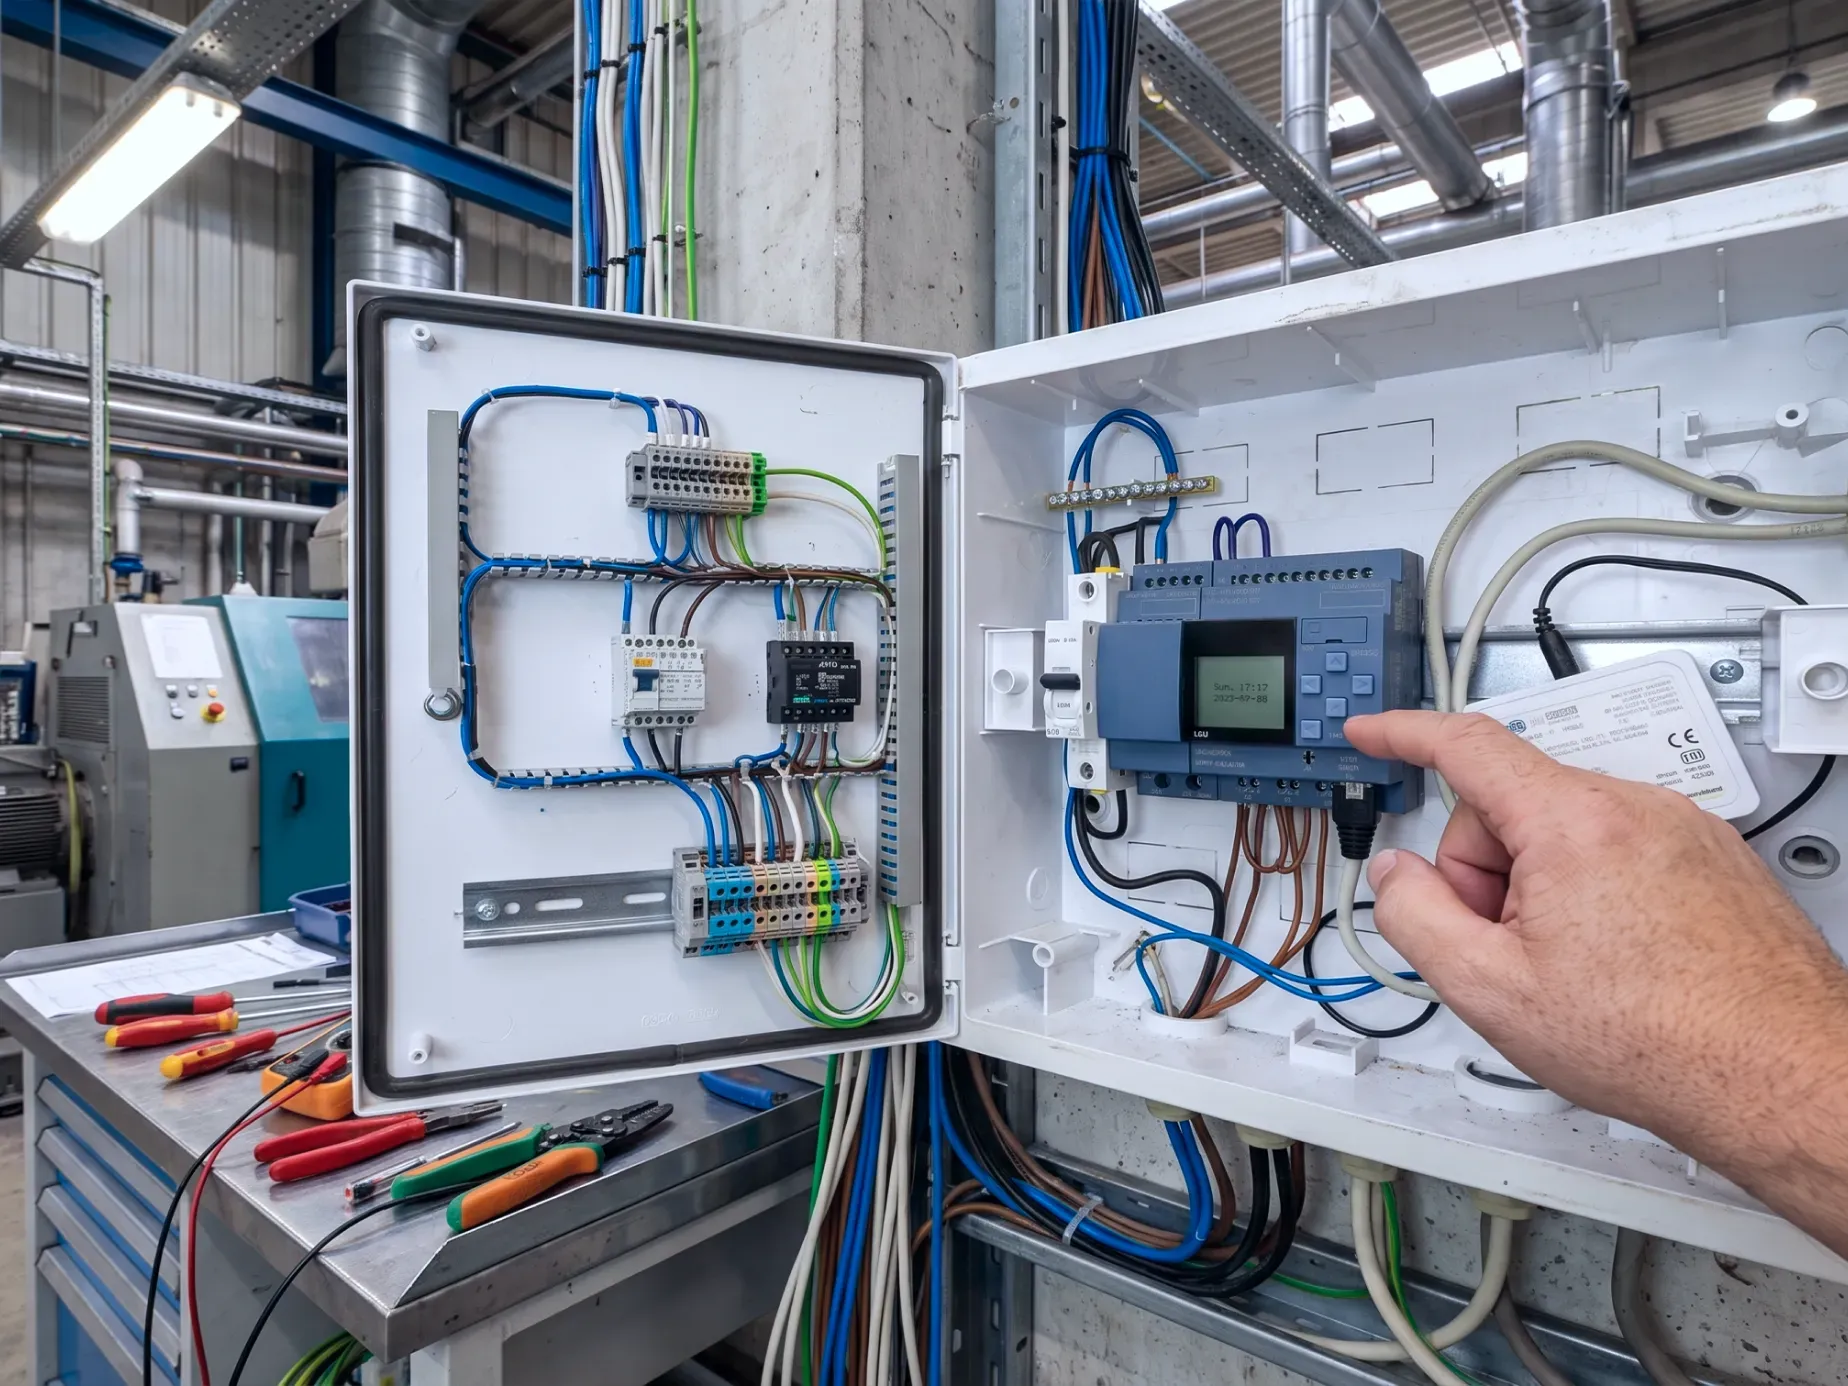
This guide helps security leaders and OT operators address common risks across device scanning, policy enforcement, live system scanning, secure file transfer, and firmware updates through practical, field-based workflows.
Verify Devices Before They Enter Critical Environments
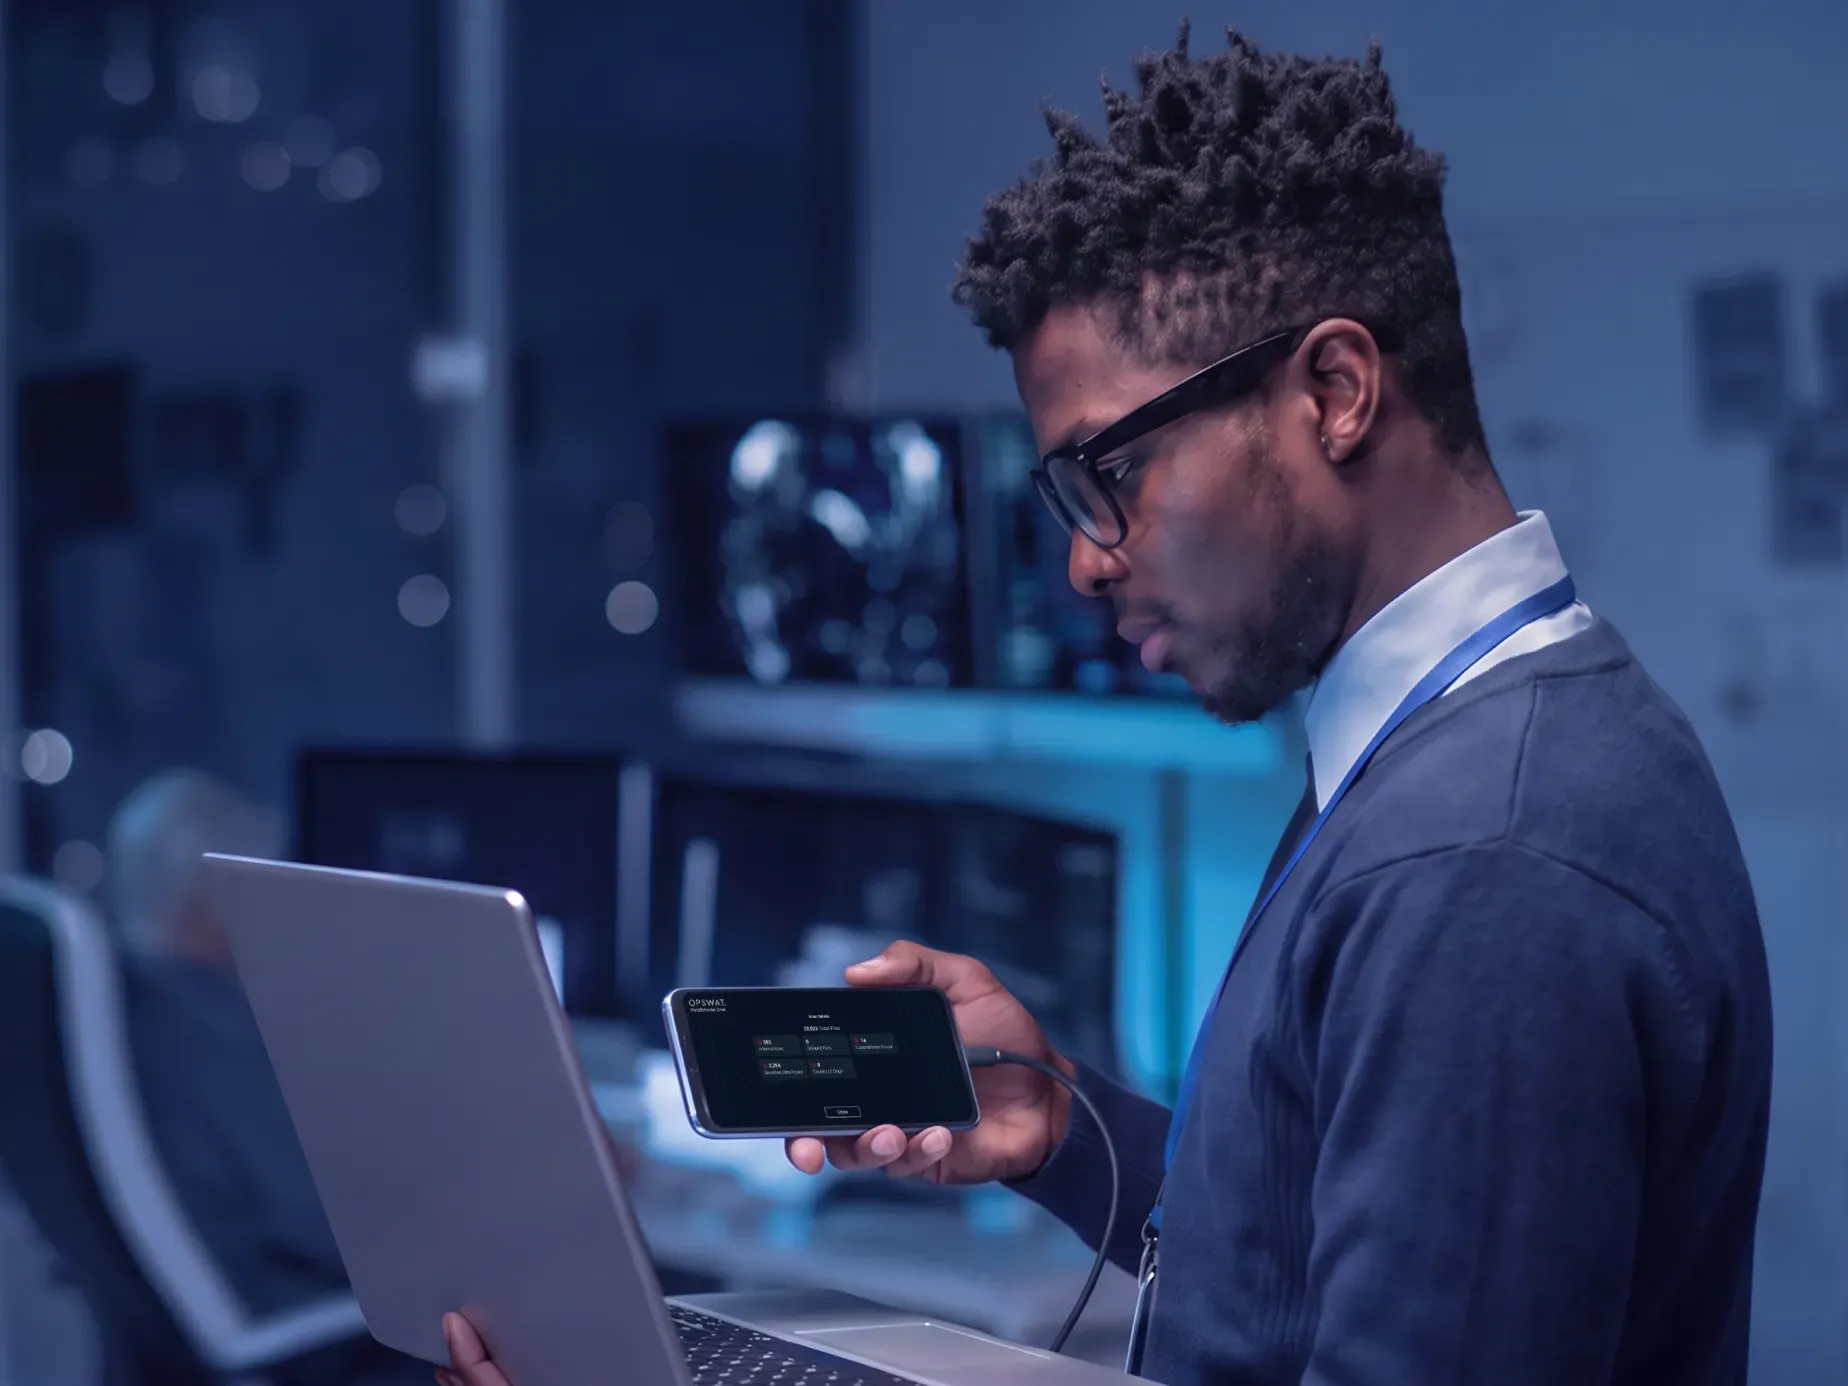
Scan incoming vendor and contractor devices before they connect to critical systems. See how pre-boot scanning, centralized reporting, and coordinated SOC and OT workflows support more informed access decisions.
Scan Critical Systems Without Downtime
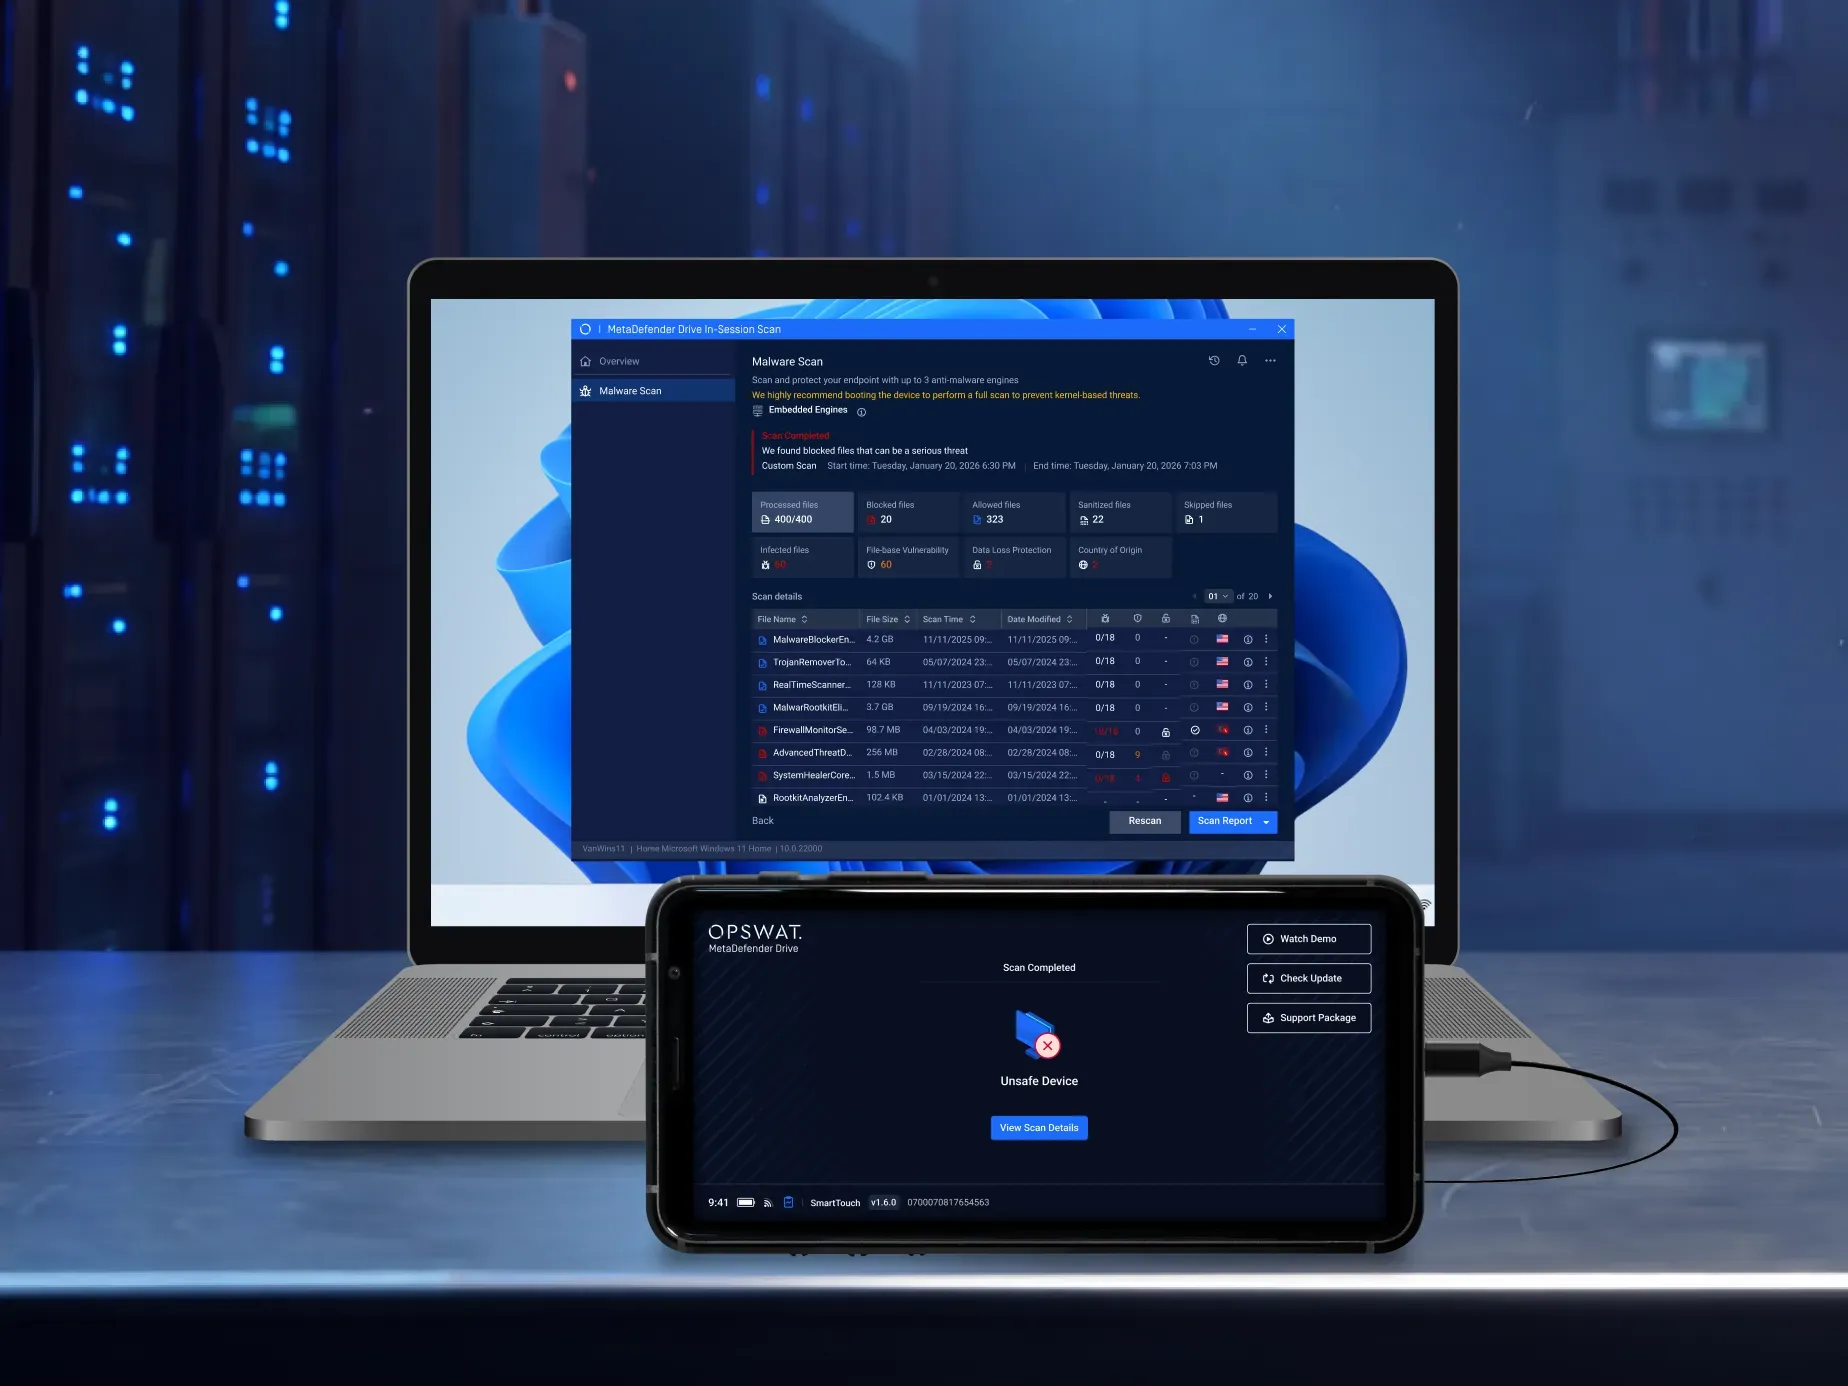
Some critical systems cannot be restarted or taken offline because they support ongoing operations. In-Session scanning allows operators to scan the running system without installing software on the host, helping maintain uptime while identifying potential threats.
Enforce Consistent Security Workflows Across Sites
See how organizations can apply consistent scanning policies across multiple facilities, control exceptions through centralized approval, and enforce secure workflows for file transfer and PLC or HMI firmware updates.
 “MetaDefender Drive plays a key role in adding new appliances into our environment, giving us the assurance they’re safe to be introduced.”
 Adam WhitmoreEngineering Manager for Systems Infrastructure, Genesis Energy
 "OPSWAT and MetaDefender Drive help us control that, showing that anything that comes into our environments is clean. We are able to run a full scan on a third party’s laptop before it comes onto our site and goes anywhere near any of our infrastructure."
 Alan TaylorCSIA, Dounreay Nuclear Restoration Services
Ready to Strengthen Security Across Your Critical OT Environment?
Access five practical workflows for security leaders and OT operators to scan devices, enforce consistent policies, secure file distribution, and support firmware updates across critical environments.